 Pierluigi Paganini
 January 25, 2022
Threat actors are actively exploiting a critical flaw (CVE-2021-20038) in SonicWall’s Secure Mobile Access (SMA) gateways addressed in December. Threat actors are actively exploiting a critical flaw, tracked as CVE-2021-20038, in SonicWall’s Secure Mobile Access (SMA) gateways addressed by the vendor in December. The vulnerability is an unauthenticated stack-based buffer overflow that was reported by […]
 Pierluigi Paganini
January 24, 2022
Threat actors planted a backdoor into multiple WordPress themes and plugins after compromising the website of their developer. In a classic supply chain attack, threat actors planted a backdoor in dozens of WordPress plugins and themes hosted on a developer’s website. The attack took place in the first half of September 2021, the attackers compromised […]
 Pierluigi Paganini
January 24, 2022
Russian authorities arrested four alleged members of the international cyber theft ring tracked as ‘Infraud Organization.’ In February 2008, the US authorities dismantled the global cybercrime organization tracked as Infraud Organization, which was involved in stealing and selling credit card and personal identity data. The Justice Department announced indictments for 36 people charged with being […]
 Pierluigi Paganini
January 24, 2022
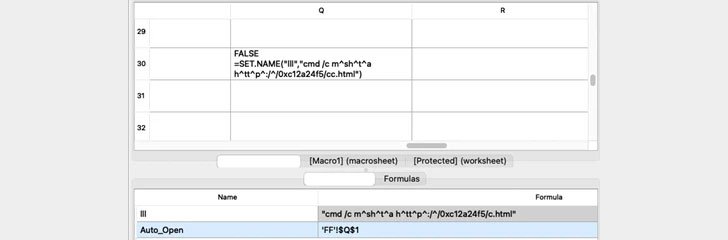
Experts warn Emotet malware campaign using “unconventional” IP address formats in an attempt to evade detection. Threat actors behind a recent Emotet malware campaign have been observed using using “unconventional” IP address formats to evade detection. Trend Micro researchers reported that threat actors are using hexadecimal and octal representations of the IP address. “We observed Emotet spam […]
 Pierluigi Paganini
January 24, 2022
The FBI warns that cybercriminals are using malicious QR codes to steal their credentials and financial info. The Federal Bureau of Investigation (FBI) published a public service announcement (PSA) to warn that cybercriminals are using QR codes to steal their credentials and financial info. QR codes are widely adopted by businesses to facilitate payment. In a classic […]
 Pierluigi Paganini
January 23, 2022
A new round of the weekly Security Affairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. Pay attention to Log4j attacks, Dutch National Cybersecurity Centre (NCSC) warns Vulnerabilities in Control […]
 Pierluigi Paganini
January 22, 2022
The Dutch National Cybersecurity Centre (NCSC) warns organizations of risks associated with cyberattacks exploiting the Log4J vulnerability. The Dutch National Cybersecurity Centre (NCSC) warns organizations to remain vigilant on possible attacks exploiting the Log4J vulnerability. According to the Dutch agency, threat actors the NCSC will continue to attempt to exploit the Log4Shell flaw in future […]
 Pierluigi Paganini
January 22, 2022
Two critical security vulnerabilities in Control Web Panel potentially expose Linux servers to remote code execution attacks Researchers from Octagon Networks disclosed details of two critical security flaws in Control Web Panel that potentially expose Linux servers to remote code execution attacks. Control Web Panel is a popular open-source Linux control panel for servers and VPS that allows easy […]
 Pierluigi Paganini
January 21, 2022
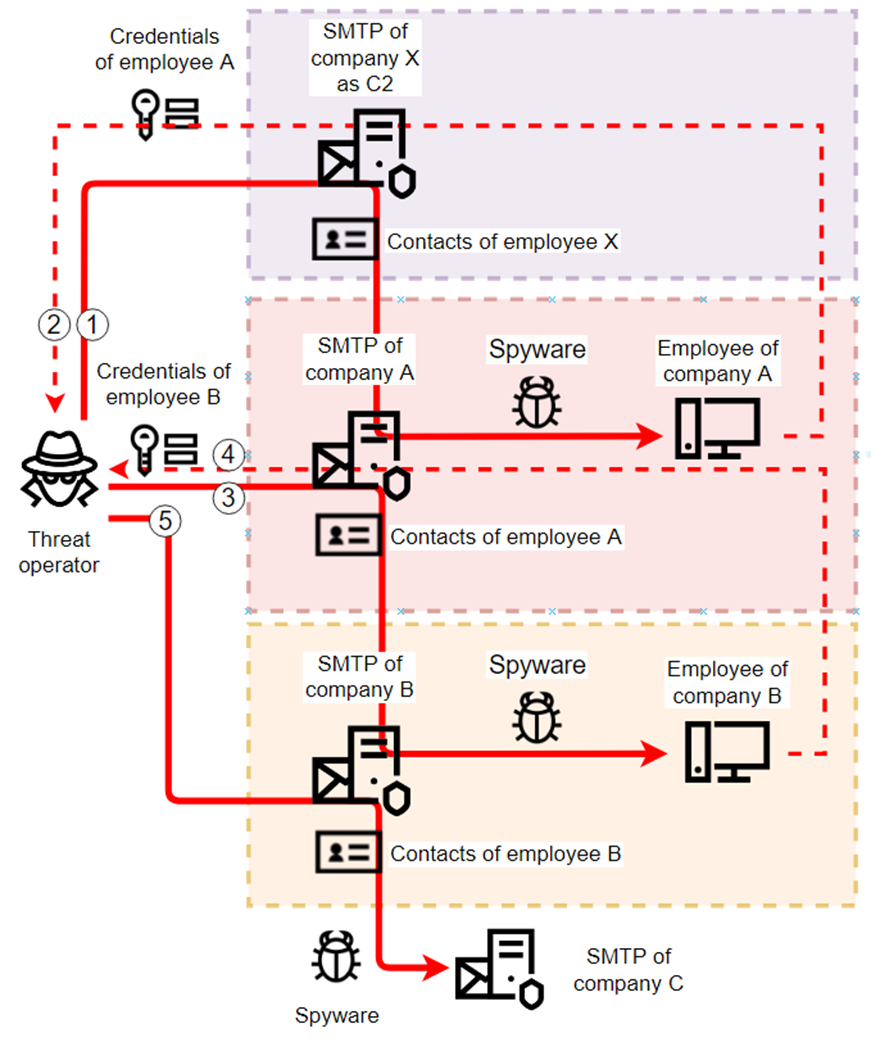
Researchers spotted several spyware campaigns targeting industrial enterprises to steal credentials and conduct financial fraud. Researchers from Kaspersky Lab have uncovered multiple spyware campaigns that target industrial firms to steal email account credentials and carry out fraudulent activities. Threat actors sent spear-phishing messages from compromised corporate accounts to their contacts, the email carry malicious attachments. […]
 Pierluigi Paganini
January 20, 2022
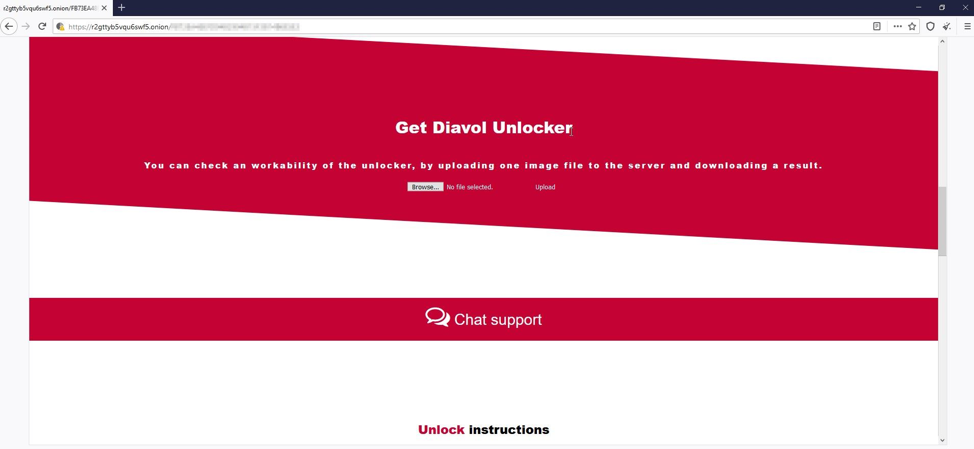
The Federal Bureau of Investigation (FBI) officially linked the Diavol ransomware operation to the infamous TrickBot gang. The FBI officially linked the Diavol ransomware operation to the infamous TrickBot gang, the group that is behind the TrickBot banking trojan. “The FBI first learned of Diavol ransomware in October 2021. Diavol is associated with developers from […]