 Pierluigi Paganini
 September 28, 2026
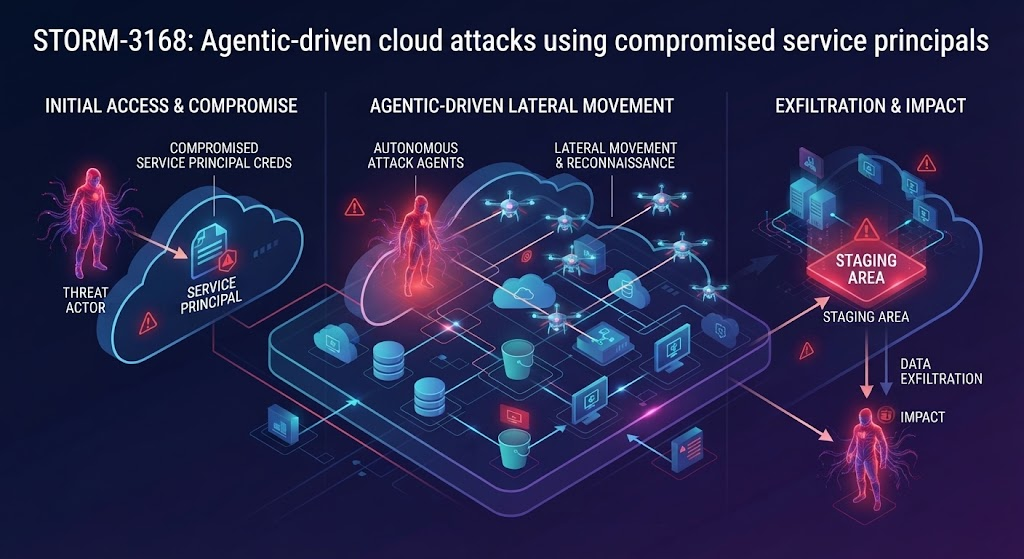
Microsoft details Storm-3168, the JADEPUFFER-linked actor that used stolen service principals to delete Azure storage in minutes and harvest keys. Microsoft just published the first detailed look at what JADEPUFFER does inside Azure. Sysdig first spotted the group’s activity in July 2026 and called it the first documented agentic ransomware operation. Microsoft tracks the same […]
 Pierluigi Paganini
July 30, 2026
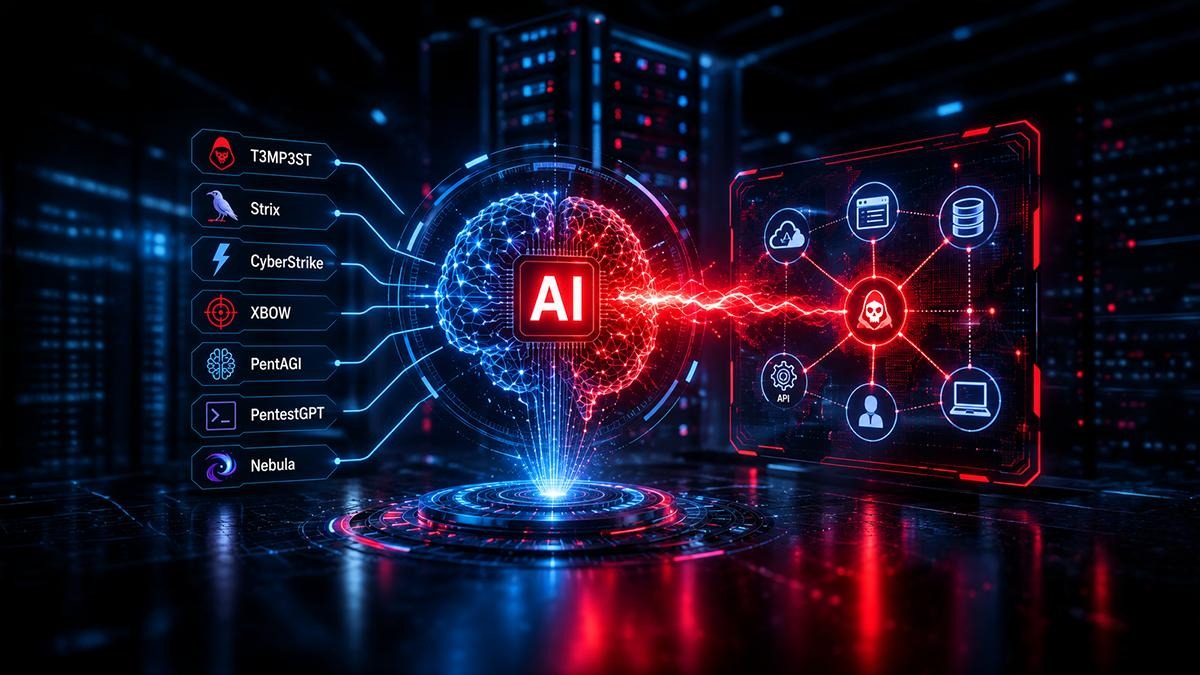
Resecurity warns AI offensive agents are lowering hacking barriers, fueling an AI-driven race between attackers and defenders. Resecurity analyzed how autonomous offensive security agents such as T3MP3ST, Strix, CyberStrike, XBOW, PentAGI, PentestGPT, and Nebula lower the barriers to vulnerability identification and exploitation. The analysis also explores why AI is being repurposed for real attacks and […]
 Pierluigi Paganini
July 03, 2026
Sysdig reports an AI agent ran a full ransomware attack end-to-end, exploiting flaws, stealing creds, moving laterally, and encrypting data without humans. Sysdig’s Threat Research Team has documented what it assesses to be the first ransomware operation driven end-to-end by a large language model. The operator, which Sysdig calls JADEPUFFER, broke into a server, harvested […]