 Pierluigi Paganini
 August 31, 2023
Russia-linked threat actors have been targeting Android devices of the Ukrainian military with a new malware dubbed Infamous Chisel. GCHQ’s National Cyber Security Centre and international partners reported that Russia-linked threat actors are using a new malware to target the Ukrainian military Government experts attribute the attack to the Russian military intelligence service the GRU. […]
 Pierluigi Paganini
August 30, 2023
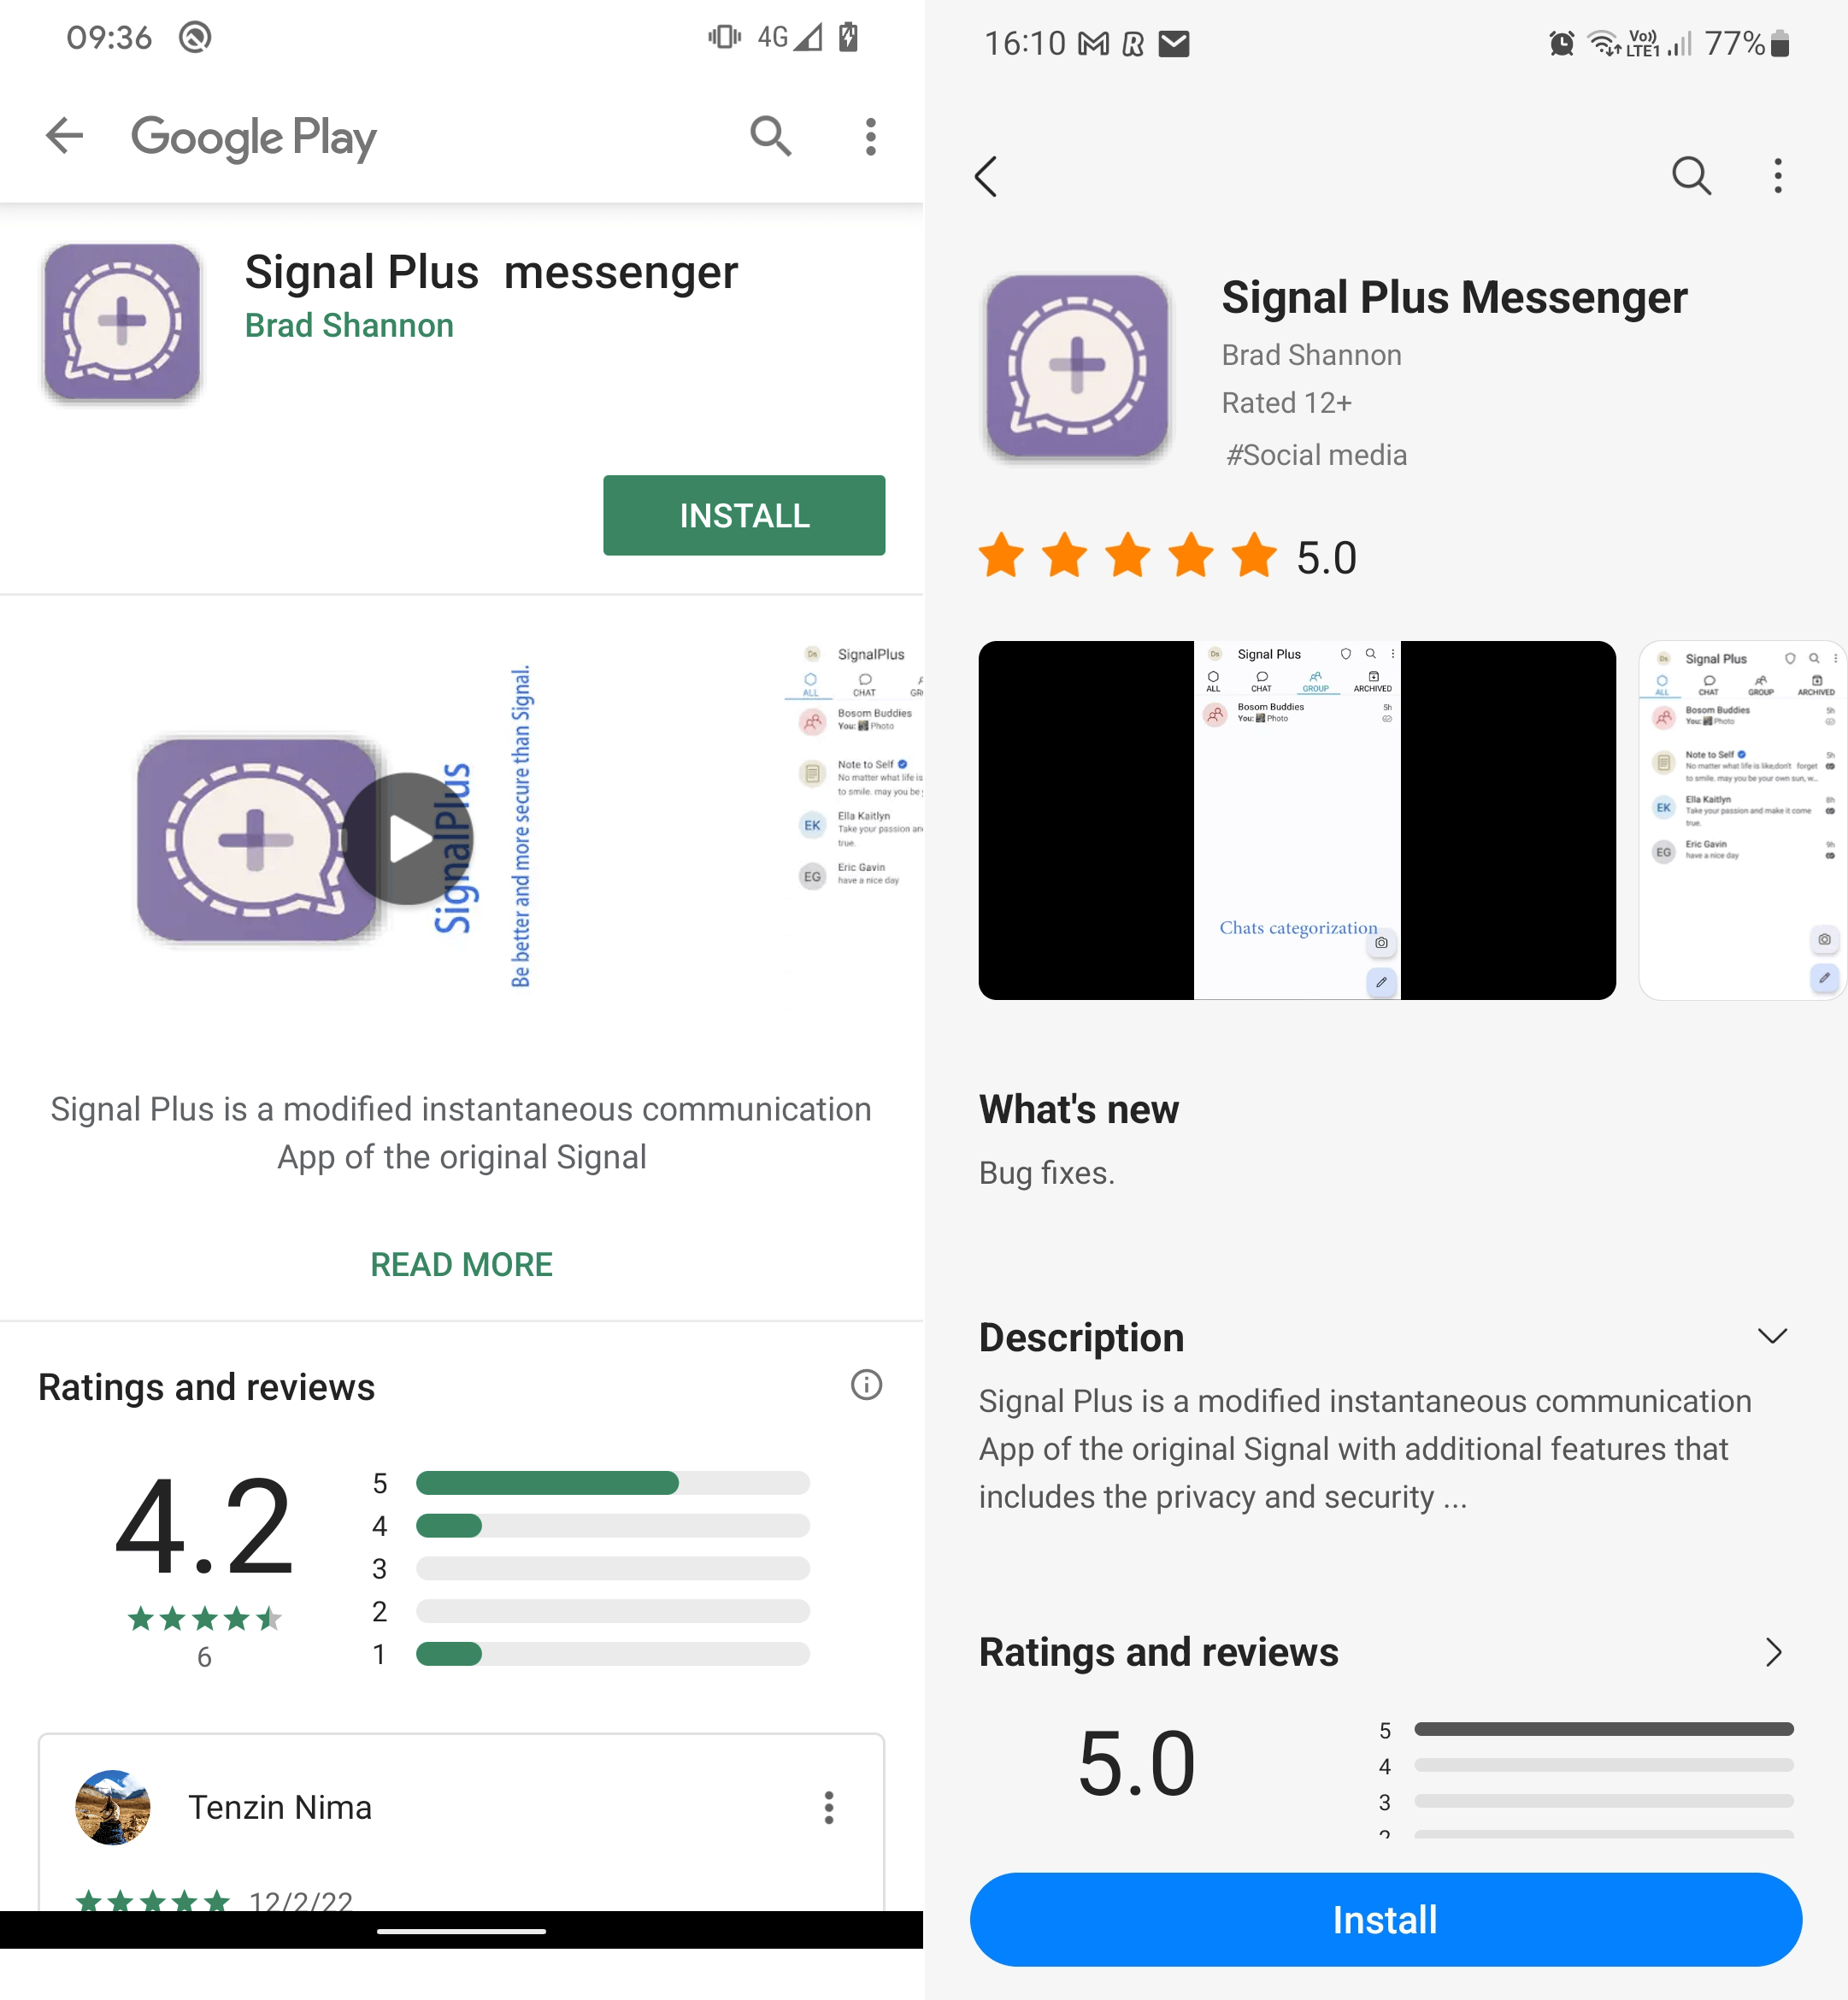
China-linked APT group GREF is behind a malware campaign distributing spyware via trojanized Signal and Telegram apps on Google Play ESET researchers uncovered a cyberespionage campaign carried out by the China-linked APT group known as GREF that is distributing spyware via trojanized Signal and Telegram apps on Google Play and Samsung Galaxy stores. The malware […]
 Pierluigi Paganini
August 30, 2023
FBI coordinated an international law enforcement operation, named Operation ‘Duck Hunt’, that dismantled the Qakbot botnet. The FBI announced that the Qakbot botnet has been dismantled as a result of an international law enforcement operation named Operation ‘Duck Hunt.’ Qakbot, also known as QBot, QuackBot and Pinkslipbot, is an info-stealing malware that has been active […]
 Pierluigi Paganini
August 28, 2023
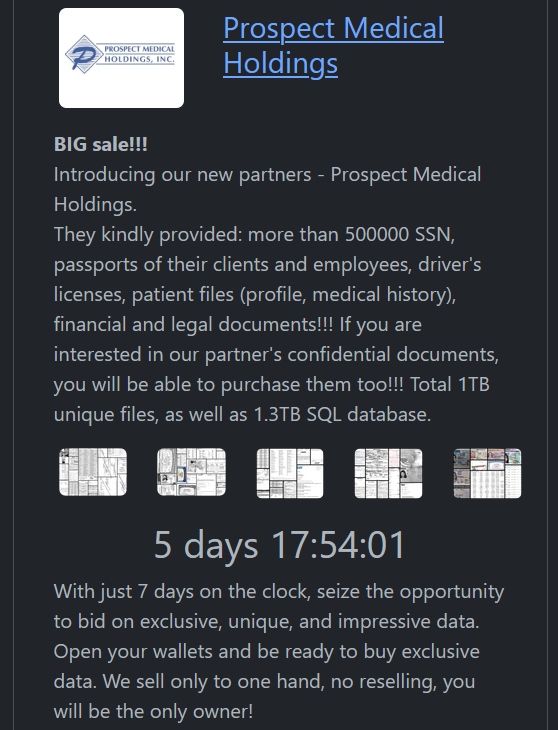
The Rhysida ransomware group claimed to have hacked Prospect Medical Holdings and sensitive information from the company. In early August, a cyberattack disrupted the computer systems of multiple hospitals operated by Prospect Medical Holdings, which are located in multiple states, including California, Texas, Connecticut, Rhode Island, and Pennsylvania. Some emergency rooms in multiple hospitals in […]
 Pierluigi Paganini
August 28, 2023
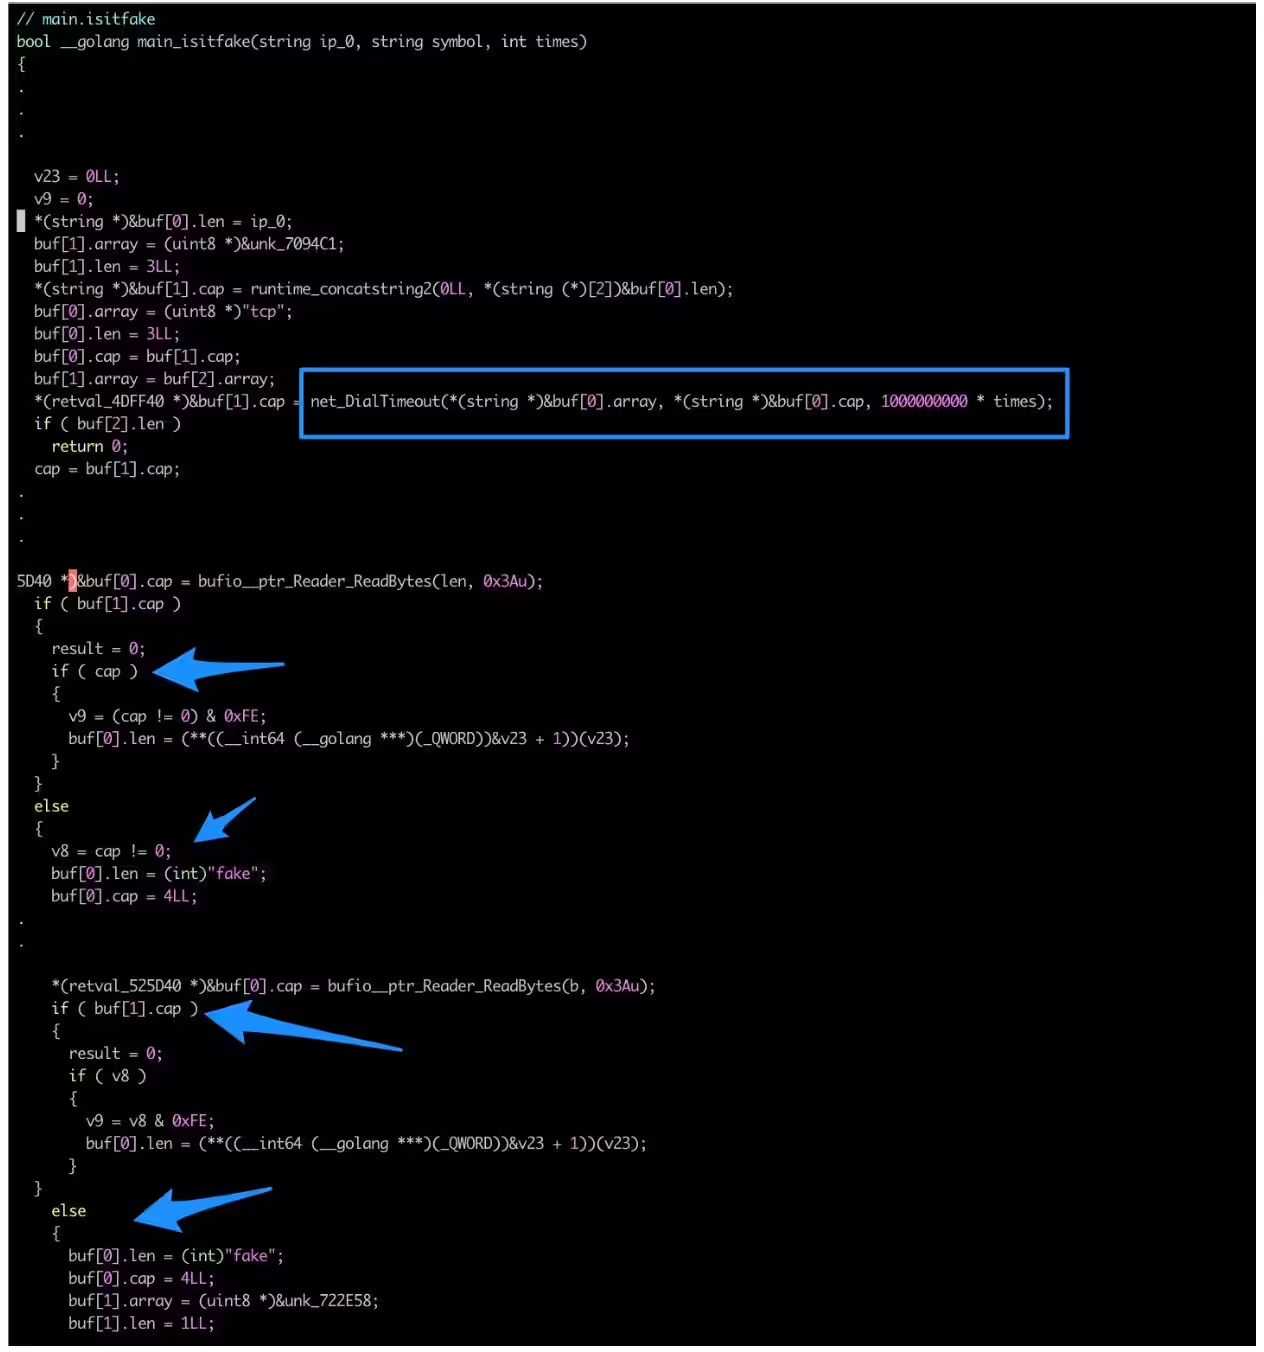
Researchers spotted an updated version of the KmsdBot botnet that is now targeting Internet of Things (IoT) devices. The Akamai Security Intelligence Response Team (SIRT) discovered a new version of the KmsdBot botnet that employed an updated Kmsdx binary targeting Internet of Things (IoT) devices. KmsdBot is an evasive Golang-based malware that was first detected by […]
 Pierluigi Paganini
August 27, 2023
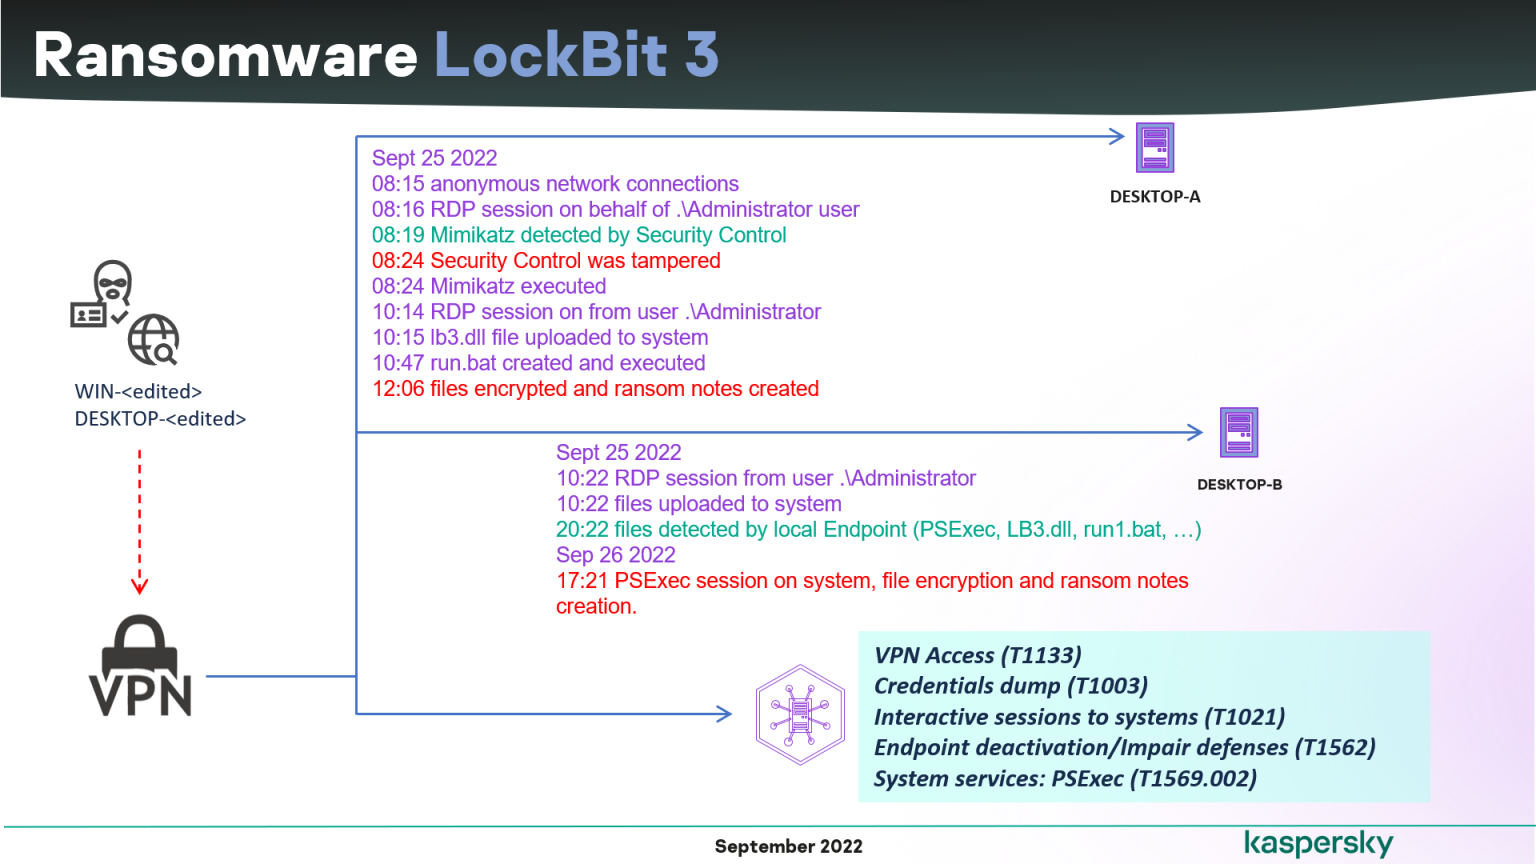
The leak of the source code of the LockBit 3.0 ransomware builder in 2022 allowed threat actors to create new variants of the threat. Lockbit v3, aka Lockbit Black, was detected in June 2022, but in September 2022 a builder for this variant was leaked online. The availability of the builder allowed anyone to create their own […]
 Pierluigi Paganini
August 27, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Cloud and hosting provider Leaseweb took down critical systems after a cyber attack French employment agency […]
 Pierluigi Paganini
August 25, 2023
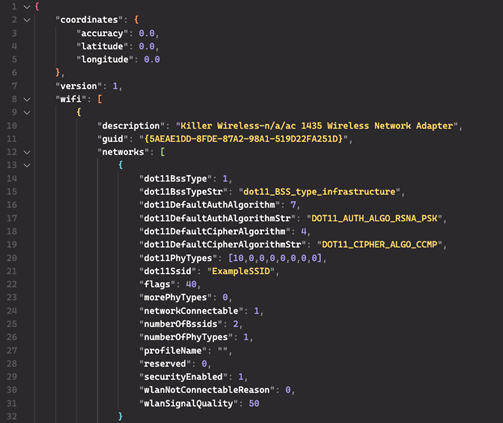
Experts observed the SmokeLoader malware delivering a new Wi-Fi scanning malware strain dubbed Whiffy Recon. Secureworks Counter Threat Unit (CTU) researchers observed the Smoke Loader botnet dropping a new Wi-Fi scanning malware named Whiffy Recon. The malicious code triangulates the positions of the infected systems using nearby Wi-Fi access points as a data point for Google’s […]
 Pierluigi Paganini
August 24, 2023
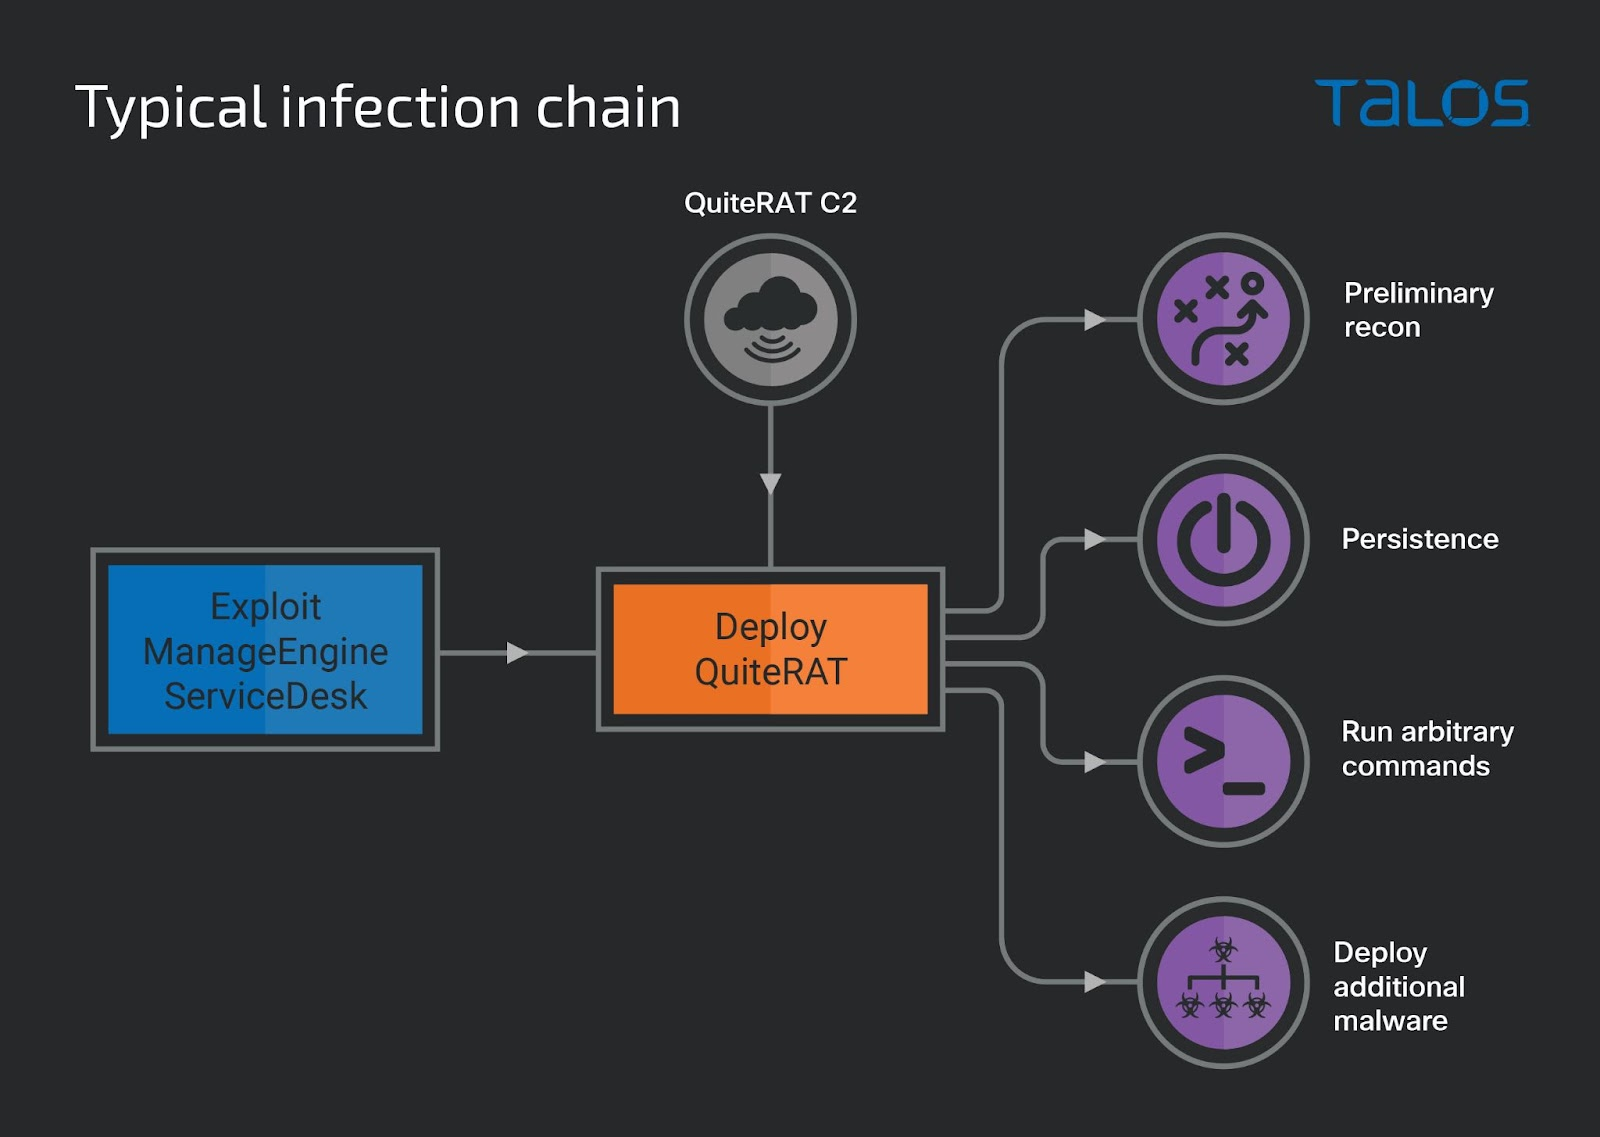
The North Korea-linked Lazarus group exploits a critical flaw in Zoho ManageEngine ServiceDesk Plus to deliver the QuiteRAT malware. The North Korea-linked APT group Lazarus has been exploiting a critical vulnerability, tracked as CVE-2022-47966, in Zoho’s ManageEngine ServiceDesk in attacks aimed at the Internet backbone infrastructure provider and healthcare organizations. The state-sponsored hackers targeted entities […]
 Pierluigi Paganini
August 23, 2023
The U.S. FBI warned that North Korea-linked threat actors may attempt to cash out stolen cryptocurrency worth more than $40 million. The Federal Bureau of Investigation shared details about the activity of six cryptocurrency wallets operated by North Korea-linked threat actors. The wallets hold roughly 1,580 Bitcoin (roughly $41 million at the current rate) that […]