 Pierluigi Paganini
 April 16, 2023
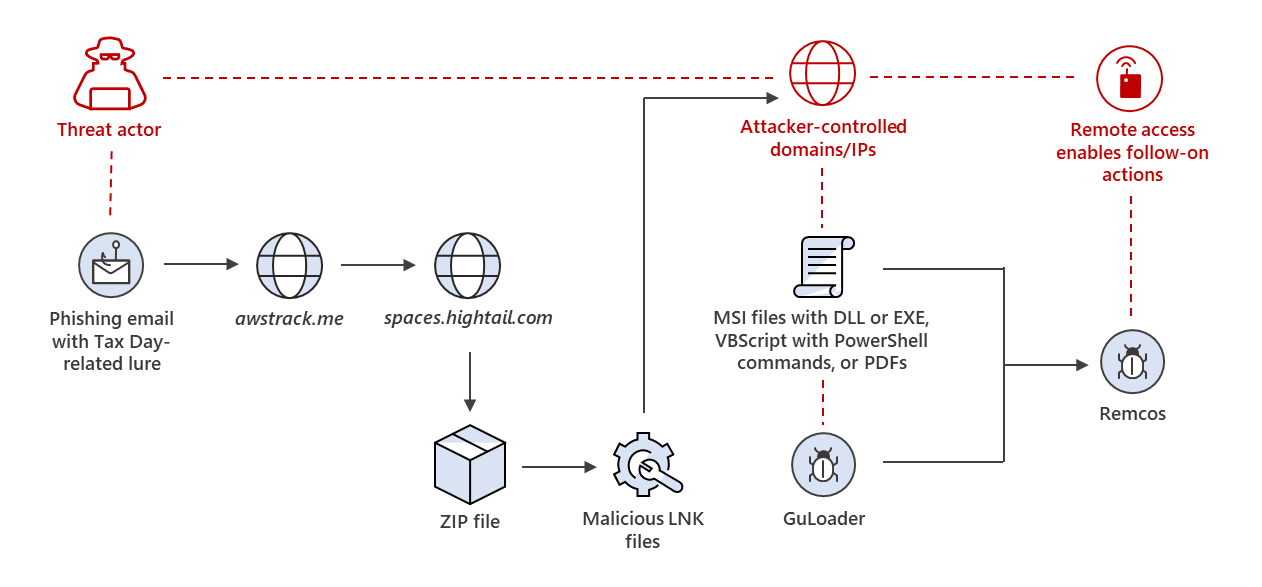
Microsoft warns of a new Remcos RAT campaign targeting US accounting and tax return preparation firms ahead of Tax Day. Ahead of the U.S. Tax Day, Microsoft has observed a new Remcos RAT campaign targeting US accounting and tax return preparation firms. The phishing attacks began in February 2023, the IT giant reported. Remcos is […]
 Pierluigi Paganini
April 15, 2023
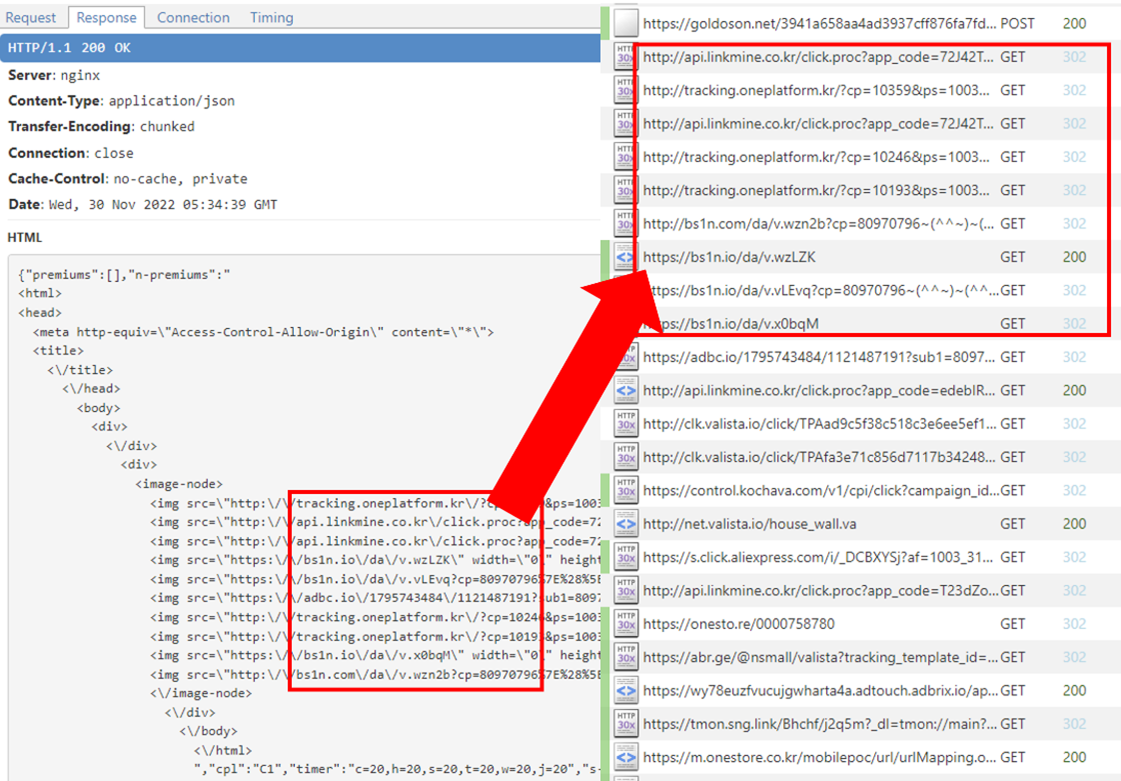
A new Android malware named Goldoson was distributed through 60 legitimate apps on the official Google Play store. The Goldoson library was discovered by researchers from McAfee’s Mobile Research Team, it collects lists of applications installed on a device, and a history of Wi-Fi and Bluetooth devices information, including nearby GPS locations. The third-party library can perform ad fraud by clicking advertisements […]
 Pierluigi Paganini
April 14, 2023
Cybersecurity firm Trellix analyzed the activity of an emerging cybercriminal group called ‘Read The Manual’ RTM Locker. Researchers from cybersecurity firm Trellix have detailed the tactics, techniques, and procedures of an emerging cybercriminal gang called ‘Read The Manual RTM Locker. The group provides a ransomware-as-a-service (RaaS) and provides its malicious code to a network of […]
 Pierluigi Paganini
April 13, 2023
Security experts warn that a Kyocera Android printing app is vulnerable to improper intent handling and can be abused to drop malware. An improper intent handling issue affecting the Kyocera Android printing app can allow malicious applications to drop malware. Such kinds of flaws expose a resource to the wrong control sphere, providing unintended actors with inappropriate […]
 Pierluigi Paganini
April 12, 2023
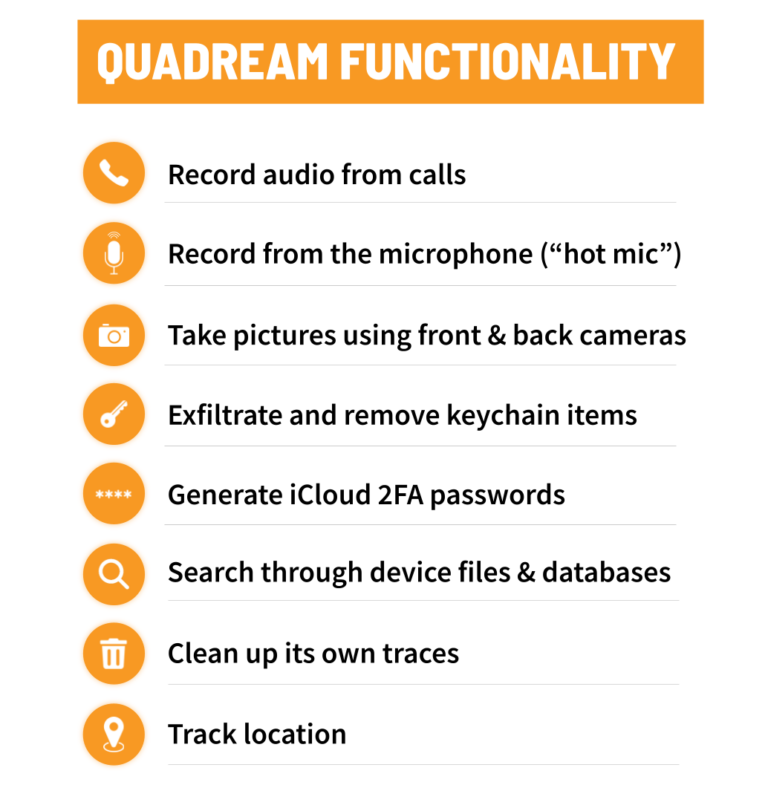
At least five members of civil society worldwide have been targeted with spyware and exploits developed by surveillance firm QuaDream. Citizen Lab researchers reported that at least five civil society members were victims of spyware and exploits developed by the Israeli surveillance firm QuaDream. The victims include journalists, political opposition figures, and an NGO worker […]
 Pierluigi Paganini
April 12, 2023
Microsoft has addressed a zero-day in the Windows Common Log File System (CLFS) actively exploited in ransomware attacks. Microsoft has addressed a zero-day vulnerability, tracked as CVE-2023-28252, in the Windows Common Log File System (CLFS), which is actively exploited in ransomware attacks. Microsoft fixed the issue with the release of Patch Tuesday security updates for […]
 Pierluigi Paganini
April 11, 2023
Yum! Brands, the company that owns the KFC, Pizza Hut, and Taco Bell brands, disclosed a data breach after the January ransomware attack. On January 13, 2023, Yum! Brands suffered a cyberattack that forced the company to take its systems offline closing roughly 300 restaurants in the UK for one day. Now the company, which owns the […]
 Pierluigi Paganini
April 10, 2023
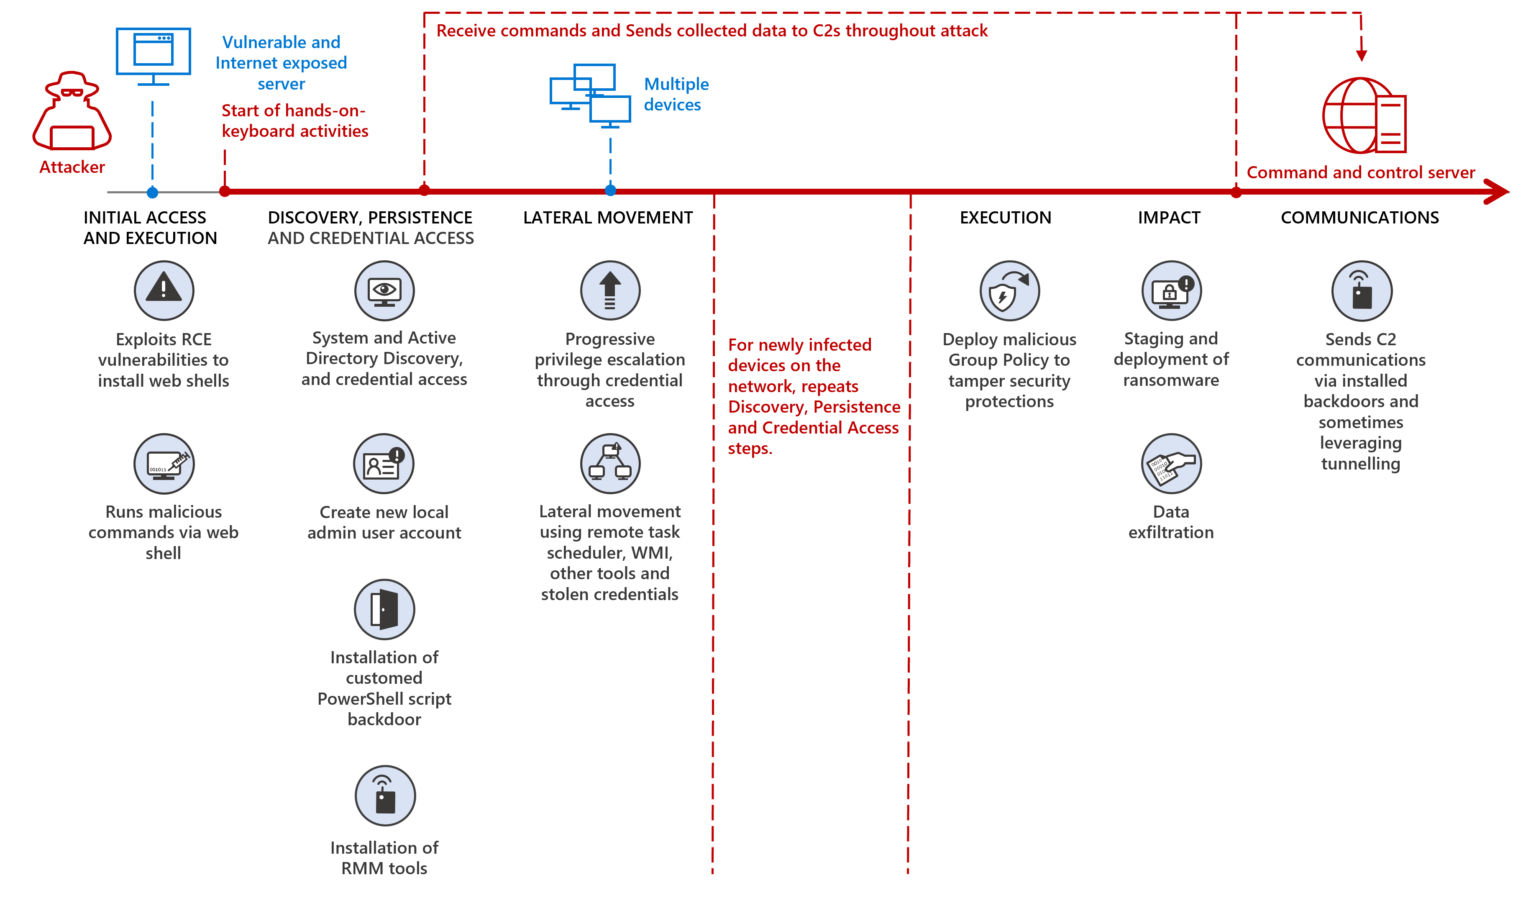
Iran-linked APT group MERCURY is behind destructive attacks on hybrid environments masquerading as a ransomware operation. The Microsoft Threat Intelligence team observed a series of destructive attacks on hybrid environments that were carried out by MuddyWater APT group (aka MERCURY). Threat actors masqueraded the attacks as a standard ransomware operation. MERCURY (aka MuddyWater, SeedWorm and TEMP.Zagros) has been active since […]
 Pierluigi Paganini
April 07, 2023
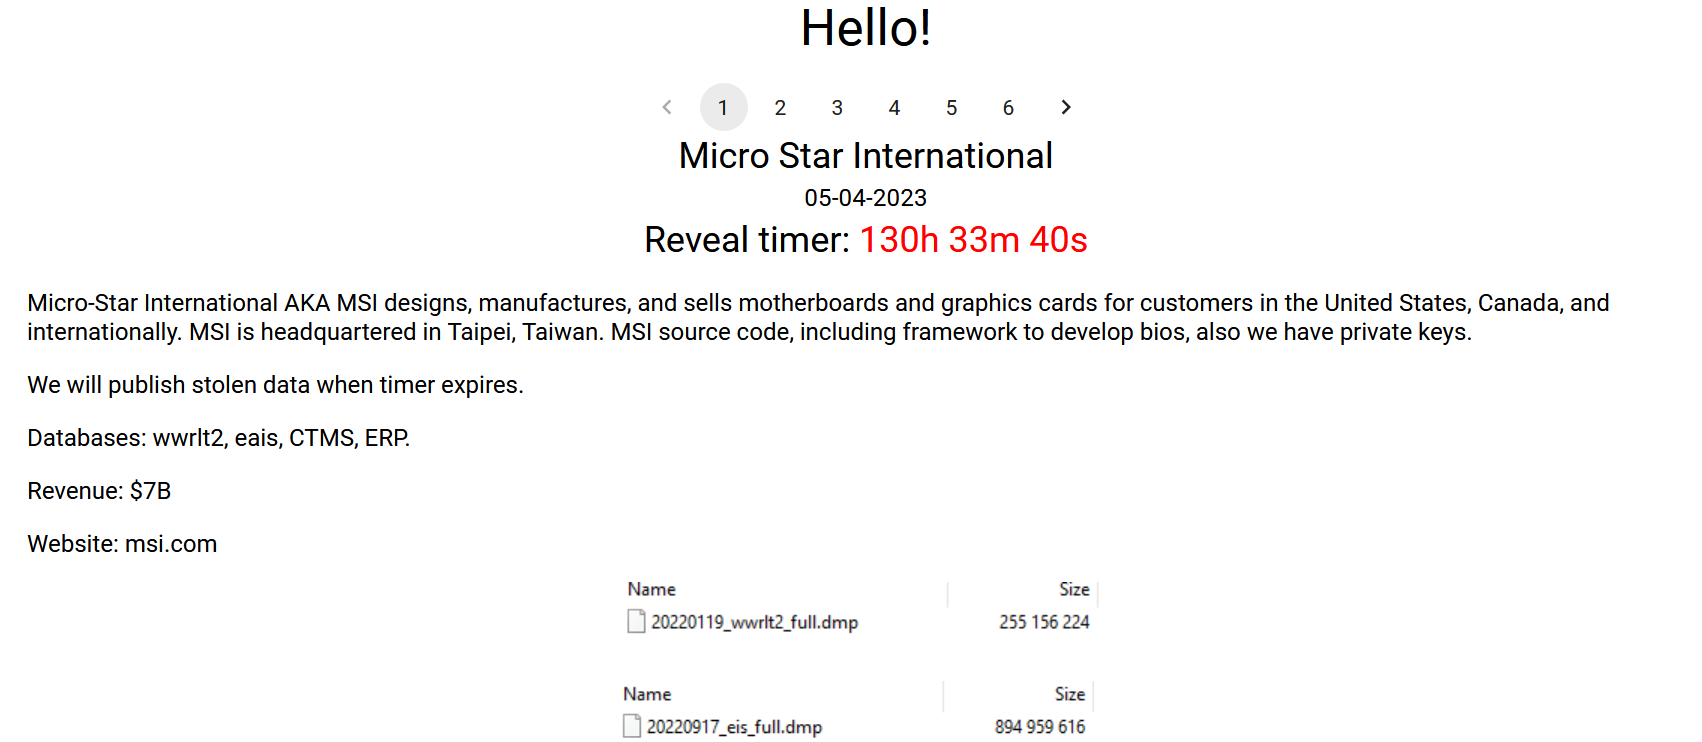
Multinational IT corporation MSI (Micro-Star International) confirms security breach after Money Message ransomware gang claimed the hack. This week the ransomware gang Money Message announced to have hacked the Taiwanese multinational IT corporation MSI (Micro-Star International). Micro-Star International AKA MSI designs, manufactures, and sells motherboards and graphics cards for customers in the United States, Canada, and […]
 Pierluigi Paganini
April 07, 2023
Microsoft announced it has taken legal action to disrupt the illegal use of copies of the post-exploitation tool Cobalt Strike by cybercriminals. Cobalt Strike is a paid penetration testing product that allows an attacker to deploy an agent named ‘Beacon’ on the victim machine. The Beacon includes a wealth of functionality for the attacker, including, but […]