


 Pierluigi Paganini
 February 27, 2023
The Dutch police arrested three individuals as a result of an investigation into computer trespass, data theft, extortion, extortion, and money laundering. The Dutch police announced the arrest of three men as the result of an extensive investigation into computer trespass, data theft, extortion, extortion, and money laundering The suspects were arrested by the Amsterdam […]
 Pierluigi Paganini
February 27, 2023
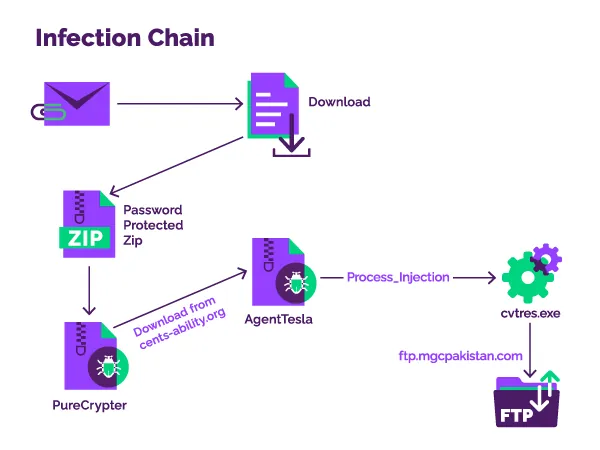
An unknown threat actor is targeting government organizations with the PureCrypter downloader, Menlo Security firm reported. Menlo Labs researchers uncovered an unknown threat actor is using the PureCrypter downloader in attacks aimed at government entities. The campaign relies on the domain of a compromised non-profit organization as a C2 server to deliver a second-stage payload. […]
 Pierluigi Paganini
February 27, 2023
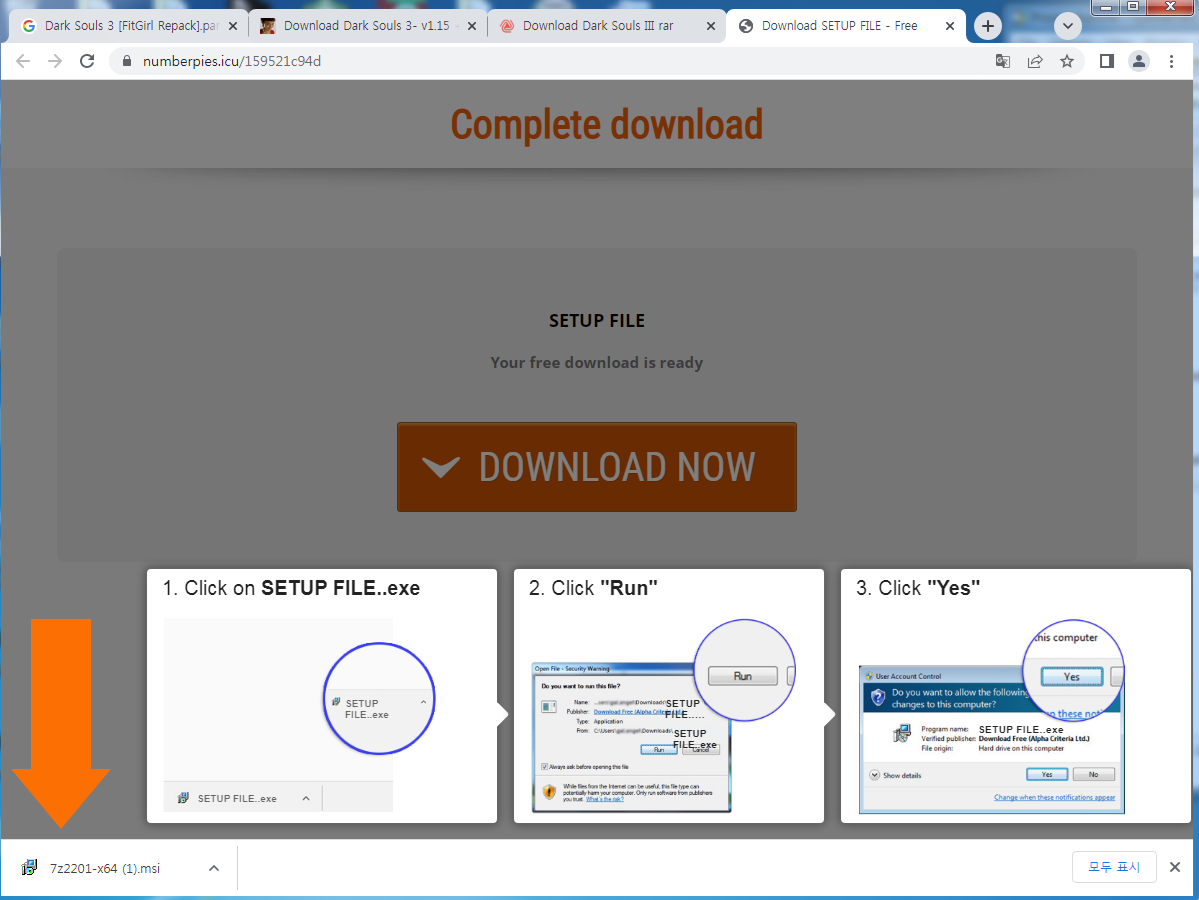
Threat actors behind the ChromeLoader malware campaign are using VHD files disguised as popular games, experts warn. Researchers from Ahnlab Security Emergency Response Center (ASEC) recently uncovered a malware campaign distributing the ChromeLoader using VHD files. ChromeLoader is a malicious Chrome browser extension, it is classified as a pervasive browser hijacker that modifies browser settings to redirect user traffic. […]
 Pierluigi Paganini
February 26, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. Clasiopa group targets materials research in Asia CERT of Ukraine says Russia-linked APT backdoored multiple govt […]
 Pierluigi Paganini
February 25, 2023
A previously unknown threat actor, tracked as Clasiopa, is using a distinct toolset in attacks aimed at materials research organizations in Asia. Broadcom Symantec researchers have reported that a previously unknown threat actor, tracked as Clasiopa, that is using a distinct toolset in attacks aimed at materials research organizations in Asia. At the time of […]
 Pierluigi Paganini
February 25, 2023
The CERT of Ukraine (CERT-UA) revealed that Russia-linked threat actors have compromised multiple government websites this week. The Computer Emergency Response Team of Ukraine (CERT-UA) said that Russia-linked threat actors have breached multiple government websites this week. The government experts attribute the attack to UAC-0056 group (DEV-0586, unc2589, Nodaria, or Lorec53). “the Government Computer Emergency […]
 Pierluigi Paganini
February 24, 2023
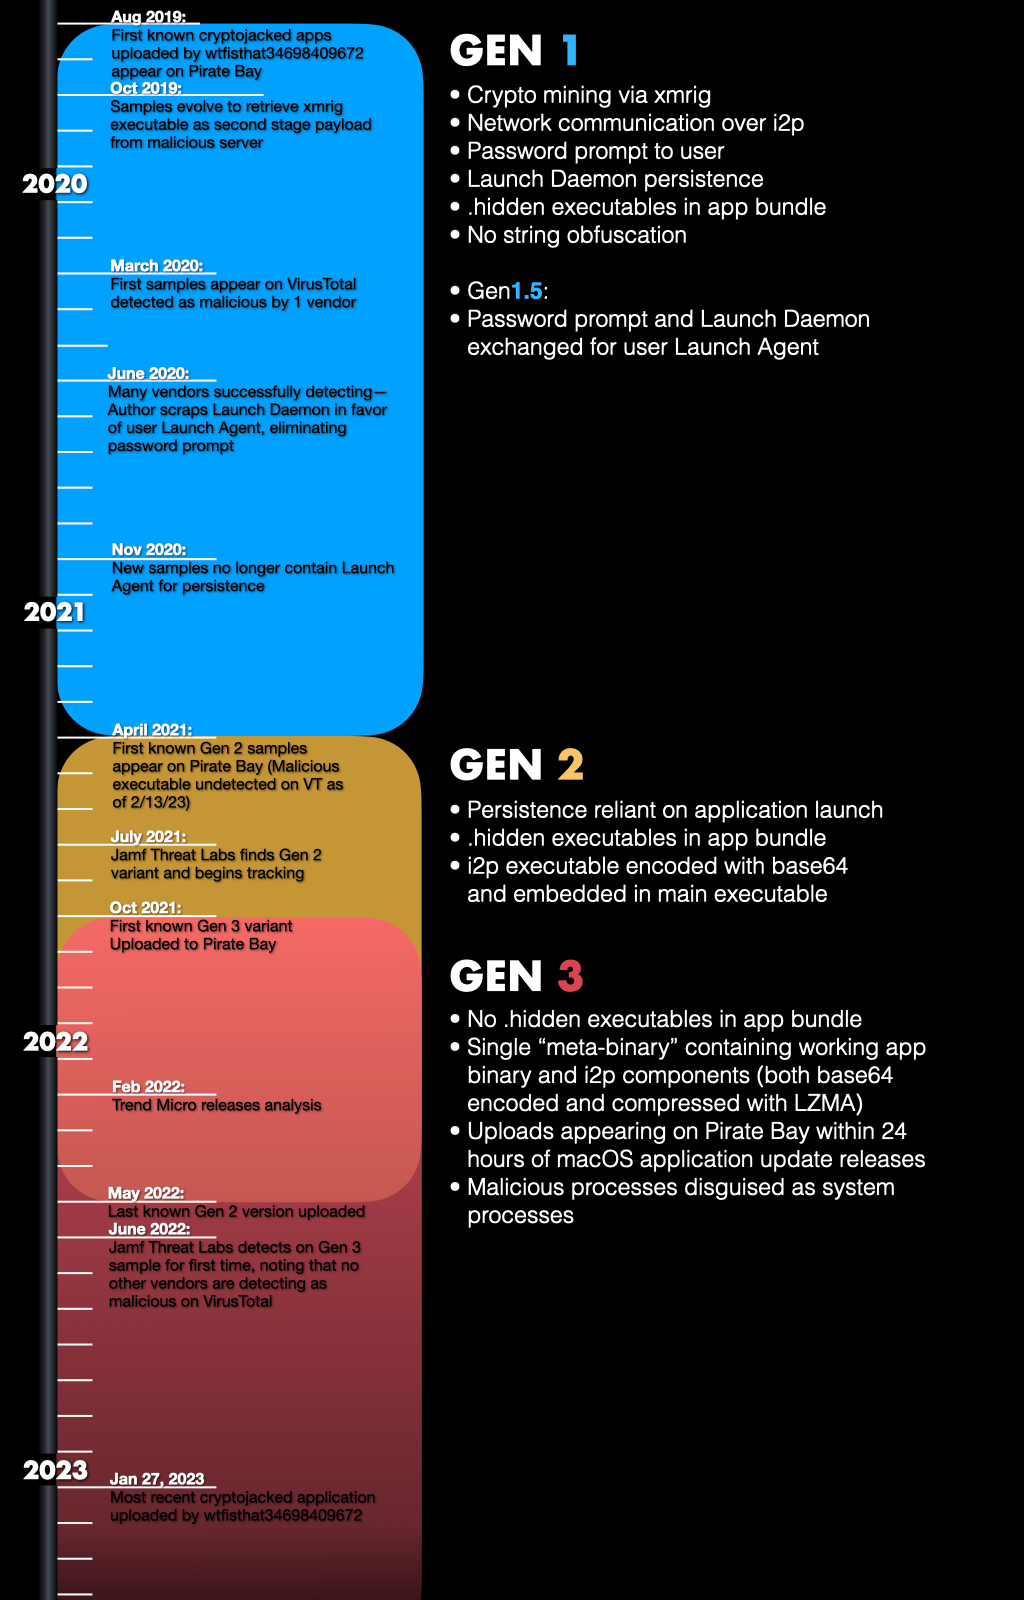
Researchers warn of an evasive cryptojacking malware targeting macOS which spreads through pirated applications Jamf Threat Labs researchers reported that an evasive cryptojacking malware targeting macOS was spotted spreading under the guise of the Apple-developed video editing software, Final Cut Pro. Trojanized versions of legitimate applications are being used to deploy XMRig cryptocurrency miner on […]
 Pierluigi Paganini
February 24, 2023
Dariy Pankov, a Russian VXer behind the NLBrute malware, has been extradited to the United States from Georgia. The Russian national Dariy Pankov, aka dpxaker, is suspected to be the author of the NLBrute malware. The man has been extradited to the United States from Georgia. “Pankov, a citizen and resident of Russia, was taken […]
 Pierluigi Paganini
February 22, 2023
Researchers warn that the MyloBot botnet is rapidly spreading and it is infecting thousands of systems worldwide. The MyloBot botnet has been active since 2017 and was first detailed by cybersecurity firm Deep Instinct in 2018. MyloBot is a highly evasive Windows botnet that supports advanced anti-analysis techniques. The first sample of the bot analyzed by the […]
 Pierluigi Paganini
February 21, 2023
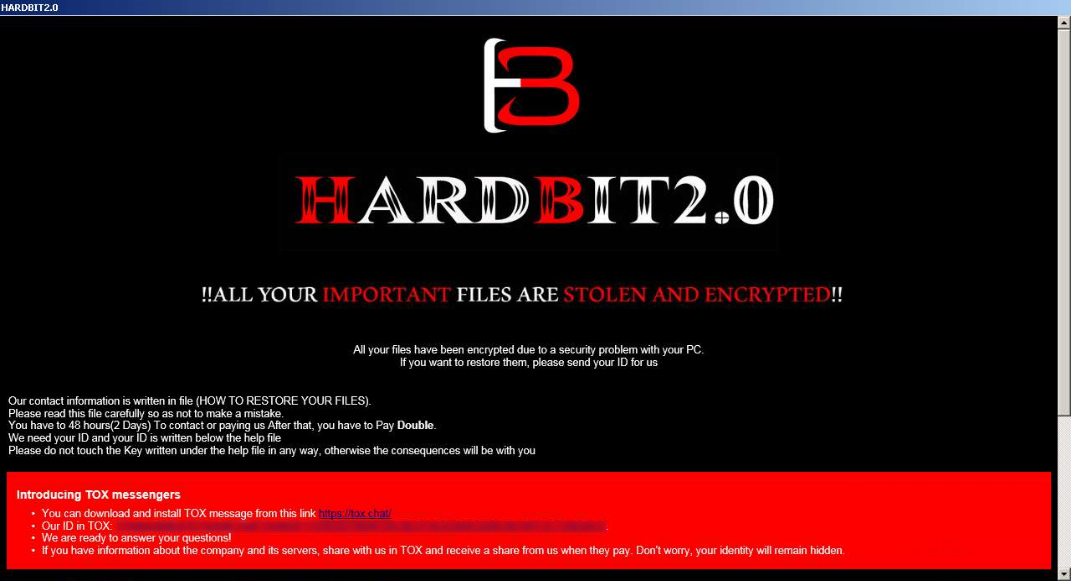
Recently emerged HardBit ransomware gang adjusts their demands so the insurance company would cover the ransom cost. The HardBit ransomware group first appeared on the threat landscape in October 2022, but unlike other ransomware operations, it doesn’t use a double extortion model at this time. The gang threatens victims of further attacks if their ransom […]
Security / September 30, 2026
Artificial Intelligence / September 30, 2026


Security / September 30, 2026


