


 Pierluigi Paganini
 February 01, 2023
Authors of the Prolex PoS malware improved their malicious code to target contactless credit card transactions. The threat actors behind the sophisticated point-of-sale (PoS) malware Prilex have have improved its capabilities to block contactless payment transactions. Researchers from Kaspersky Lab discovered three new versions of the PoS malware designed to target credit cards using NFC technology. […]
 Pierluigi Paganini
February 01, 2023
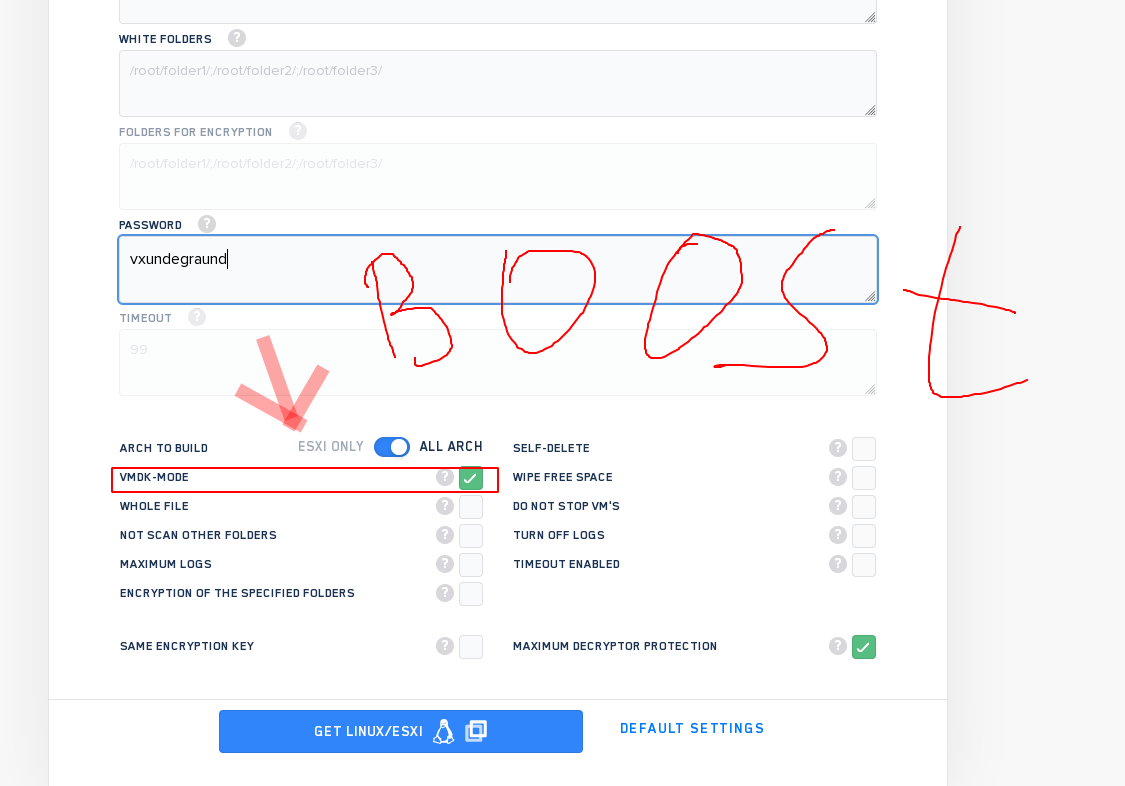
Lockbit ransomware operators have released a new version of their malware, LockBit Green, that also targets cloud-based services. Lockbit ransomware operators have implemented a new version of their malware, dubbed LockBit Green, which was designed to include cloud-based services among its targets. This is the third version of the ransomware developed by the notorious gang, […]
 Pierluigi Paganini
February 01, 2023
Researchers from Resecurity have identified a new version of Nevada Ransomware which recently emerged on the Dark Web right before the start of 2023. Resecurity, California-based cybersecurity company protecting Fortune 500 globally, has identified a new version of Nevada Ransomware which recently emerged on the Dark Web right before the start of 2023. The actors […]
 Pierluigi Paganini
February 01, 2023
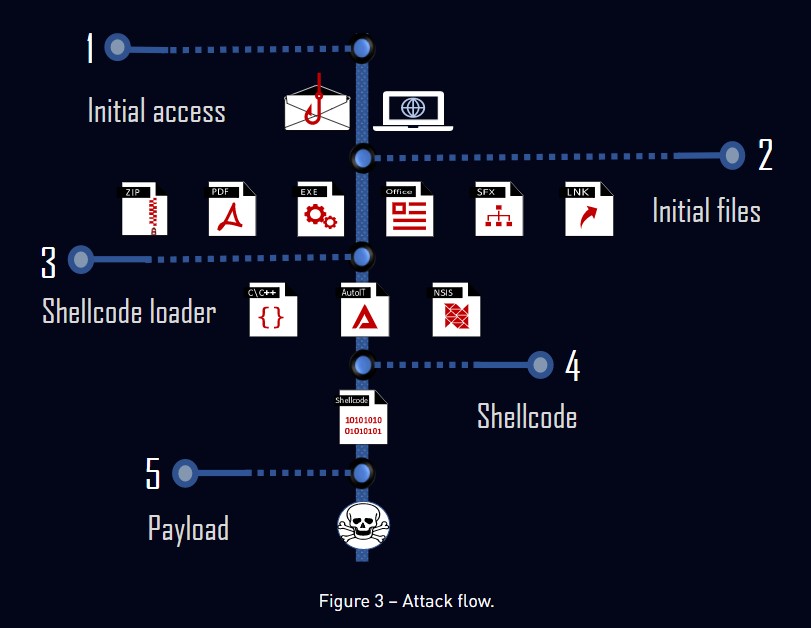
TrickGate is a shellcode-based packer offered as a service to malware authors to avoid detection, CheckPoint researchers reported. TrickGate is a shellcode-based packer offered as a service, which is used at least since July 2016, to hide malware from defense programs. A packer (aka “Crypter” and “FUD”) implements a series of functionalities to make it harder for […]
 Pierluigi Paganini
January 31, 2023
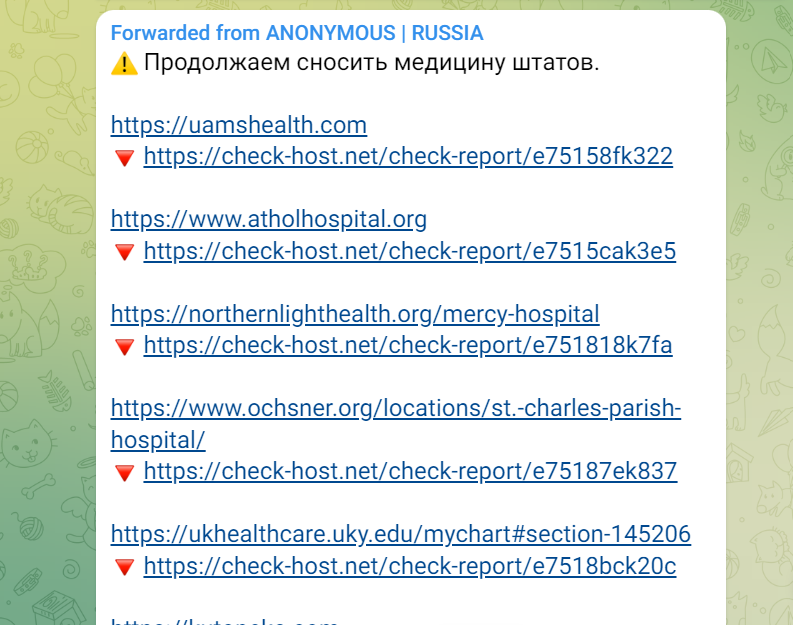
The Pro-Russia group Killnet is launching a series of DDoS attacks against the websites of US healthcare organizations and hospitals. The Pro-Russia group Killnet launched a series of DDoS attacks against US healthcare organizations and hospitals. The group announced the attacks on its Telegram channel, calling for action against the US government healthcare. The list of targets […]
 Pierluigi Paganini
January 30, 2023
The Ukrainian (CERT-UA) discovered five different wipers deployed on the network of the country’s national news agency, Ukrinform. On January 17, 2023, the Telegram channel “CyberArmyofRussia_Reborn” reported the compromise of the systems at the Ukrainian National Information Agency “Ukrinform”. The Ukrainian Computer Emergency Response Team (CERT-UA) immediately investigated the claims and as of January 27, […]
 Pierluigi Paganini
January 30, 2023
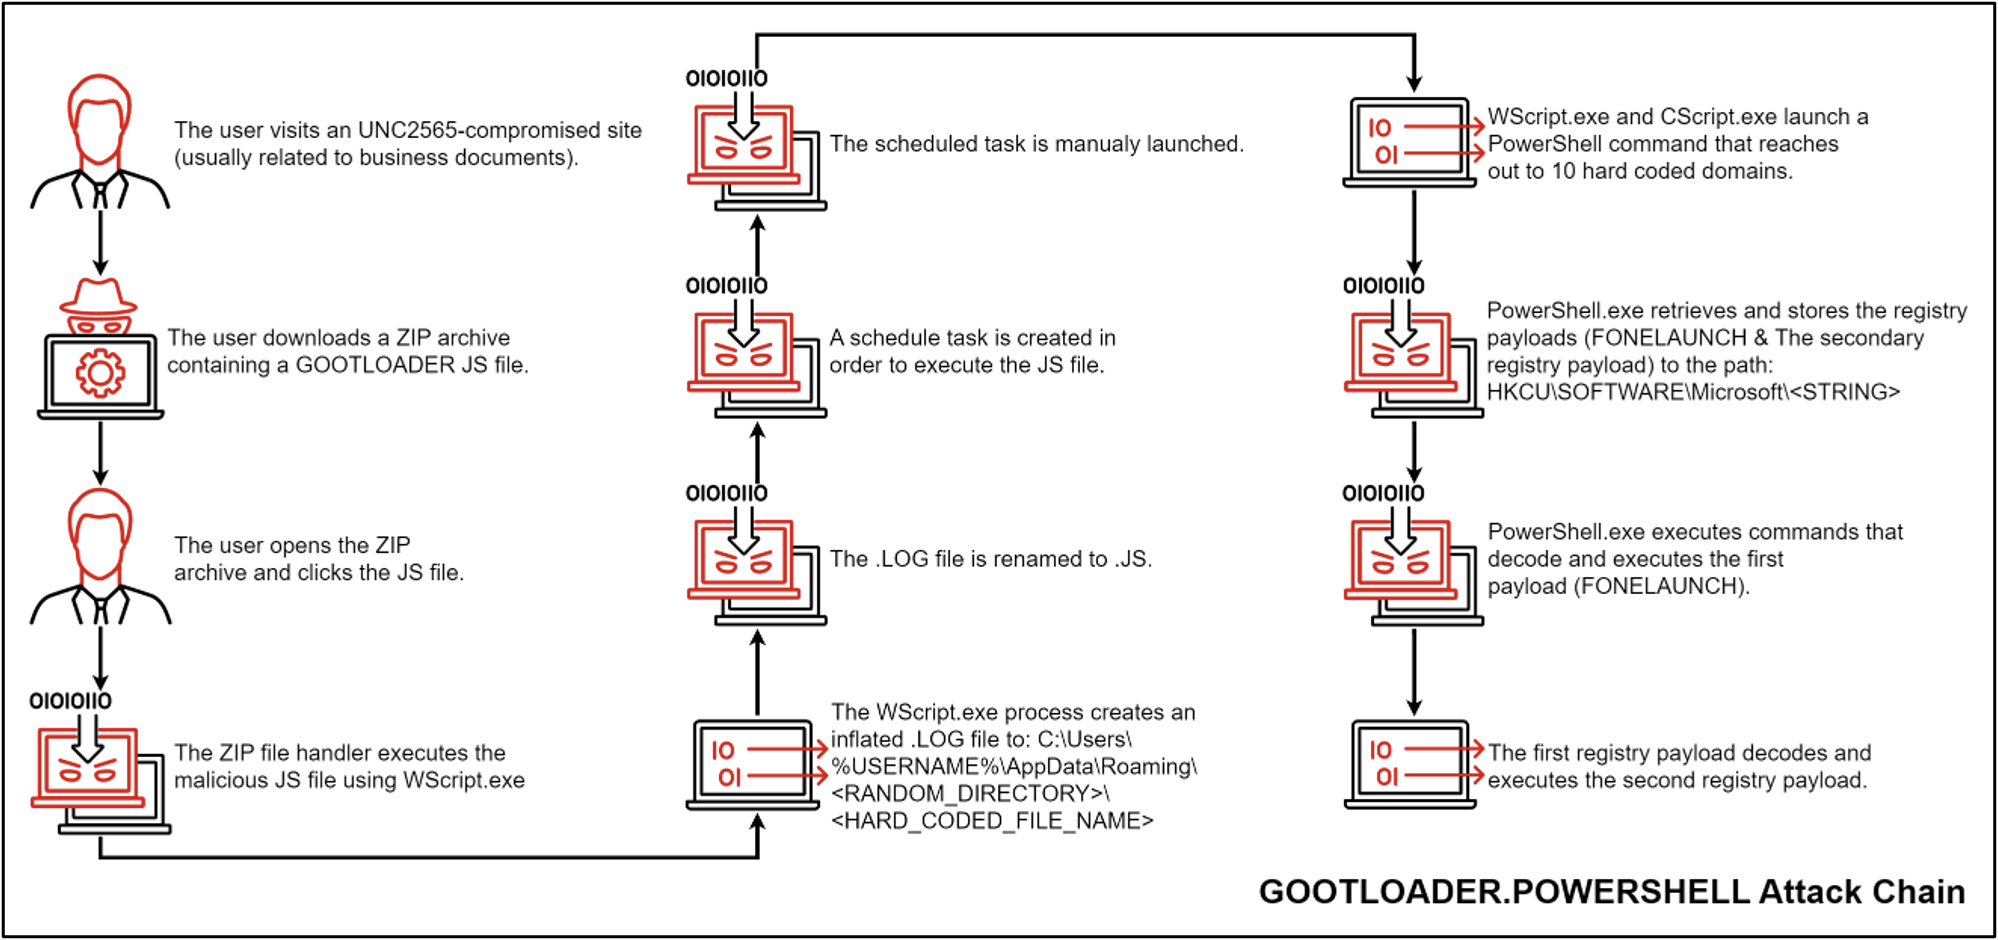
The threat actors behind the GOOTLOADER malware continues to improve their code by adding new components and implementing new obfuscation techniques. Mandiant researchers reported that the UNC2565 group behind the GOOTLOADER malware (aka Gootkit) continues to improve their code by adding new components and implementing new obfuscation techniques. Gootkit runs on an access-a-as-a-service model, it is used […]
 Pierluigi Paganini
January 29, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. Copycat Criminals mimicking Lockbit gang in northern Europe Sandworm APT targets Ukraine with new SwiftSlicer wiper […]
 Pierluigi Paganini
January 28, 2023
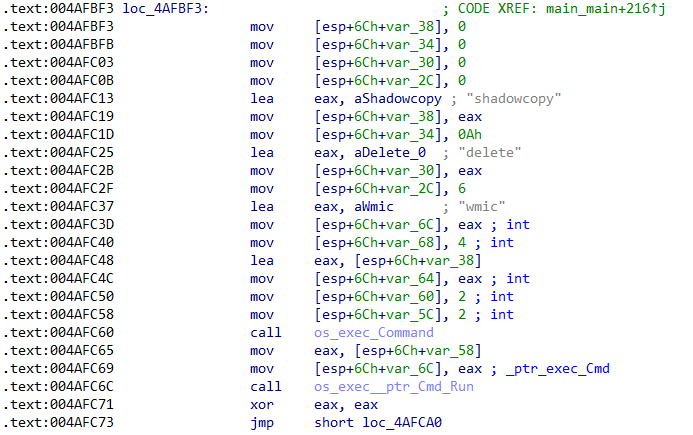
Recent reports of Lockbit locker-based attacks against North European SMBs indicate that local crooks started using Lockbit locker variants. Executive Summary Incident Insights Recently, there has been a significant increase in ransomware attacks targeting companies in northern Europe. These attacks are being carried out using the LockBit locker, which is known to be in use […]
 Pierluigi Paganini
January 28, 2023
Russia-linked Sandworm APT group is behind a new Golang-based wiper, tracked as SwiftSlicer, that hit Ukraine, ESET reports. Researchers from ESET discovered a new Golang-based wiper, dubbed SwiftSlicer, that was used in attacks aimed at Ukraine. The experts believe that the Russia-linked APT group Sandwork (aka BlackEnergy and TeleBots) is behind the wiper attacks. The Sandworm group has been […]
Security / September 30, 2026
Artificial Intelligence / September 30, 2026


Security / September 30, 2026


