 Pierluigi Paganini
 February 22, 2023
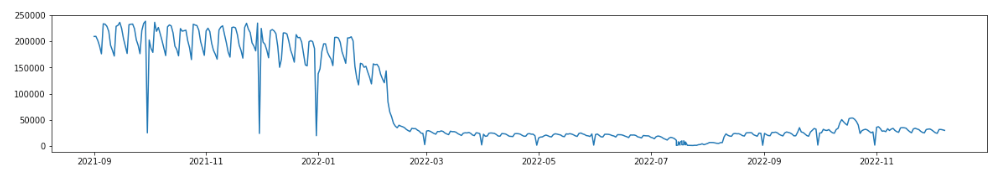
Researchers warn that the MyloBot botnet is rapidly spreading and it is infecting thousands of systems worldwide. The MyloBot botnet has been active since 2017 and was first detailed by cybersecurity firm Deep Instinct in 2018. MyloBot is a highly evasive Windows botnet that supports advanced anti-analysis techniques. The first sample of the bot analyzed by the […]
 Pierluigi Paganini
February 21, 2023
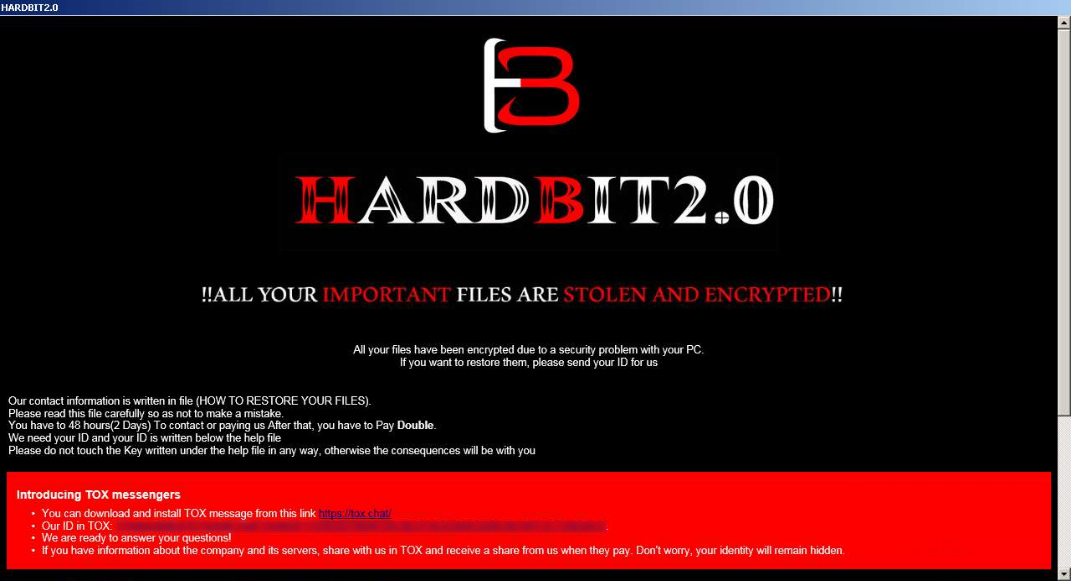
Recently emerged HardBit ransomware gang adjusts their demands so the insurance company would cover the ransom cost. The HardBit ransomware group first appeared on the threat landscape in October 2022, but unlike other ransomware operations, it doesn’t use a double extortion model at this time. The gang threatens victims of further attacks if their ransom […]
 Pierluigi Paganini
February 20, 2023
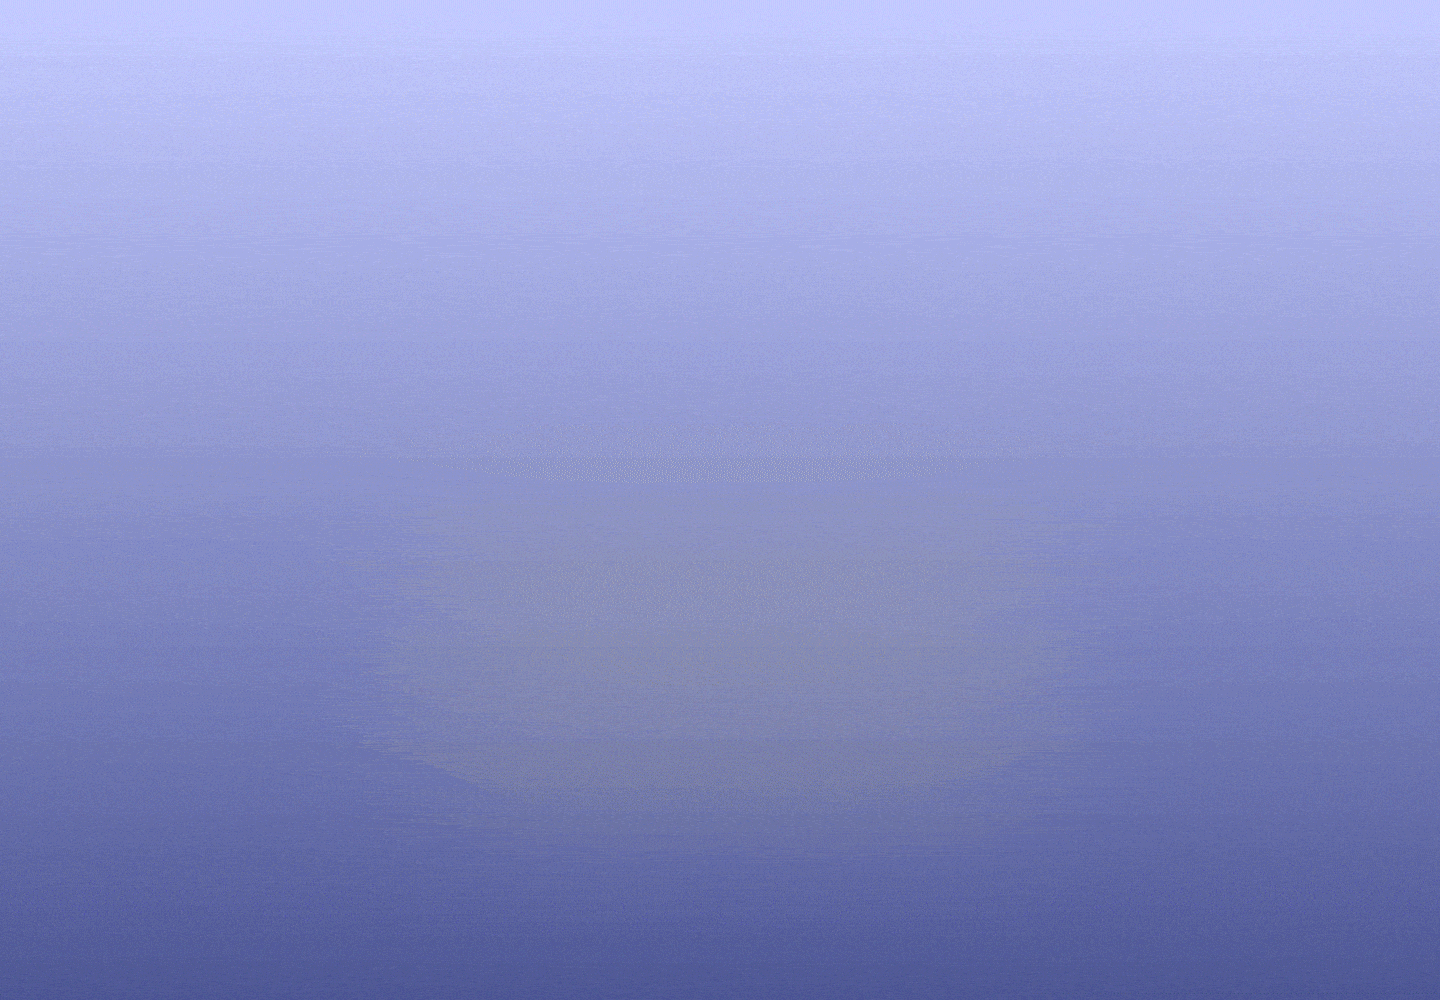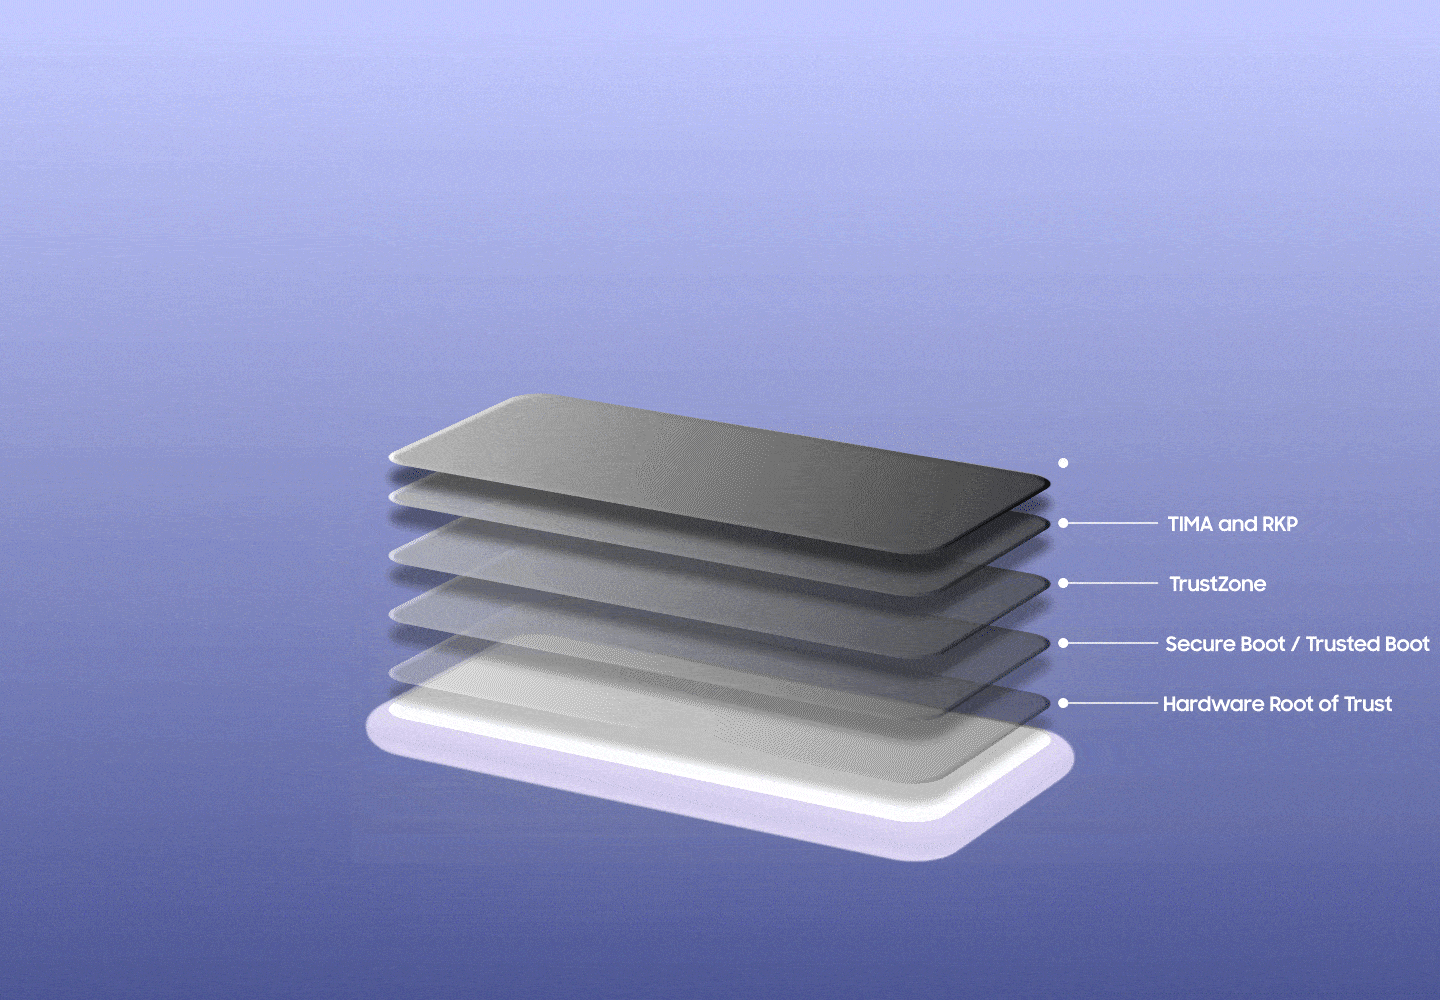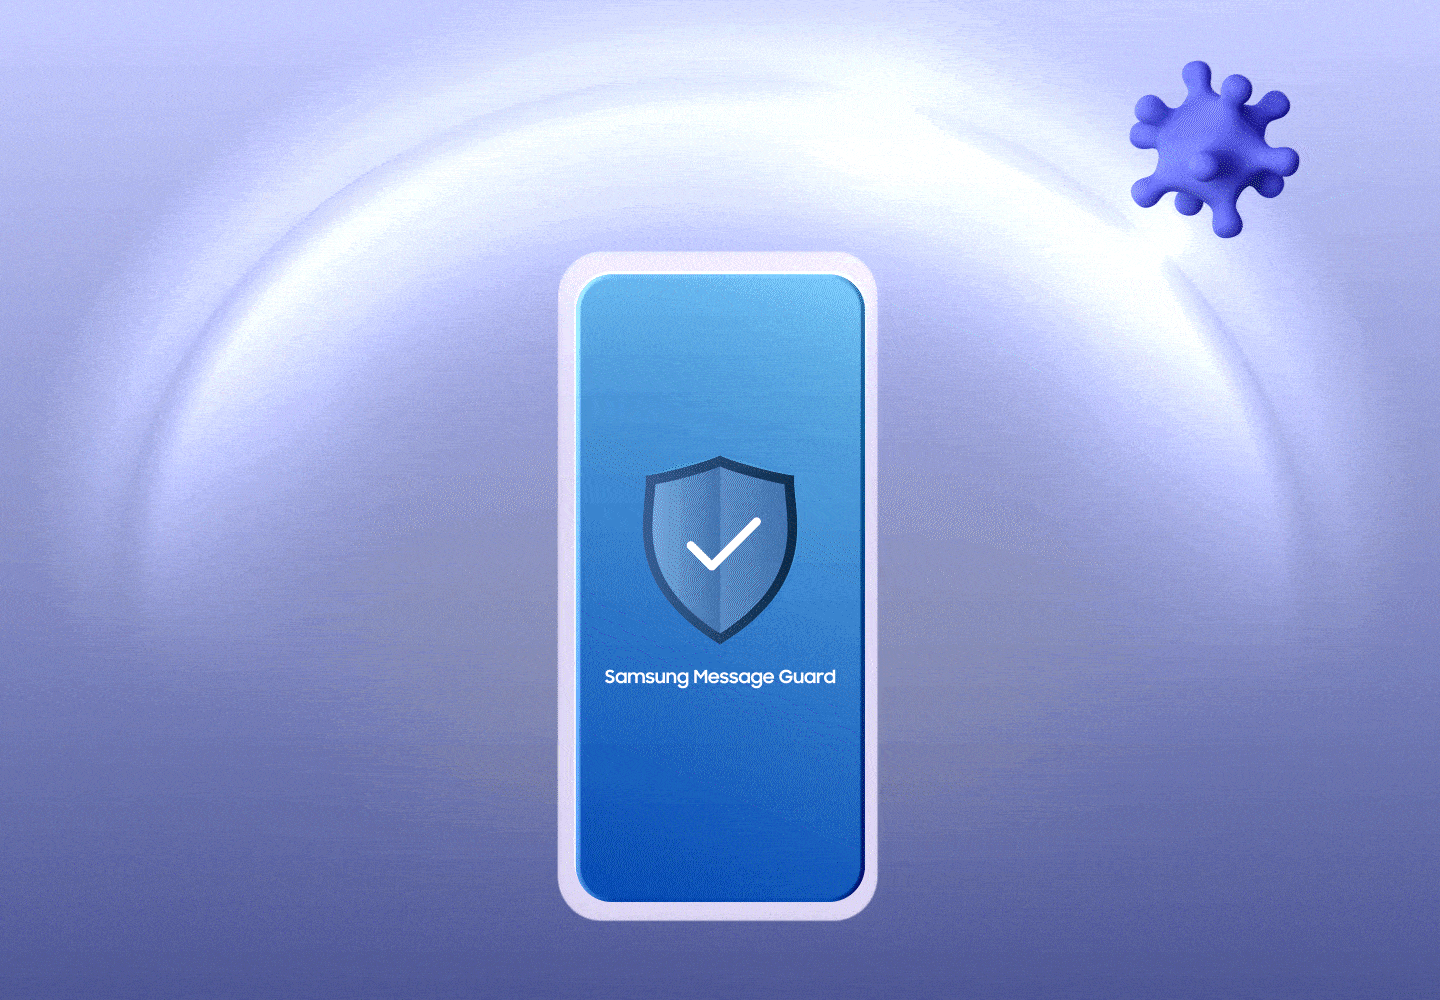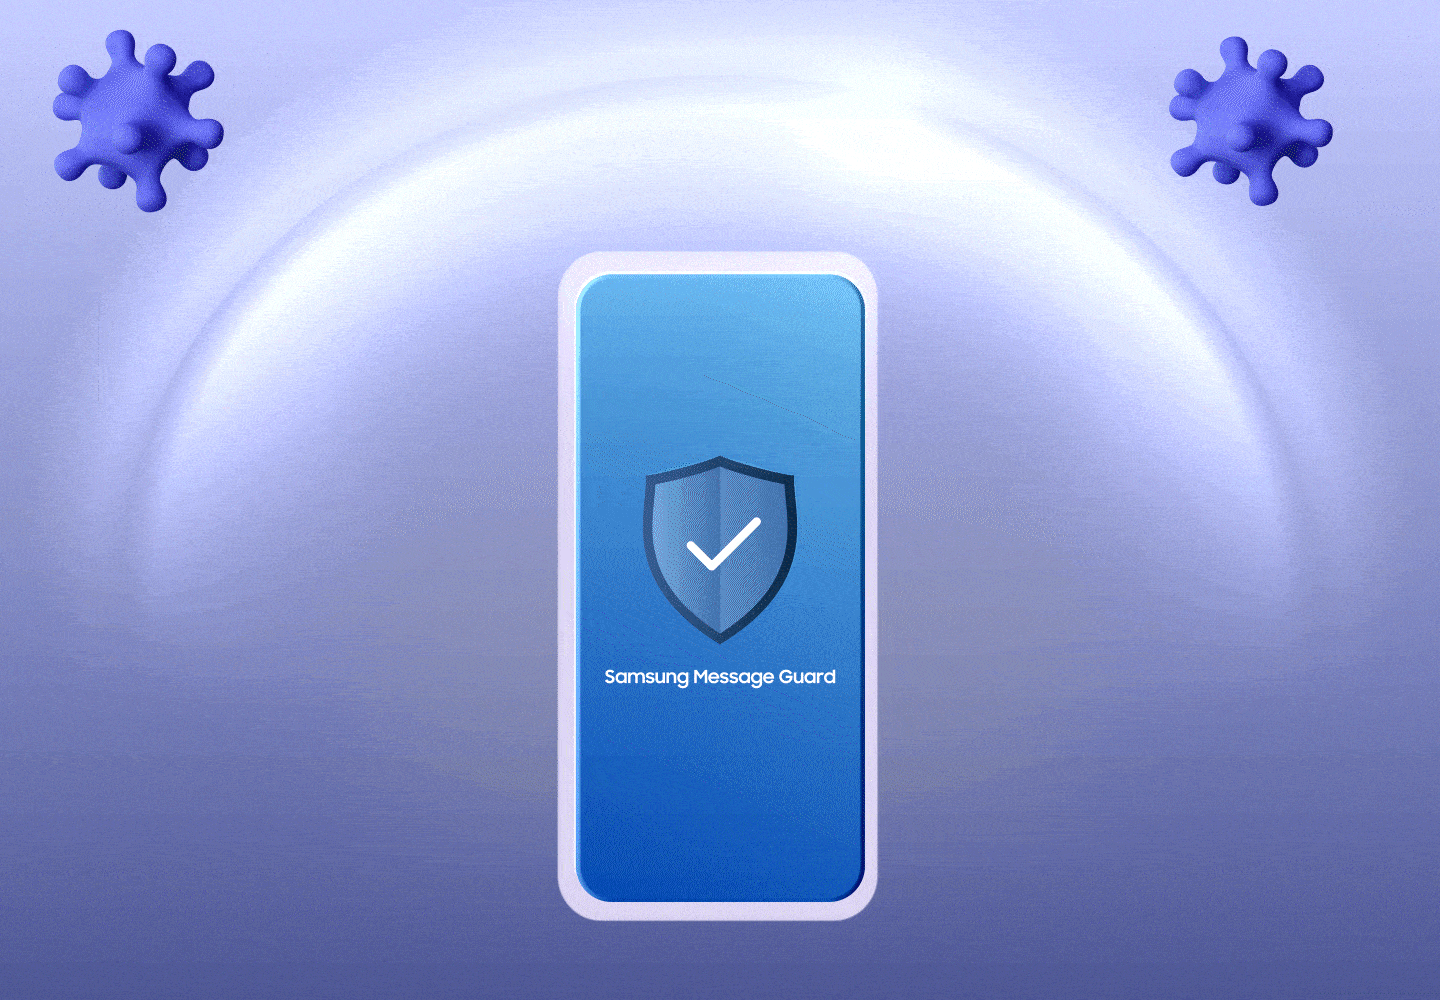
Samsung introduces a new protection feature called Message Guard to protect users from zero-click malware attacks. Samsung announced the implementation of a new security feature called Message Guard that aims at protecting users from malicious code that can be installed via zero-click attacks. Zero-click exploits allow attackers to compromise the target device without any user interaction, for example, a […]
 Pierluigi Paganini
February 20, 2023
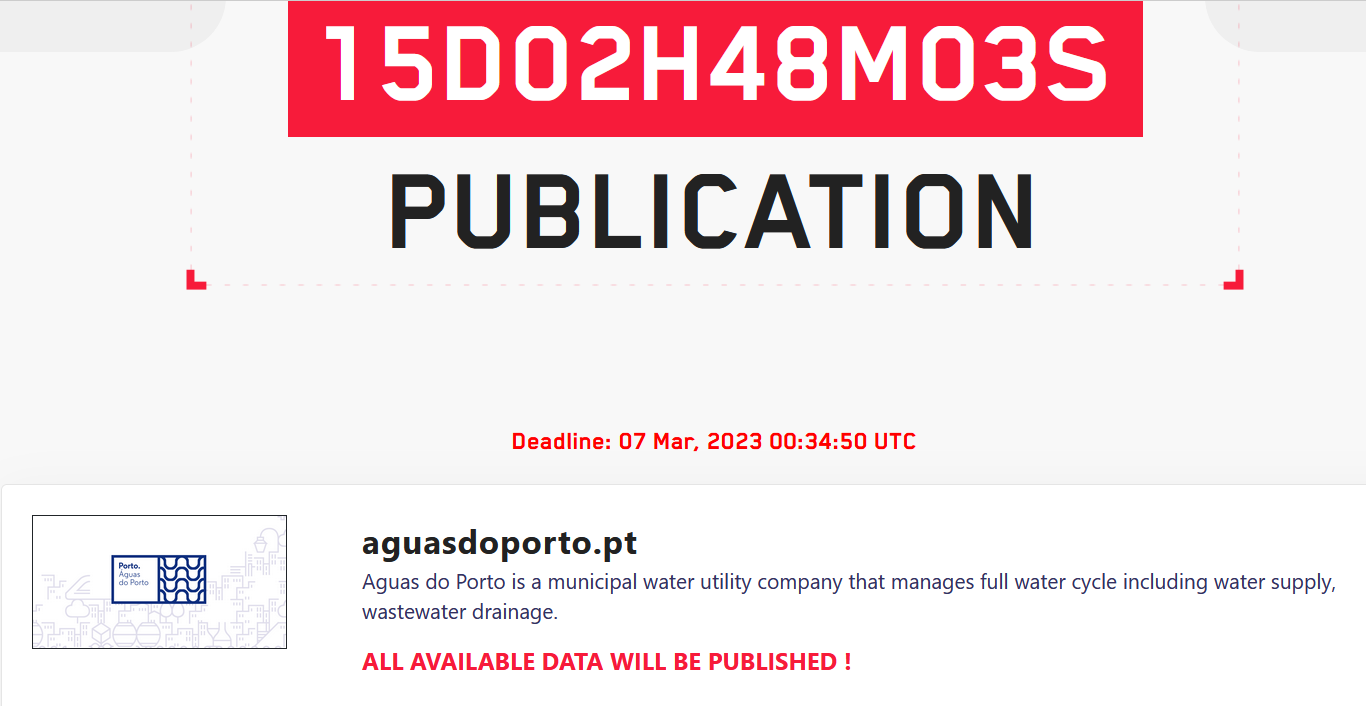
The LockBit ransomware gang claims to have hacked Aguas do Porto, a Portuguese municipal water utility company. The LockBit ransomware gang claims to have hacked Aguas do Porto, a Portuguese municipal water utility company, and is threatening to leak the stolen data. Aguas do Porto is a municipal water utility company that manages the full […]
 Pierluigi Paganini
February 19, 2023
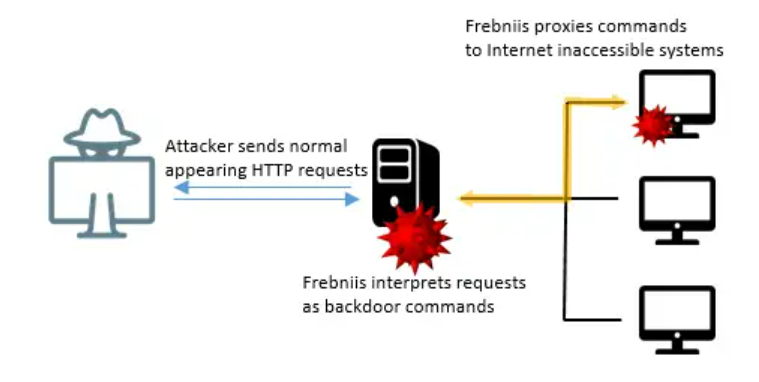
Experts spotted a malware dubbed Frebniis that abuses a Microsoft IIS feature to deploy a backdoor and monitor all HTTP traffic to the system. Broadcom Symantec researchers have spotted a new malware, tracked as Frebniis, that abuses Microsoft Internet Information Services (IIS) to deploy a backdoor and monitor all HTTP traffic to the infected system, […]
 Pierluigi Paganini
February 19, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. Twitter will allow using the SMS-based two-factor authentication (2FA) only to its Blue subscribers GoDaddy […]
 Pierluigi Paganini
February 16, 2023
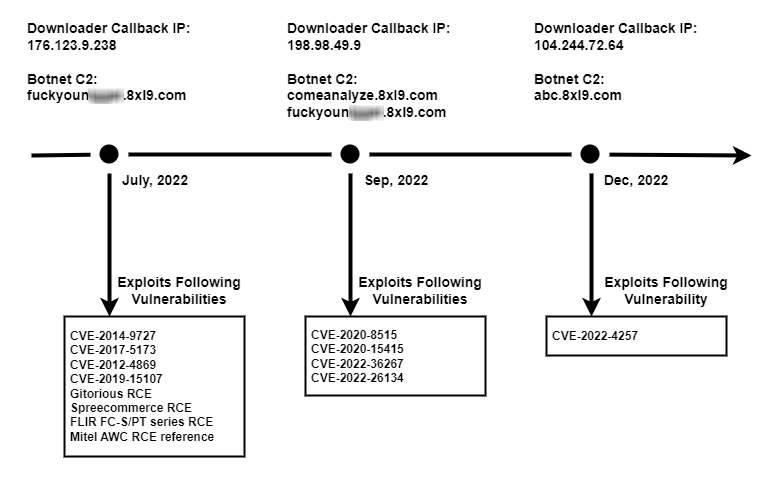
During the second half of 2022, a variant of the Mirai bot, tracked as V3G4, targeted IoT devices by exploiting tens of flaws. Palo Alto Networks Unit 42 researchers reported that a Mirai variant called V3G4 was attempting to exploit several flaws to infect IoT devices from July to December 2022. Below is the list […]
 Pierluigi Paganini
February 16, 2023
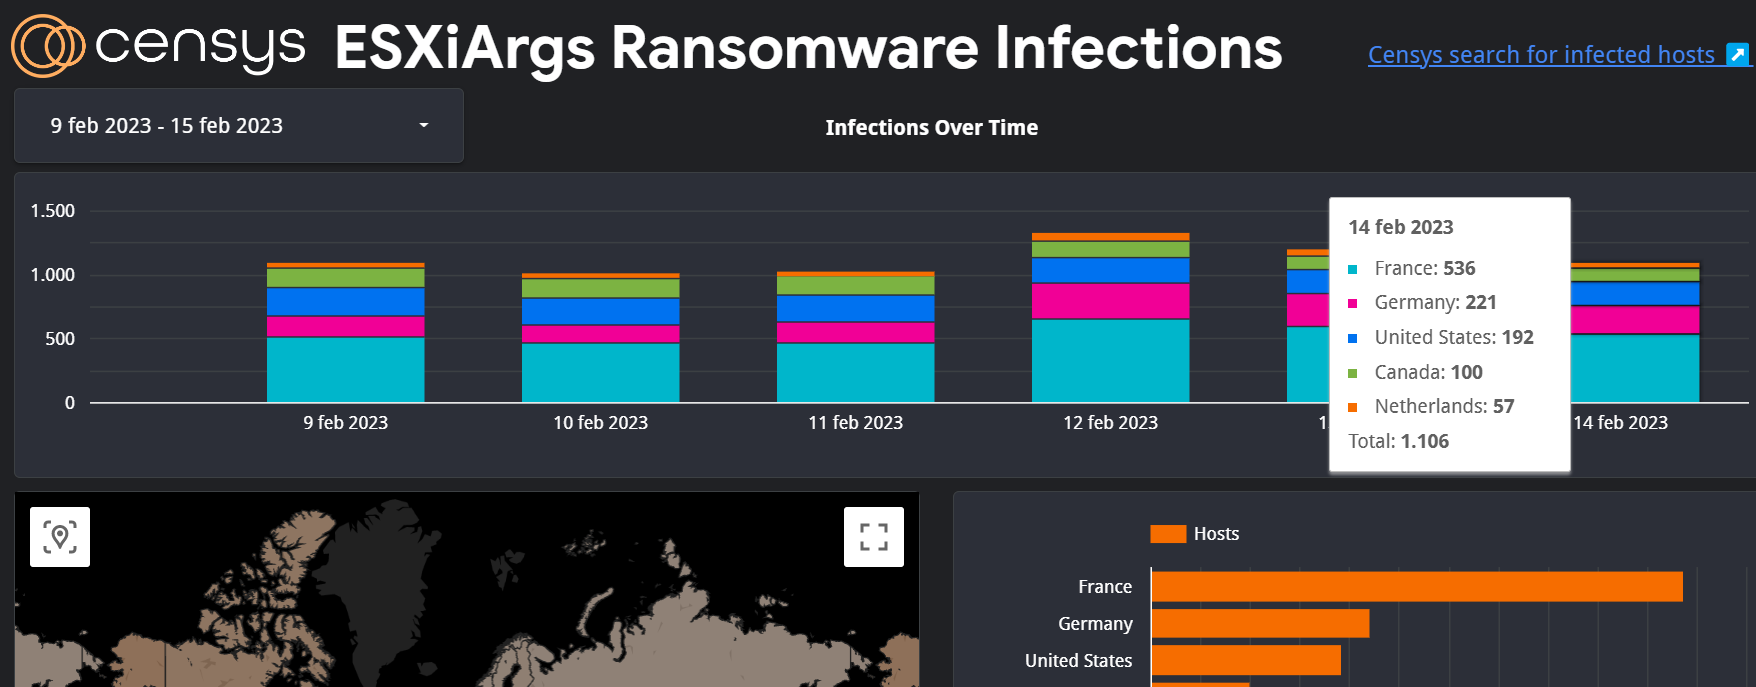
ESXiArgs ransomware continues to spread in Europe, most of the recent infections were observed in France, Germany, the Netherlands, the UK, and Ukraine Researchers from Censys reported that more than 500 hosts have been infected in a new wave of ESXiArgs ransomware attacks, most of which are in France, Germany, the Netherlands, and the U.K.. […]
 Pierluigi Paganini
February 16, 2023
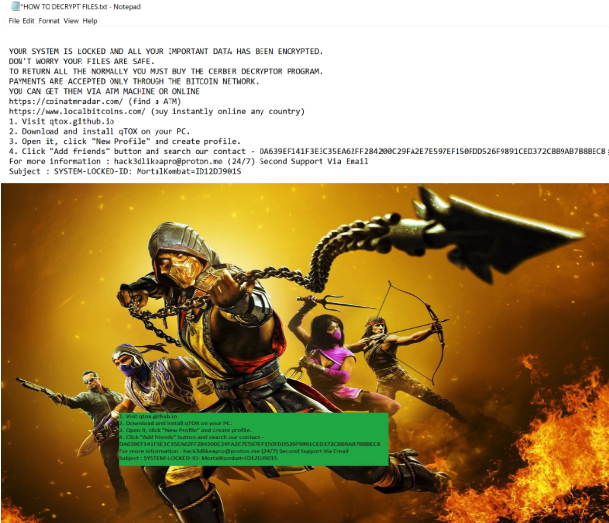
Talos researchers observed a financially motivated threat actor using a new ransomware dubbed MortalKombat and a clipper malware named Laplas. Since December 2022, Cisco Talos researchers have been observing an unidentified financially motivated threat actor deploying two new malware, the recently discovered MortalKombat ransomware and a GO variant of the Laplas Clipper malware. The threat actor […]
 Pierluigi Paganini
February 16, 2023
Hyundai and Kia car makers are releasing an emergency software update to fix a flaw that can allow stealing a car with a USB cable. Carmakers Hyundai and KIA are rolling out an emergency update for the software shipped with several car models. The update addresses a bug that can be exploited by thieves to […]