 Pierluigi Paganini
 October 01, 2017
According to Kaspersky Lab, sixty percent of institutions in Saudi Arabia have experienced malware-based attacks over the past 12 months. Malware continues to be one of the most dangerous threats for organizations worldwide, and data recently disclosed by security firms. According to Kaspersky Lab, Saudi Arabia is under a constant malware-based attack, the experts reported that […]
 Pierluigi Paganini
October 01, 2017
Cisco researchers discovered a malware campaign abusing a legitimate VMware binary to spread a banking Trojan. The threat actor behind the campaign uses multiple methods of re-direction when infecting the victims’ machines in order to remain under the radar, it also implemented a variety of anti-analysis techniques. The malware is written in Delphi, a novelty for […]
 Pierluigi Paganini
September 28, 2017
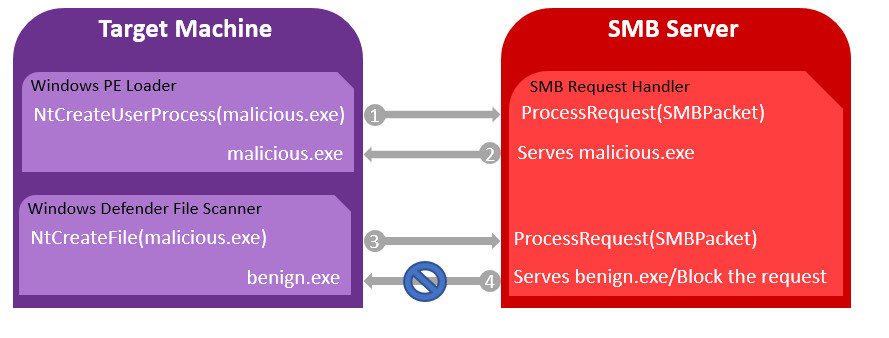
Researchers have developed an attack method dubbed Illusion Gap for bypassing Windows Defender that will allow avoiding antivirus detection. Researchers from security firm CyberArk have devised a new technique dubbed ‘Illusion Gap’ that allows attackers to bypass Windows Defender. The technique leverages on the fact that Windows Defender detection can be bypassed by tricking the antivirus into […]
 Pierluigi Paganini
September 27, 2017
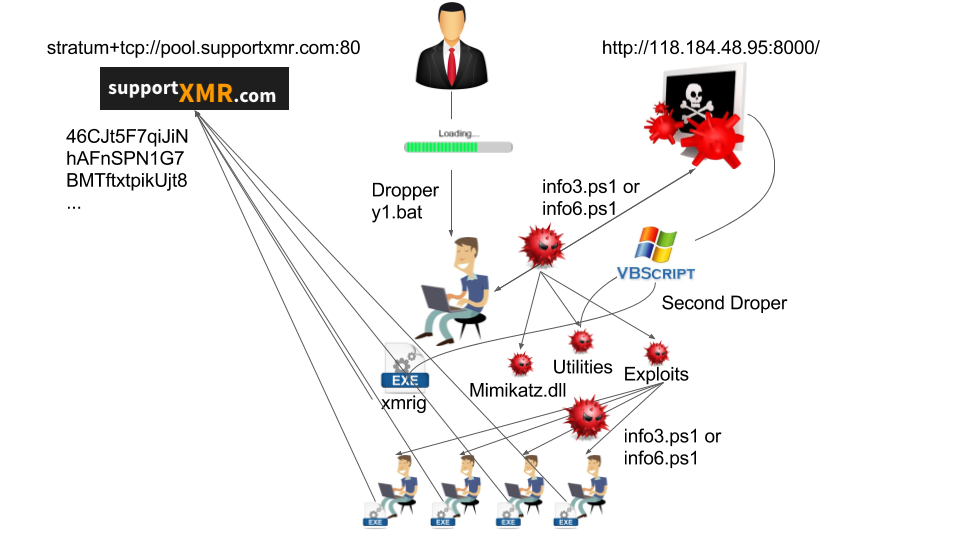
The popular security expert Marco Ramilli shared the analysis of a cryptoworm having significant capabilities, enjoy the report! Introduction. Today I want to share a nice Malware analysis having an interesting flow. The “interesting” adjective comes from the abilities the given sample owns. Capabilities of exploiting, hard obfuscations and usage of advanced techniques to steal […]
 Pierluigi Paganini
September 27, 2017
Security experts at Trend Micro have recently spotted a new strain of Android malware, dubbed ZNIU, that exploits the Dirty COW Linux kernel vulnerability. The Dirty COW vulnerability was discovered by the security expert Phil Oester in October 2016, it could be exploited by a local attacker to escalate privileges. The name ‘Dirty COW’ is due to the fact that it’s […]
 Pierluigi Paganini
September 26, 2017
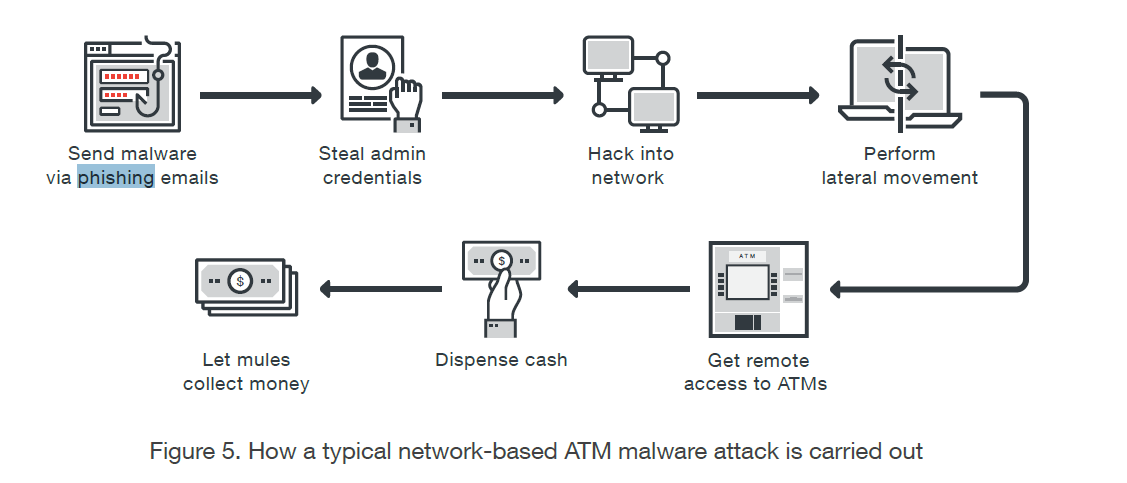
Cyber criminals are targeting ATM machines through the banks’ networks, the operations involve squads of money mules for the cashout. The Europe’s policing agency warns of a rise of cyber attacks against ATM machines. Criminal organizations are targeting ATM machines through the banks’ networks, the operations involve squads of money mules for the cashout. “The malware being used has […]
 Pierluigi Paganini
September 25, 2017
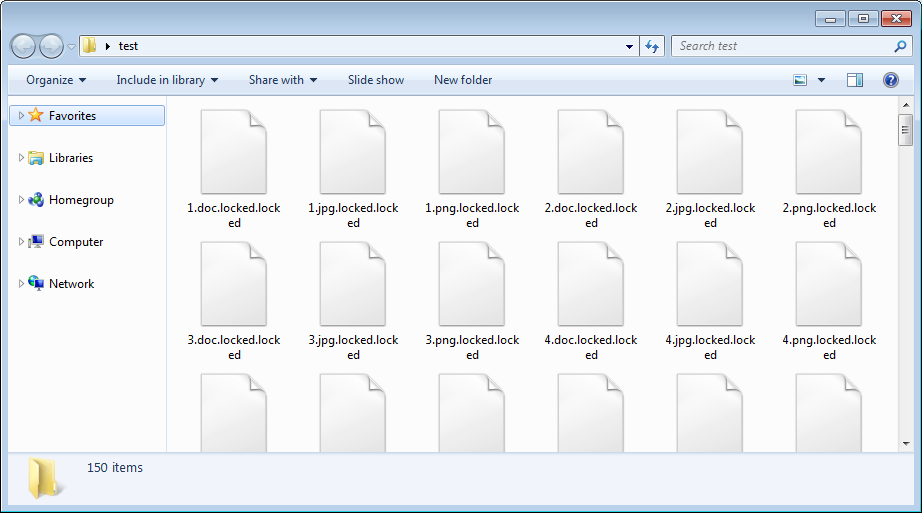
The RedBoot ransomware encrypts files on the infected computer, replaces the Master Boot Record and then modifies the partition table. Malware Blocker researcher discovered a new bootlocker ransomware, dubbed RedBoot, that encrypts files on the infected computer, replaces the Master Boot Record (MBR) of the system drive and then modifies the partition table. The experts noticed that […]
 Pierluigi Paganini
September 23, 2017
I’m proud to share with you the second report produced by Z-Lab, the Malware Lab launched by the company CSE CybSec. Enjoy the Analysis Report Petya. CybSec Enterprise recently launched a malware Lab called it Z-Lab, that is composed of a group of skilled researchers and lead by Eng. Antonio Pirozzi. It’s a pleasure for me to […]
 Pierluigi Paganini
September 22, 2017
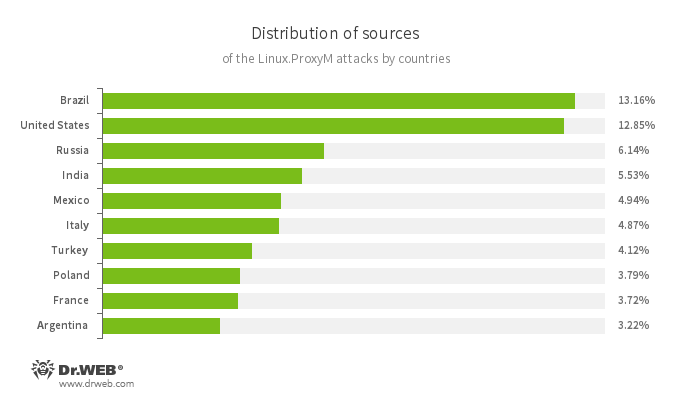
Experts at security firm Doctor Web discovered a new botnet of IoT devices leveraging the Linux.ProxyM, that is used by crooks for mass spam mailings. The most popular thingbot since now is the Mirai, but it isn’t the only one targeting Linux-based internet-of-things (IoT) devices. Researchers with security firm Doctor Web discovered a new botnet of […]
 Pierluigi Paganini
September 22, 2017
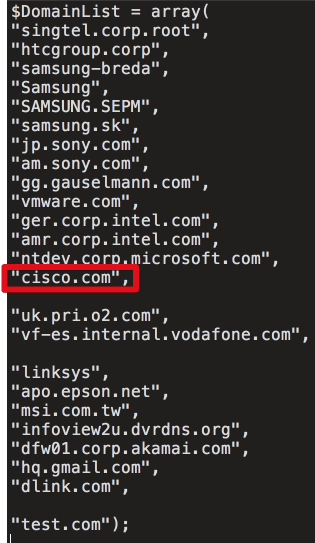
The threat actor that recently compromised the supply chain of the CCleaner software targeted at least 20 tech firms with a second-stage malware. The threat actor that recently compromised the supply chain of the CCleaner software to distribute a tainted version of the popular software targeted at least 20 major international technology firms with a […]