 Pierluigi Paganini
 September 21, 2017
Security researchers at ESET have uncovered a surveillance campaign using a new variant of FinFisher spyware, also known as FinSpy. Finfisher infected victims in seven countries and experts believe that in two of them the major internet providers have been involved. “New surveillance campaigns utilizing FinFisher, infamous spyware known also as FinSpy and sold to governments and their […]
 Pierluigi Paganini
September 21, 2017
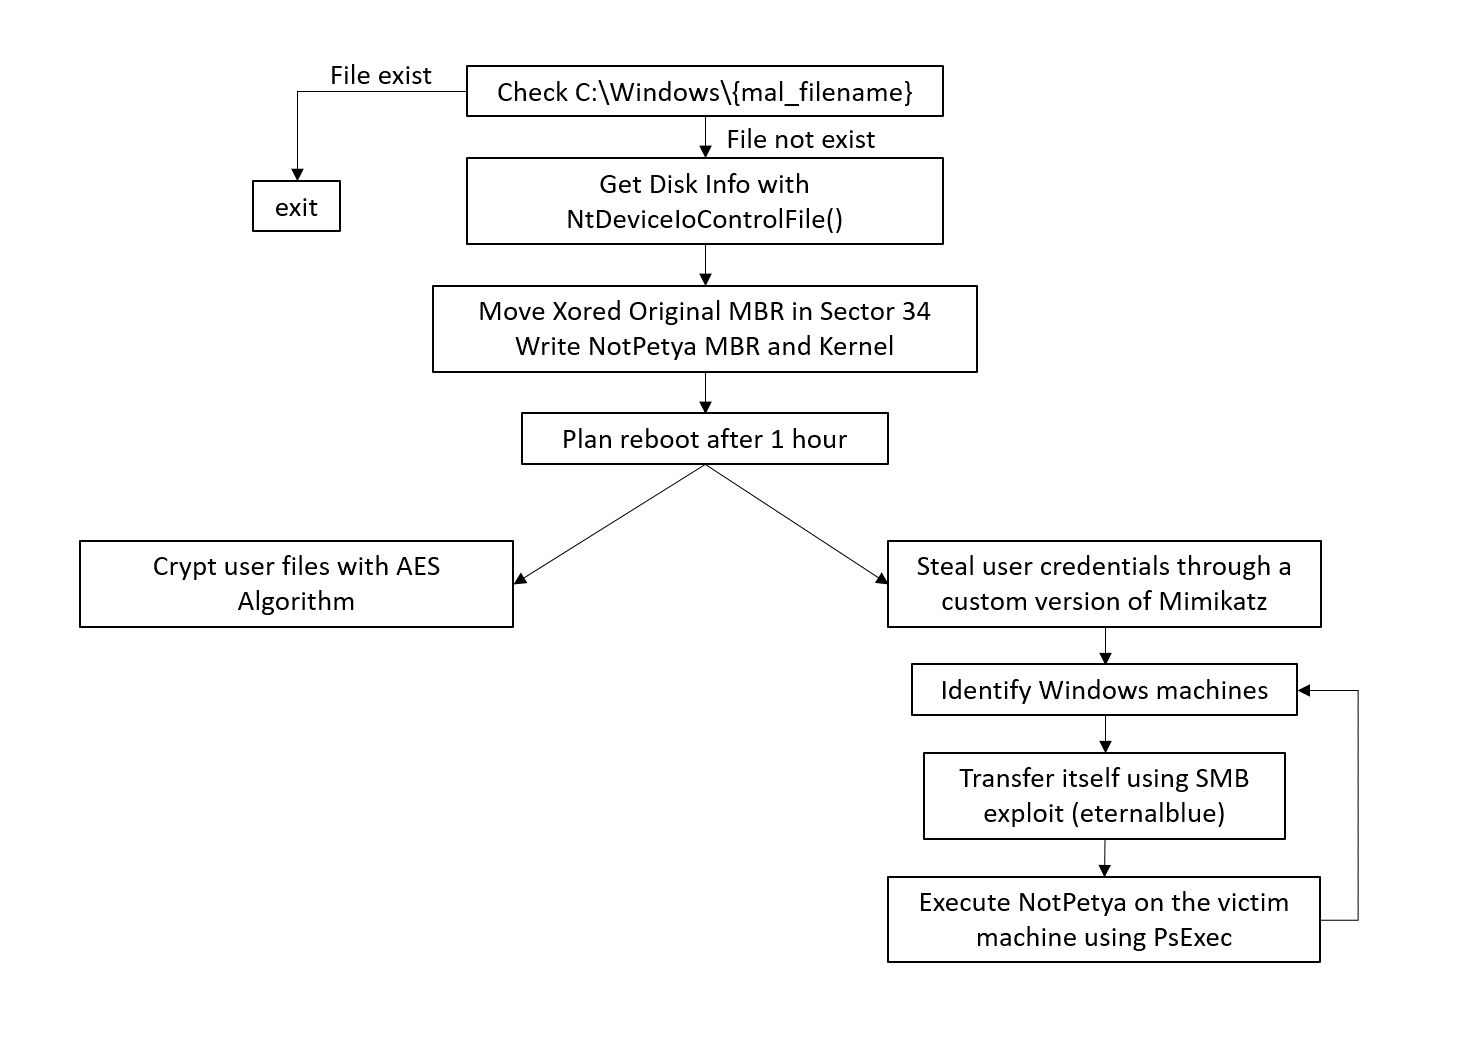
FedEx is the last firm in order of time that disclosed the cost caused by the massive NotPetya, roughly $300m in lost business and response costs. The malware compromised systems worldwide, most of them in Ukraine, the list of victims is long and includes the US pharmaceutical company Merck, the shipping giant Maersk, the Ukraine’s central […]
 Pierluigi Paganini
September 18, 2017
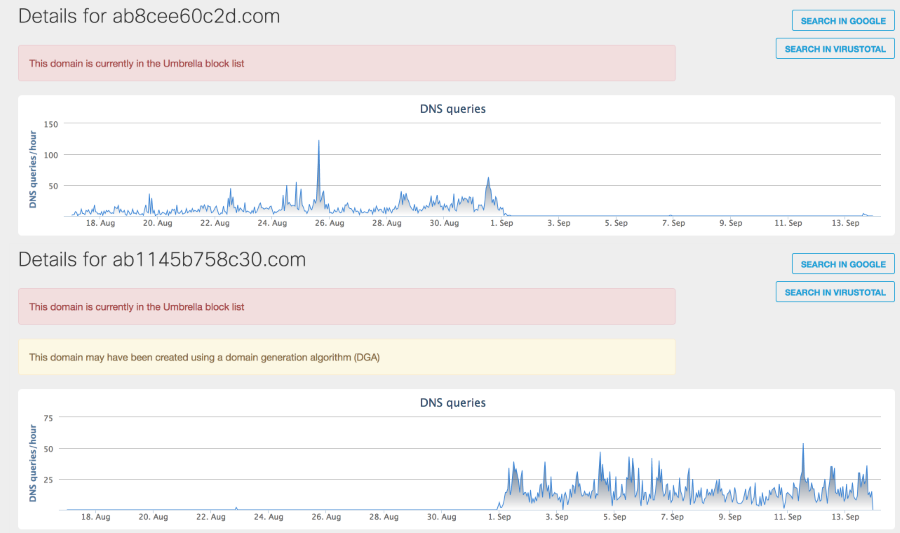
CCleaner app version 5.33 that was available for download between August 15 and September 12 was modified to include the Floxif malware Bad news for the users of the CCleaner app, according to researchers with Cisco Talos, version 5.33 that was available for download between August 15 and September 12 was modified to include the Floxif […]
 Pierluigi Paganini
September 18, 2017
I’m proud to share with you the first report produced by Z-Lab, the Malware Lab launched by the company CSE CybSec. Enjoy the Analysis Report NotPetya. As most of you already know I have officially presented my new Co a couple of months ago, CybSec Enterprise is its name and we already started to work on […]
 Pierluigi Paganini
September 14, 2017
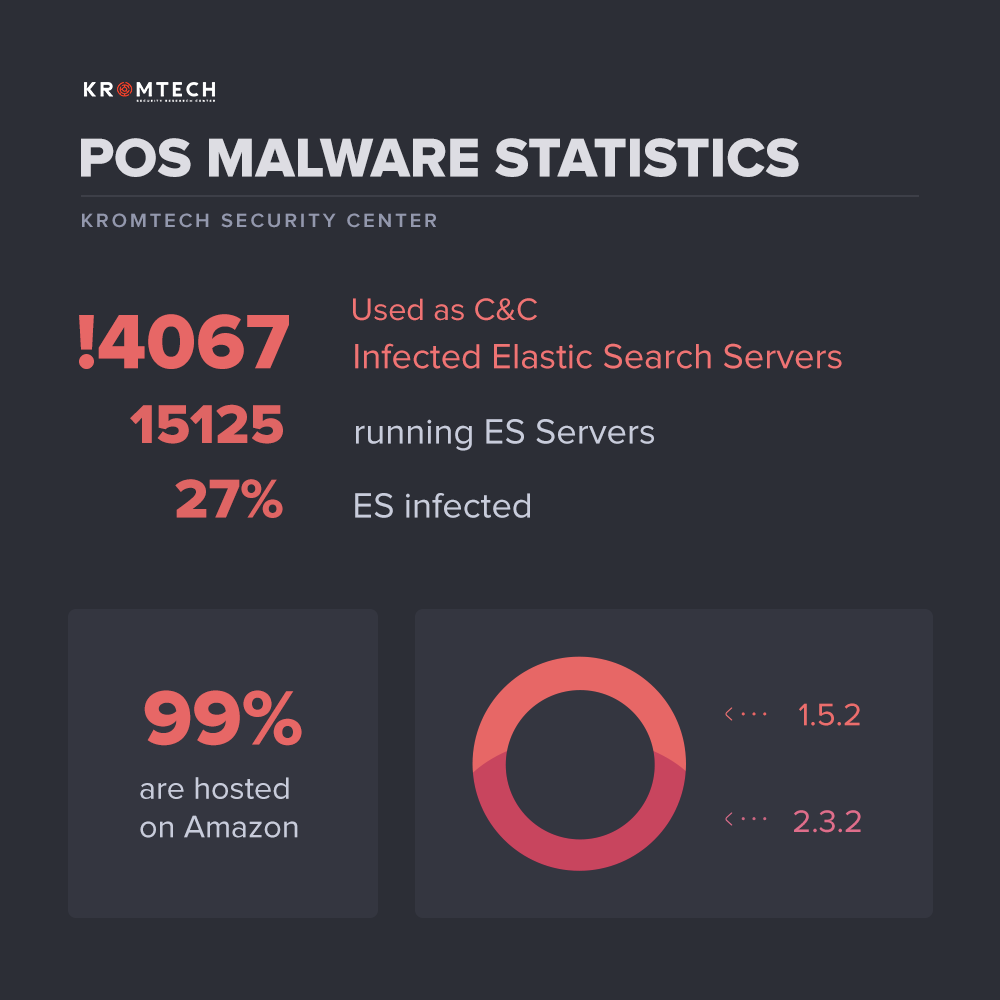
Experts discovered 4,000 compromised installations on Amazon AWS of open source analytics and search tool Elasticsearch that were running PoS malware. Security researchers from the firm Kromtech have discovered 4,000 compromised instances of open source analytics and search tool Elasticsearch that were running PoS malware. According to Kromtech, this is just a portion of the overall number of compromised […]
 Pierluigi Paganini
September 10, 2017
Crooks are abusing Facebook CDN servers to deliver malware and evading detection exploiting the trust in the CDN network of the social networking giant. Crooks are abusing Facebook CDN (Content Delivery Network) servers to store malware and to deliver it evading detection exploiting the trust in the CDN network of the social network giant. Researchers from […]
 Pierluigi Paganini
September 07, 2017
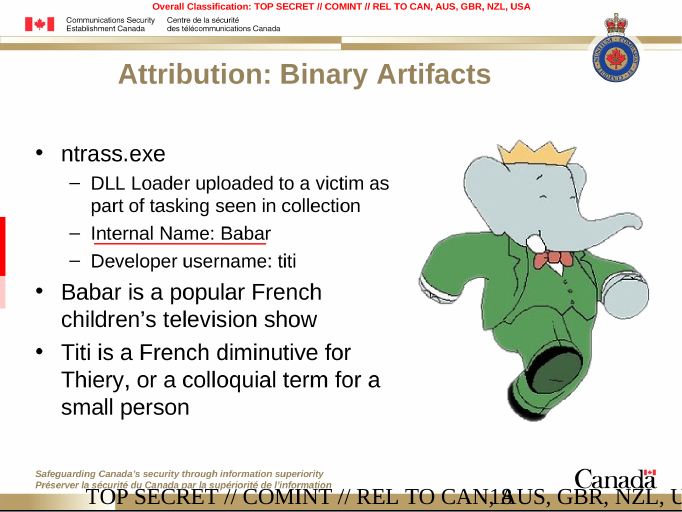
Malware researchers at Palo Alto Networks have spotted a 2007 variant of Babar, a strain of malware likely designed by the French Intelligence. In March 2015, researchers detected Babar for the first time, analysis led them into believing it was a product of the French intelligence. According to the experts, Babar malware was used by the General Directorate for […]
 Pierluigi Paganini
September 07, 2017
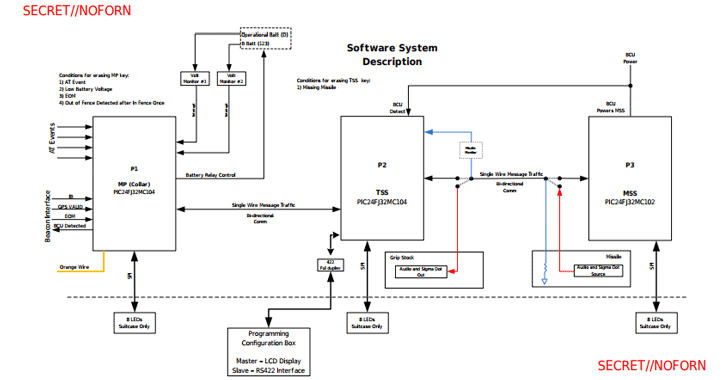
WikiLeaks has published a new batch of documents that details the Project Protego, a secret CIA Missile Control System Project for fighters Another week, another batch of CIA Vault7 leaks was published by Wikileaks. This time the documents provide details about the Project Protego, a CIA Secret Missile Control System. WikiLeaks published four secret documents from […]
 Pierluigi Paganini
September 07, 2017
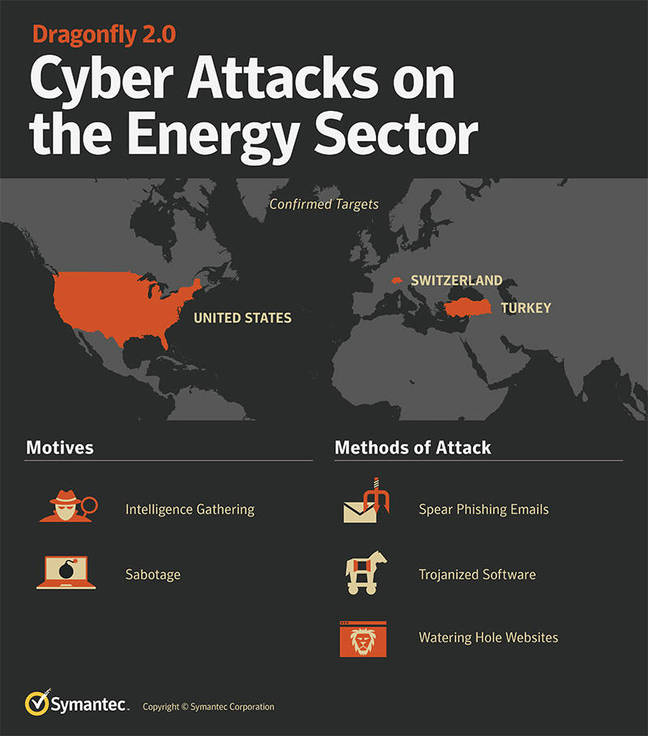
While the first Dragonfly campaigns appear to have been a more reconnaissance phase, the Dragonfly 2.0 campaign seems to have destructive purposes. Symantec has spotted a new wave of cyber attacks against firms in the energy sector powered by the notorious Dragonfly group. The Dragonfly group, also known as Energetic Bear, has been active since at […]
 Pierluigi Paganini
September 06, 2017
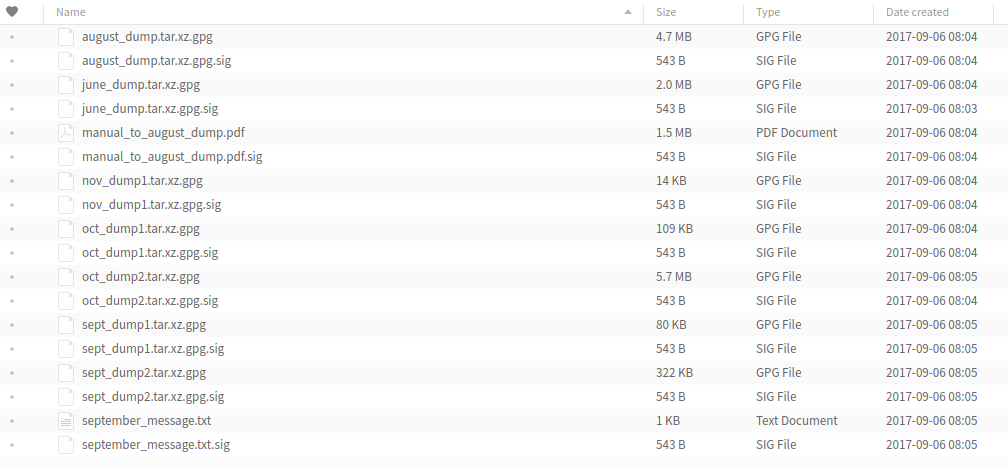
The dreaded hacking group ShadowBrokers posted a new message, promising to deliver two data dumps a month as part its monthly dumps. The notorious group ShadowBrokers is back with announcing new interesting changes to their Dump Service. The hackers published a new message on the Steemit platform announcing new changed to their service. “Missing theshadowbrokers? If someone […]