 Pierluigi Paganini
 July 26, 2017
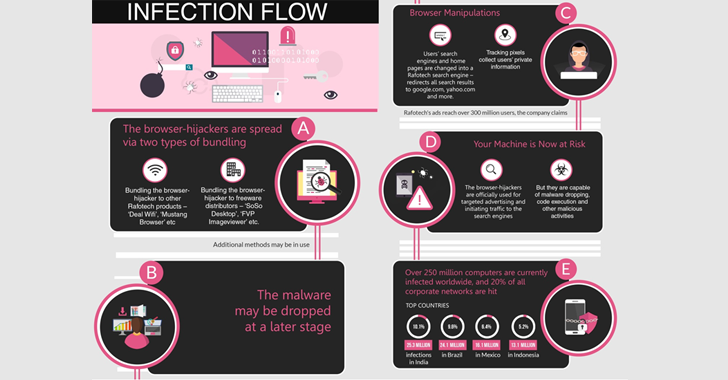
Chinese authorities arrested eleven members of the gang behind the Fireball adware campaign that infected more than 250 Million PCs. Chinese police have identified and arrested individuals suspected to be the operators behind the massive adware campaign that infected more than 250 Million computers across the world earlier this year. In June, researchers at security firm Check Point discovered the […]
 Pierluigi Paganini
July 26, 2017
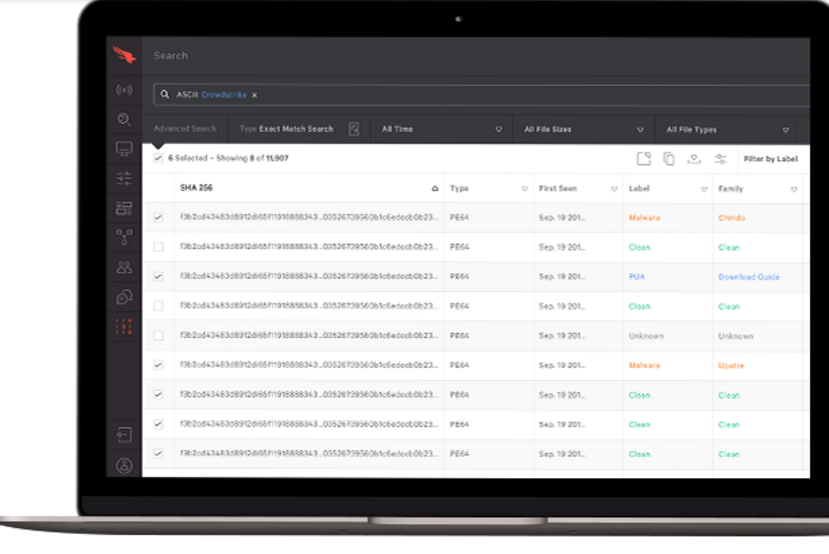
CrowdStrike Inc., the leader in cloud-delivered endpoint protection, announced the fastest and largest cybersecurity search engine. Security firm CrowdStrike, the leader in cloud-delivered endpoint protection, announced a significant improvement of its Falcon platform that has been integrated with a powerful cybersecurity search engine. According to the company the cybersecurity search engine has high performance, it claims it […]
 Pierluigi Paganini
July 25, 2017
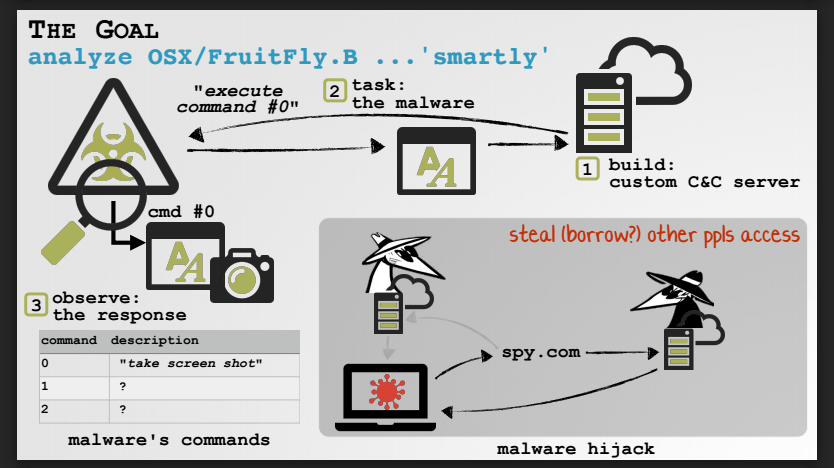
A new mysterious strain of macOS and OS X malware dubbed Fruitfly went undetected by malware researchers and security software for at least five years. Fruitfly is a backdoor that could be used by attackers to gain full control over the infected systems by implementing many spying features. Fruitfly has the ability to capture screenshots, keystrokes, […]
 Pierluigi Paganini
July 24, 2017
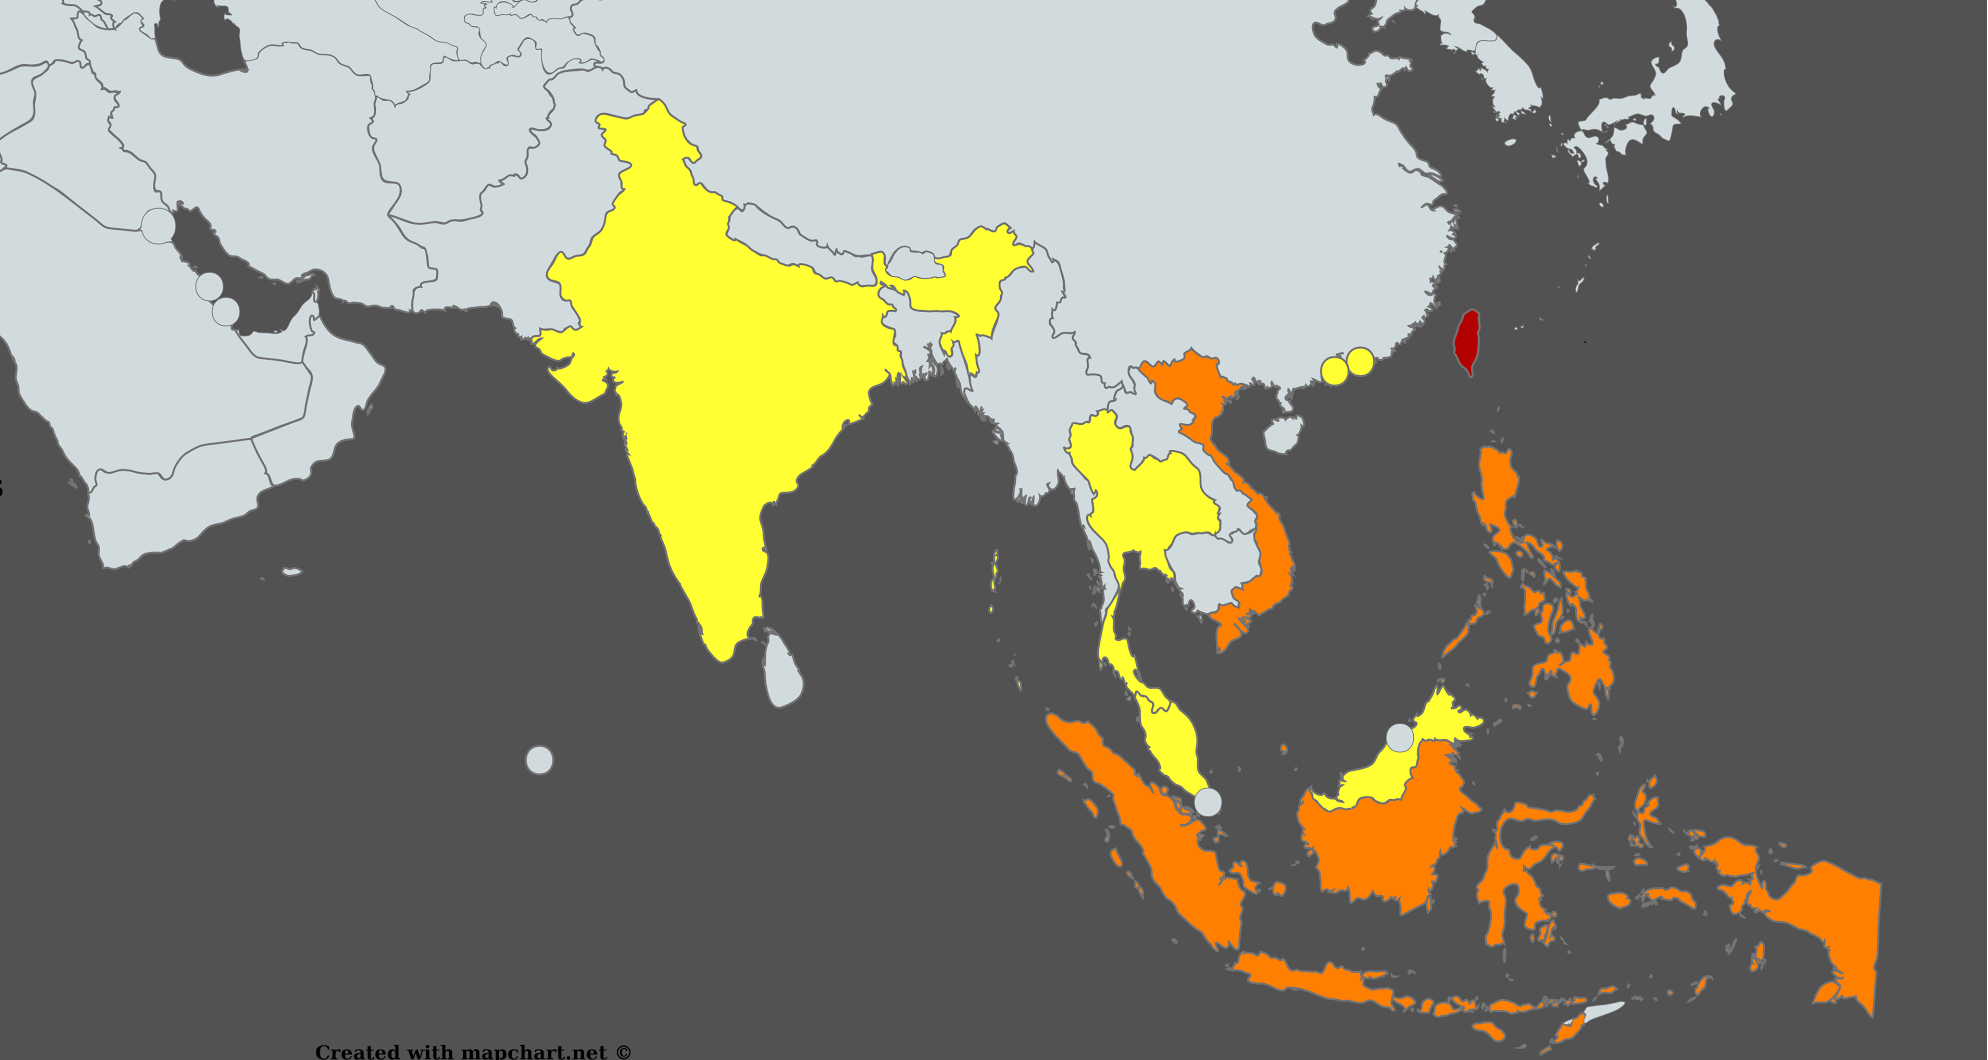
The threat actor behind Spring Dragon APT has been developing and updating its wide range of tools throughout the years, new attacks reported in South Asia. According to a new report published by Kaspersky Lab, the China-linked APT group Spring Dragon (aka Lotus Blossom, Elise, and Esile) has used more than 600 malware samples in […]
 Pierluigi Paganini
July 24, 2017
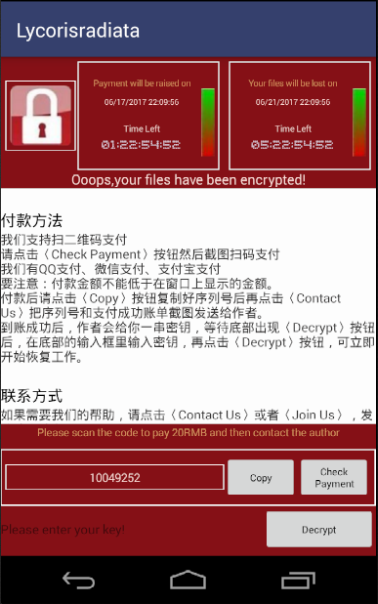
The SLocker code leaked online, it is one of the oldest mobile lock screen and file-encrypting ransomware. The code of the SLocker Android malware, one of the most popular Android ransomware families, has been leaked online for free, allowing crooks to develop their own variant of the threat. SLocker was first spotted in 2015, it is the […]
 Pierluigi Paganini
July 22, 2017
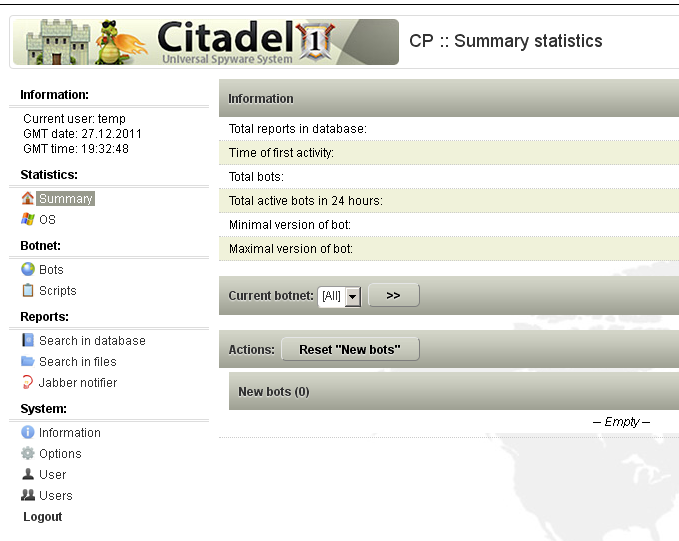
The Russian hacker Mark Vartanyan was sentenced to five years in prison for his involvement in the development and maintenance of the Citadel botnets. It’s a terrific moment for cyber criminals, law enforcement worldwide continues their fight against illegal activities online and the recent shut down of AlphaBay and Hansa black markets demonstrate it. The news of […]
 Pierluigi Paganini
July 21, 2017
Microsoft used the lawsuit to disrupt a large number of cyber espionage campaigns conducted by infamous Fancy Bear APT hacking group We have discussed several times about hacking back and the case we are going to analyze is a good example of an alternative approach to hit back an APT group. Microsoft used the lawsuit […]
 Pierluigi Paganini
July 21, 2017
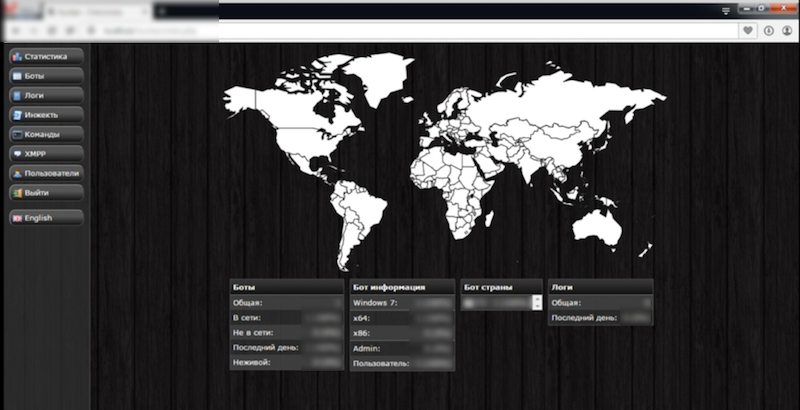
Apparently, different cyber gangs are using modified versions of the Nukebot in wild after code Leak occurred in March 2017. Crooks are adapting the leaked source code for the Nukebot banking Trojan to target banks in the United States and France and to steal mail client and browser passwords. Apparently, different cyber gangs are using modified versions of […]
 Pierluigi Paganini
July 19, 2017
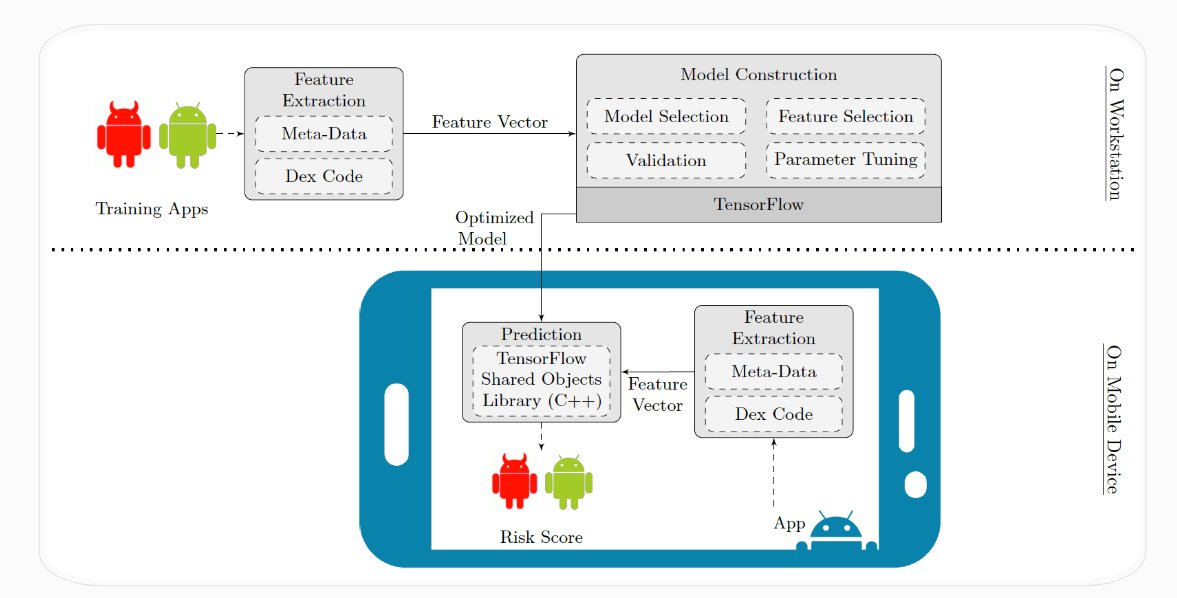
IntelliAV is a practical intelligent anti-malware solution for Android devices based on the open-source and multi-platform TensorFlow library. Android is targeted the most by malware coders as the number of Android users is increasing. Although there are many Android anti-malware solutions available in the market, almost all of them are based on malware signatures, and more advanced solutions based on […]
 Pierluigi Paganini
July 18, 2017
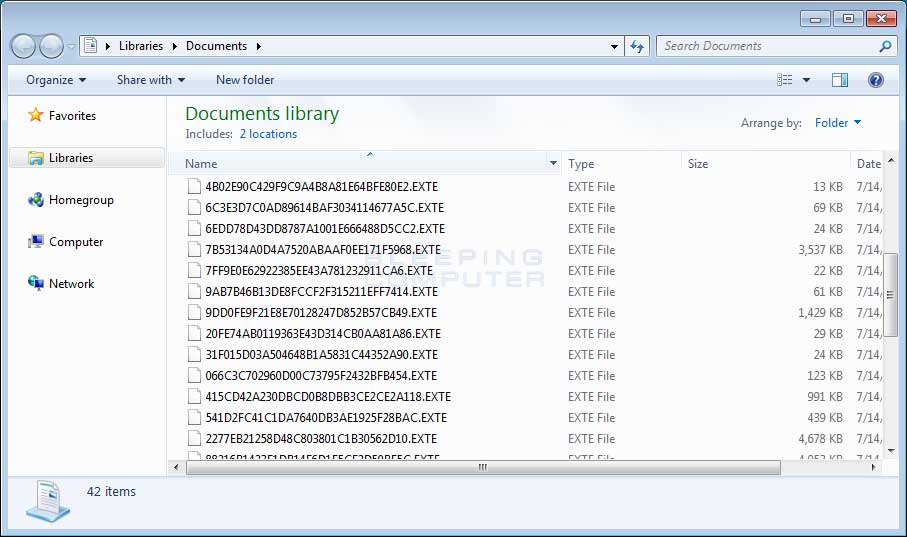
Two CryptoMix Ransomware variants emerged in a few days, a circumstance that suggests the operators behind the threat are very active. Malwarebytes’ researcher Marcelo Rivero has spotted a new variant of the CryptoMix ransomware. #CryptoMix #Ransomware adds ext ".EXTE" to encrypted files, and the note "_HELP_INSTRUCTION.TXT" – md5: 1059676fbb9d811e88af96716cc1ffb5 pic.twitter.com/Ha4jeRMPEv — Marcelo Rivero (@MarceloRivero) July 13, […]

APT / October 15, 2026