 Pierluigi Paganini
 April 19, 2017
The InterContinental Hotels Group announced that last week payment card systems at more than 1,000 of its hotels had been compromised by crooks. The multinational hotel chain owns prestigious brands like Holiday Inn and Crowne Plaza. This is the second time that the InterContinental Hotels Group suffers a credit card breach, early this year the hotel chain […]
 Pierluigi Paganini
April 18, 2017
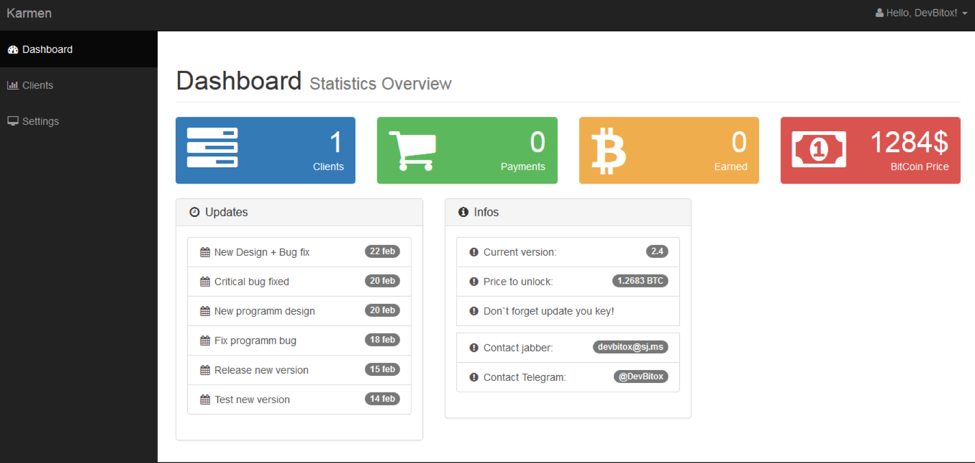
Experts at Recorded Future have discovered a cheap RaaS, the Karmen Ransomware that deletes decryptor if detects a sandbox. Security experts from threat intelligence firm Recorded Future have spotted a new ransomware as a service (RaaS) called Karmen. The service allows customers to easy create their ransomware campaign in a few steps and without specific skills. Wannabe-crooks […]
 Pierluigi Paganini
April 18, 2017
Security researchers who analyzed the documents and hacking tools included in the last Shadow Brokers dump found a link to the Stuxnet virus. On Friday, the Shadow Brokers leaked a new bunch of files belonging to the alleged NSA arsenal. Security researchers who analyzed the documents and hacking tools included in the last dump have […]
 Pierluigi Paganini
April 18, 2017
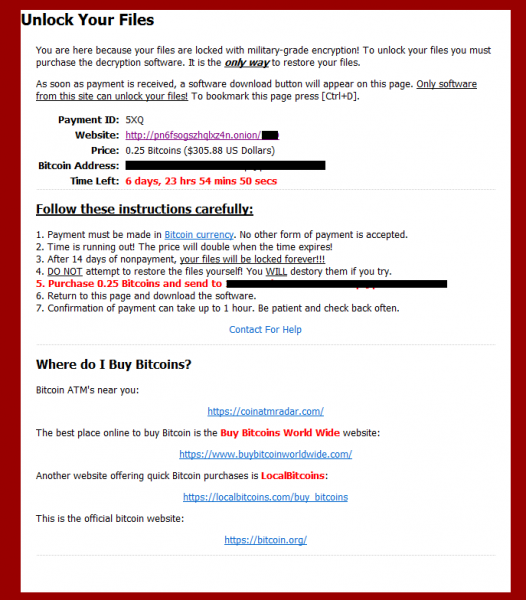
CradleCore ransomware is a malware offered in the underground as a source code, instead of the classic ransomware-as-a-service (RaaS) model. According to the experts at Forcepoint, the author is offering the malware in many Tor-based crime forums as source code allowing crooks to request a customized version of the code. The CradleCore ransomware is offered by the author as a […]
 Pierluigi Paganini
April 17, 2017
The Sundown EK has been inactive since early this year, the Terror EK is being very popular in the cybercriminal ecosystem. One year ago the Angler EK and Nuclear EK disappeared from the threat landscape, while the Sundown EK was conquering the criminal underground. What’s happening now? The Sundown EK has been inactive since early this year, the […]
 Pierluigi Paganini
April 13, 2017
Security researchers at FireEye discovered that the Microsoft Word CVE-2017-0199 exploit was linked to cyberspying in Ukraine conflict. The zero-day vulnerability in Microsoft Office that was recently fixed by Microsoft was used to deliver a surveillance malware to Russian-speaking targets. Security experts from firm FireEye spotted the targeted attacks leveraging specifically crafted Microsoft Word documents that […]
 Pierluigi Paganini
April 13, 2017
Hackers exploited the CVE-2014-9222 flaw, also known as ‘Misfortune Cookie’, to hack thousands of home routers and abuse them for WordPress attacks. According to the experts at the security firm Wordfence tens of thousands, of home routers have been hacked and used to power cyber attacks on WordPress websites. The security firm observed a spike in […]
 Pierluigi Paganini
April 09, 2017
According to Kaspersky Lab, crooks have robbed at least 8 ATMs in Russia and stole $800,000 in just one night using a Fileless malware dubbed ATMitch. According to experts at Kaspersky, hackers have robbed at least 8 ATMs in Russia and stole $800,000 in just one night. The cyber heist caught the attention of security […]
 Pierluigi Paganini
April 08, 2017
The Shadow Brokers hacking crew sent a message to President Trump commenting recent political events and released more alleged NSA hacking tools. The Shadow Brokers is the mysterious group that in October 2016 claimed to have stolen a bunch of hacking tools used by the NSA for its operations. At the end of October 2016, the hackers […]
 Pierluigi Paganini
April 08, 2017
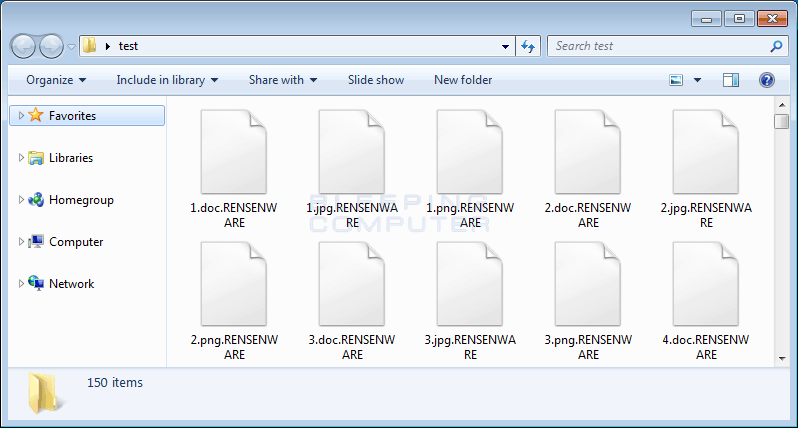
The rensenWare ransomware rather than demanding money, it requires the victims to score “over 0.2 billion” playing “TH12 game. Security experts at MalwareHunterTeam have spotted a new ransomware dubbed ‘rensenWare’. The ransomware is very strange, rather than demanding money, it requires the victims to score “over 0.2 billion” playing “TH12 — Undefined Fantastic Object”. The RensenWare […]