


 Pierluigi Paganini
 September 11, 2014
Security experts warn Dyre malware is being used by cyber criminals for corporate espionage instead harvest banking credentials. Dyre is the name of a new variant of the immortal Zeus banking trojan worries cyber security experts, this new strain doesn’t limit its stealing activity to user’s banking credentials, but search for customer information. Dyre has been detected […]
 Pierluigi Paganini
September 09, 2014
Experts at Clearsky detected the Gholee virus which was likely developed by highly qualified factors, which may even be related to Israel’s long-time nemesis Iran. Experts from Clearsky, an Israeli cyber-security company, detected an “operation protective edge” themed spear phishing attack, carried out via emails containing a malicious excel file. Once opened and its VBA […]
 Pierluigi Paganini
September 08, 2014
Apple CEO Tim Cook announced that the company will improve the security of its solutions, including iCloud, starting from extension of 2FA mechanisms. The recent disclosure of hundreds celebrity pictures has raised the discussion on the level of security offered by the Apple iCloud stored service. To improve the security offered by the iCloud service, Apple’s CEO Tim Cook […]
 Pierluigi Paganini
September 06, 2014
Security Experts at FireEye Lab discovered a new variant of the XSLCmd backdoor that has been used in targeted attacks infecting Mac OX based systems. Experts at FireEye Labs have discovered a previously unknown variant of the APT backdoor XSLCmd, OSX.XSLCmd, which is used by a group of hackers known for past cyber espionage activities against the U.S. […]
 Pierluigi Paganini
September 06, 2014
Expert at TrendMicro published a new chapter of the Cybercriminal Underground Economy Series in which analyzed the Chinese underground. Chinese cybercrime underground activity is rapidly increasing, according to a new interesting report published by Trend Micro the Chinese it is doubled between 2012 and 2013. The findings confirm that amount of underground activity in China doubled both with […]
 Pierluigi Paganini
September 05, 2014
Experts at Akamai-Prolexic discovered a botnet dubbed IptabLes and IptabLex that infects and exploits poorly-maintained Linux servers to run DDoS attacks. Akamai’s Prolexic division has uncovered a new botnet dubbed IptabLes and IptabLex, which was used in a series of attacks targeting malware based on Linux servers. The experts revealed that the IptabLes and IptabLex botnet compromises misconfigured and […]
 Pierluigi Paganini
September 04, 2014
An independent researcher has analyzed for years the metadata on submissions to VirusTotal service identifying patterns related to many bad actors. VirusTotal is the Google owned company which offers free checking of URLs and files for viruses and other malicious code, its systems use up to 54 different antivirus software to scan files and URLs provided by the userscheck. Cyber criminals […]
 Pierluigi Paganini
September 01, 2014
Experts at Dr.Web detected a Linux DDoS Trojan designed to infect also Windows OS, the circumstance is considered rare in the criminal ecosystem. The Russian antivirus company Dr. Web discovered that a Chinese DDoS Trojan written for Linux operating system seems have jumped to Windows, an event considered rare. “Cases of Linux malware being tailored by […]
 Pierluigi Paganini
September 01, 2014
The APWG Report Q2 2014 states that phishing activities continue to increase, phishers are targeting Crypto Currency, Payment Services and Retail Sites. The APWG has published its new report related to phishing activities in the period April – June 2014, the document titled “Phishing Activity Trends Report, 2nd Quarter 2014” states that online payment services […]
 Pierluigi Paganini
August 31, 2014
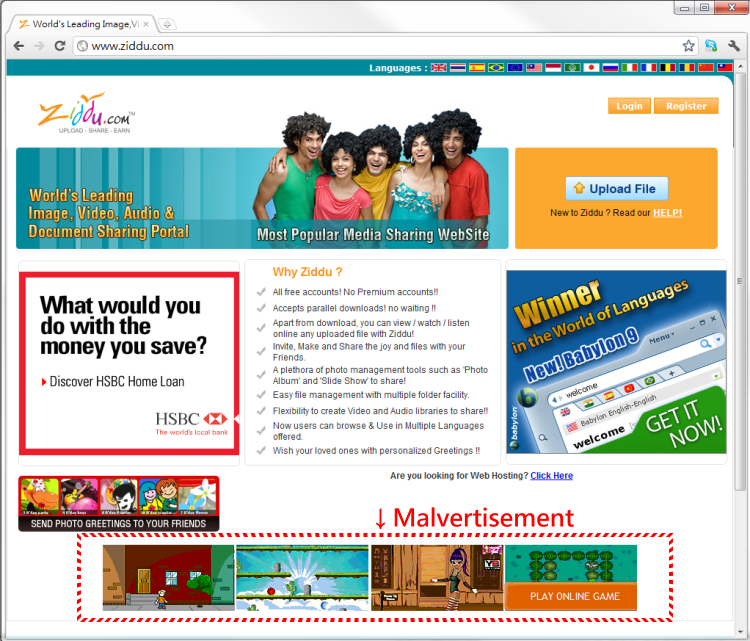
A new malvertising campaign has been spotted by experts at Fox-IT, the researchers discovered malicious ads on high-profile websites including Java.com. Experts at Fox-IT revealed in a blog post the Internet firm AppNexus is the origin of a new “malvertising” campaign, which is based on the Angler Exploit Kit to redirect visitors to malicious websites serving the Asprox malware. AppNexus provides a platform […]







