


 Pierluigi Paganini
 August 15, 2014
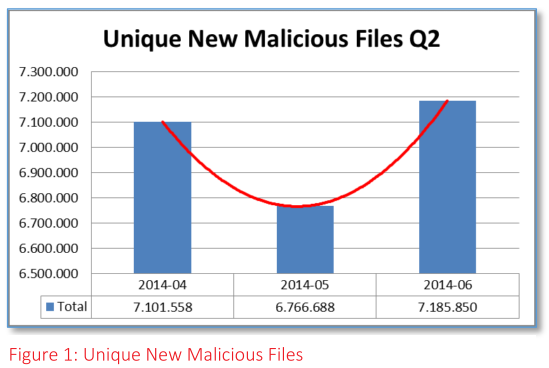
RedSocks Malware Research Labs issued the Malware Trend Report Q2 2014, which contains data evolution of principal cyber threats observed in the second quarter of the year. The Dutch company specializing in Malware detection RedSocks Research Lab. Has published the second quarterly trend report for 2014. The experts have analyzed large numbers of malicious files […]
 Pierluigi Paganini
August 14, 2014
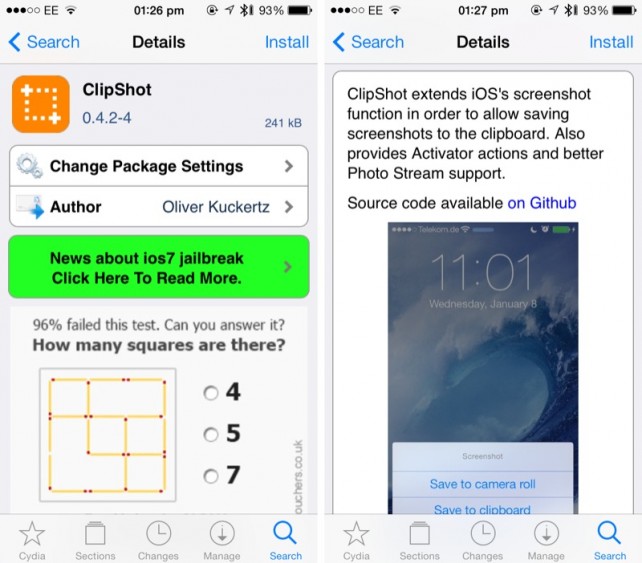
Malware expert Axelle Apvrille explained how the iOS AdThief malware infected more than 75000 jailbroken iOS devices hijacking millions advertisements. More than 75,000 jailbroken iPhones have been infected by a Chinese malware which were used by cyber criminals to hijack nearly 22 million advertisements and steal revenue from developers on the iOS jailbreak community. The […]
 Pierluigi Paganini
August 13, 2014
Security experts at Symantec detected a large-scale cyber espionage campaign which hit personnel at embassies of former Soviet states. Security researchers at Symantec discovered a large-scale cyber attack which is targeting embassies of former soviet states worldwide. The experts detected a huge cyber attack that has been carried out across more than 15 countries, the […]
 Pierluigi Paganini
August 09, 2014
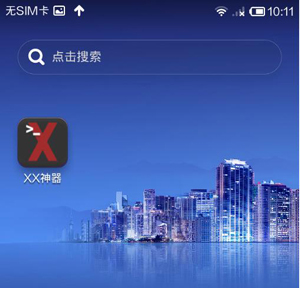
One million Android devices in China were infected with an Xshqi SMS worm on August 2, the day the country celebrated Valentine’s Day. Experts at Kaspersky Lab revealed that a malware, dubbed Trojan.AndroidOS.Xshqi.a, infected neatly 500,000 Android devices in just six hours last week in China, but Chinese media provided a more pessimistic estimate declaring that the […]
 Pierluigi Paganini
August 08, 2014
Experts at GData discovered Poweliks, a persistent malware able to infect machines without installing any files on the targeted machine. Researchers at GData software have discovered a new surprising strain of malware named Poweliks which is able to infect systems and steals data without installing any file onto the victim’s machine. This malware maintains persistence storing its components […]
 Pierluigi Paganini
August 08, 2014
A Hacker claims to have hacked the network of Gamma International firm and he has leaked docs related to the malware-for-government FinFisher. Earlier this week the British company Gamma International appears to have been hacked and a collection of files from its systems have been leaked on the Internet. The security firm is popular because it […]
 Pierluigi Paganini
August 07, 2014
A report disclosed by Wired suggests that the FBI is using a malware to identify Tor users by infecting machines on a large scale. It’s not a mystery that usage of the Tor network represents a problem for investigators of law enforcement agencies and for government entities that need to track users on the popular anonymizing network. […]
 Pierluigi Paganini
August 05, 2014
Experts at the German security firm G-Data discovered a RAT dubbed IcoScript which receives commands from C&C via email services including Yahoo and Gmail. Security experts have detected a new Remote Administration Trojan dubbed IcoScript which is controlled by bad actors through Yahoo Mail and is able to elude detection systems by using seemingly benign domains for […]
 Pierluigi Paganini
August 03, 2014
Experts at IBM discovered a new variant of Citadel banking malware which includes different remote management tools to maintain persistence on victims’ PC. Researchers at IBM discovered a new variant of the Citadel banking malware which includes a new interesting feature that allows attackers to maintain persistence in the victim’s machine through remote management tools. Citadel is directly […]
 Pierluigi Paganini
August 02, 2014
The Kaspersky Lab Team has issued a report which includes details of the investigation related to the Energetic Bear – Crouching Yeti APT campaign. Energetic Bear, aka Crouching Yeti, is the recently discovered APT campaign that targeted energy companies, manufacturers, industrial, pharmaceutical, construction, and many IT companies. Security experts have analyzed the Energetic Bear APT campaign, which appears […]







