


 Pierluigi Paganini
 April 30, 2015
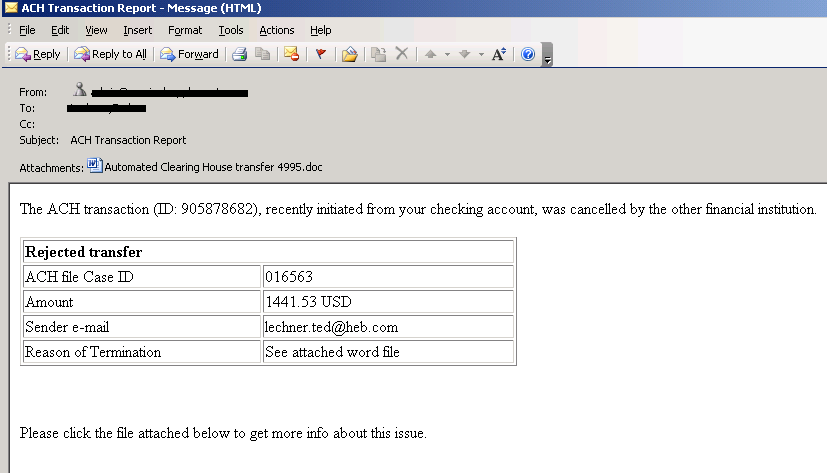
Microsoft is observing a major spike in the volume of malware using macros since the beginning of the year. The infection method was very common in the past I remember when I was starting my career, around 2006 that a lot of the existent malware would arrive to their victims trough Word/Excel macros, and that […]
 Pierluigi Paganini
April 17, 2015
Security experts worldwide have discovered that threat actors are exploiting the Microsoft Zero-Day vulnerability MS15-034 in cyber attacks. Security researchers at SANS Internet Storm Center revealed that the critical remote code execution vulnerability MS15-034 affecting the Windows HTTP protocol stack is being actively exploited in the wild. The experts explained that the MS15-034 flaw affects […]
 Pierluigi Paganini
April 14, 2015
The Redirect to SMB vulnerability affects all supported versions of Windows and could be exploited to steal users’ credentials for various services. Experts at Cylance have discovered a new credential hijacking vulnerability dubbed Redirect to SMB that affects all versions of Windows OSs, including the upcoming Windows 10. The Redirect to SMB could be exploited by an attacker […]
 Pierluigi Paganini
March 11, 2015
Microsoft and Apple released security updates to fix the FREAK vulnerability recently discovered and affecting their products. FREAK is a major security flaw recently discovered that left users of Apple and Google devices exposed to MITM attack while visiting supposedly secure Websites. At the same time Microsoft issued a specific security advisory to inform its […]
 Pierluigi Paganini
March 07, 2015
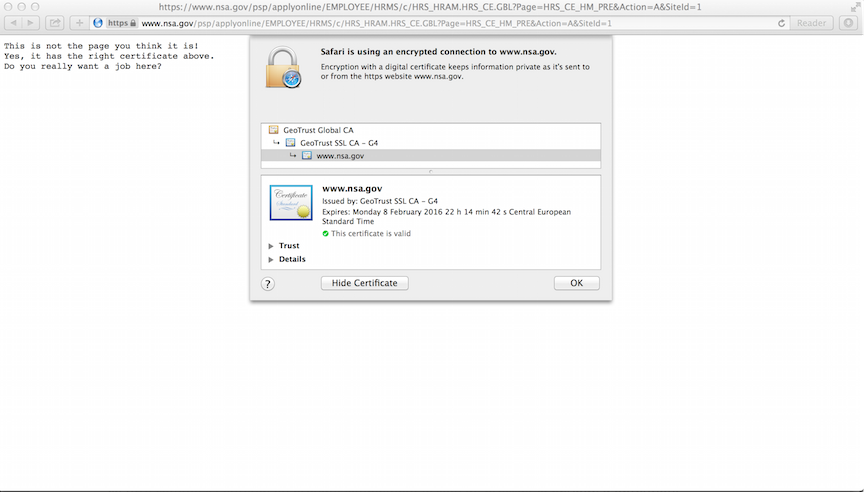
Researchers hack NSA’s website with only $104 and 8 hours of Amazon’s cloud computing power using the #FREAK vulnerability A team of researchers demonstrated that it is possible to exploit the FREAK vulnerability to hack the official NSA website by using 8 hours of Amazon’s cloud computing power and spending only $104. The researcher made […]
 Pierluigi Paganini
March 06, 2015
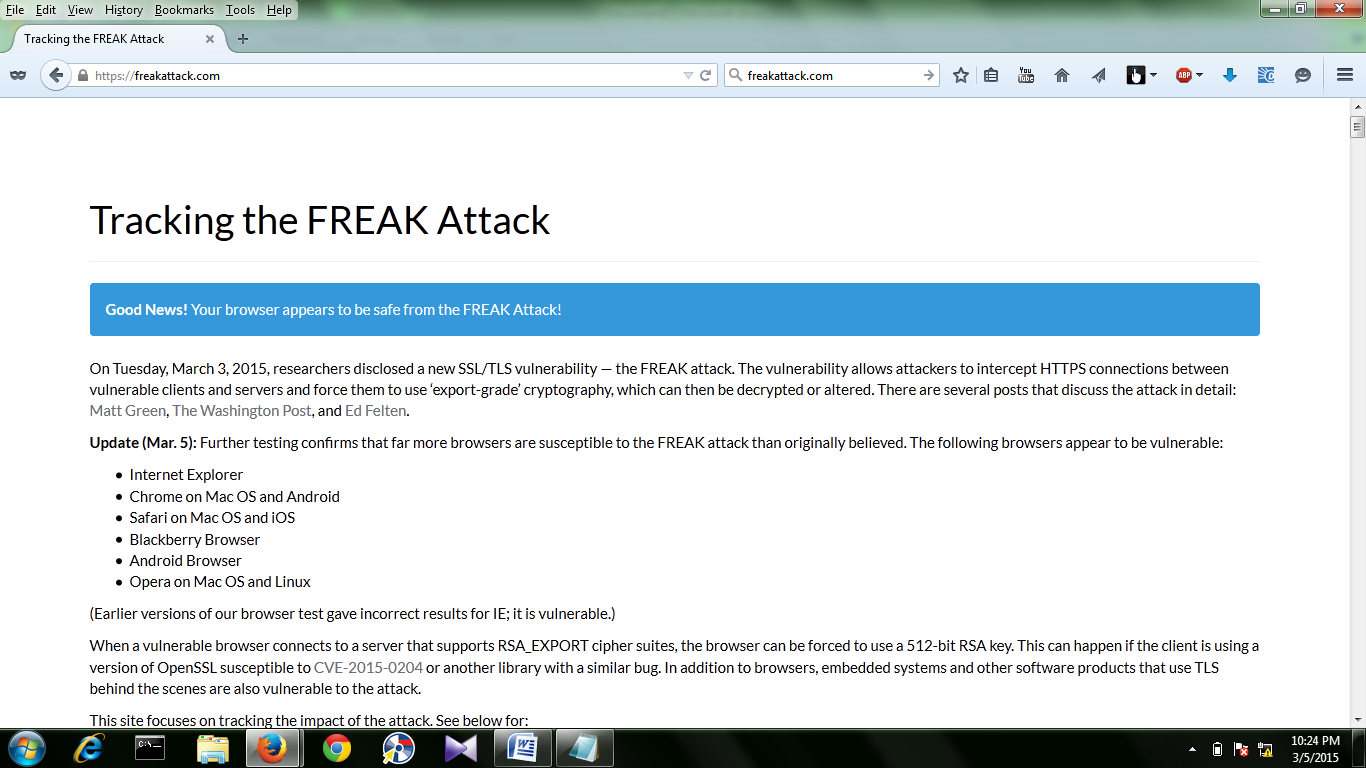
According to a security advisory published by Microsoft all supported versions of Windows are affected by the recently discovered FREAK vulnerability FREAK is major security SSL/TLS vulnerability recently discovered that for more than a decade left users of Apple and Google devices vulnerable to hacking when they visited millions of legitimate and secure websites. The critical […]
 Pierluigi Paganini
February 25, 2015
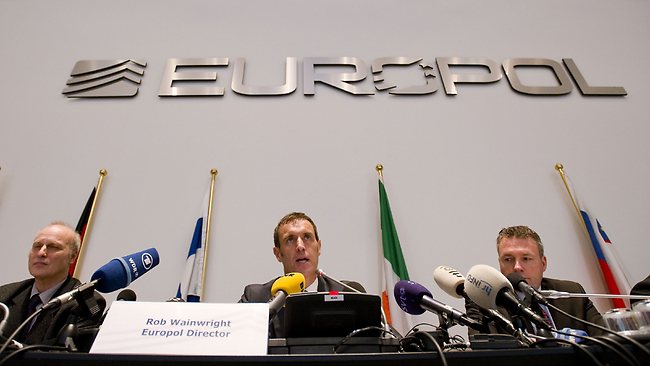
The Ramnit botnet has been shut down in a joint effort by the Europol and the security firms Symantec, Microsoft, and Anubis Networks. Another success For the Europol and its allies Microsoft, Symantec, and Anubis Networks. The organizations in a joint effort have shut down command and control servers of the popular Ramnit botnet. The Joint Cybercrime […]
 Pierluigi Paganini
February 14, 2015
The experts at the IT Department of the EU parliament bans the Microsoft mobile Outlook app due to the recently disclosed privacy and security issues. A few day ago I wrote about serious security issues for day ago I wrote about serious security issues for Microsoft mobile Outlook app, the researcher and Head of Development at midpoints […]
 Pierluigi Paganini
February 11, 2015
Microsoft issued a security advisory for the JASBUG critical flaw, affecting all Windows OSs, that could be remotely exploitable. The news of the day is that a 15-year-old vulnerability in all Microsoft systems was fixed by the last critical patch issued by the company. The vulnerability, dubbed JASBUG and coded as CVE-2015-0008, could be exploited by an attacker to […]
 Pierluigi Paganini
February 10, 2015
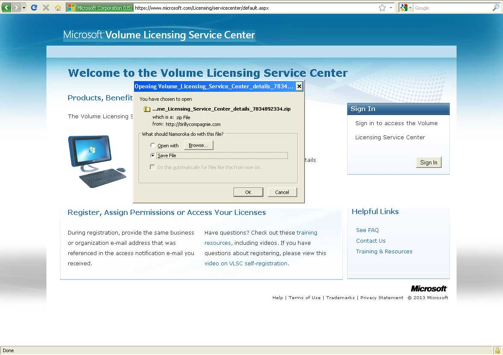
Cisco experts discovered a phishing campaign that is spreading fake Volume License Trojan Chanitor to corporate users and is able to evade sandboxes. A few weeks ago, multiple Cisco Managed Threat Defense (MTD) customers received an email that appeared as sent by the Microsoft Volume Licensing Service Center (VLSC), which contains a link to login to the […]

Security / October 08, 2026




