 Pierluigi Paganini
 August 15, 2017
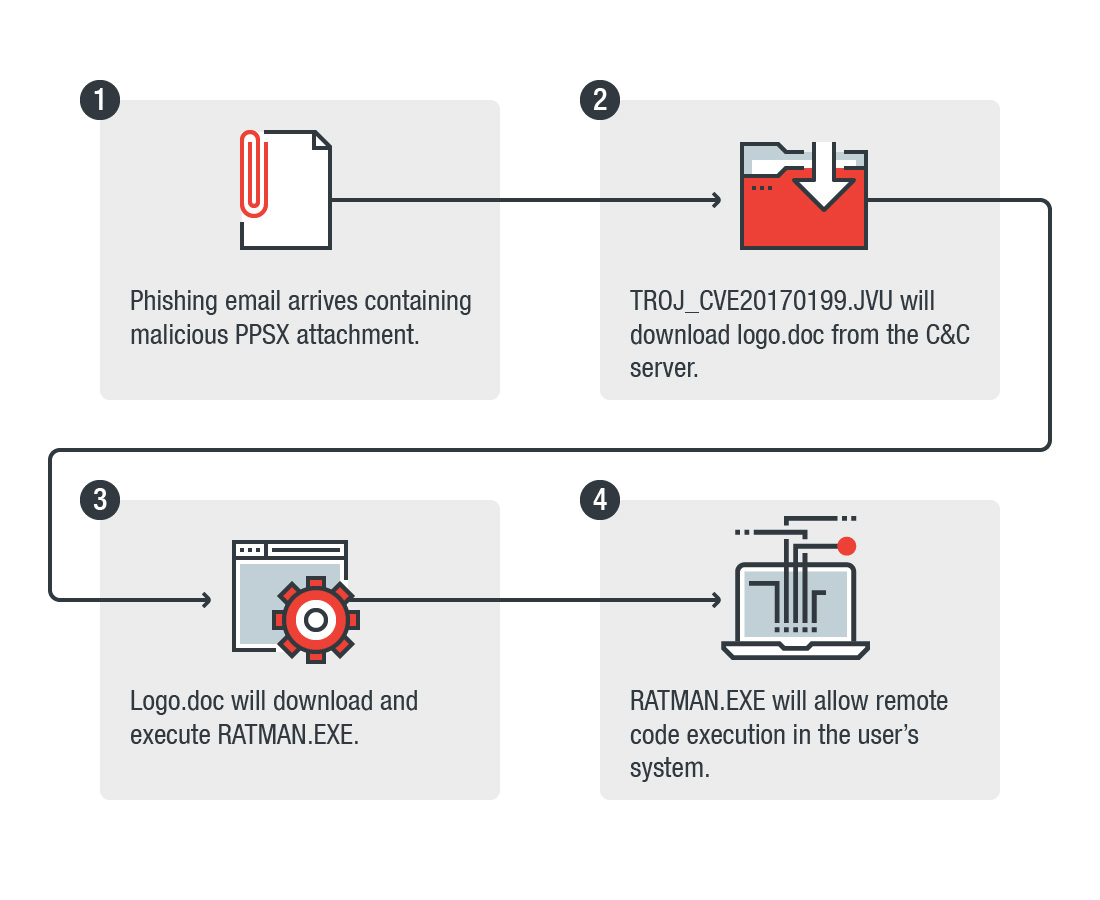
According to Trend Micro, cyber criminals abuse the CVE-2017-0199 vulnerability to deliver malware via PowerPoint Slide Show. In April Microsoft fixed the CVE-2017-0199 vulnerability in Office after threat actors had been exploiting it in the wild. Hackers leveraged weaponized Rich Text File (RTF) documents exploiting a flaw in Office’s Object Linking and Embedding (OLE) interface to deliver malware such […]
 Pierluigi Paganini
August 13, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. · Flaws in solar panels potentially threatening European power grids · Hackers leak the fourth episode of Game of Thrones season 7 online · Security Affairs newsletter Round 122 – News of the week · US Army […]
Pierluigi Paganini
August 06, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. · Apple removed iOS VPN apps from Chinese App Store in compliance to censorship law · Bypassing locking mechanisms of a smart gun with $15 worth of magnets · DEF CON 25 – BBC Micro:bit could be […]
 Pierluigi Paganini
August 03, 2017
Former Employee of the Healthcare giant Bupa offered for sale records of 1 Million clients on Dark Web. A former employee of healthcare giant Bupa was selling between 500,000 and 1 million records on the healthcare giant Bupa was selling between 500,000 and 1 million records on the dark web. The former employee whose identity […]
 Pierluigi Paganini
August 01, 2017
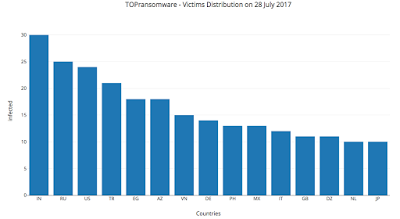
TOPransom – Analyzing the entire process from getting an email attachment to powning the ransom server trying to stop the infection. Hi folks, today I want to share a quick but intensive experience in fighting cybercrime. I wish you would appreciate the entire process of getting an email attachment to powning the ransom server trying […]
 Pierluigi Paganini
July 27, 2017
Google has identified a new strain of Android malware, the Lipizzan spyware, that could be used as a powerful surveillance tool. Malware researchers at Google have spotted a new strain of Android spyware dubbed Lipizzan that could exfiltrate any kind of data from mobile devices and use them as surveillance tools. The Lipizzan spyware is a project developed […]
 Pierluigi Paganini
July 26, 2017
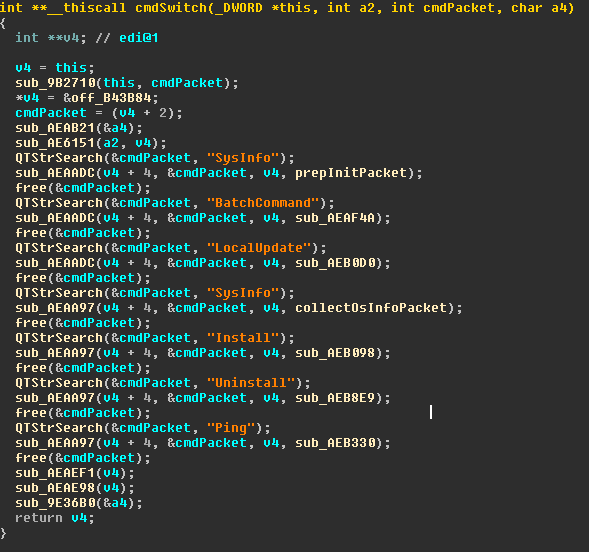
Malware researchers at Kaspersky Lab have found a new Windows Backdoor dubbed CowerSnail linked to the recently discovered SHELLBIND SambaCry Linux malware. Security experts at Kaspersky Lab have spotted a new Windows Backdoor dubbed CowerSnail linked to the recently discovered SHELLBIND SambaCry Linux malware. SHELLBIND has infected most network-attached storage (NAS) appliances, it exploits the Samba vulnerability (also known as SambaCry and EternalRed) to upload a shared […]
Pierluigi Paganini
July 23, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. · Crooks used Infrared insert skimmers in a recent wave of ATM attacks · Did you receive a WhatsApp subscription ending email or text? Watch out! · Hackshit PhaaS platform, even more easy to power Phishing campaigns […]
Pierluigi Paganini
July 09, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. · FBI hacked a US Darknet shopper who tried to purchase Mail Bomb · NATO attributed the massive NotPetya attack to a ‘state actor and call for a joint investigation · NATO CCD COE attributed the massive […]
 Pierluigi Paganini
July 05, 2017
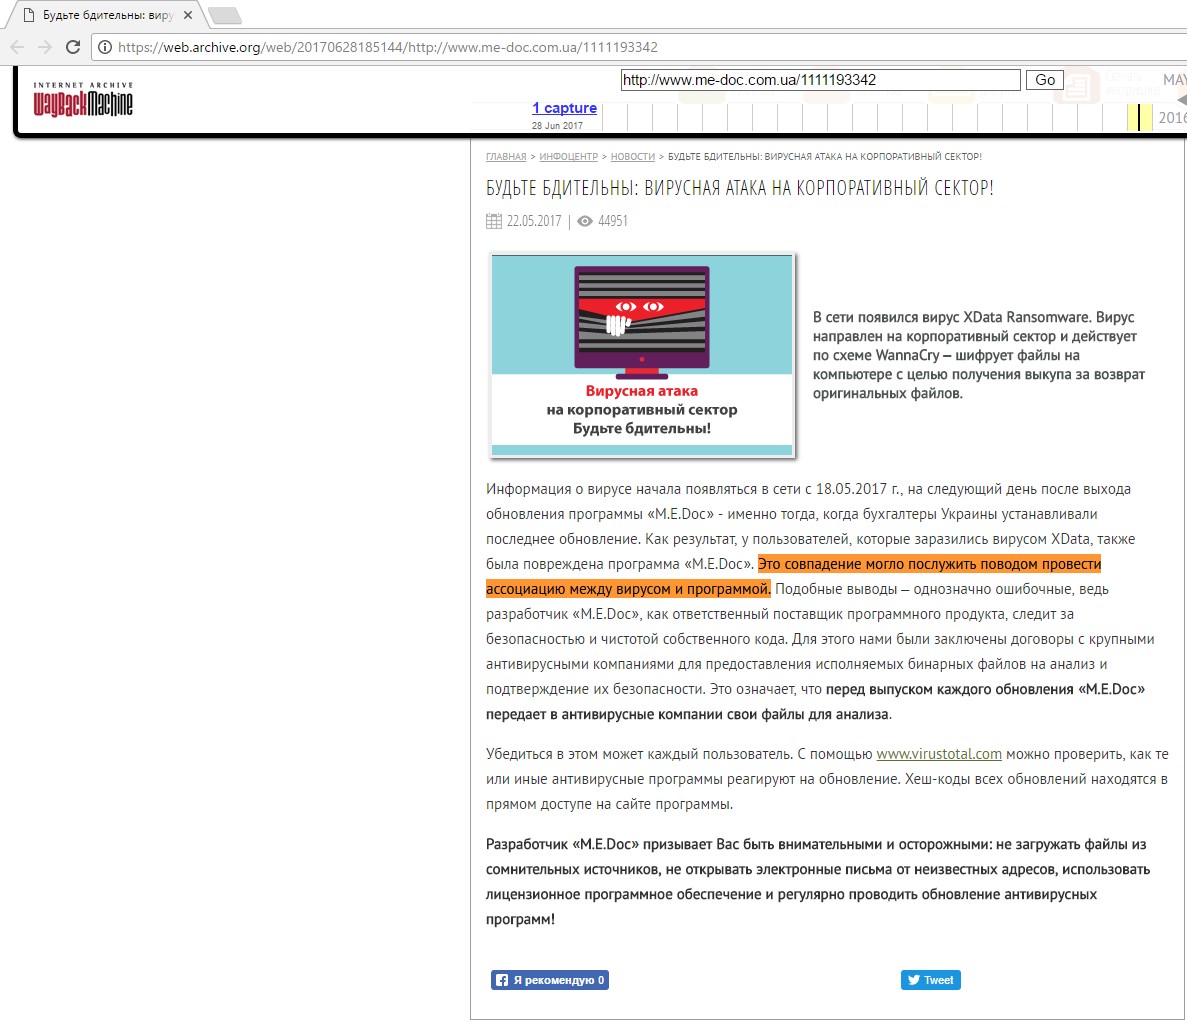
The Ukraine’s cyber police seized the MeDoc servers after detecting a new suspicious activity and fearing new malware-based attacks. The Ukrainian authorities have seized equipment from the online accounting firm MeDoc which is suspected to have had a significant role in the recent NotPetya attack. The Ukraine’s cyber police have seized the servers after detecting a new suspicious activity, the […]