


 Pierluigi Paganini
 May 14, 2015
According to a report published by the experts at root9B the hacking crew APT28 is planning to attack several financial institutions worldwide. In October 2014, security expert at FireEye published a report on the activities conducted by a group of Russian hackers, dubbed APT28, the hacking crew is behind long-running cyber espionage campaigns that targeted US defense contractors, European security organizations and […]
 Pierluigi Paganini
May 13, 2015
Security Researcher at CrowdStrike claims VENOM vulnerability leaves millions of virtual machines vulnerable to cyber attacks. A new security vulnerability dubbed VENOM (CVE-2015-3456) is threatening the security industry. The CrowdStrike Senior Security Researcher Jason Geffner who discovered the vulnerability explained that the flaw could be exploited by an attacker to compromise any machine is a data […]
 Pierluigi Paganini
May 09, 2015
Onapsis study found that over 95% of SAP systems are exposed to vulnerabilities that could lead to full compromise of the company’s business. SAP is one of the most popular enterprise software used by companies to manage business operations and customer relations. A recent study conducted by the SAP solutions provider revealed that more than 95 percent […]
 Pierluigi Paganini
May 07, 2015
According to data provided by British law enforcement, at least a 25 percent of organised criminals in the country is converting themselves to cybercrime. Cybercrime is becoming even more attractive to traditional crooks, including violent offenders. According to data provided by British law enforcement traditional crimes were continuing to fall while the number of online crimes […]
 Pierluigi Paganini
May 04, 2015
Hackers belonging to the Anonymous collective hacked the website of the World Trade Organization (WTO) and leaked personal data of thousands of officials. Hackers belonging the Anonymous collective compromised the website of the World Trade Organization (WTO) and leaked its database containing personal data of its members. The stolen data are related to personnel of […]
 Pierluigi Paganini
May 02, 2015
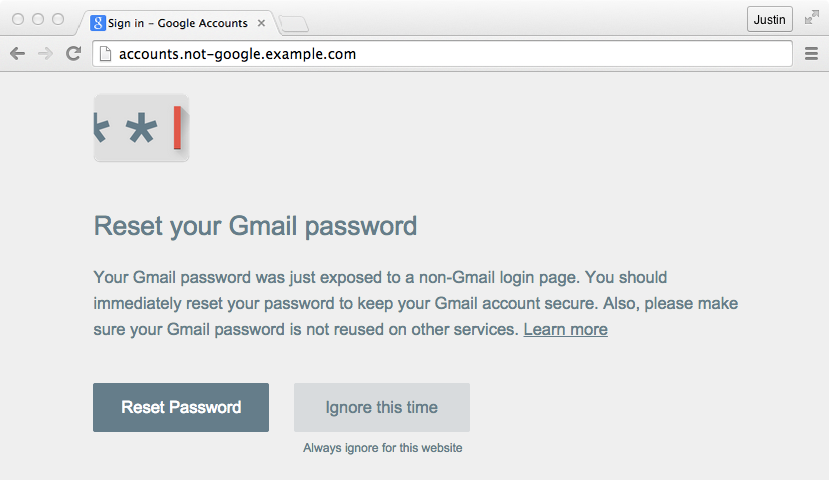
A few hours after the presentation of the Google Password Alert extension a researcher already have developed two methods to bypass it. A few hours ago, Google released the Password Alert extension that was designed to warn users when they are submitting their Google credentials to fraudulent websites. “Here’s how it works for consumer accounts. Once you’ve […]
 Pierluigi Paganini
May 01, 2015
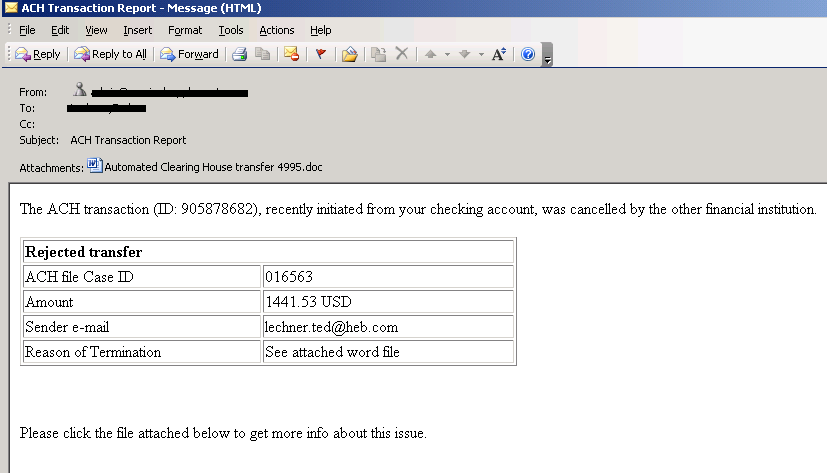
Foreign hackers are targeting background investigation databases to blackmail US government personnel or to try to bribe them. It is not a mystery that Chinese hackers continuously target US companies and government offices, the attackers usually backed by the Government of Bejing mainly run cyber espionage campaigns to steal intellectual property and any kind of information related to person […]
 Pierluigi Paganini
April 30, 2015
Microsoft is observing a major spike in the volume of malware using macros since the beginning of the year. The infection method was very common in the past I remember when I was starting my career, around 2006 that a lot of the existent malware would arrive to their victims trough Word/Excel macros, and that […]
 Pierluigi Paganini
April 23, 2015
Kaspersky Lab discovered another APT group dubbed CozyDuke which is believed to have hacked the US Department of State and the White House. Experts at Kaspersky Lab have uncovered a new advanced persistent threat (APT) dubbed CozyDuke that targeted several high-profile organizations in the second half of 2014. Kaspersky experts have published an interesting blog post that includes […]
 Pierluigi Paganini
April 19, 2015
FireEye recently detected a new highly targeted attack run by APT28 exploiting two zero-day flaws to compromise an “international government entity”. Security experts at FireEye have recently detected a new cyber espionage campaign, dubbed “Operation RussianDoll,” operated by the Russian APT28 group. This time the hackers run highly targeted attack by exploiting two zero-day vulnerabilities to target an “international […]

Artificial Intelligence / September 17, 2026
Hacking / September 17, 2026





