


 Pierluigi Paganini
 December 26, 2014
Chinese hackers brought down all major Afghanistan Government websites by hacking an official CDN network used in the country. The experts of the ThreatConnect Intelligence Research Team (TCIRT) recently reported the operation, dubbed Operation Helmand, run by a group of Chinese hackers that attacked the entire Afghan government web network. The hackers allegedly used a targeted cross-site scripting […]
 Pierluigi Paganini
December 25, 2014
Security Experts at Sophos explained the efficiency of the business model known as Cybercrime-as-a-Service in the specific case of Vawtrak botnet. The term Cybercrime-as-a-Service refers to the practice in the cybercriminal ecosystem to provide product and services for use by other criminals. In September 2014, a report from Europol’s European Cybercrime Centre (EC3), the 2014 […]
 Pierluigi Paganini
December 15, 2014
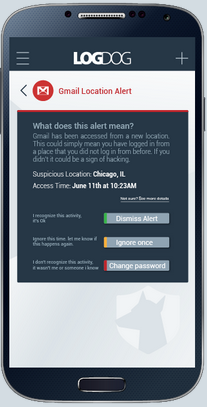
Mobile developers behind the Logdog app have conducted a rapid survey to analyze the trend in the hacking of accounts for the principal web services. A few weeks ago I was contacted by LogDog, a company that has developed is free protection app from hacking attacks and identity theft, the developer asked me to try the […]
 Pierluigi Paganini
December 15, 2014
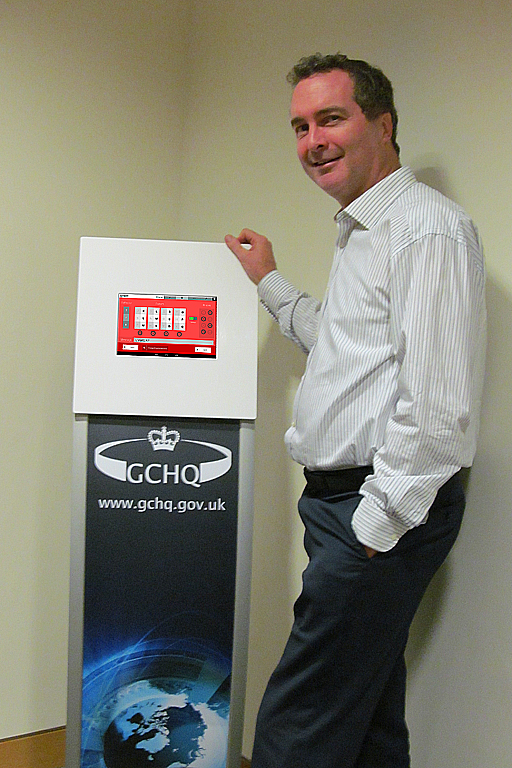
Cryptoy is the free educational app about cryptography designed by GCHQ for use by secondary school students and their teachers. The British Intelligence agency GCHQ has launched “Cryptoy”, an Android mobile app that was designed to encourage youngsters to tackle emerging cyber security threats, the Agency made it available to download today. The Cryptoy mobile app was developed by […]
 Pierluigi Paganini
December 02, 2014
FIN4 hacking team has targeted over 100 organizations since 2013, all of which are either publicly traded companies or advisory firms. Researchers at FireEye issued a report on a hacking crew dubbed FIN4 which is specialized in hacking of publicly traded companies with the intent to steal sensitive data, including mergers and acquisitions intelligence. ” FIN4 has pursued targets at more than […]
 Pierluigi Paganini
November 26, 2014
FireEye discovered that the Group of hackers dubbed APT3 that managed the Op Clandestine Fox is now running a new campaign dubbed Operation Double Tap. Researchers at FireEye have uncovered a new advanced persistent threat crew dubbed APT3, which is using exploits targeting recently disclosed vulnerabilities in Windows. The experts at FireEye believe that APT3 is the same […]
 Pierluigi Paganini
November 17, 2014
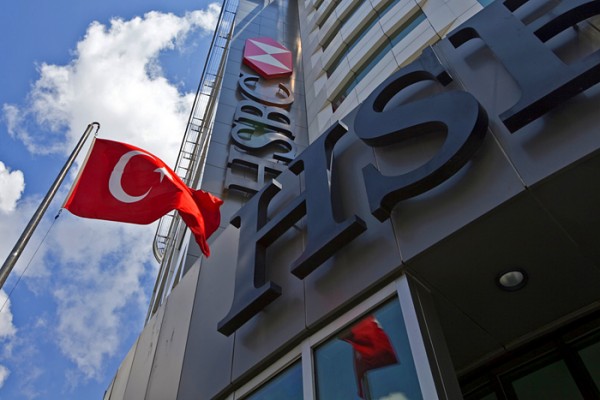
The International bank Hong Kong and Shanghai Banking Corporation (HSBC) announced that its systems suffered a major data breach. Last week the International bank Hong Kong and Shanghai Banking Corporation (HSBC) has announced that its computer networks in Turkey were breached by unknowns. The data breach has exposed the personal data of about 2.7 million customers of the HSBC bank, […]
 Pierluigi Paganini
November 12, 2014
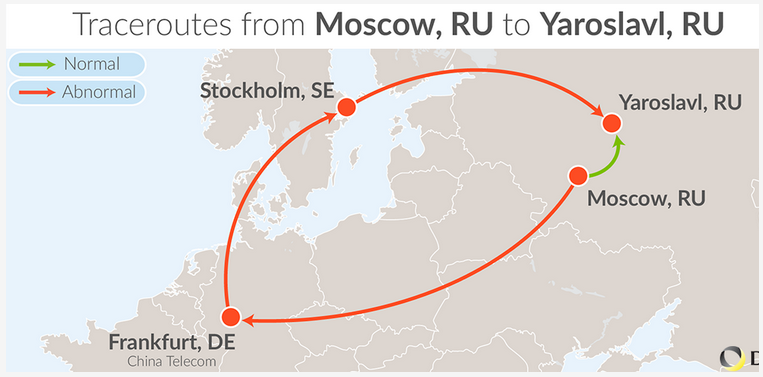
Russian Internet Traffic redirected by a Chinese operator due to routing errors caused by a weakness in the Border gateway protocol (BGP). The Russian Internet traffic in several circumstances has been re-routed outside the country, the incidents seem to be caused by routing errors made by China Telecom. The news has been published by the Internet monitoring service Dyn in a blog […]
 Pierluigi Paganini
November 11, 2014
Happy BirthDay Security Affairs! Three years together, it all began the 11/11/2011, a dream that becomes more and more real every day with your loving support. And it is just the beginning! I’m very happy and proud to be here with you for the third year of SecurityAffairs. We are a growing community that has tens of […]
 Pierluigi Paganini
October 26, 2014
The security firm AdaptiveMobile has discovered a new variant of Koler ransomware is capable of self-replication via SMS messages. A new strain of the Koler Android ransomware is threatening the mobile industry, the new variant spreads itself via SMSs and holds the victim’s device phone hostage until a ransom is paid. The Koler ransomware were detected by experts […]


Security / September 18, 2026

Artificial Intelligence / September 17, 2026
Hacking / September 17, 2026



