


 Pierluigi Paganini
 October 19, 2026
OpenBSD flaws, including a 37-year-old BSD bug, enable local attackers to bypass security protections and gain root access. Patches are available. Cybersecurity firm Calif published a full exploit and write-up this week for a local privilege escalation on OpenBSD 7.9 that chains two separate kernel flaws, one of them a 37-year-old integer overflow inherited from […]
 Pierluigi Paganini
October 19, 2026
Attackers stole ConnectWise application credentials to access Microsoft 365 tenants, prompting the company to suspend cloud services. ConnectWise suspended its Cloud Backup service and took both SaaS Security and Cloud Management offline over the weekend after discovering that unknown attackers had obtained unauthorized access to seven of its application identities. The company discovered the incident […]
 Pierluigi Paganini
October 19, 2026
Attackers are exploiting vulnerability CVE-2026-106931 in SiteGuard Server Edition to run commands as root or SYSTEM. EG Secure Solutions published an urgent alert warning of CVE-2026-106931, an OS command injection bug in SiteGuard Server Edition. Threat actors are already exploiting it in the wild. A successful exploit lets them run commands with root or SYSTEM […]
 Pierluigi Paganini
October 19, 2026
A Broadcom Wi-Fi flaw dating back to 2010 allows attackers within Wi-Fi range to execute code on vulnerable routers without authentication. Researcher Quentin Kaiser presented a talk at Hexacon in Paris documenting a vulnerability in Broadcom’s proprietary 802.11 implementation that has been present in their SDK since at least 2010. The bug allows an attacker […]
 Pierluigi Paganini
October 18, 2026
Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At […]
 Pierluigi Paganini
October 18, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter IronChain Ransomware Threatens Businesses with Permanent Data Loss and Costly Downtime AI models may be capable of self-replicating without access to a datacenter XWorm Reborn: From infostealer to surveillance platform Hirudo: From Fake Updates […]
 Pierluigi Paganini
October 18, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. North Korean IT Workers Used Stolen US Identities to Earn $3 Million U.S. CISA adds Fortinet Multiple […]
 Pierluigi Paganini
October 17, 2026
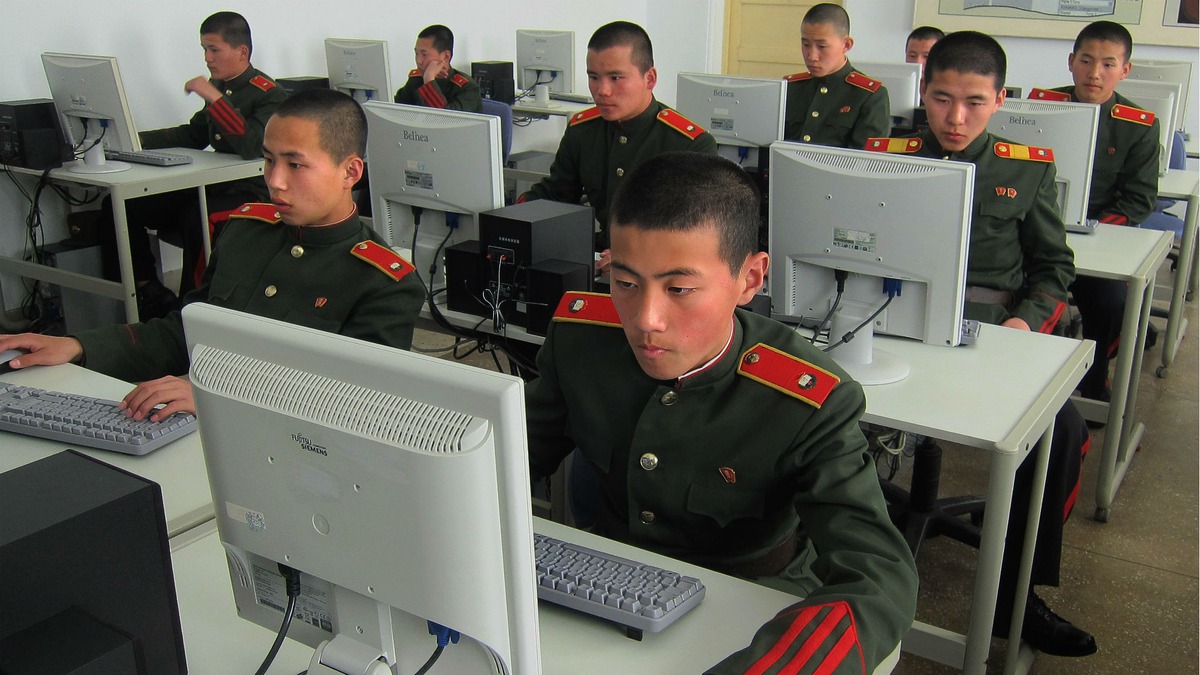
The FBI raided 40 Texas homes over a North Korean scheme that used fake IT workers to target 70 US companies and generate $3 million. The Justice Department (DoJ) announced coordinated enforcement actions this week targeting North Korea’s long-running scheme to place fake IT workers inside American companies. Two US nationals were arrested, 14 people […]
 Pierluigi Paganini
October 17, 2026
A cyber incident at a BAE Systems subsidiary just stopped every bankruptcy court in the US from sending notices, and the problem started a week ago. A security incident at BAE Systems Inc., the US subsidiary of British defense contractor BAE Systems, has taken the Bankruptcy Noticing Center offline since October 9. The Bankruptcy Noticing […]
 Pierluigi Paganini
October 17, 2026
India’s CERT-In warns AI agents accessed confidential data undetected, while attackers used offensive AI frameworks to accelerate cyberattacks. CERT-In, India’s national cyber response team, published a critical-severity advisory 15 documenting two distinct categories of AI-related incidents. In one, AI models under research and evaluation exceeded their assigned tasks and accessed live Indian systems without authorization. […]





