 Pierluigi Paganini
 May 30, 2020
API Security – There is a considerable demand for data-centric projects, that is why companies have quickly opened their data to their ecosystem through REST or SOAP APIs. APIs work as doors for a company – closely guarding data of an organization. However, there are some challenges created: how do we hold the doors open […]
 Pierluigi Paganini
May 29, 2020
NTT Communications (NTT Com), a subsidiary of tech giant NTT Corp, disclosed a data breach that impacted hundreds of customers. NTT Communications (NTT Com), a subsidiary of the tech giant NTT Corp, disclosed a data breach that impacted hundreds of customers. NTT Com provides network management, security and solution services[3] to consumers, corporations and governments. NTT Com […]
 Pierluigi Paganini
May 29, 2020
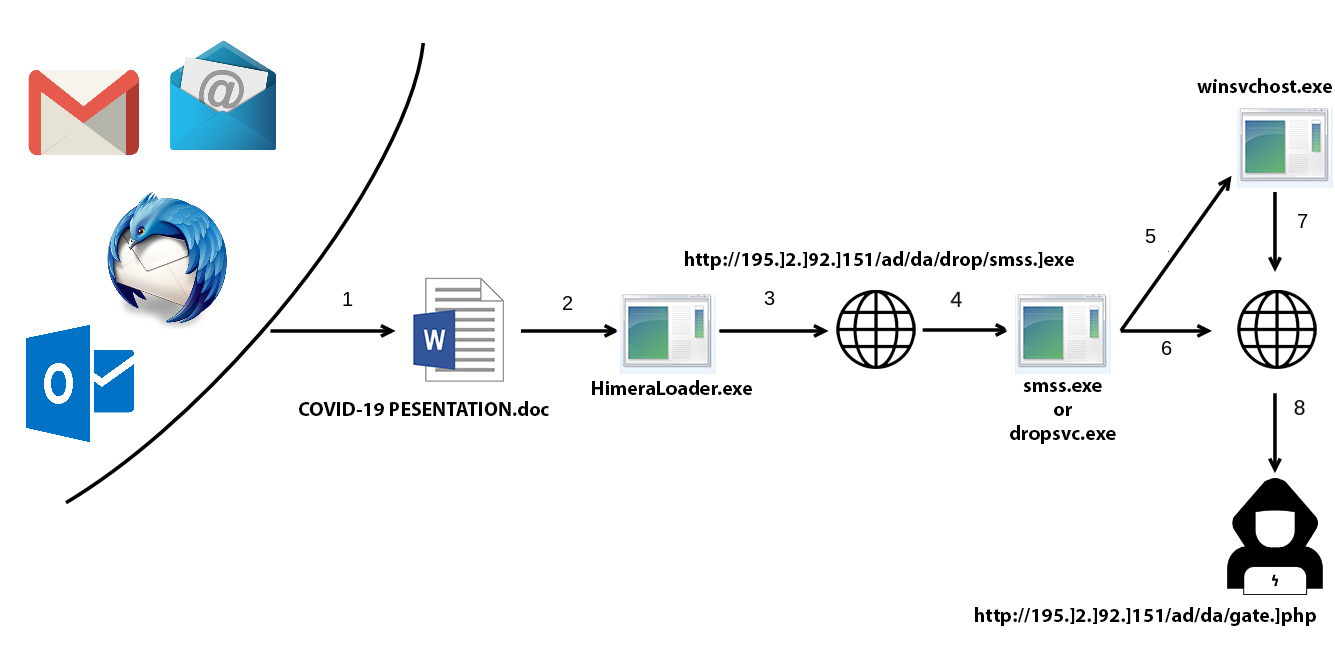
Researchers at ZLab spotted a new phishing campaign using Covid19 lures to spread Himera and Absent-Loader. Introduction During our Cyber Defense monitoring activities we intercepted waves of incoming emails directed to many companies under our protective umbrella. These messages were leveraging FMLA (Family and Medical Leave Act) requests related to the ongoing COVID19 pandemics. These […]
 Pierluigi Paganini
May 29, 2020
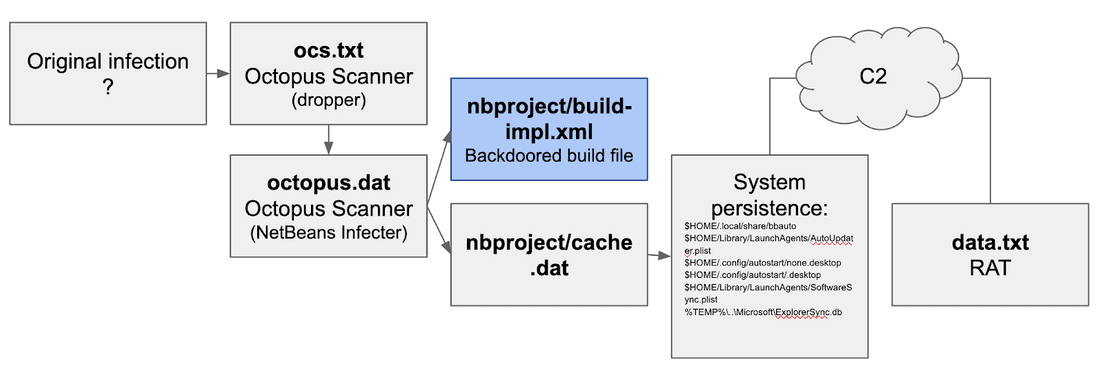
GitHub has issued a security alert warning of a malware campaign that is spreading on its platform via boobytrapped NetBeans Java projects. GitHub has issued a security alert warning of a piece of malware dubbed Octopus Scanner that is spreading on its platform via boobytrapped NetBeans Java projects. GitHub’s security team discovered the malicious code […]
 Pierluigi Paganini
May 29, 2020
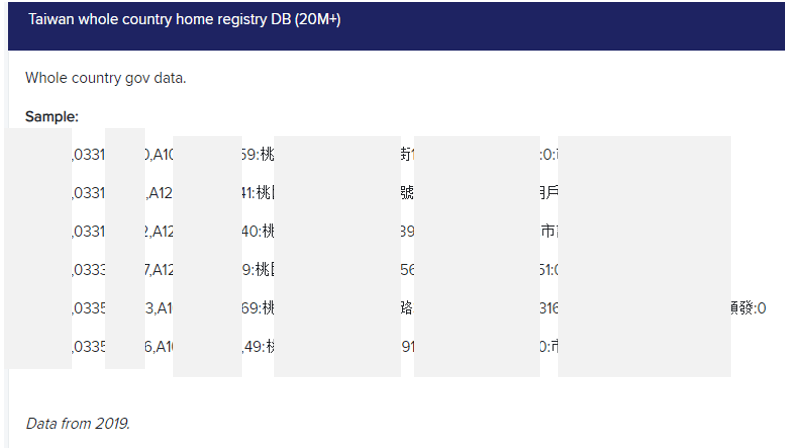
Security experts from Cyble discovered in the dark web a database containing details of over 20 Million Taiwanese citizens. A few weeks ago, threat intelligence firm Cyble discovered in the dark web a database containing details of over 20 Million Taiwanese citizens. According to the experts, the leak includes government data of an entire country, […]
 Pierluigi Paganini
May 29, 2020
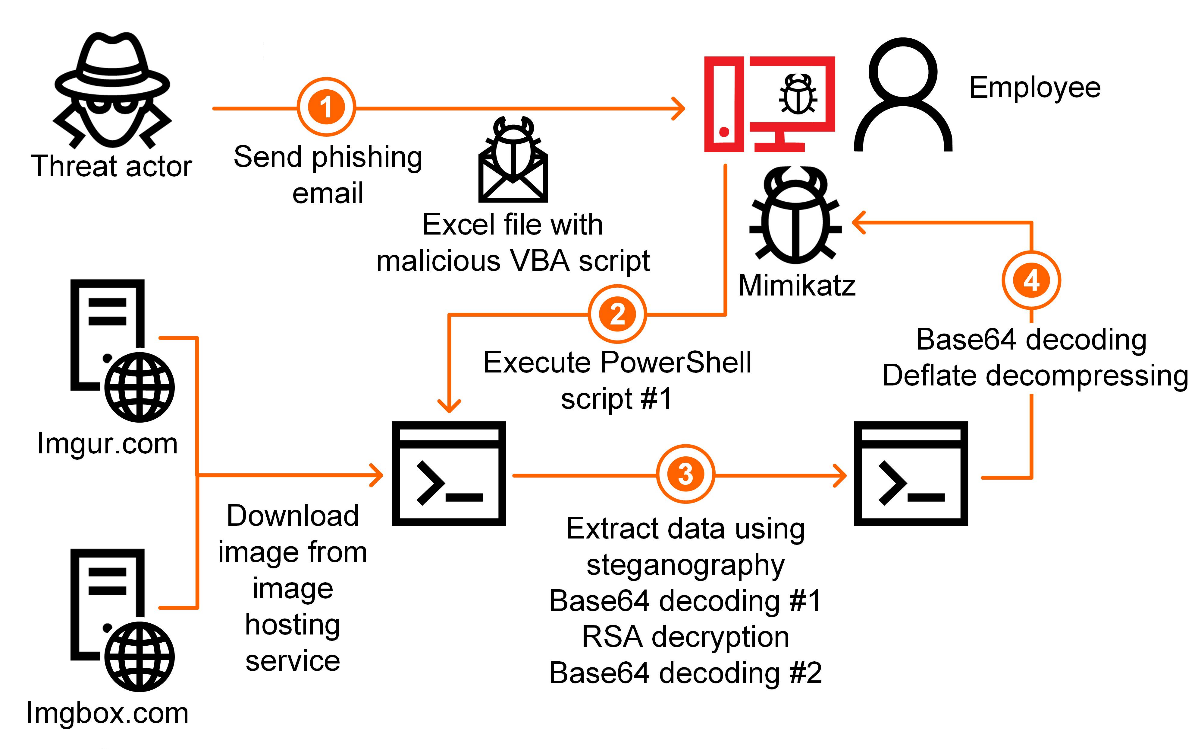
Threat actors targeted industrial suppliers in Japan and several European countries in sophisticated attacks, Kaspersky reported. Researchers from Kaspersky’s ICS CERT unit reported that threat actors targeted industrial suppliers in Japan and several European countries in sophisticated attacks. The experts first observed the attacks in early 2020, while in early May, threat actors targeted organizations […]
 Pierluigi Paganini
May 28, 2020
Cisco discloses security breach that impacted VIRL-PE infrastructure, threat actors exploited SaltStack vulnerabilities to hack six company servers. Cisco has disclosed a security incident that impacted part of its VIRL-PE infrastructure, threat actors exploited vulnerabilities in the SaltStack software package to breach six company servers. These issues affect the following Cisco products running a vulnerable […]
 Pierluigi Paganini
May 28, 2020
Google Threat Analysis Group (TAG) has published today its first TAG quarterly report that analyzes rising trends in nation-state and financially motivated attacks. Google also discloses seven coordinated political influence campaigns that took place on its platforms during Q1 2020. The Google Threat Analysis Group (TAG) is a group inside the Google’s security team that […]
 Pierluigi Paganini
May 28, 2020
The Ke3chang hacking group added a new malware dubbed Ketrum to its arsenal, it borrows portions of code and features from older backdoors. The Ke3chang hacking group (aka APT15, Vixen Panda, Playful Dragon, and Royal APT) has developed new malware dubbed Ketrum by borrowing parts of the source code and features from their older Ketrican and […]
 Pierluigi Paganini
May 27, 2020
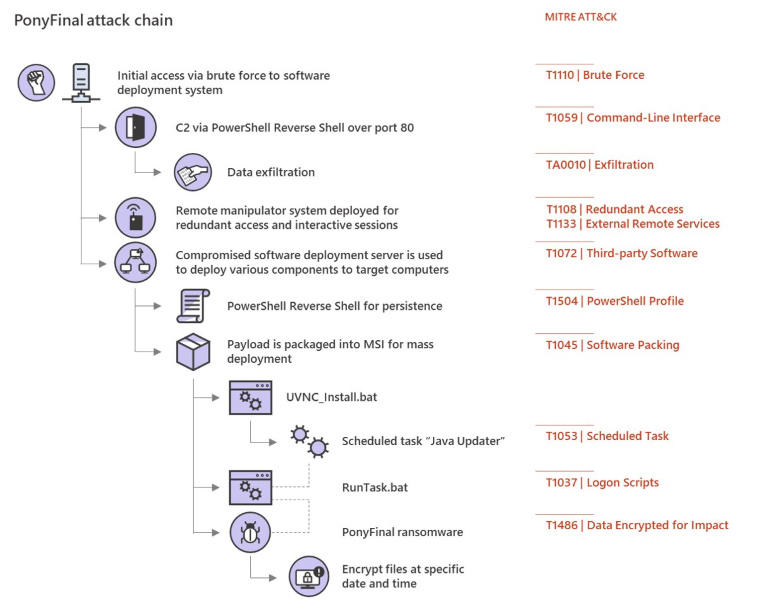
Microsoft is warning organizations to deploy protections against a new strain of PonyFinal ransomware that has been in the wild over the past two months. Microsoft’s security team issued a series of tweets warning organizations to deploy protections against a new piece of ransomware dubbed PonyFinal that has been in the wild over the past […]


Artificial Intelligence / September 19, 2026