


 Pierluigi Paganini
 June 08, 2020
A Korean threat actor, tracked as Higaisa, has been using malicious LNK files in recent attacks aimed at organizations that use the Zeplin collaboration platform. The Korean threat actor Higaisa, has been using malicious LNK files in recent attacks aimed at organizations that use the Zeplin collaboration platform. The group is believed to be a […]
 Pierluigi Paganini
June 08, 2020
Any Indian DigiLocker Account Could’ve Been Accessed Without Password The Indian Government fixed a flaw in the secure document wallet service Digilocker that could have potentially allowed anyone’s access without password. The Indian Government announced to have fixed a critical vulnerability in its secure document wallet service Digilocker that could have potentially allowed a remote attacker […]
 Pierluigi Paganini
June 08, 2020
IBM has released open-source toolkits implementing fully homomorphic encryption (FHE) that allow researchers to process data while it’s still encrypted. IBM has released open-source toolkits implementing fully homomorphic encryption (FHE), which allows researchers to process encrypted data without having access to the actual data. The toolkits released by IBM are already available for macOS and […]
 Pierluigi Paganini
June 08, 2020
Researchers uncovered a malware campaign that is targeting Windows and Linux servers with a Golang-based malicious code called Stealthworker. Akamai researchers uncovered a malware campaign spreading a Golang-based malicious code tracked as Stealthworker. The malware targets Windows and Linux servers running popular web services and platforms including (i.e. cPanel / WHM, WordPress, Drupal, Joomla, OpenCart, Magento, […]
 Pierluigi Paganini
June 07, 2020
British Army has created a new regiment that will be tasked to operate its in-house security operations centre … cybersecurity is a pillar of UK defence strategy! The British Ministry of Defence continues to invest in cybersecurity as part of its strategy, it has launched a new regiment that will take charge of its in-house […]
 Pierluigi Paganini
June 07, 2020
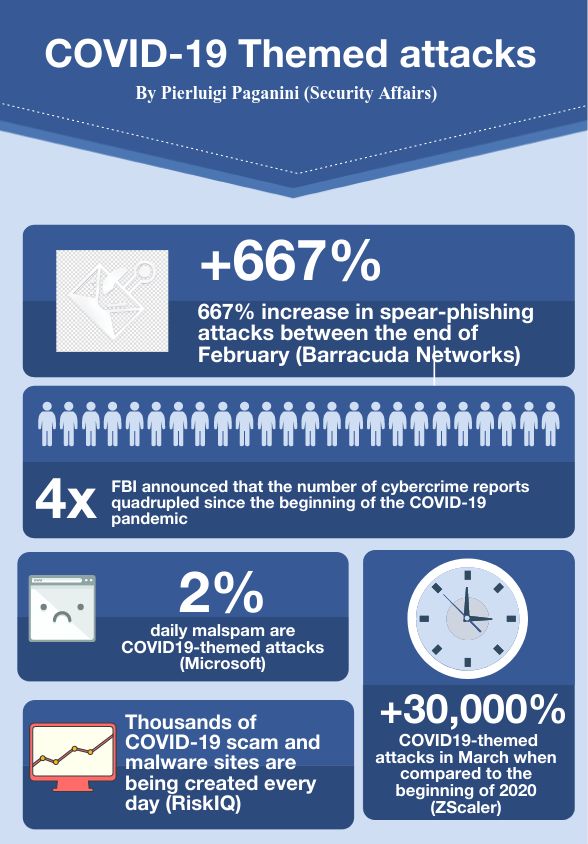
This infographic includes interesting data related to the Covid-19 themed attacks observed by security researchers and law enforcement in the past months. [adrotate banner=”9″] [adrotate banner=”12″] Pierluigi Paganini (SecurityAffairs – COVID-19, hacking) [adrotate banner=”5″] [adrotate banner=”13″]
 Pierluigi Paganini
June 07, 2020
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. Anonymous demands justice for George Floyd and threatens attacks ENISA published Proactive detection – Measures and information sources report Over 100K+ WordPress sites using PageLayer plugin exposed to hack Expert […]
 Pierluigi Paganini
June 06, 2020
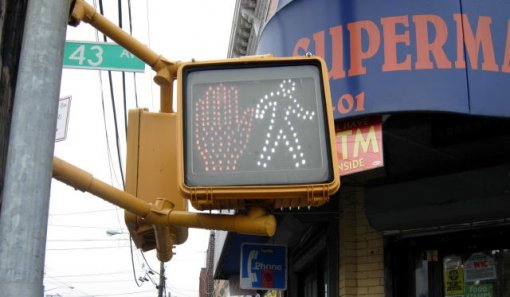
A critical vulnerability in traffic light controllers manufactured by SWARCO could have been exploited by attackers to disrupt traffic lights. A critical vulnerability in traffic light controllers designed by SWARCO could have been exploited by hackers to disrupt traffic lights. SWARCO is the world’s largest manufacturer of signal heads and the number two internationally for […]
 Pierluigi Paganini
June 06, 2020
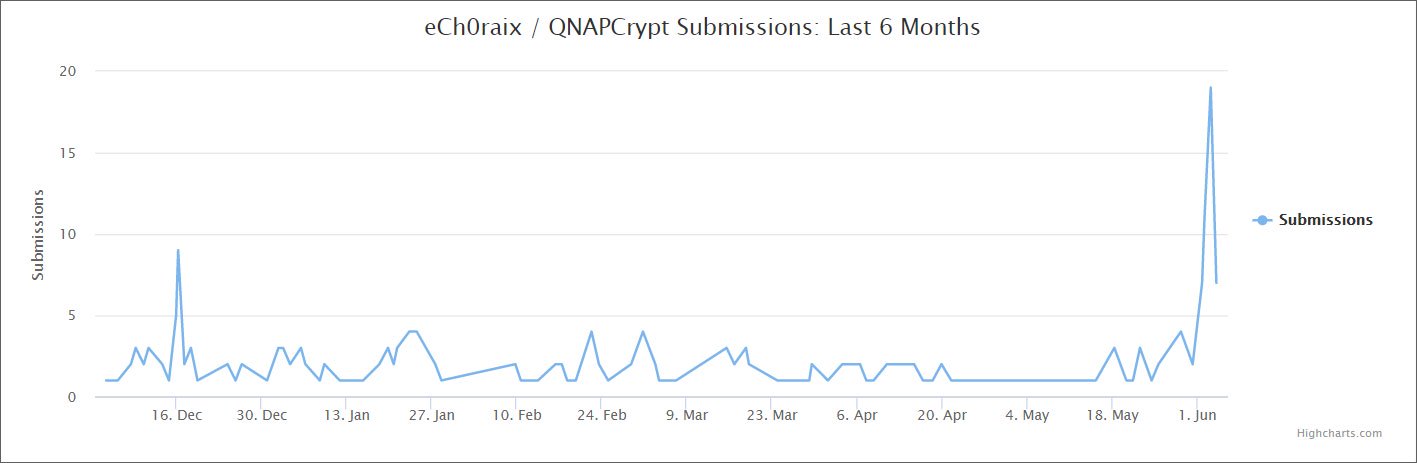
eCh0raix Ransomware operators are back after months of apparent inactivity, now are targeting QNAP storage devices in a new campaign. Threat actors behind the eCh0raix Ransomware have launched a new campaign aimed at infecting QNAP storage devices. The eCh0raix ransomware was appeared in the threat landscape in June 2019 by experts at security firms Intezer […]
 Pierluigi Paganini
June 05, 2020
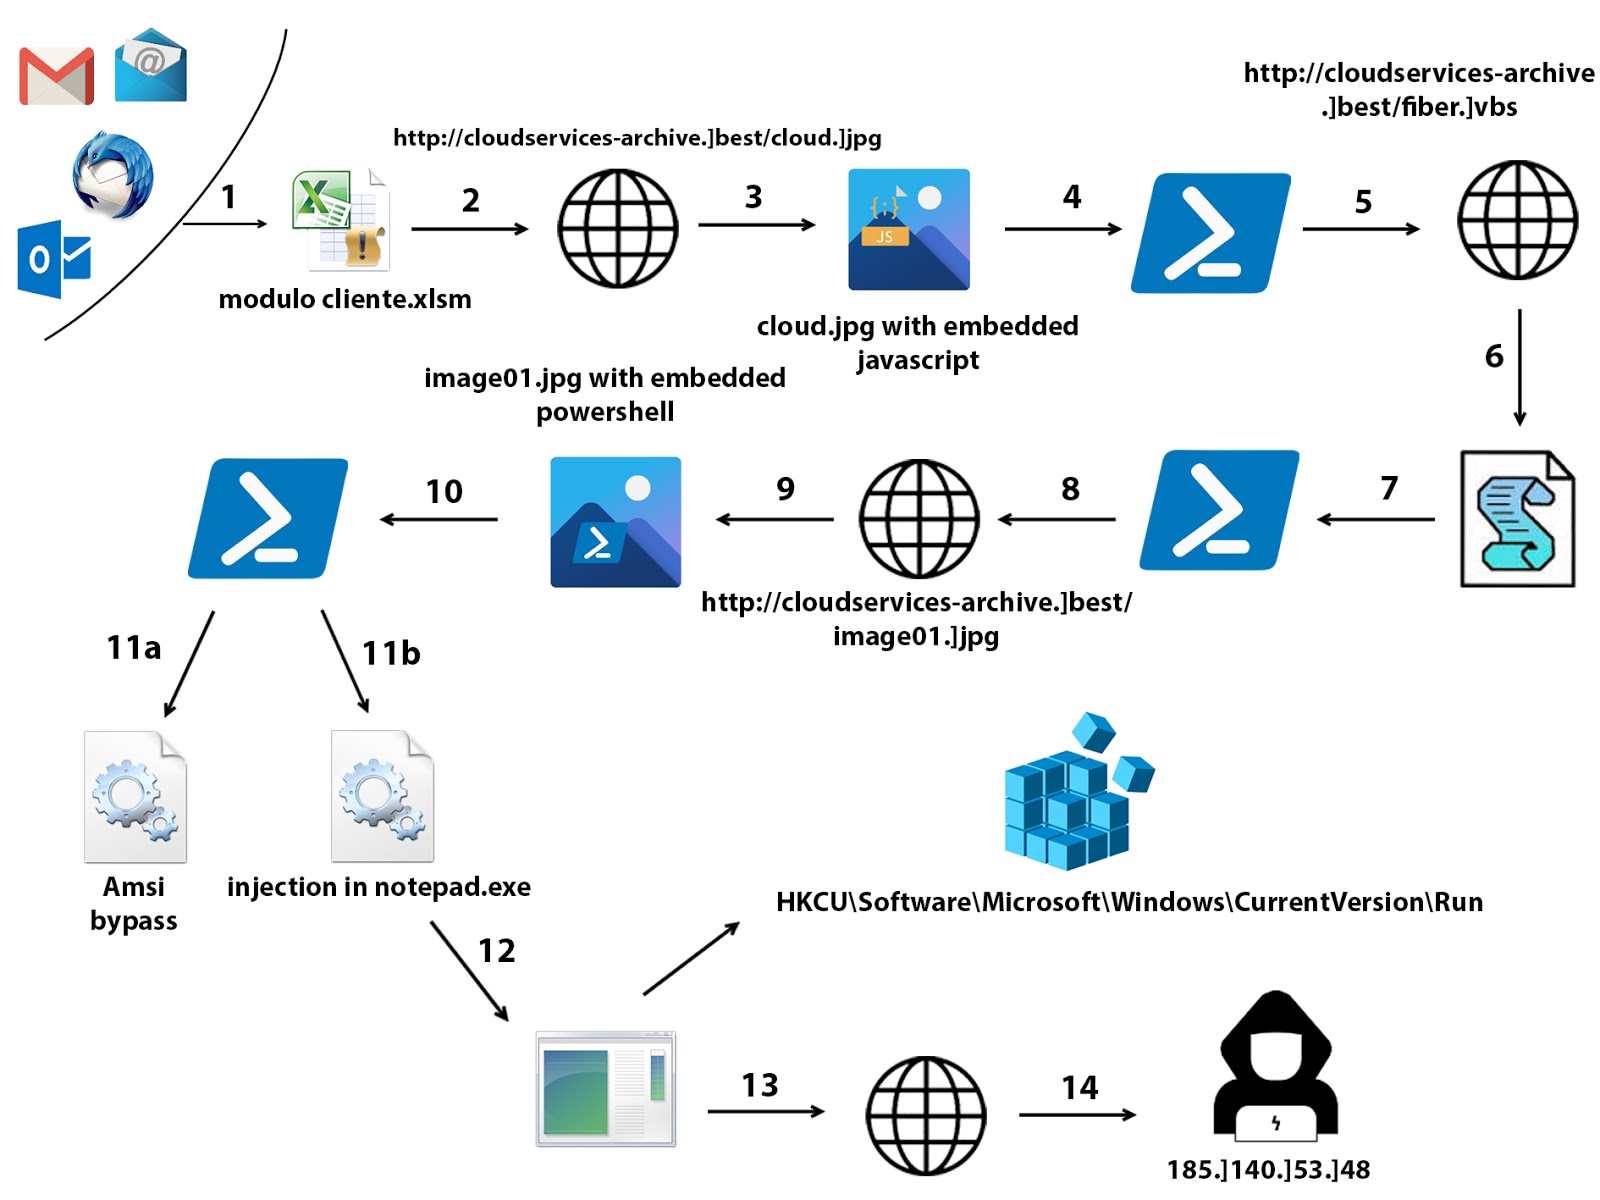
ZLab malware researchers analyzed the attack chain used to infect Italian speaking victims with the Netwire malware. Introduction Info stealer malware confirms to be one of the most adopted weapons of cyber actors. One of them is Netwire (MITRE S0198), a multiplatform remote administration tool (RAT) that has been used by criminals and espionage groups […]
Uncategorized / September 27, 2026
Cyber Crime / September 26, 2026

Security / September 26, 2026


