


 Pierluigi Paganini
 June 28, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter More Than 4,000 Legacy Routers Compromised by AryStinger, Turned into Global Attack Proxies for Hackers A VBScript campaign distributed through WhatsApp deploying RMM software Lost in relocation: analysis of a new loader distributing CASTLESTEALER […]
 Pierluigi Paganini
June 28, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. New FBI Alert: Russian Intelligence Uses Signal Recovery Keys to Access Messages Hospitality Sector Hit by […]
 Pierluigi Paganini
June 27, 2026
FBI warns Russian spies now target Signal Backup Recovery Keys, enabling access to message history and long-term account takeover. The FBI and CISA updated their March 2026 warning about Russian intelligence phishing campaigns, and the new advisory adds a detail that wasn’t in the original: the operators have shifted their primary objective from stealing verification […]
 Pierluigi Paganini
June 27, 2026
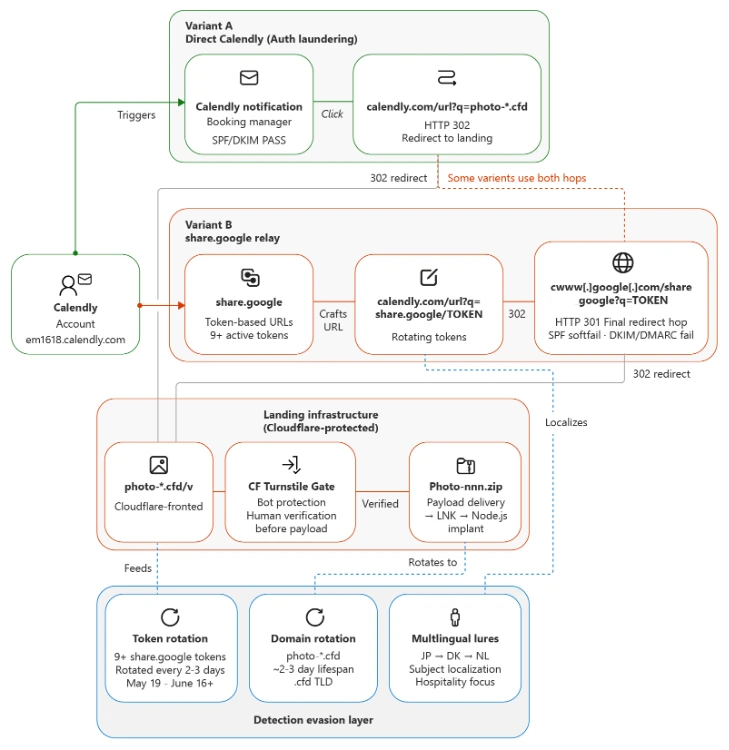
Microsoft warns of a phishing campaign targeting the hospitality sector with fake guest emails that install TonRAT using resilient persistence. Microsoft Threat Intelligence published a detailed analysis on an ongoing hacking campaign against hospitality organizations that has been running since April 2026. The targets are specific: device names observed across compromised environments include strings like […]
 Pierluigi Paganini
June 26, 2026
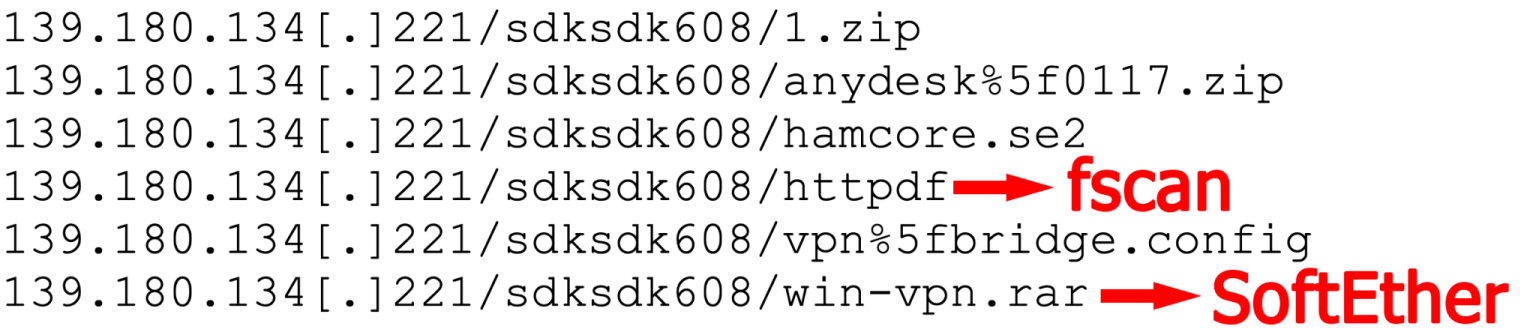
Chinese-speaking APT CL-STA-1062 targeted Southeast Asian government and energy networks open-source tools, and a new TinyRCT backdoor. Palo Alto Networks Unit 42 researchers published a detailed report on a Chinese-speaking threat actor, tracked as CL-STA-1062, that has been running persistent operations across East Asia since at least March 2022 and shifted focus to Southeast Asian […]
 Pierluigi Paganini
June 26, 2026
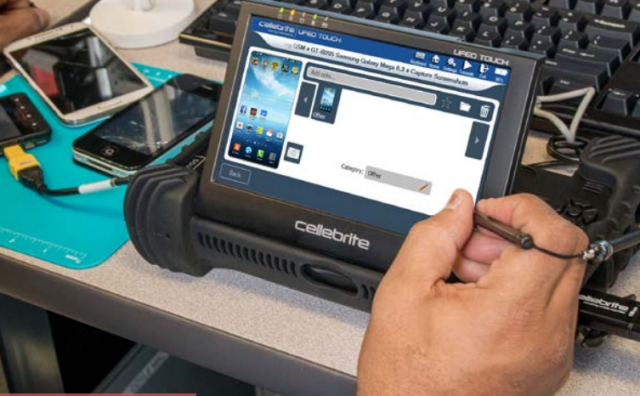
Russian authorities used Cellebrite tools to unlock an activist’s iPhone and analyze private data despite canceled support, raising abuse concerns. On May 31, 2021, Russian security services pulled opposition activist Andrey Pivovarov off a flight at St. Petersburg airport and confiscated his iPhone 12 and MacBook. He never consented to a search and never gave […]
 Pierluigi Paganini
June 26, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco and PTC Windchill and FlexPLM flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Cisco and PTC Windchill and FlexPLM flaws to its Known Exploited Vulnerabilities (KEV) catalog. The two flaws added to the catalog are: CVE-2026-12569 is a critical remote […]
 Pierluigi Paganini
June 26, 2026
Polymarket confirmed hackers stole funds from some users after attackers injected malicious code through a compromised third-party vendor. Polymarket confirmed that a security breach at a third-party vendor allowed attackers to inject malicious code into its website, leading to the theft of funds from an undisclosed number of users. The company said it has contained […]
 Pierluigi Paganini
June 26, 2026
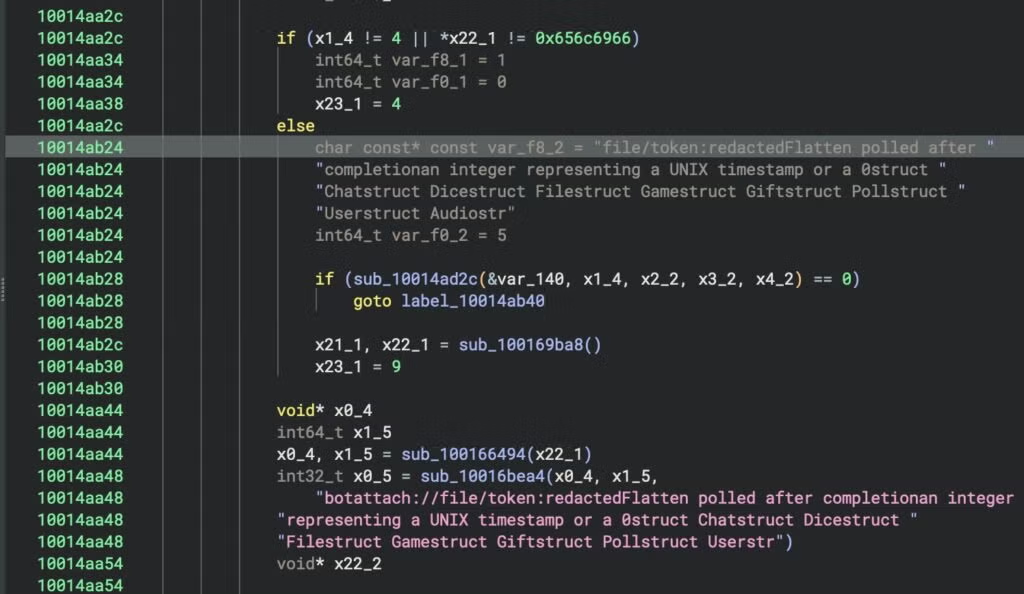
macOS.Gaslight: DPRK Rust implant for Mac with a prompt injection payload designed to fool AI-based malware analysts. SentinelLabs researchers spotted a Rust-based macOS implant, dubbed macOS.Gaslight, that surfaced in early June after an Apple XProtect update pointed to a VirusTotal sample uploaded on May 22. The binary was undetected by static engines at the time […]
 Pierluigi Paganini
June 25, 2026
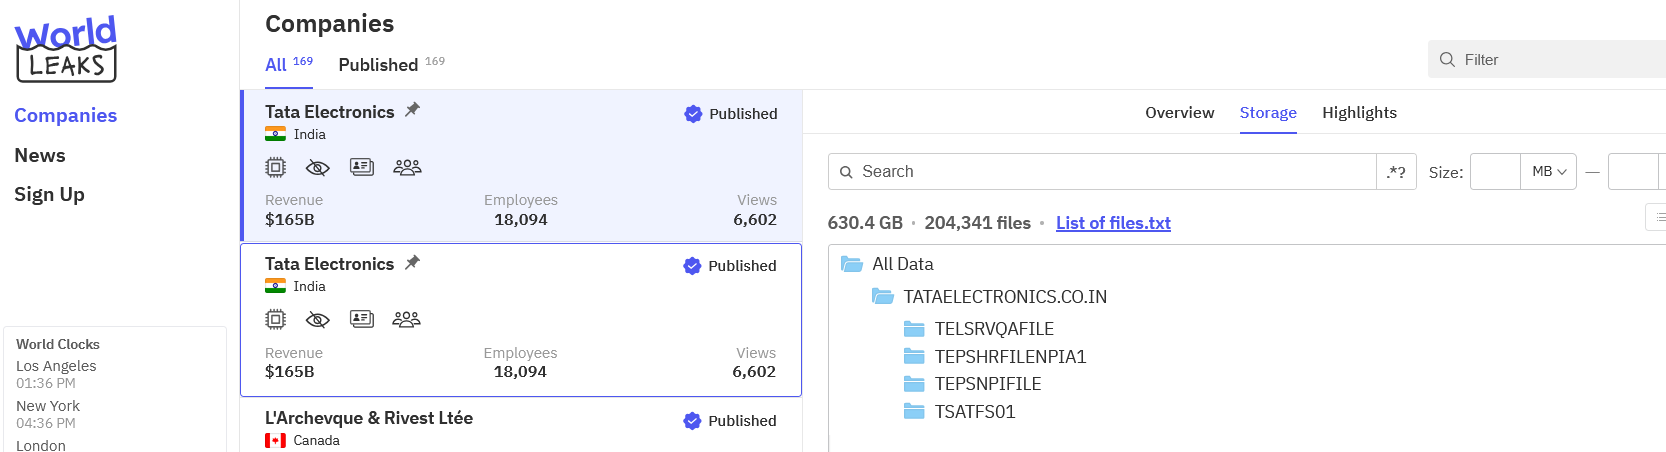
Tata Electronics confirmed a data breach after hackers claimed to steal 630GB of data, including alleged Apple supplier and Tesla documents. Tata Electronics, a major supplier to Apple and Tesla, has confirmed a cybersecurity breach weeks after stolen data was advertised on a hacker forum. Tata Electronics confirmed a cyberattack affected parts of its IT […]


Security / September 18, 2026

Artificial Intelligence / September 17, 2026


