


 Pierluigi Paganini
 August 04, 2022
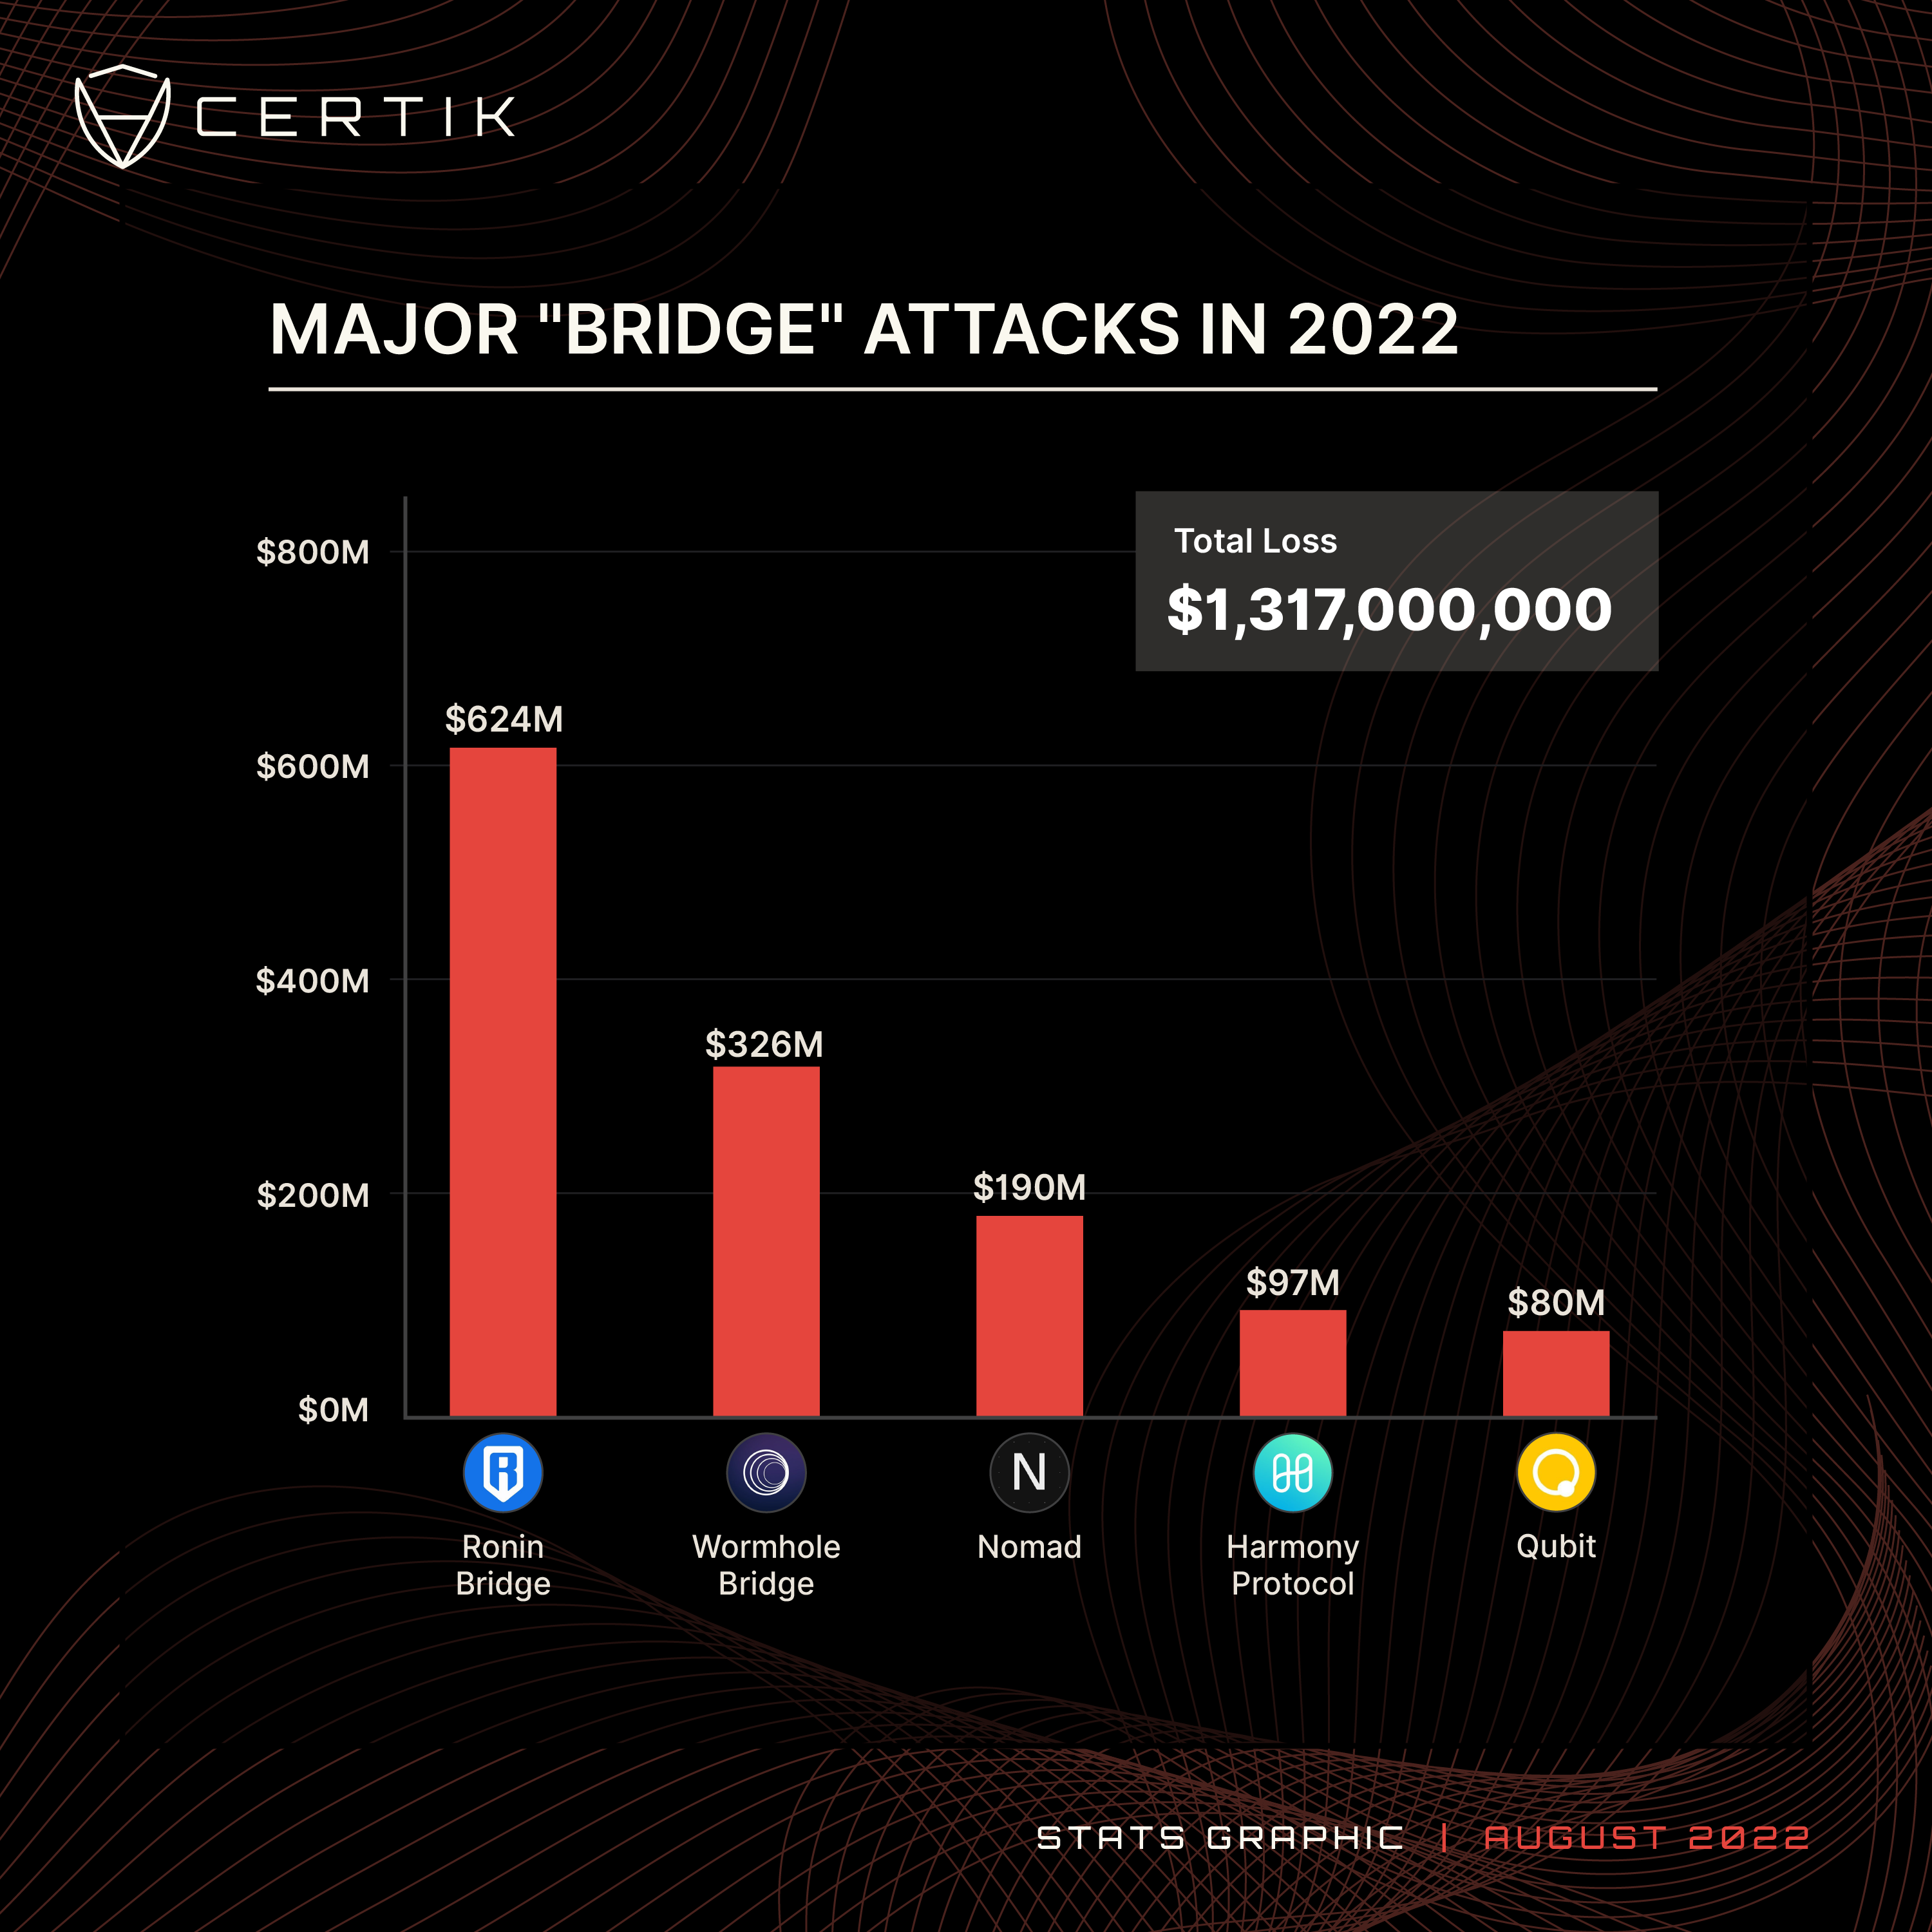
The cryptocurrency bridge Nomad is the last victim of a cyber heist, threat actors stole almost $200 million of its funds. Another crypto heist made the headlines, threat actors stole nearly $200 million worth of cryptocurrency from the bridge Nomad. Nomad Bridge is a cross-chain bridge between Ethereum, Moonbeam, Avalanche, Evmos and Milkomeda. The project […]
 Pierluigi Paganini
August 04, 2022
Cisco fixes critical remote code execution vulnerability, tracked as CVE-2022-20842, impacting Small Business VPN routers. Cisco addressed a critical security vulnerability, tracked as CVE-2022-20842, impacting Small Business VPN routers. The flaw resides in the web-based management interface of several Small Business VPN routers, including Cisco RV340, RV340W, RV345, and RV345P Dual WAN Gigabit VPN Routers. […]
 Pierluigi Paganini
August 03, 2022
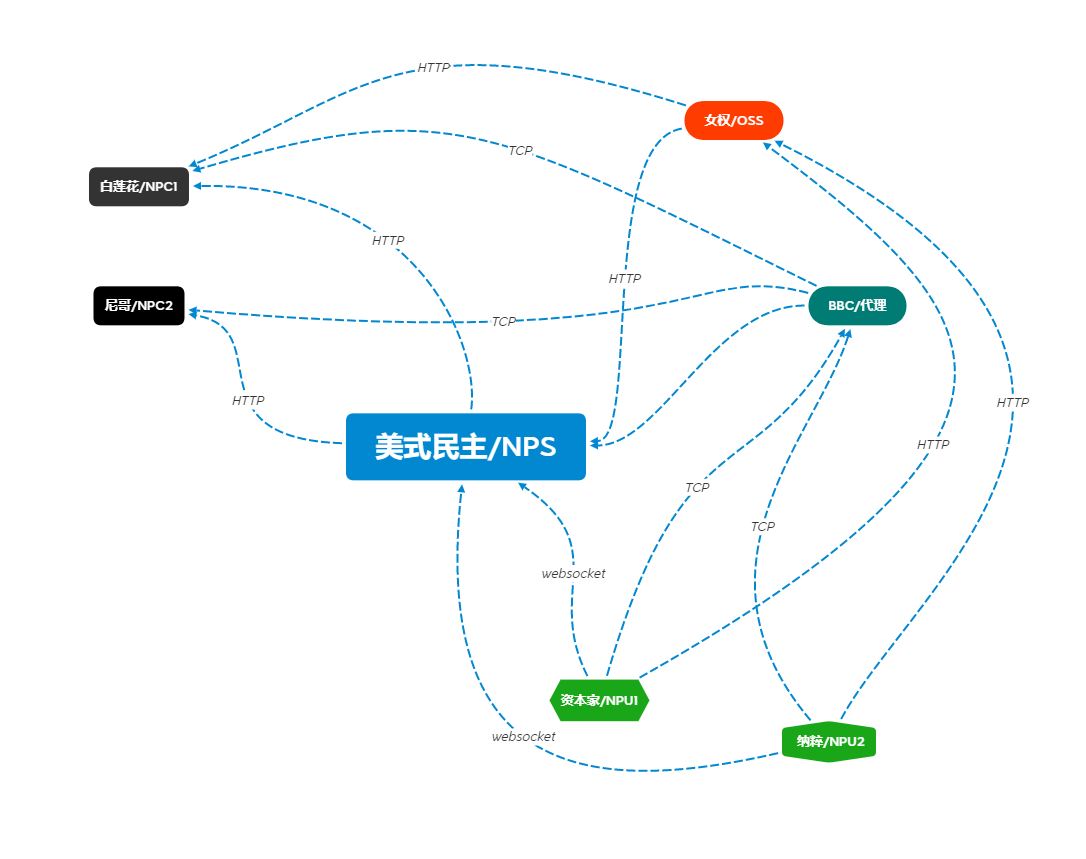
Researchers spotted a Chinese threat actors using a new offensive framework called Manjusaka which is similar to Cobalt Strike. Talos researchers observed a Chinese threat actor using a new offensive framework called Manjusaka (which can be translated to “cow flower” from the Simplified Chinese writing) that is similar to Sliver and Cobalt Strike tools. The […]
 Pierluigi Paganini
August 02, 2022
VMware patched a critical authentication bypass security flaw, tracked as CVE-2022-31656, impacting local domain users in multiple products. VMware has addressed a critical authentication bypass security flaw, tracked as CVE-2022-31656, impacting local domain users in multiple products. An unauthenticated attacker can exploit the vulnerability to gain admin privileges. “A malicious actor with network access to the […]
 Pierluigi Paganini
August 02, 2022
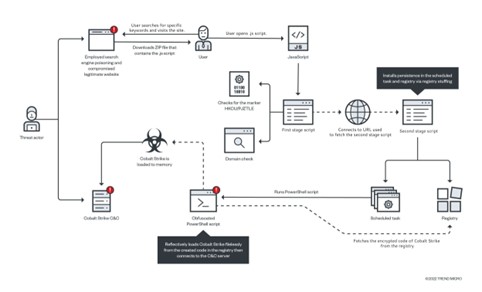
Gootkit access-as-a-service (AaaS) malware is back with tactics and fileless delivery of Cobalt Strike beacons. Gootkit runs on an access-a-as-a-service model, it is used by different groups to drop additional malicious payloads on the compromised systems. Gootkit has been known to use fileless techniques to deliver threats such as the SunCrypt, and REvil (Sodinokibi) ransomware, Kronos trojans, […]
 Pierluigi Paganini
August 02, 2022
Austria is investigating a report that an Austrian firm DSIRF developed spyware targeting law firms, banks and consultancies. At the end of July, Microsoft Threat Intelligence Center (MSTIC) and the Microsoft Security Response Center (MSRC) researchers linked a threat group known as Knotweed to an Austrian surveillance firm named DSIRF, known for using multiple Windows […]
 Pierluigi Paganini
August 01, 2022
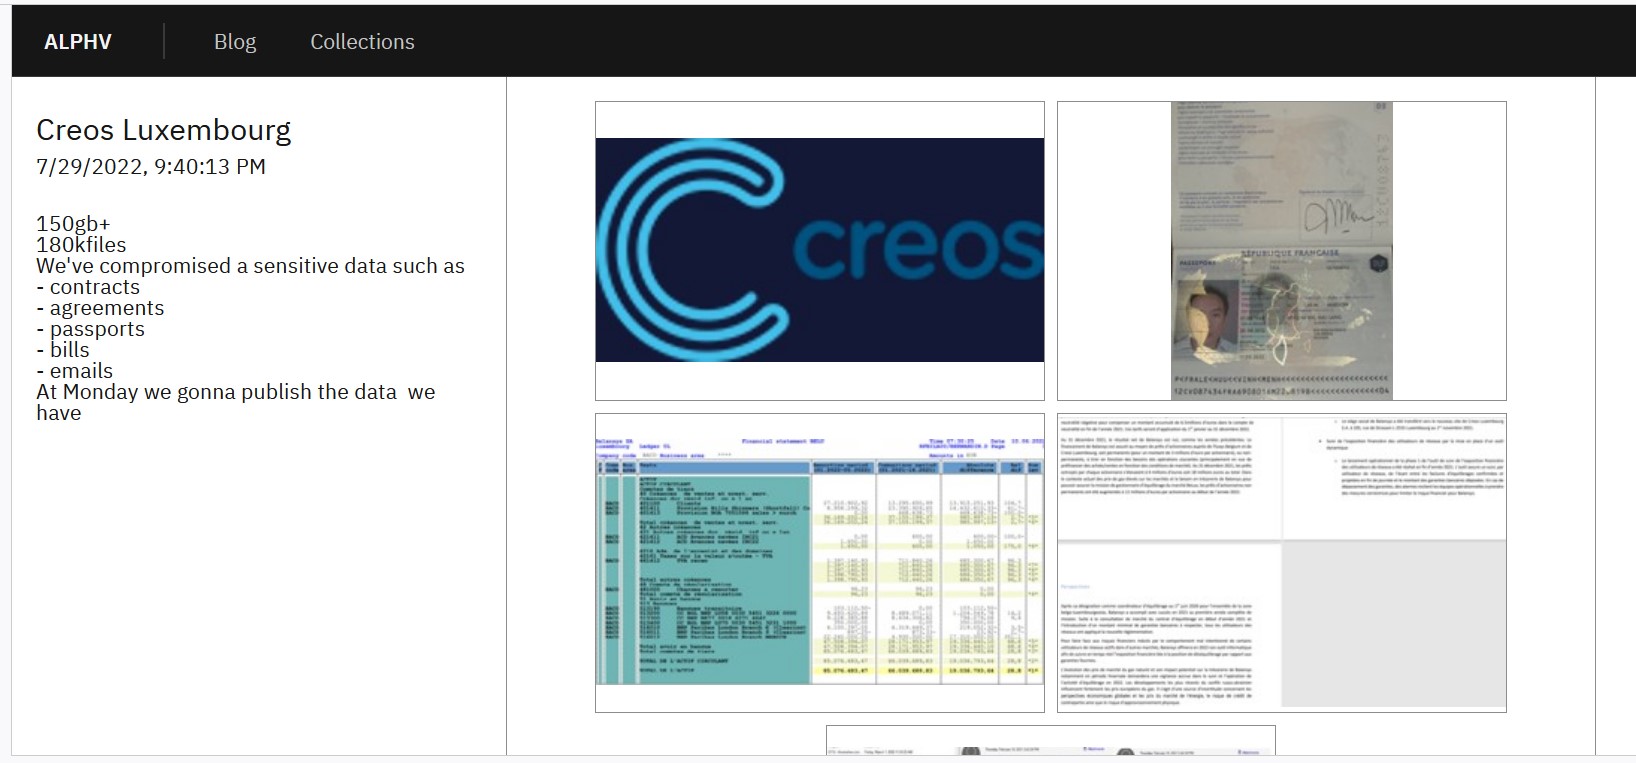
The ALPHV/BlackCat ransomware gang claims to have breached the European gas pipeline Creos Luxembourg S.A. The ALPHV/BlackCat ransomware gang claims to have hacked the European gas pipeline Creos Luxembourg S.A. Creos Luxembourg S.A. owns and manages electricity networks and natural gas pipelines in the Grand Duchy of Luxembourg. In this capacity, the company plans, constructs […]
 Pierluigi Paganini
August 01, 2022
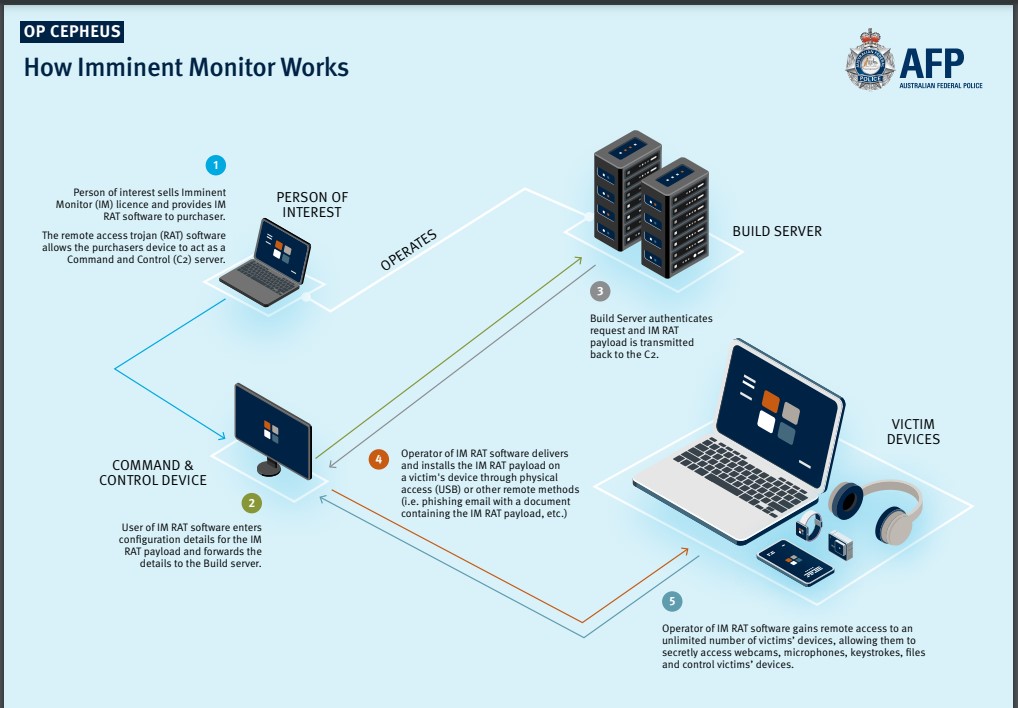
An Australian national has been charged for the creation and sale of the Imminent Monitor (IM) spyware, which was also used for criminal purposes. The 24-year-old Australian national Jacob Wayne John Keen has been charged for his alleged role in the development and sale of spyware known as Imminent Monitor (IM). The Australian Federal Police (AFP) launched […]
 Pierluigi Paganini
August 01, 2022
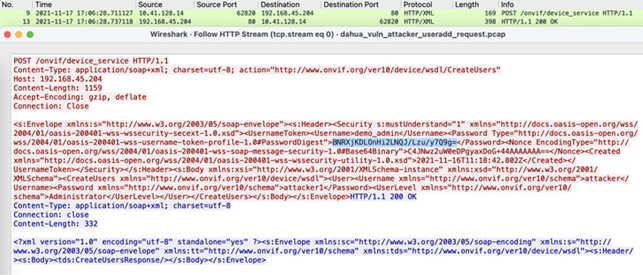
A vulnerability, tracked as CVE-2022-30563, impacting Dahua IP Camera can allow attackers to seize control of IP cameras. The CVE-2022-30563 vulnerability impacting Dahua IP Camera can allow attackers to seize control of IP cameras. The issue affects Dahua’s implementation of the Open Network Video Interface Forum (ONVIF). ONVIF provides and promotes standardized interfaces for effective […]
 Pierluigi Paganini
August 01, 2022
The Federal Communications Commission (FCC) warned Americans of the rising threat of smishing (robotexts) attacks. The Federal Communications Commission (FCC) issued an alert to warn Americans of the rising threat of smishing (robotexts) attacks aimed at stealing their personal information or for financial scams. “The FCC’s Robocall Response Team is alerting consumers to the rising […]






