Pierluigi Paganini
 October 29, 2026
Volt Typhoon used disposable relay chains to hide zero-day attacks on critical systems. Lumen linked Silent Train to at least four zero-days. Lumen’s Black Lotus Labs has spent three years tracking a covert network it calls Silent Train, which it ties to Volt Typhoon, the China-linked APT group. The cybersecurity firm says the network hid […]
 Pierluigi Paganini
October 26, 2026
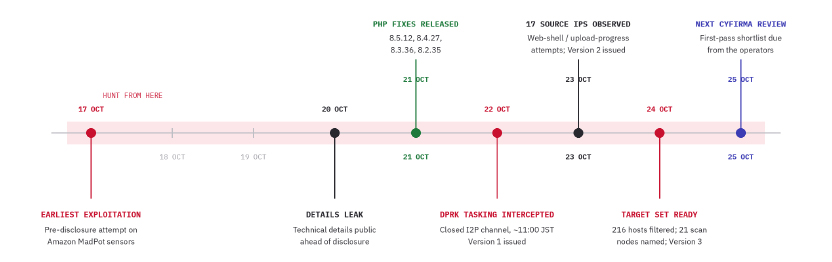
Cyfirma links PHP2Shell scans of 216 vulnerable hosts to a suspected North Korean campaign using AI to rank public exploits. On October 21, PHP released emergency patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on the CVSS scale. The flaws affect all PHP versions that handle web requests. The vulnerable code dates […]
 Pierluigi Paganini
October 22, 2026
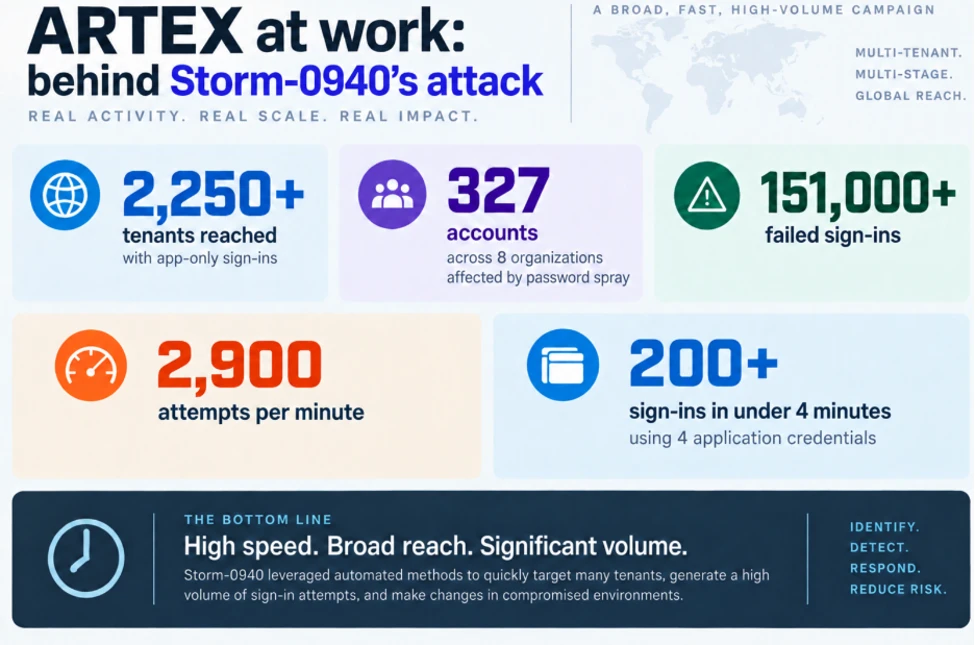
China-linked Storm-0940 used AI tool ARTEX to target 2,250 Microsoft 365 tenants, exploiting stolen ConnectWise credentials at machine speed. Microsoft published a detailed technical report naming Storm-0940, a China state-aligned group, as the actor behind the ConnectWise Cloud Backup supply chain compromise. The group used ARTEX, an open-source AI-driven penetration testing framework, to run attacks […]
 Pierluigi Paganini
October 17, 2026
The FBI raided 40 Texas homes over a North Korean scheme that used fake IT workers to target 70 US companies and generate $3 million. The Justice Department (DoJ) announced coordinated enforcement actions this week targeting North Korea’s long-running scheme to place fake IT workers inside American companies. Two US nationals were arrested, 14 people […]
 Pierluigi Paganini
October 15, 2026
Silent Lynx, a group likely based in Kazakhstan, targets Russian energy and government entities in espionage campaigns across Central Asia. Researchers from Cisco Talos and Recorded Future published a detailed paper on a threat actor they call Silent Lynx (aka UAT-6275, TAG-193), a Kazakhstan nexus group conducting espionage across Central Asia. The targets include the […]
 Pierluigi Paganini
October 08, 2026
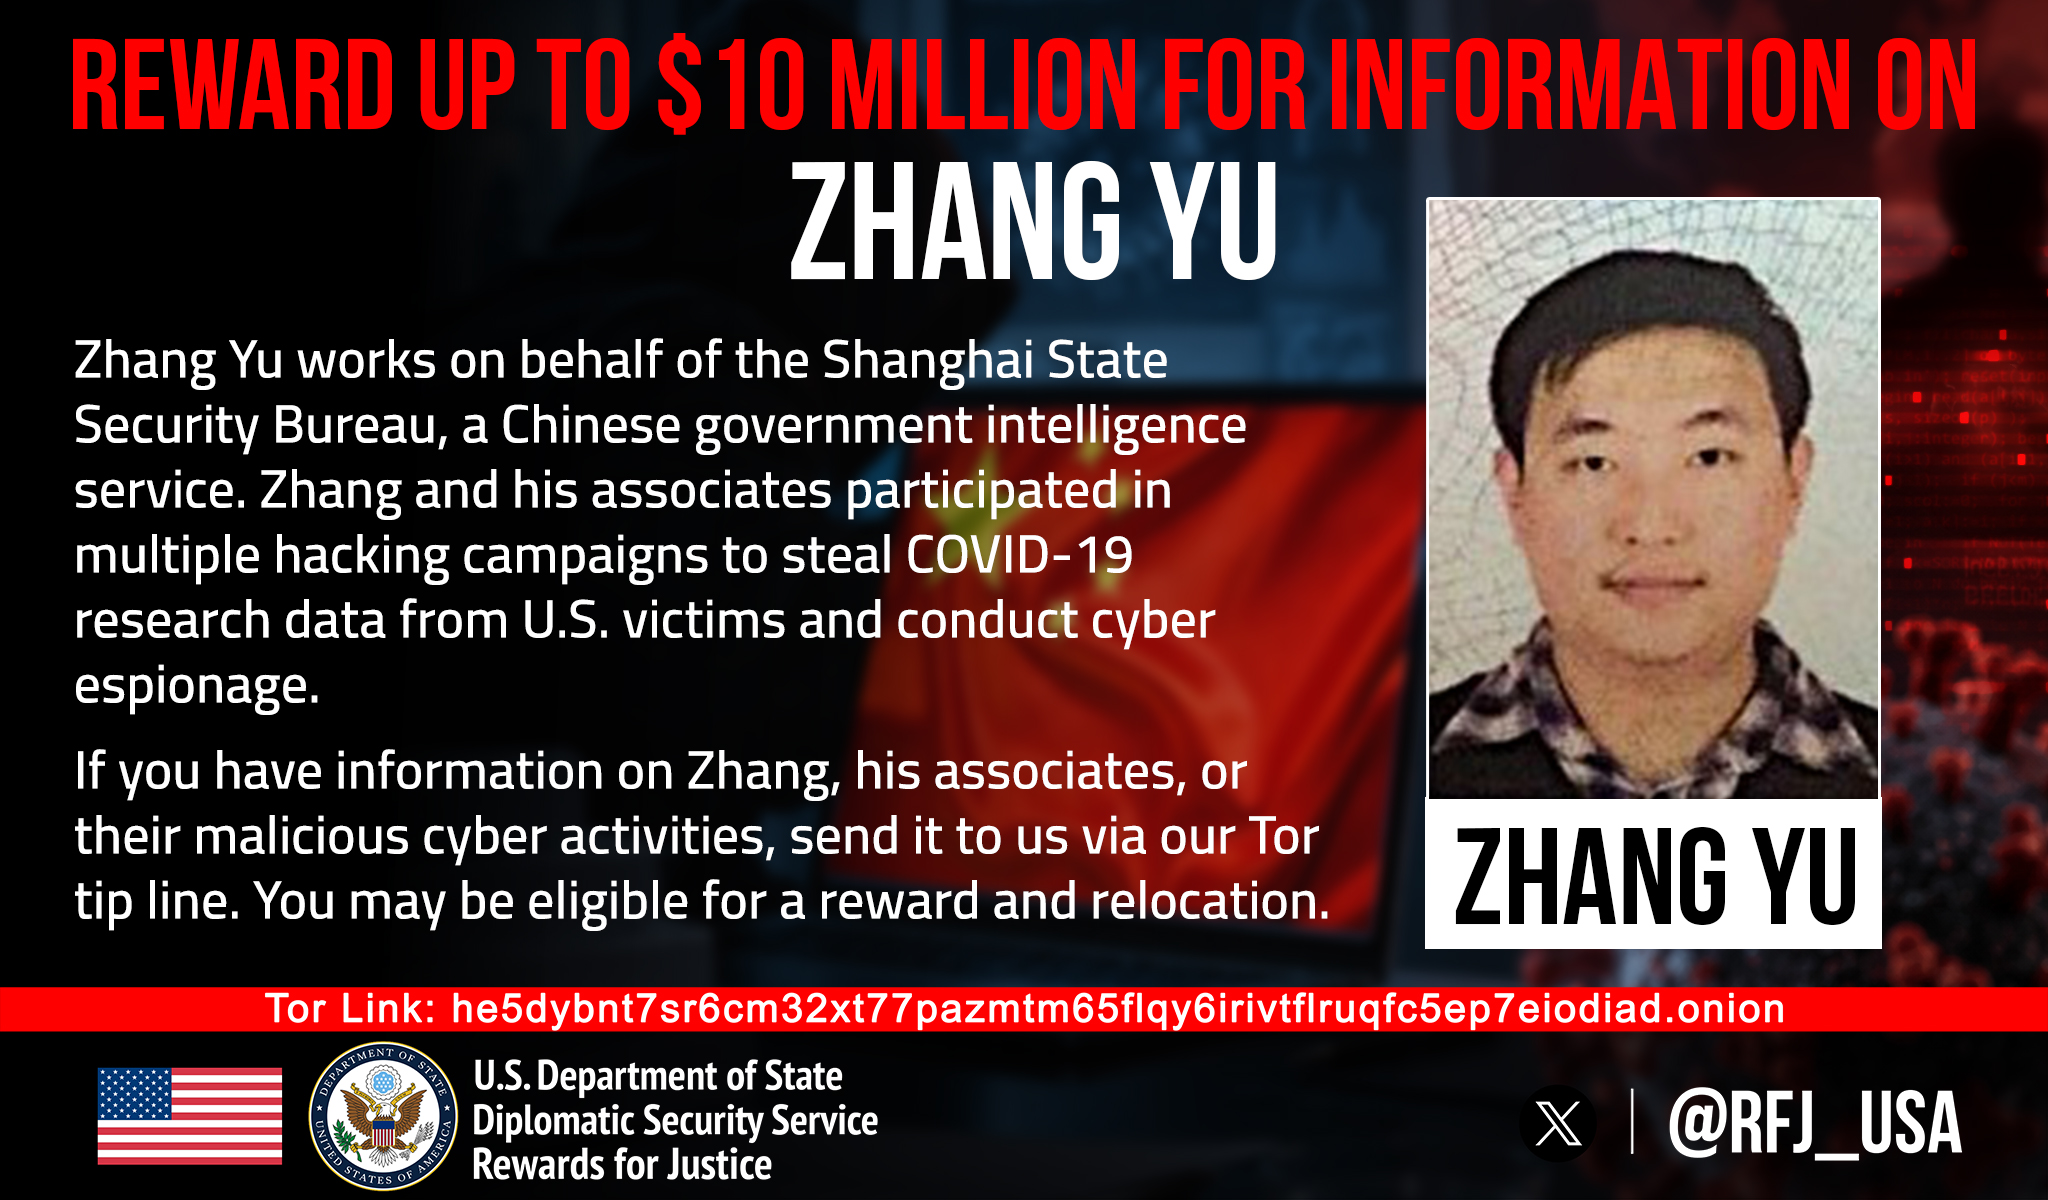
The U.S. offers $10M for Zhang Yu, accused of helping run HAFNIUM attacks that compromised thousands of organizations worldwide. The U.S. State Department is offering a $10 million reward for information leading to the arrest of Zhang Yu. He is accused of being a key figure in the HAFNIUM campaign, the 2021 operation that targeted […]
 Pierluigi Paganini
October 04, 2026
Warlock ransomware continues to exploit unpatched SharePoint flaws to breach water utilities, telecoms, governments, and universities worldwide. Warlock ransomware made headlines back in mid-2025 for exploiting a chain of SharePoint zero-days collectively dubbed ToolShell. More than a year later, the same group is still using that door, and it’s still getting in. Symantec tracks the […]
 Pierluigi Paganini
October 03, 2026
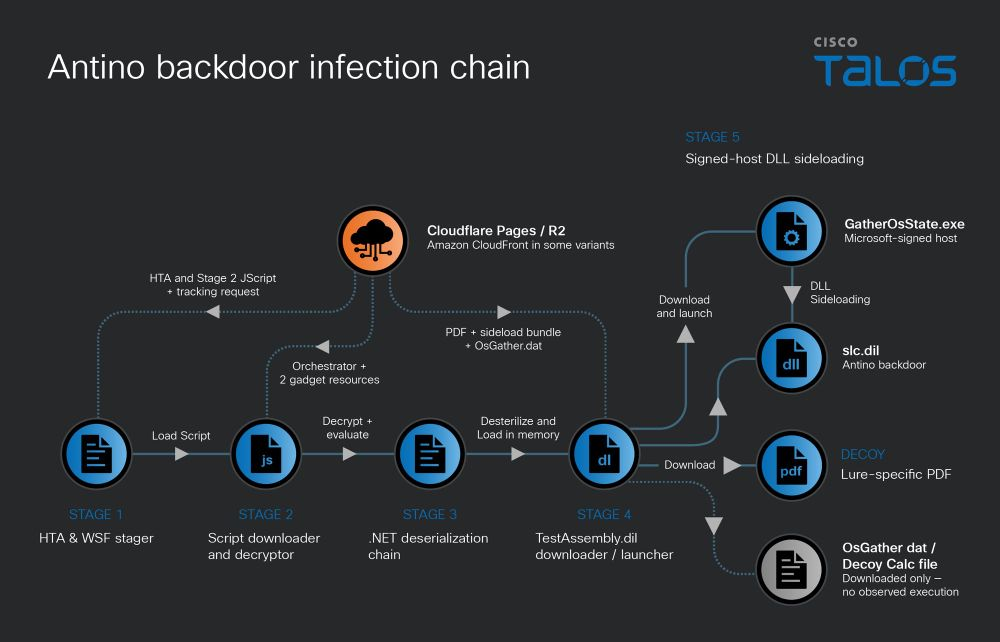
Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments. Cisco Talos has been tracking a cluster of espionage activity since September 2025 that it calls UAT-11587, and by July 2026 the group had hit at least 16 government and policy organizations across eight […]
 Pierluigi Paganini
September 25, 2026
Bitget says suspected North Korea-linked actors stole $351.6M from hot and warm wallets. Withdrawals were suspended while Mandiant investigates. Cryptocurrency exchange Bitget says suspected North Korea-linked threat actors stole $351.6 million from a limited number of hot and warm wallets. The company detected unauthorized transfers on September 24 and temporarily suspended withdrawals. Bitget said customer […]
 Pierluigi Paganini
September 17, 2026
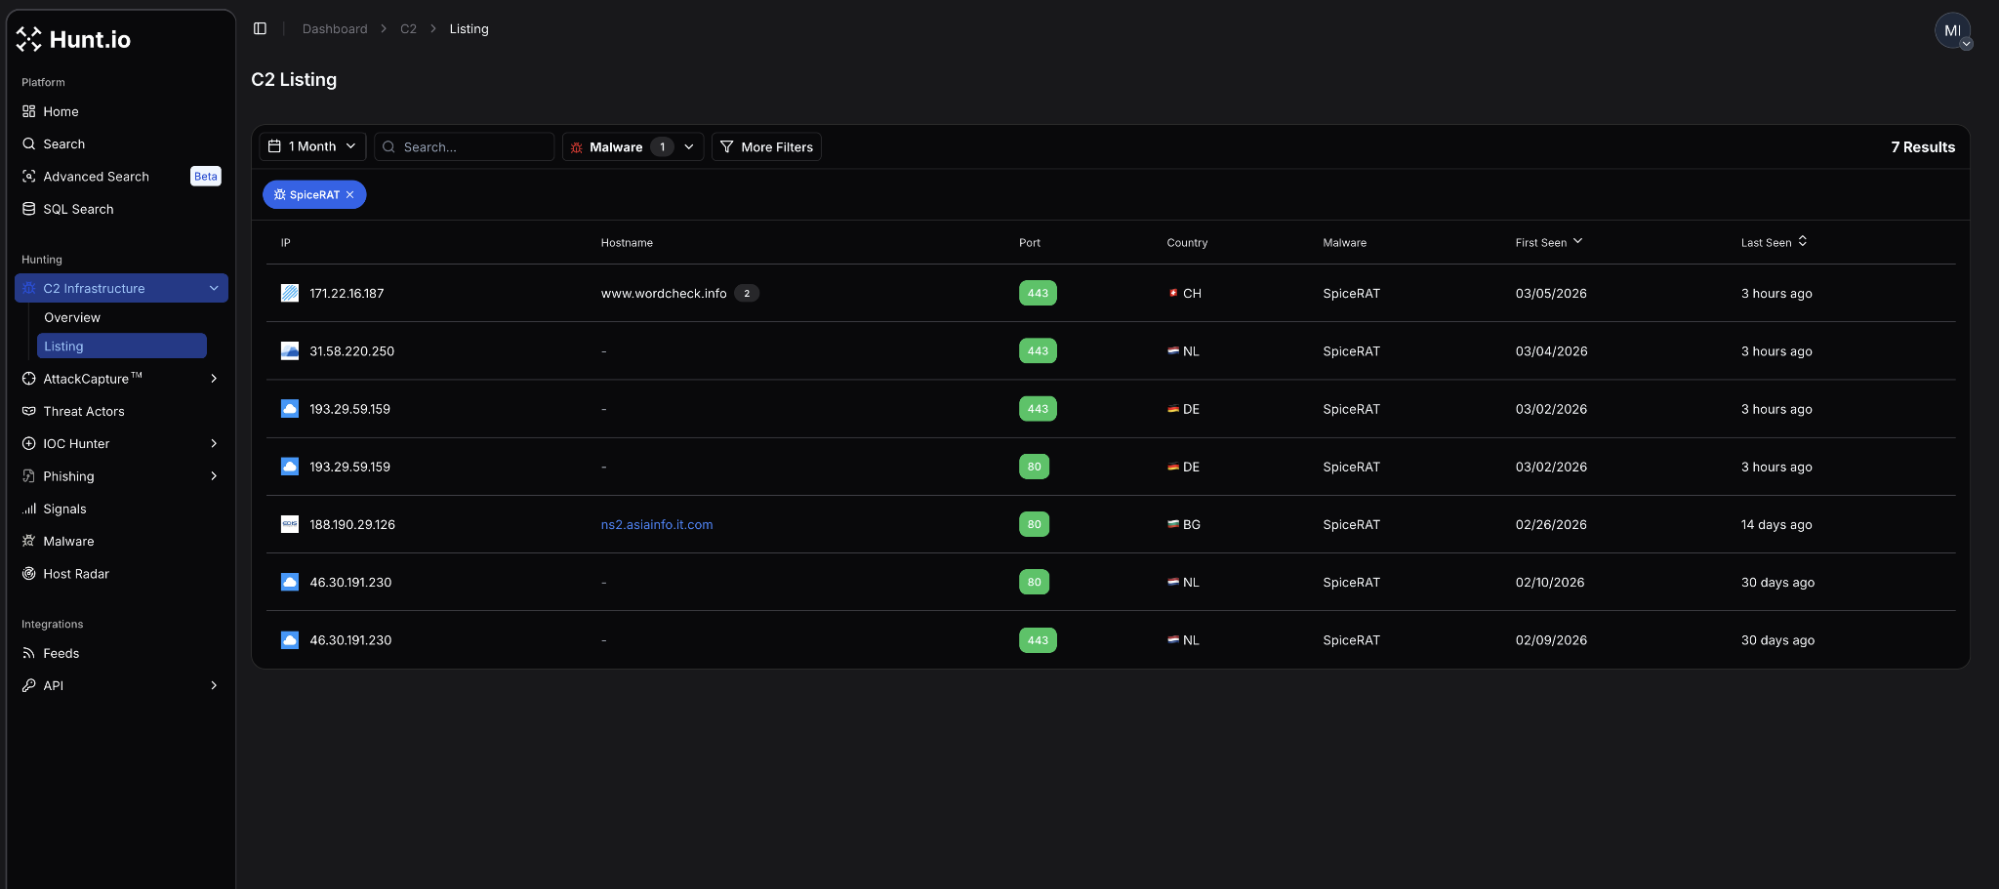
Hunt.io links SpiceRAT, NodeEdgeRAT and NomadRAT to a four-year SilkParasite campaign targeting governments and critical sectors in Central Asia. Hunt.io and researcher Guy Yasur have traced a tight cluster of SpiceRAT command‑and‑control servers that predate and extend Bitdefender’s August 2026 SilkParasite report. The work doesn’t dissect malware samples; it maps the network side of the […]