 Pierluigi Paganini
 September 02, 2026
Mirage Kitten used fake LinkedIn coding tests to spread NodeRabbit and PollCat, even banning AI tools that could have spotted the malware. Iran-linked Mirage Kitten hackers just found a genuinely clever way to make their own malware harder to detect: telling job candidates not to use AI tools while reviewing the trojanized code they were […]
 Pierluigi Paganini
September 01, 2026
Huntress found five DPRK-linked workers hired in 2026 using fake identities, remote-access setups and proxy tools to infiltrate legitimate companies. Companies keep accidentally hiring North Korea-linked individuals as remote workers, and Huntress just published the receipts. The security firm’s investigation documents five confirmed cases in 2026 alone where DPRK-aligned workers, tracked under the name FAMOUS […]
 Pierluigi Paganini
August 31, 2026
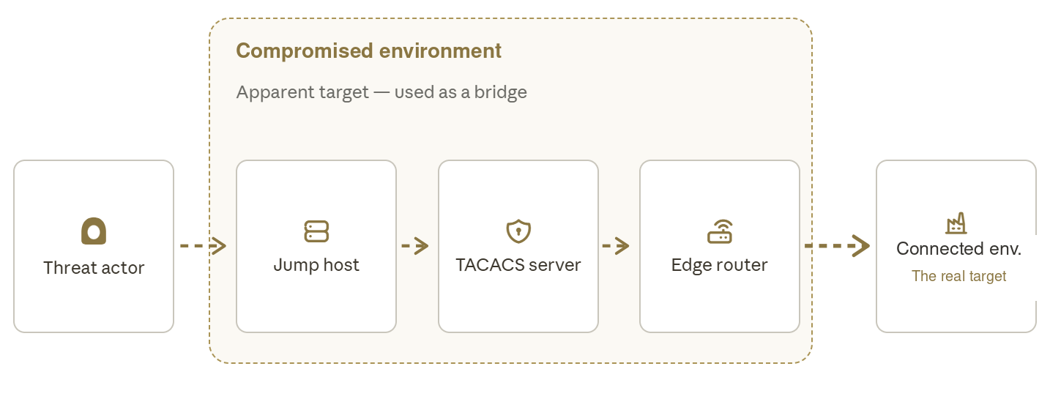
Fire Ant hijacked Cisco routers, stole credentials and altered logs to hide its tracks, using trusted infrastructure to reach high-value networks. Chinese-linked cyber espionage group Fire Ant has spent the past year quietly graduating from hacking individual computers to hacking the infrastructure that connects them. Sygnia’s new report traces how the group expanded from compromising […]
 Pierluigi Paganini
August 29, 2026
An alleged Chinese-speaking actor breached Philippine nuclear and naval targets by exploiting known flaws, stealing sensitive data. A suspected Chinese-speaking operator targeted a Philippine nuclear research body and a marine engineering company that supports the Philippine Navy, using well-known vulnerabilities in internet-facing ownCloud and WordPress systems. The activity was uncovered after Hunt.io found an exposed […]
 Pierluigi Paganini
August 28, 2026
BlueDelta (APT28) uses webhook.site and Microsoft Edge to hide HOOKEDGE espionage traffic targeting European governments. Recorded Future’s Insikt Group documented a campaign by BlueDelta, the Russian GRU-linked group that overlaps with the group APT28, running an entire espionage operation against European government targets using webhook.site, a service built for developers to test HTTP requests, as […]
 Pierluigi Paganini
August 27, 2026
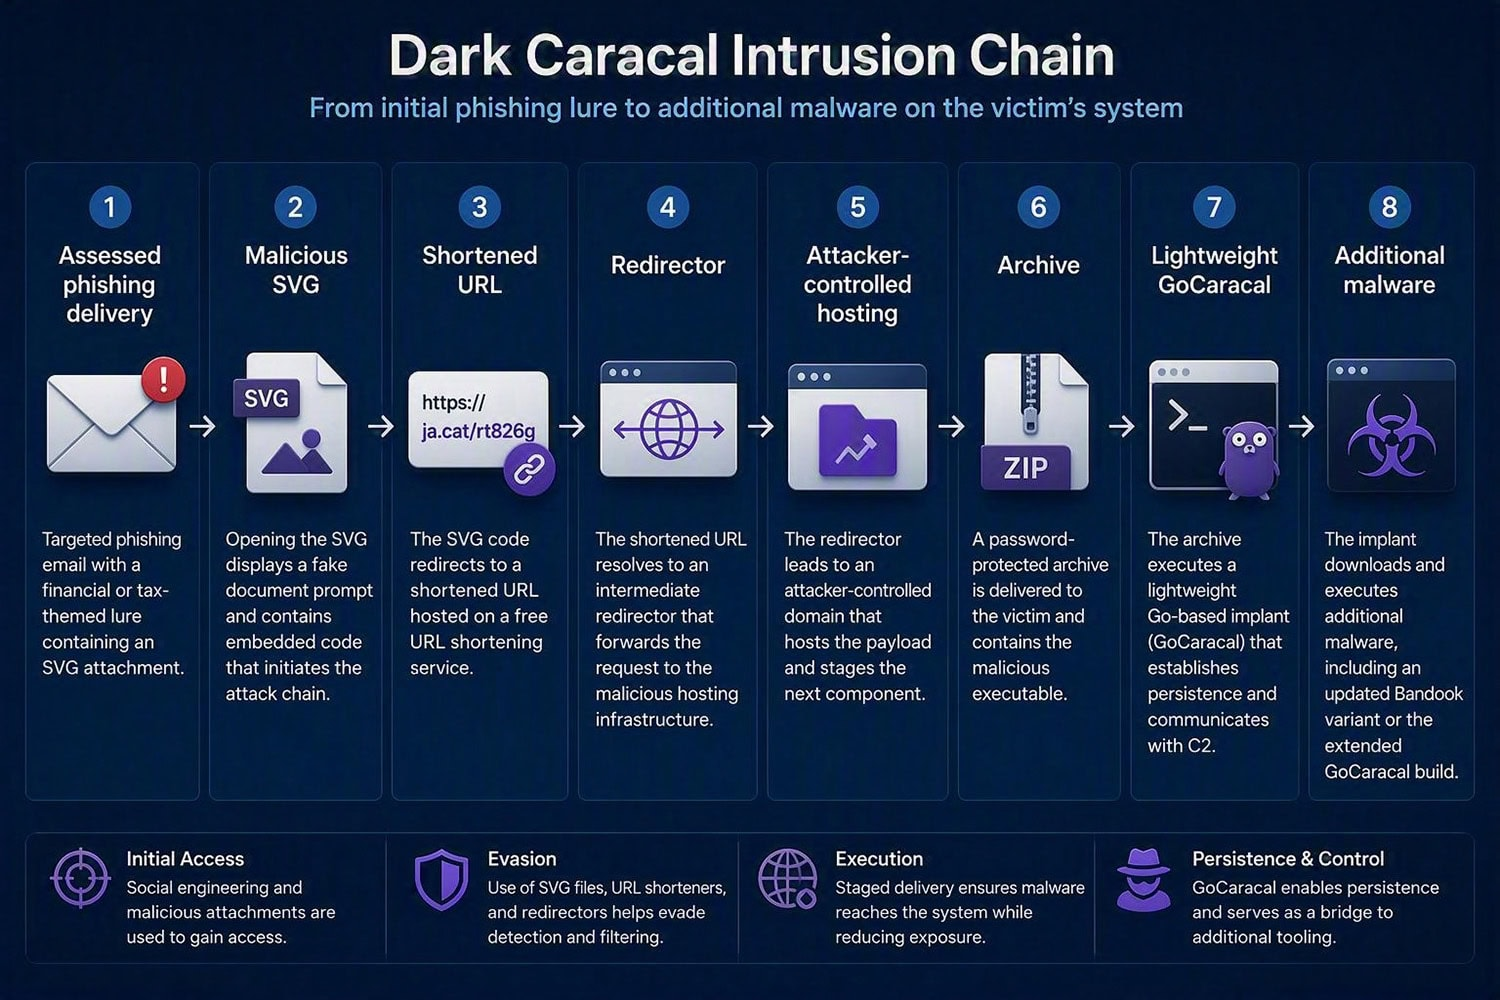
Dark Caracal targets Venezuela with GoCaracal, an upgraded Bandook toolkit and an Ethereum fallback for resilient C2 communications. Dark Caracal is back with new malware and the same hunting grounds. Arctic Wolf Labs researchers link a June 2026 intrusion against a communications organisation in Venezuela to the Lebanon‑linked espionage group, and says it deployed a […]
 Pierluigi Paganini
August 26, 2026
FBI seizes QScan and QTRouter, China-linked platforms used to hide intrusions and target U.S. critical infrastructure. The U.S. Department of Justice and the FBI have seized two platforms, QScan and QTRouter, used by a China-linked group to hide cyberattacks and target critical infrastructure. The operation matters because it shows how state-backed actors no longer need […]
 Pierluigi Paganini
August 23, 2026
Iran-linked hackers shut down a UK power plant for four days in the first confirmed attack of its kind, concurrent with water infrastructure attacks across 12 US states. Iran-linked hackers shut down a British power plant for four days in what The Telegraph describes as the most successful cyberattack of its kind against UK energy […]
 Pierluigi Paganini
August 21, 2026
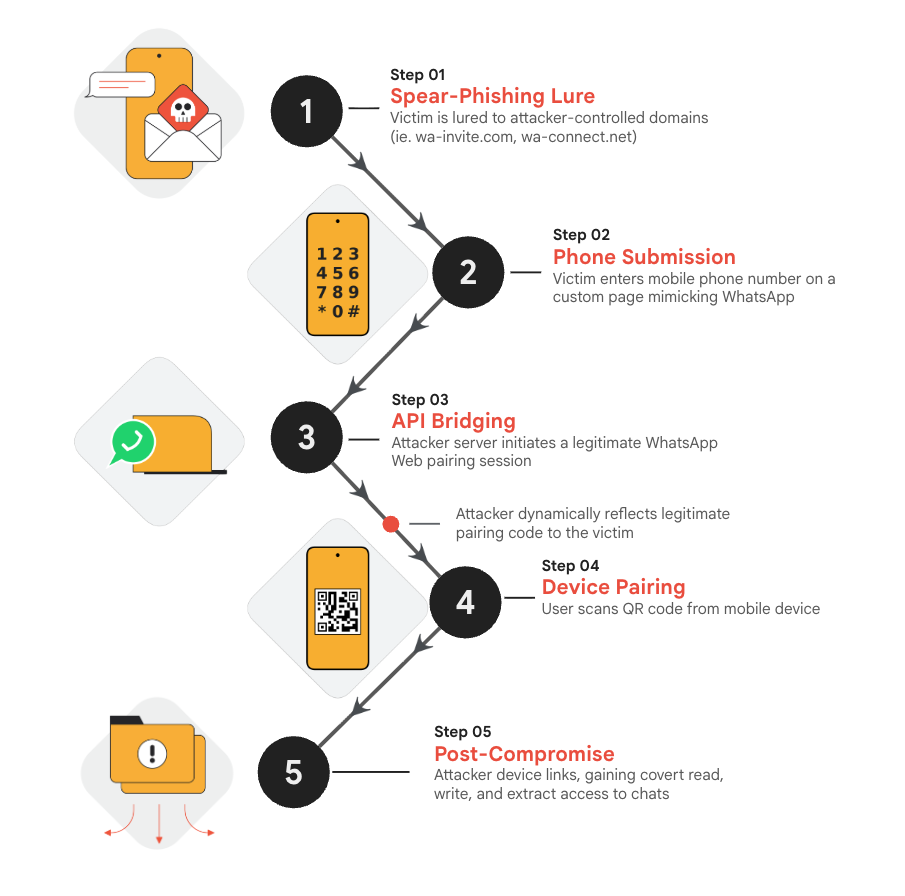
Google tracks three Russia-linked espionage clusters using phishing and legitimate authentication tools to target researchers, diplomats and defense staff. Google’s Threat Intelligence Group tracked three separate suspected Russia-linked cyber espionage clusters. All three focus on the same thing: abusing authentication features that are supposed to protect accounts to access them instead. Threat actors target researchers, […]
 Pierluigi Paganini
August 16, 2026
Mustang Panda upgraded CoolClient with a signed kernel driver that hides processes, files and network activity, making the backdoor harder to detect. HoneyMyte, also known as Mustang Panda, has pushed its CoolClient backdoor another step deeper into Windows. Kaspersky’s latest analysis shows a new variant that can deploy a signed kernel-mode driver as a Windows […]
Artificial Intelligence / November 21, 2026

Security / November 20, 2026