 Pierluigi Paganini
 August 27, 2026
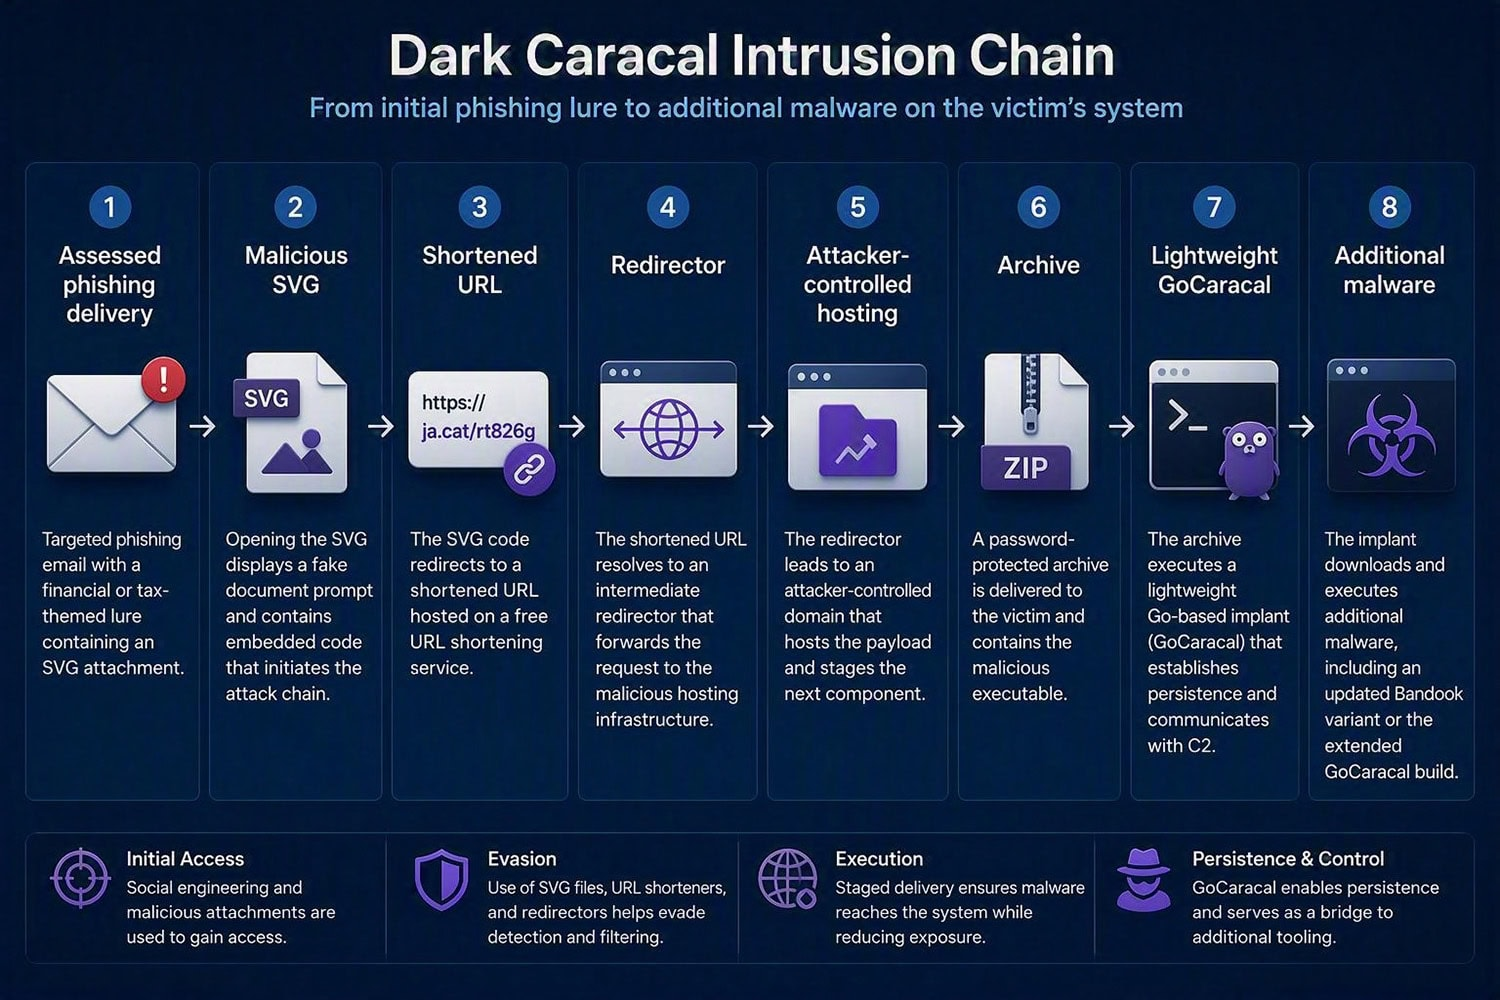
Dark Caracal targets Venezuela with GoCaracal, an upgraded Bandook toolkit and an Ethereum fallback for resilient C2 communications. Dark Caracal is back with new malware and the same hunting grounds. Arctic Wolf Labs researchers link a June 2026 intrusion against a communications organisation in Venezuela to the Lebanon‑linked espionage group, and says it deployed a […]
 Pierluigi Paganini
August 26, 2026
FBI seizes QScan and QTRouter, China-linked platforms used to hide intrusions and target U.S. critical infrastructure. The U.S. Department of Justice and the FBI have seized two platforms, QScan and QTRouter, used by a China-linked group to hide cyberattacks and target critical infrastructure. The operation matters because it shows how state-backed actors no longer need […]
 Pierluigi Paganini
August 23, 2026
Iran-linked hackers shut down a UK power plant for four days in the first confirmed attack of its kind, concurrent with water infrastructure attacks across 12 US states. Iran-linked hackers shut down a British power plant for four days in what The Telegraph describes as the most successful cyberattack of its kind against UK energy […]
 Pierluigi Paganini
August 21, 2026
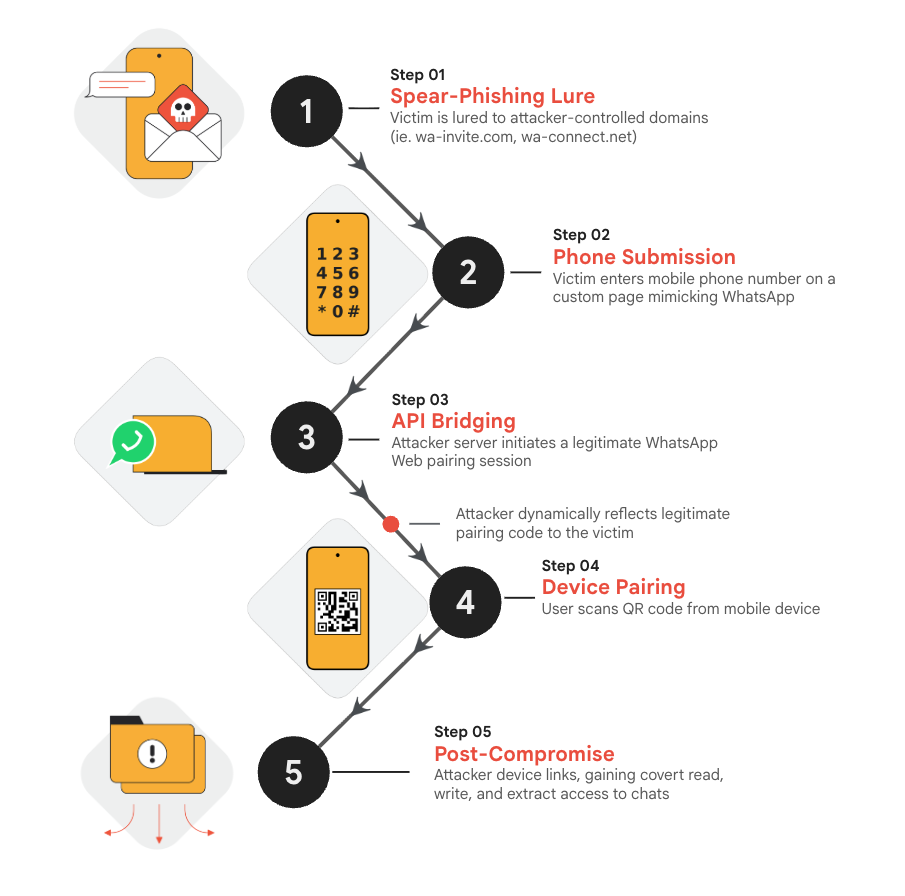
Google tracks three Russia-linked espionage clusters using phishing and legitimate authentication tools to target researchers, diplomats and defense staff. Google’s Threat Intelligence Group tracked three separate suspected Russia-linked cyber espionage clusters. All three focus on the same thing: abusing authentication features that are supposed to protect accounts to access them instead. Threat actors target researchers, […]
 Pierluigi Paganini
August 16, 2026
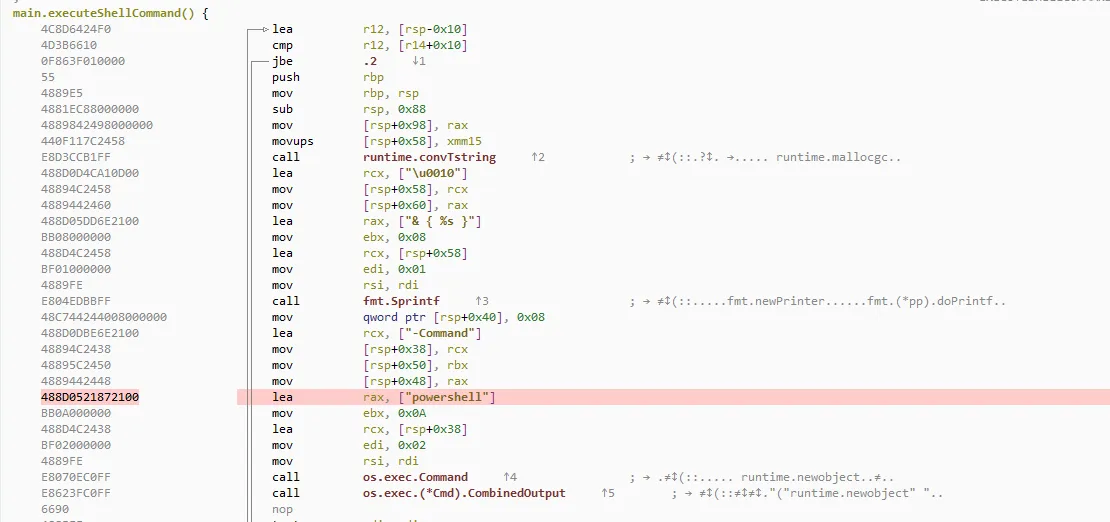
Mustang Panda upgraded CoolClient with a signed kernel driver that hides processes, files and network activity, making the backdoor harder to detect. HoneyMyte, also known as Mustang Panda, has pushed its CoolClient backdoor another step deeper into Windows. Kaspersky’s latest analysis shows a new variant that can deploy a signed kernel-mode driver as a Windows […]
 Pierluigi Paganini
August 16, 2026
Acronis uncovered PATCHCORD, a stealthy backdoor targeting Afghan telecom and South Asian infrastructure via fake VPN tools and Google Sheets C2. Researchers at Acronis just documented an espionage operation that reads like it was built by someone with genuinely good taste in disguises. Their Threat Research Unit report tracks a previously undocumented backdoor called PATCHCORD, […]
Pierluigi Paganini
August 12, 2026
China-linked hackers reportedly used eight AI agents to breach a government network, steal data and compromise accounts with minimal human oversight. Israeli cybersecurity firm Dream documented what looks like the first fully autonomous, end-to-end AI hacking operation against a government target. Over four days at the start of July, according to the Financial Times, suspected […]
 Pierluigi Paganini
August 02, 2026
After attacks hit 30+ Minnesota water systems, CISA urged utilities to remove internet-exposed PLCs and strengthen OT security. Between Sunday and Monday, July 26 and 27, a coordinated cyberattack hit operational technology (OT) systems at more than 30 community water utilities across the state, according to Minnesota IT Services (MNIT). “A coordinated cyberattack targeted operational technology […]
 Pierluigi Paganini
August 01, 2026
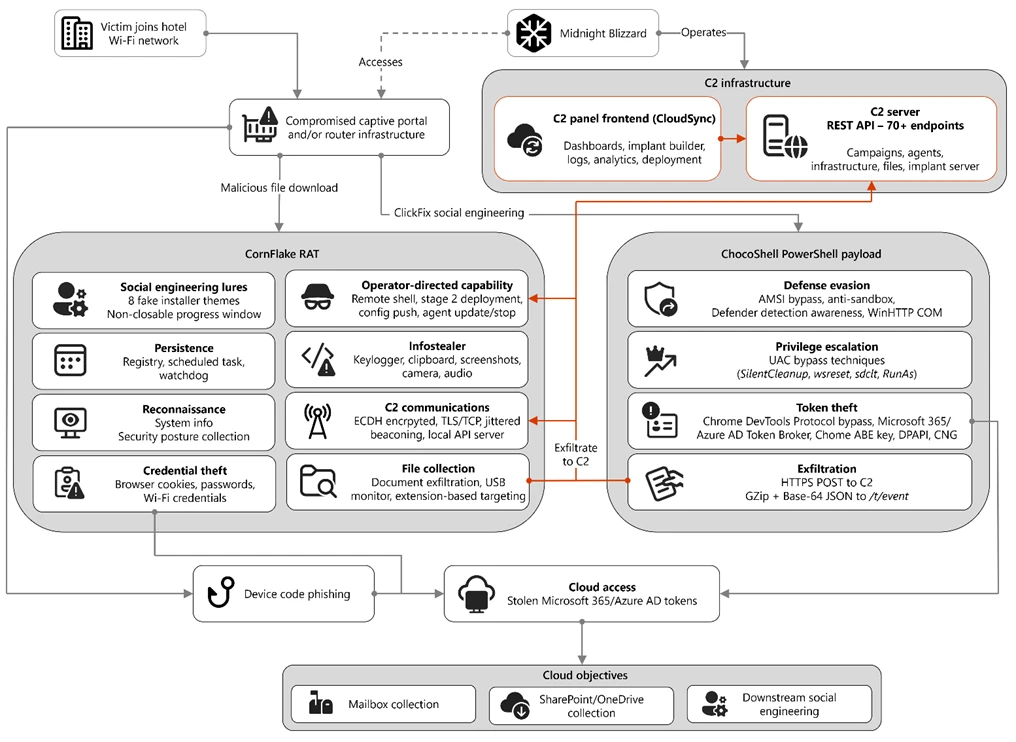
Microsoft says Russian hackers hijacked hotel Wi-Fi portals to spread malware and steal Microsoft 365 tokens from travelers. Microsoft Threat Intelligence disclosed CaptiveCrunch, a campaign it attributes to Storm-2945, an operational sub-cluster of Midnight Blizzard, the Russian SVR-linked group also known as APT29 and Cozy Bear. Since early May 2026, Storm-2945 has been manipulating DNS […]
 Pierluigi Paganini
July 31, 2026
South Korea warned that nation-state actors are using phishing and compromised websites to silently infect citizens and businesses. South Korea agencies (The National Intelligence Service, the National Police Agency, the Korea Internet & Security Agency, and the Financial Security Institute) jointly published an advisory warning that a state-backed hacking group is actively targeting South Korean […]
Uncategorized / September 21, 2026
Security / September 20, 2026