


 Pierluigi Paganini
 August 16, 2026
Large DDoS attacks disrupted Threema, causing severe communication outages. Threema On-Prem users were unaffected by the attacks. Threema suffered multiple large-scale DDoS attacks that disrupted its secure messaging service and caused severe communication issues. Organizations using Threema On-Prem were not affected, as their deployments run on their own infrastructure. Threema is a Swiss paid secure […]
 Pierluigi Paganini
August 16, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Kimsuky Integrates AI into Attack Operations, From AI-Generated Decoy Documents to a Local LLM ShieldBreak – August 2026 disclosure Kimwolf v7: An Evolution of the Kimwolf Botnet CISA, FBI and Partners Warn Organizations of […]
 Pierluigi Paganini
August 16, 2026
Mustang Panda upgraded CoolClient with a signed kernel driver that hides processes, files and network activity, making the backdoor harder to detect. HoneyMyte, also known as Mustang Panda, has pushed its CoolClient backdoor another step deeper into Windows. Kaspersky’s latest analysis shows a new variant that can deploy a signed kernel-mode driver as a Windows […]
 Pierluigi Paganini
August 16, 2026
France’s tax agency says hackers stole data on 678,000 taxpayers, including income and tax details, in a sophisticated cyberattack. A threat actor claimed to have breached France’s tax agency in late June. France’s tax administration confirmed that a cyberattack exposed personal data of 678,000 individuals and businesses, prompting an immediate criminal investigation. The cybercrime unit […]
 Pierluigi Paganini
August 16, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Crooks Are Buying Your Expired Domains and Using Them to Deliver Malware SAP Commerce Cloud CVE-2026-58231 Exploited […]
 Pierluigi Paganini
August 16, 2026
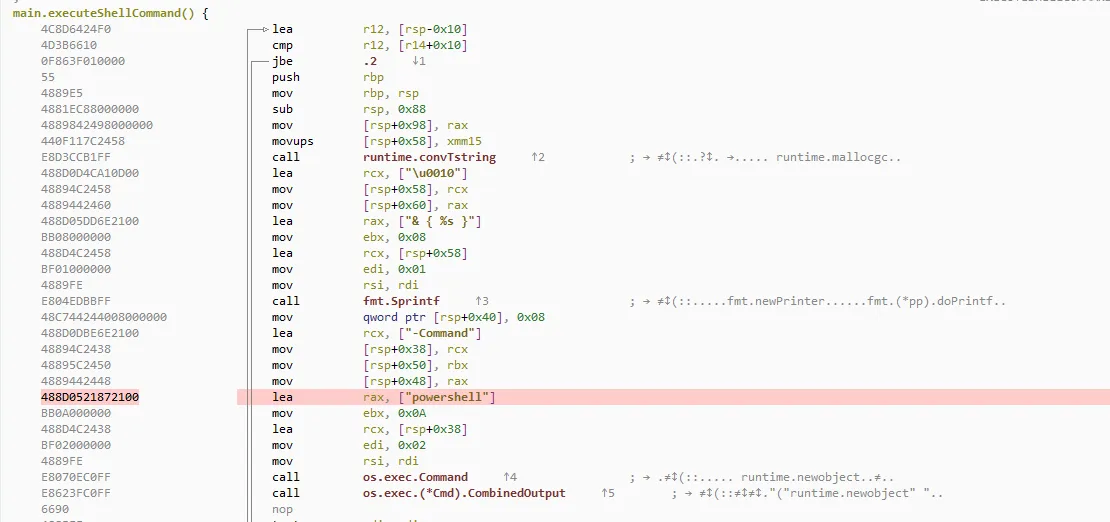
Acronis uncovered PATCHCORD, a stealthy backdoor targeting Afghan telecom and South Asian infrastructure via fake VPN tools and Google Sheets C2. Researchers at Acronis just documented an espionage operation that reads like it was built by someone with genuinely good taste in disguises. Their Threat Research Unit report tracks a previously undocumented backdoor called PATCHCORD, […]
 Pierluigi Paganini
August 15, 2026
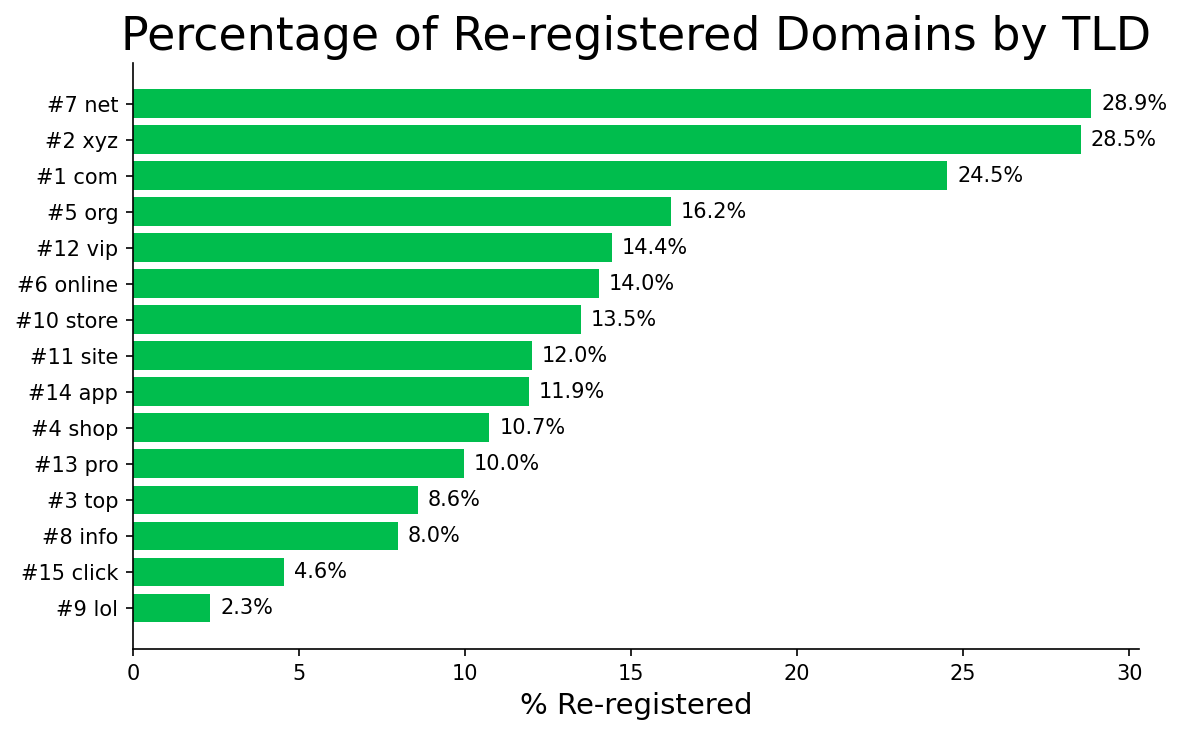
Attackers are buying expired domains to exploit their reputation, traffic and DNS history, using them for malware delivery, scams and C2 infrastructure. Every day, roughly 65,000 domain names that once belonged to someone else get re-registered by a new owner. Infoblox Threat Intel calls these dropcatch domains, and in the first half of 2026 they […]
 Pierluigi Paganini
August 15, 2026
Attackers are actively exploiting a maximum severity SAP Commerce Cloud vulnerability, tracked as CVE-2026-58231, just days after SAP released a patch. A critical SAP Commerce Cloud vulnerability, tracked as CVE-2026-58231 (CVSS score of 10.0), is under active exploitation just days after SAP released a patch. The flaw stems from insufficient authorization checks and input validation. […]
 Pierluigi Paganini
August 15, 2026
GeoServer faces an unpatched zero-day enabling SQL injection and potentially RCE, with attackers already probing exposed systems. A newly disclosed GeoServer zero-day is already attracting active exploitation attempts, and there is no patch available yet. Organisations running the open-source geospatial platform should check their exposure. A security researcher with the handler q1uf3ng discloded the vulnerability […]
 Pierluigi Paganini
August 14, 2026
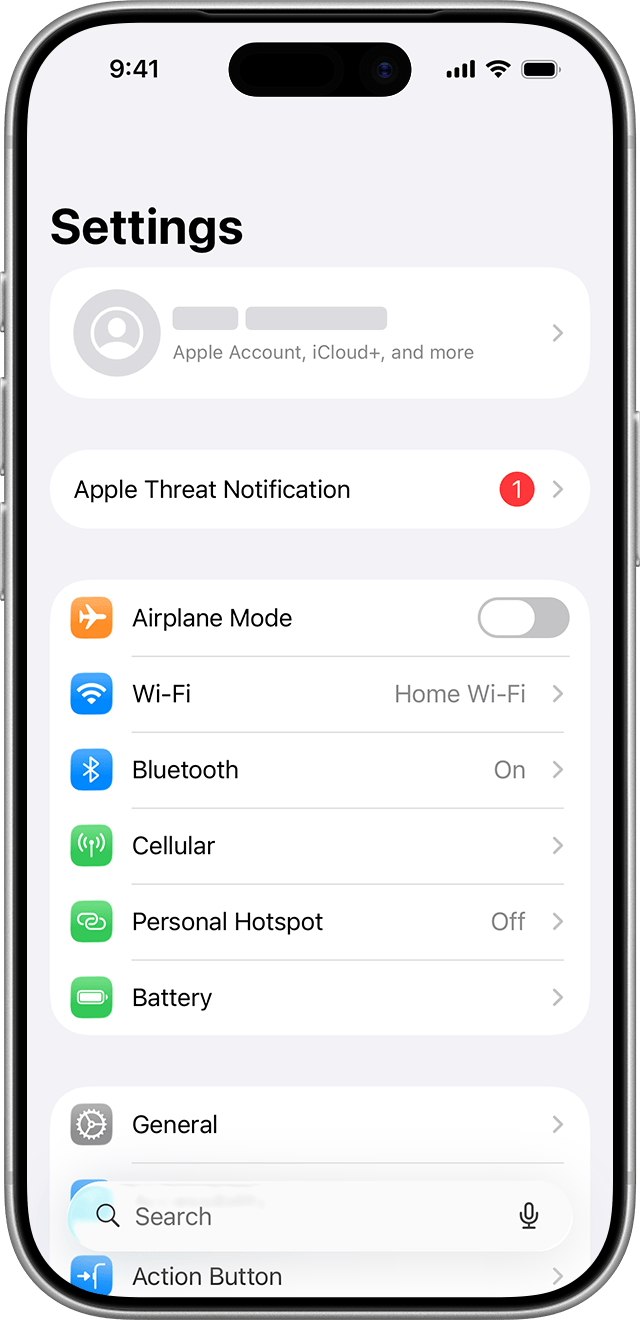
Apple warns users of credible, targeted attacks and urges immediate verification, stronger protections, and expert assistance. Apple has sent a new round of threat notifications to users it believes may have been singled out by mercenary spyware. The company told TechCrunch the latest alerts reached people in 110 countries, adding to notifications it has already […]



Artificial Intelligence / September 14, 2026


