



 Pierluigi Paganini
 August 26, 2026
CISA red teams fully compromised two critical infrastructure orgs. One SOC isolated hosts in minutes; the other never detected the breach. CISA published an advisory (AA26-237A) documenting two simultaneous red team assessments at critical infrastructure organizations. Both organizations lost full domain control and had their cloud environments compromised. One of them didn’t know until CISA […]
 Pierluigi Paganini
August 26, 2026
FBI seizes QScan and QTRouter, China-linked platforms used to hide intrusions and target U.S. critical infrastructure. The U.S. Department of Justice and the FBI have seized two platforms, QScan and QTRouter, used by a China-linked group to hide cyberattacks and target critical infrastructure. The operation matters because it shows how state-backed actors no longer need […]
Pierluigi Paganini
August 26, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Gitea flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Oracle HTTP Server and Oracle Weblogic Server Proxy Plug-in flaw, tracked as CVE-2026-60004 (CVSS score of 9,8), to its Known Exploited Vulnerabilities (KEV) catalog. Gitea is an open-source platform for […]
 Pierluigi Paganini
August 26, 2026
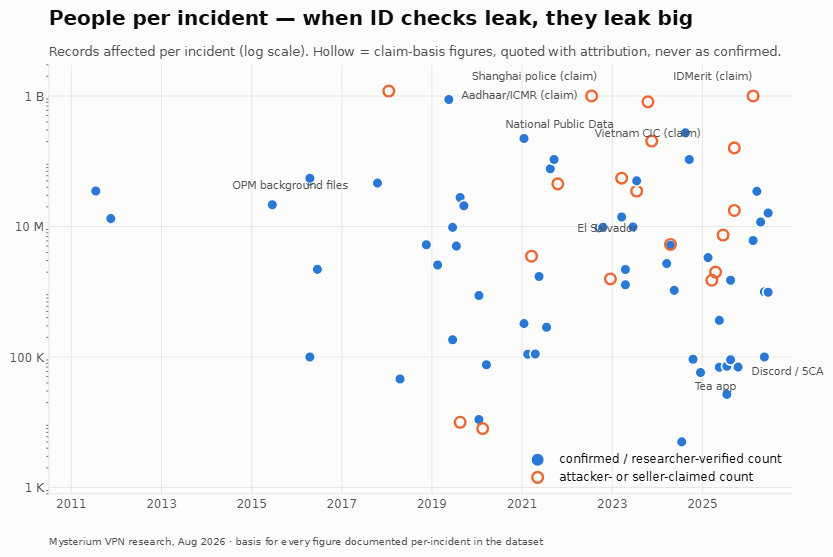
88 ID-verification breaches exposed billions of records, highlighting the growing risks of collecting sensitive identity and biometric data. A new report from Mysterium VPN compiles 88 documented incidents since 2011 where data collected specifically to verify someone’s identity or age got breached, exposed, or sold. The confirmed and researcher-verified total sits at 2.15 billion records, […]
 Pierluigi Paganini
August 25, 2026
Norway ’s shared government infrastructure suffered a third DDoS attack, disrupting digital services but showing no signs of data compromise. Norway ‘s shared digital government infrastructure has been hit by another distributed denial-of-service (DDoS) attack that disrupted services used by citizens, businesses and public agencies. The incident began at 03:38 CEST on Monday, August 24, […]
 Pierluigi Paganini
August 25, 2026
Two CVSS 9.8 miniOrange SAML WordPress plugin auth bypasses were exploited while paid editions never appeared in any vulnerability database. Manual patch required. Two critical authentication bypass vulnerabilities in the miniOrange SAML 2.0 Single Sign On WordPress plugin, both rated CVSS 9.8, are under active exploitation. Both CVE-2026-61979 and CVE-2026-15981 allow an unauthenticated attacker to […]
Pierluigi Paganini
August 25, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Oracle flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Oracle HTTP Server and Oracle Weblogic Server Proxy Plug-in flaw, tracked as CVE-2026-21962 (CVSS score of 10,0), to its Known Exploited Vulnerabilities (KEV) catalog. CVE-2026-21962 is a critical, unauthenticated vulnerability […]
 Pierluigi Paganini
August 24, 2026
A fake 113GB GTA VI build is packed with malware, using massive empty files to hide a tiny malicious payload. GTA VI hype has reached the point where people are volunteering to infect their own computers just to check if a leak is real. Someone on X asked their followers to “take one for the […]
 Pierluigi Paganini
August 24, 2026
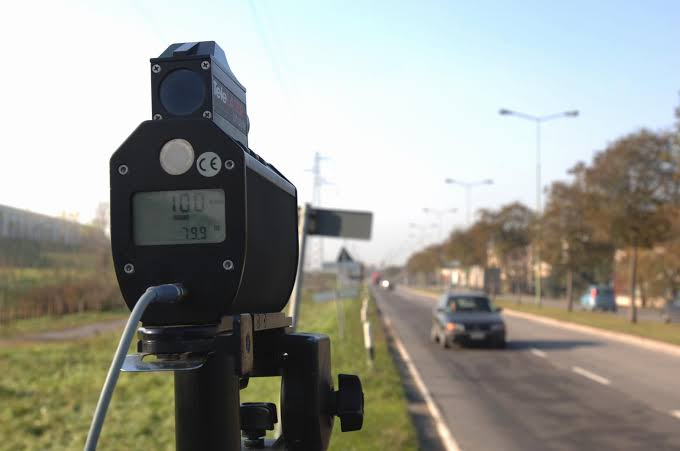
Slovakia warns that vulnerable speed cameras could expose vehicle data, enable remote access and provide attackers with a foothold into public networks. Slovakia’s National Security Authority, NBÚ, recently issued a warning about several road speed cameras, calling them a significant cyber threat. The alert is not about someone deleting a speeding ticket. It is about […]
 Pierluigi Paganini
August 23, 2026
Iran-linked hackers shut down a UK power plant for four days in the first confirmed attack of its kind, concurrent with water infrastructure attacks across 12 US states. Iran-linked hackers shut down a British power plant for four days in what The Telegraph describes as the most successful cyberattack of its kind against UK energy […]






