


 Pierluigi Paganini
 August 30, 2026
Extortion group FulcrumSec claims they stole 86GB of Manchester Airports Group data after finding API credentials exposed in client-side JavaScript. Manchester Airports Group (MAG) disclosed a data breach on August 27 affecting customers of Manchester, London Stansted, and East Midlands airports. Two days later, BleepingComputer reports the extortion group FulcrumSec claimed responsibility, saying it stole […]
 Pierluigi Paganini
August 30, 2026
PaperCut servers are under active attack, while 47% of tracked installations still run unpatched versions vulnerable to remote code execution. PaperCut, the print management software running in schools, hospitals, and offices worldwide, confirmed on August 27 that a pre-authentication remote code execution flaw is being actively exploited against real customers. Researchers at Huntress found evidence […]
 Pierluigi Paganini
August 29, 2026
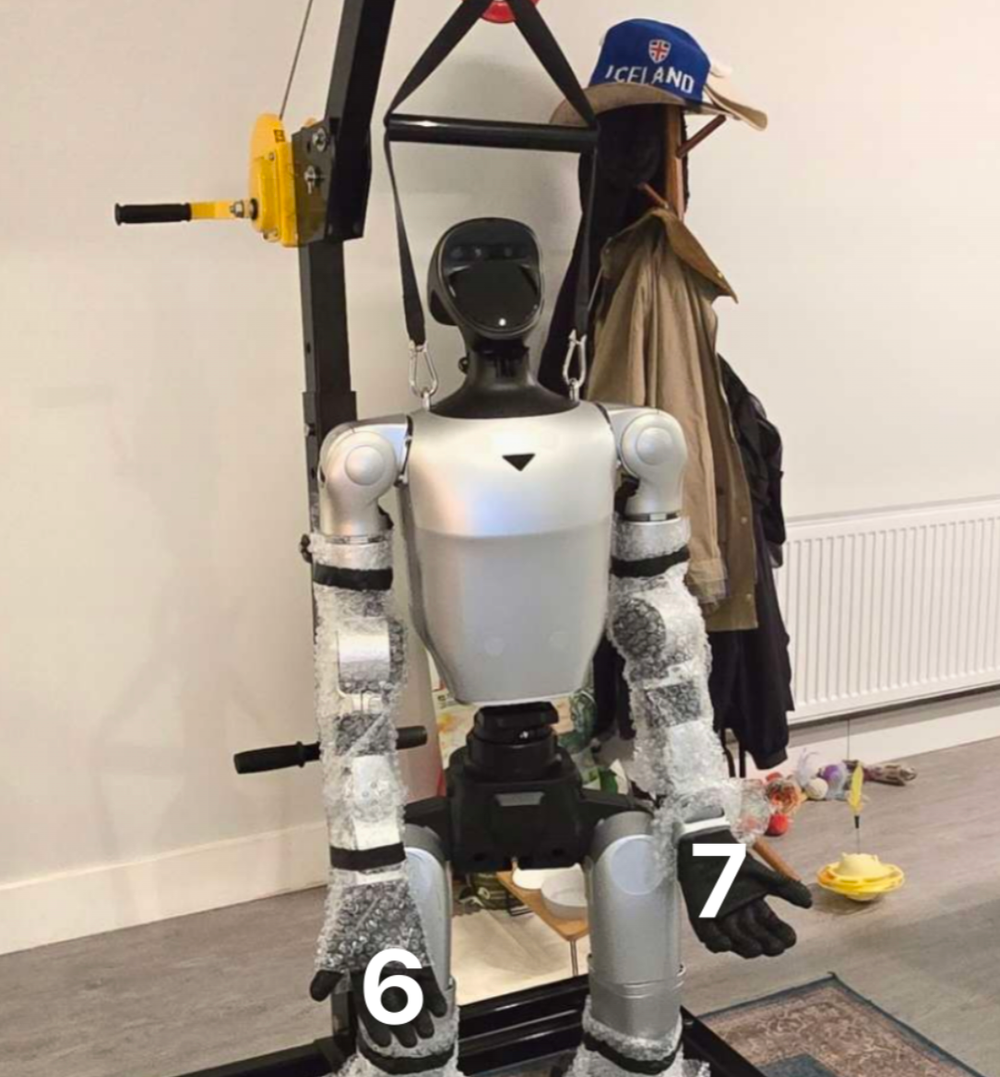
A researcher chained two Unitree G1 flaws to gain root access remotely and showed how a compromised robot could attack others nearby. Security researcher Olivier Laflamme spent about three months digging into the Unitree G1 humanoid robot and eventually found a way to fully compromise it without plugging in a single cable. In his technical […]
 Pierluigi Paganini
August 29, 2026
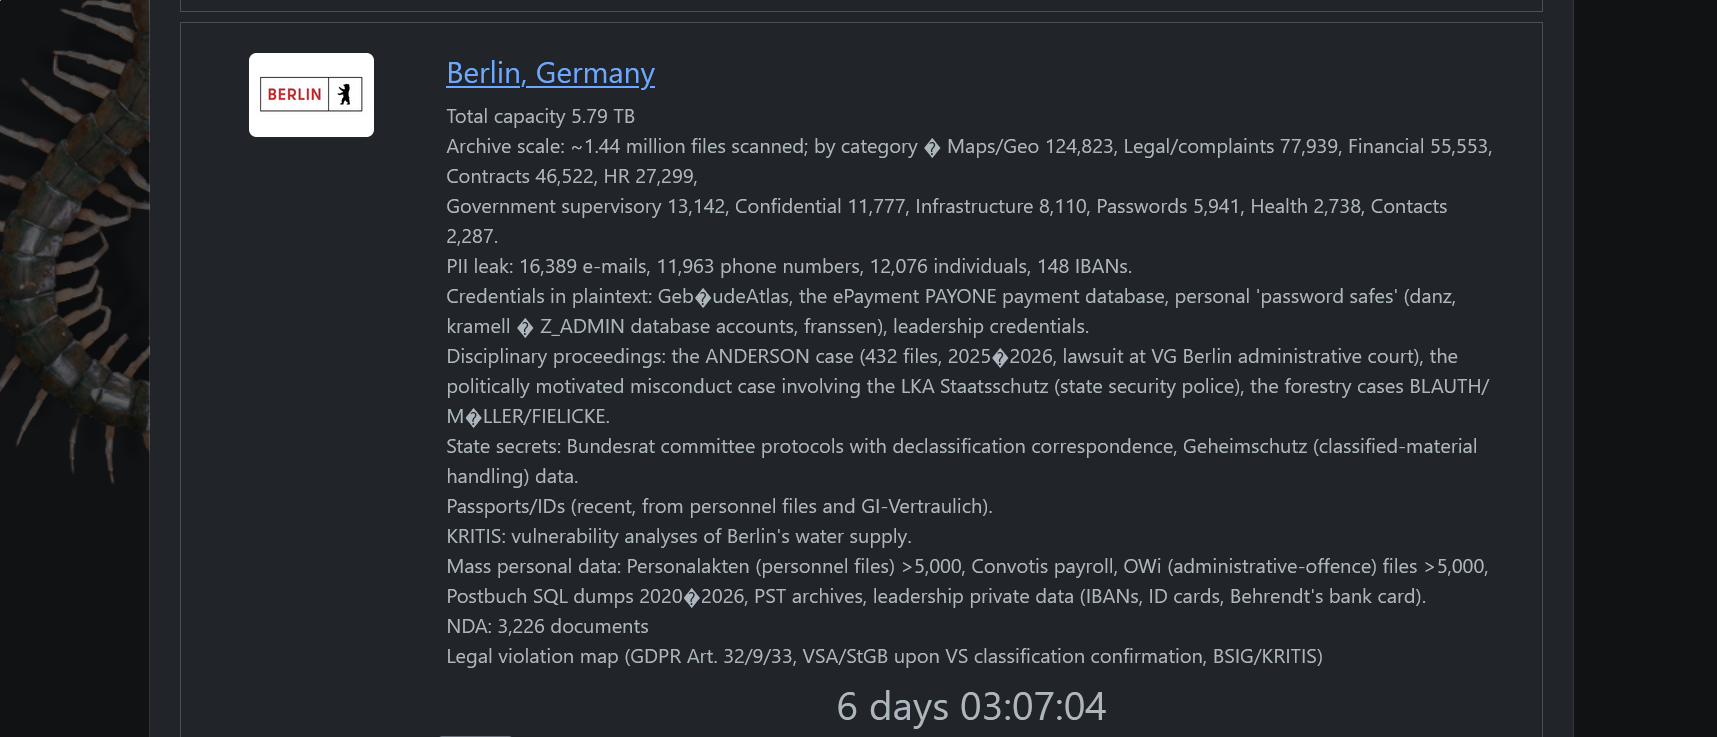
Berlin ‘s government faces a Rhysida ransomware attack weeks before elections, with officials refusing to pay despite a claimed 5.79 TB data theft. Berlin’s state government confirmed this week it’s dealing with an extortion attempt following an August cyberattack on the city-state’s administrative network, and officials have already refused the requested ransom. The ransomware group […]
 Pierluigi Paganini
August 29, 2026
An alleged Chinese-speaking actor breached Philippine nuclear and naval targets by exploiting known flaws, stealing sensitive data. A suspected Chinese-speaking operator targeted a Philippine nuclear research body and a marine engineering company that supports the Philippine Navy, using well-known vulnerabilities in internet-facing ownCloud and WordPress systems. The activity was uncovered after Hunt.io found an exposed […]
 Pierluigi Paganini
August 28, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds ownCloud, Linux Kernel, and JFrog Artifactory flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2023-49105 (CVSS score of 9.8) is an improper-authentication flaw in ownCloud Server’s WebDAV functionality. An unauthenticated attacker who […]
Pierluigi Paganini
August 28, 2026
PaperCut warns that a zero-day in NG and MF is being exploited. The company already release emergency patches to address it. PaperCut Software warns that attackers are actively exploiting a zero-day in its NG and MF print management products. The flaw has no CVE yet, and the company has not released technical details. PaperCut issued […]
Pierluigi Paganini
August 28, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Red Hat, Linux Kernel, Ajax.NET Professional, Microsoft SQL Server, and Citrix NetScaler flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2015-3246 is a race condition in Red Hat libuser that could let […]
 Pierluigi Paganini
August 28, 2026
A cyberattack on Manchester Airports Group exposed data of 8.7 million customers across Manchester, Stansted, and East Midlands airports. Manchester Airports Group disclosed that an unauthorised third party accessed customer data belonging to approximately 8.7 million people across three of England’s busiest airports: Manchester, London Stansted, and East Midlands. “Manchester, London Stansted and East Midlands […]
Pierluigi Paganini
August 27, 2026
CISA urges water utilities to find and secure internet-exposed PLCs after July attacks showed how easily exposed industrial systems can be compromised. Over 100 internet-exposed systems in the US water and wastewater sector got hit by cyberattacks in July 2026, and CISA’s response wasn’t just an incident report, it was a how-to guide for making […]






