 Pierluigi Paganini
 June 27, 2023
Researchers at Censys have identified hundreds of devices deployed within federal networks that have internet-exposed management interfaces. Researchers at Censys have analyzed the attack surfaces of more than 50 Federal Civilian Executive Branch (FCEB) organizations and sub-organizations and discovered more than 13,000 distinct hosts across 100 autonomous systems. The experts focused on roughly 1,300 of […]
 Pierluigi Paganini
June 27, 2023
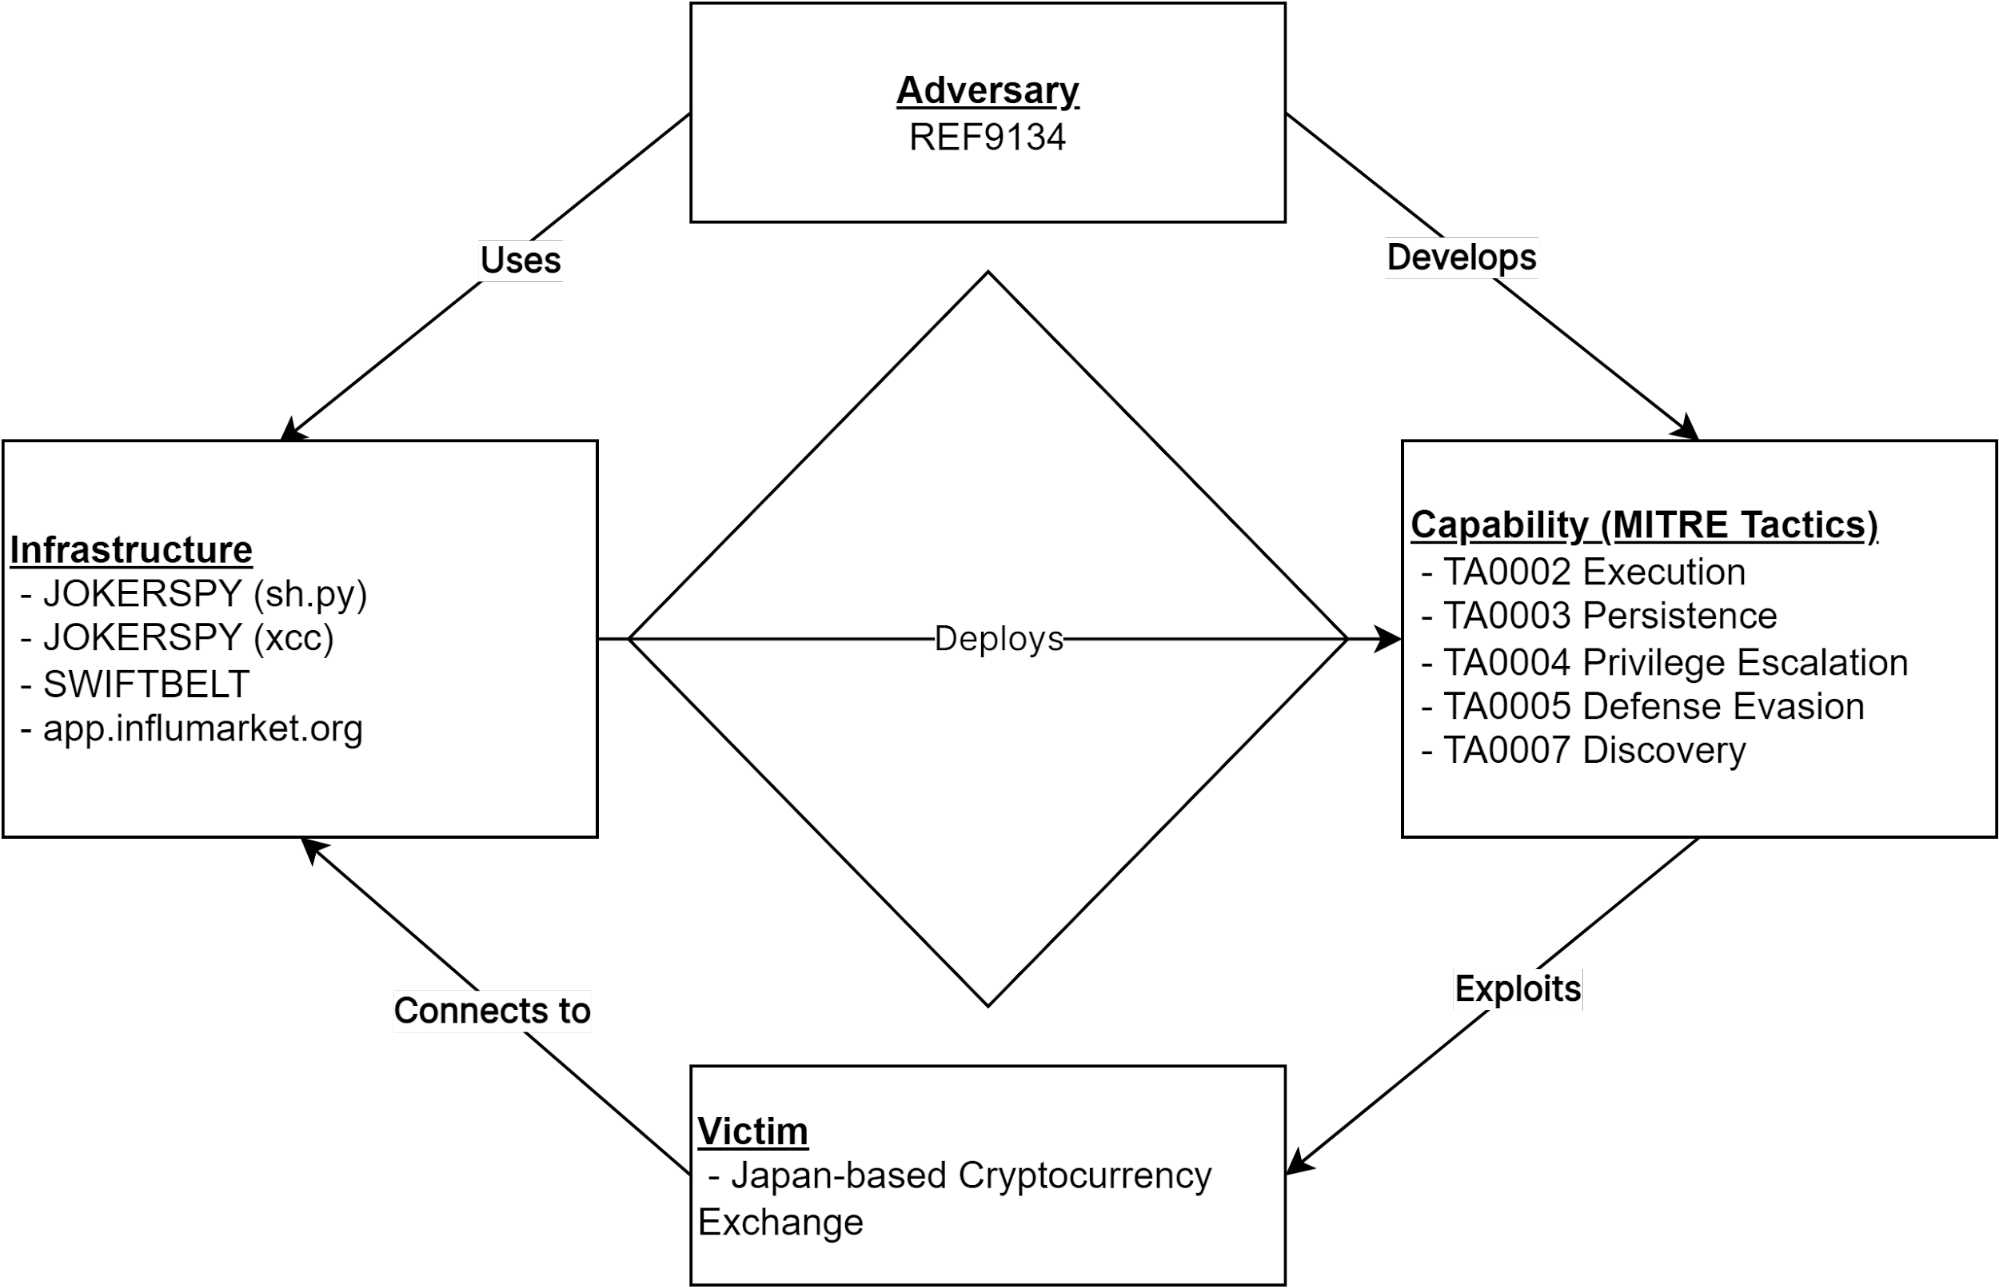
An unnamed Japanese cryptocurrency exchange was the victim of a cyber attack aimed at deploying an Apple macOS backdoor named JokerSpy. Elastic Security Labs researchers provided details about a recently discovered intrusion at an unnamed cryptocurrency exchange, aimed at deploying an Apple macOS backdoor named JokerSpy. The researchers tracked the intrusion as REF9134, the threat […]
 Pierluigi Paganini
June 26, 2023
The cyber attack suffered by Suncor Energy impacted payment operations at Petro-Canada gas stations in Canada. Suncor Energy is Canada’s leading integrated energy company that provides oil sands development, production and upgrading, offshore oil and gas, and petroleum refining in Canada and the U.S.. It owns the Petro-Canada retail and wholesale distribution networks. A cyber […]
 Pierluigi Paganini
June 26, 2023
The Internet Systems Consortium (ISC) addressed three denial-of-service (DoS) vulnerabilities in the DNS software suite BIND. The Internet Systems Consortium (ISC) released security updates to address three denial-of-service (DoS) vulnerabilities in the DNS software suite BIND. The three issues, tracked as CVE-2023-2828, CVE-2023-2829 and CVE-2023-2911, are remotely exploitable. ISC states that the three flaws, rated […]
 Pierluigi Paganini
June 26, 2023
China-linked APT group VANGUARD PANDA, aka Volt Typhoon, was spotted observing a novel tradecraft to gain initial access to target networks. CrowdStrike researchers observed the China-linked APT group VANGUARD PANDA, aka Volt Typhoon, using a novel tradecraft to gain initial access to target networks. The Volt Typhoon group has been active since at least mid-2021 […]
 Pierluigi Paganini
June 25, 2023
A U.K. citizen, who was involved in the attack on Twitter in 2020, was sentenced to five years in prison for cybercrime offenses. Joseph James O’Connor, aka PlugwalkJoe (24), the hacker who was involved in the attacks on Twitter in 2020, was sentenced to five years in prison for cybercrime offenses. On November 2021, the […]
 Pierluigi Paganini
June 23, 2023
U.S. Cybersecurity and Infrastructure Security Agency (CISA) added six new vulnerabilities to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added six new security flaws to its Known Exploited Vulnerabilities Catalog. Below is the list of the issues added to the catalog: According to Binding Operational Directive (BOD) 22-01: Reducing the […]
 Pierluigi Paganini
June 23, 2023
VMware addressed multiple memory corruption vulnerabilities in vCenter Server that can be exploited to achieve remote code execution. VMware released security updates to five memory corruption vulnerabilities (CVE-2023-20892, CVE-2023-20893, CVE-2023-20894, CVE-2023-20895, CVE-2023-20896) in vCenter Server that could lead to remote code execution. The memory corruption vulnerabilities reside in the software’s implementation of the DCERPC protocol. […]
 Pierluigi Paganini
June 23, 2023
Fortinet addressed a critical remote command execution vulnerability, tracked as CVE-2023-33299, affecting FortiNAC solution. FortiNAC is a network access control (NAC) solution designed by Fortinet that is used by organizations to secure and control access to networks by enforcing security policies, monitoring devices, and managing their access privileges. FortiNAC helps organizations protect their network infrastructure […]
 Pierluigi Paganini
June 23, 2023
Researchers reported that millions of GitHub repositories are likely vulnerable to an attack called RepoJacking. A study conducted by Aqua researchers revealed that millions of GitHub repositories are potentially vulnerable to RepoJacking. In the RepoJacking attack, attackers claim the old username of a repository after the legitimate creator changed the username, then publish a rogue repository […]