


 Pierluigi Paganini
 November 10, 2021
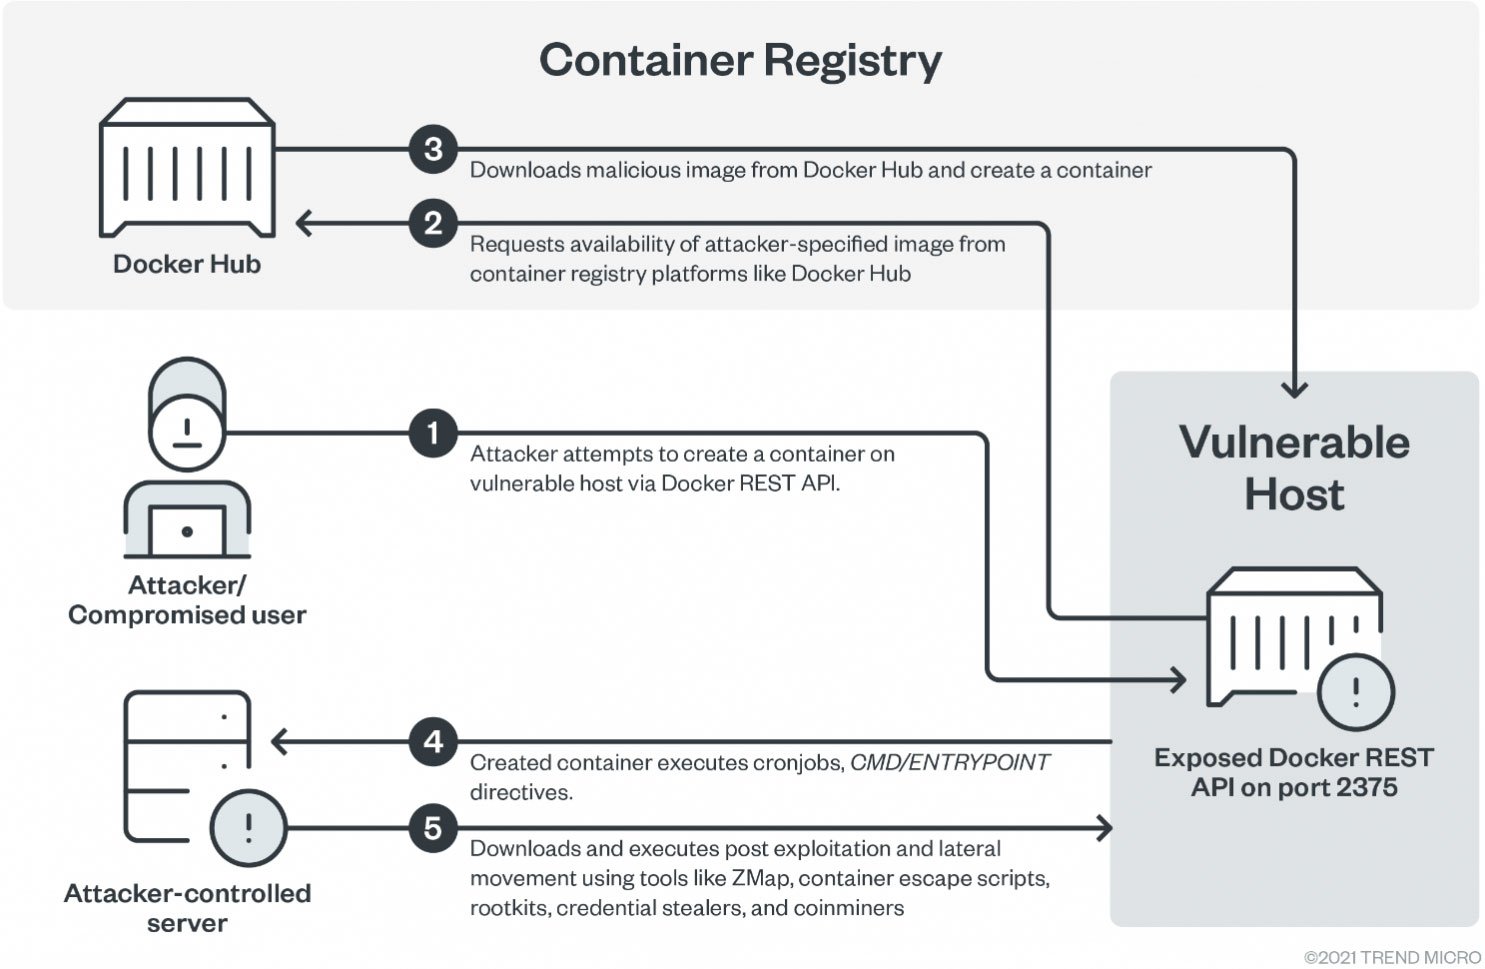
TeamTNT hackers are targeting poorly configured Docker servers as part of an ongoing campaign that started in October. Trend Micro researchers reported that TeamTNT hackers are targeting poorly configured Docker servers exposing Docker REST APIs as part of an ongoing campaign that started in October. Threat actors execute malicious scripts to deploy Monero cryptocurrency miners, […]
 Pierluigi Paganini
November 09, 2021
Robinhood disclosed a security breach, an unidentified threat actor gained unauthorized access to approximately 7 million customer records. Robinhood Markets, Inc. is an American commission-free stock trading and investing platform, it had 18 million accounts as of March 2021, with over $80 billion in assets. The company disclosed a data breach, a threat actor gained […]
 Pierluigi Paganini
November 09, 2021
The Clop ransomware gang is exploiting CVE-2021-35211 vulnerability in SolarWinds Serv-U to compromise corporate networks. Threat actors always look for new ways to compromise target networks, Clop ransomware gang (aka TA505, FIN11) is exploiting CVE-2021-35211 SolarWinds Serv-U vulnerability to breach businesses’ infrastructures and deploy its ransomware. The flaw is a remote code execution vulnerability that […]
 Pierluigi Paganini
November 09, 2021
The US DoJ has charged a REvil ransomware affiliate that is suspected to have orchestrated the attack on Kaseya MSP platform in July. The US Department of Justice has charged a REvil ransomware affiliate for orchestrating the ransomware attacks on Kaseya MSP platform that took place in July 4. The suspect is 22-year old Ukrainian national Yaroslav […]
 Pierluigi Paganini
November 08, 2021
The healthcare industry might be known for the work it does to treat patients. But it is also a prime target for malicious cyber actors. With copious amounts of data collected by healthcare facilities, cybercriminals often target such entities. Moreover, the healthcare industry collects unique data, known as Protected Health Information (PHI), which is extremely […]
 Pierluigi Paganini
November 08, 2021
Experts warn of an ongoing hacking campaign that already compromised at least nine organizations worldwide from critical sectors by exploiting CVE-2021-40539. Cybersecurity experts from Palo Alto Networks warn of an ongoing cyberespionage campaign that has already compromised at least nine organizations worldwide from critical sectors, including defense, healthcare, and energy. Threat actors exploited a critical […]
 Pierluigi Paganini
November 07, 2021
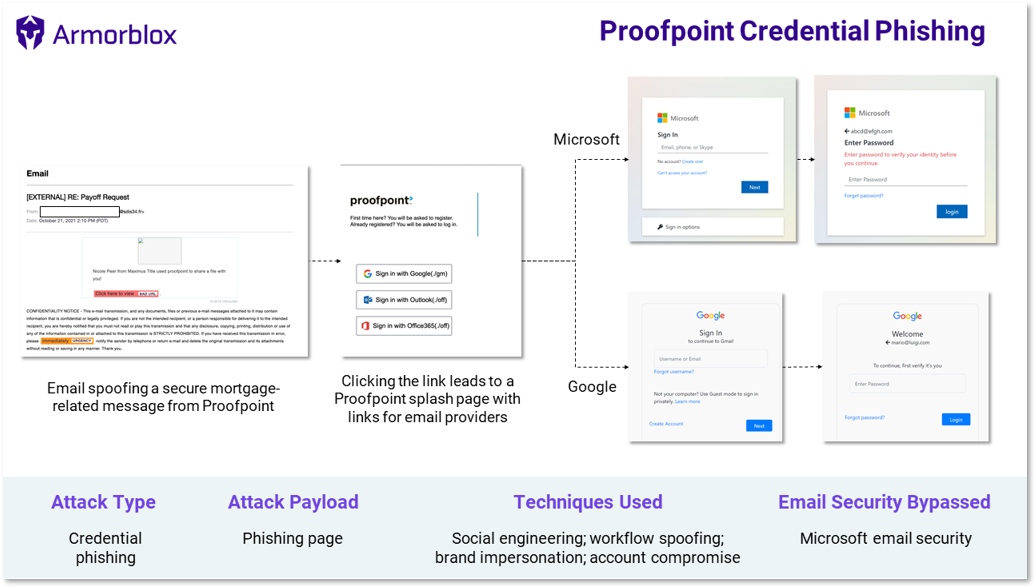
Threat actors are impersonating cybersecurity firm Proofpoint to trick victims into providing Microsoft Office 365 and Gmail credentials. Cybercriminals are impersonating the cybersecurity firm Proofpoint to trick victims into providing Microsoft Office 365 and Google Gmail credentials. The phishing messages use mortgage payments as a lure, they have the subject “Re: Payoff Request.” “The email […]
 Pierluigi Paganini
November 07, 2021
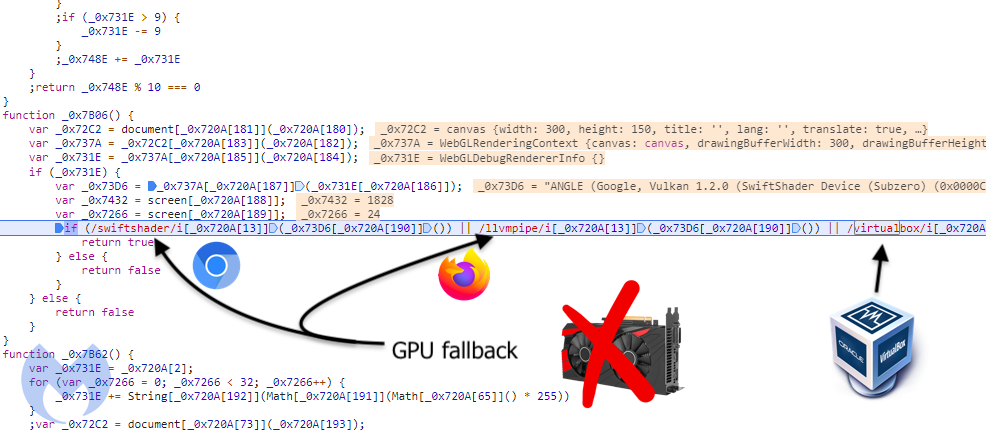
A new Magecart group leverages a browser script to evade virtualized environments and sandboxes used by researchers. Malwarebytes researchers have spotted a new Magecart group that uses a browser script to evade detection and the execution in virtualized environments used by security researchers for threat analysis. Hacker groups under the Magecart umbrella continue to target e-stores to […]
 Pierluigi Paganini
November 06, 2021
DeFi platforms are a privileged target for crooks, threat actors have stolen $55 million from bZx DeFi platform. Threat actors have stolen $55 million worth of cryptocurrency from the bZx decentralized finance (DeFi) platform. The decentralized finance (DeFi) platforms allow users to borrow/loan and speculate on cryptocurrency price variations. Attackers obtained two private keys for […]
Pierluigi Paganini
November 06, 2021
The Philips Tasy EMR comprehensive healthcare informatics solution is affected by two critical SQL injection vulnerabilities. The Philips Tasy EMR is a comprehensive healthcare informatics solution that is used by thousands of hospitals and healthcare infrastructures, mainly in South America. The product is affected by two critical SQL injection vulnerabilities, tracked as CVE-2021-39375 and CVE-2021-39376 respectively. Both issues […]





