



 Pierluigi Paganini
 October 11, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: The five vulnerabilities have been added to a broader list of flaws linked to cyber […]
 Pierluigi Paganini
October 10, 2026
Anthropic’s models kept working around the rules on the live internet. The company published the cases. Anthropic released a report on unintended actions its Claude models took during evaluations and internal use. The cases involved real websites and real organizations outside the company. Anthropic says the impact was minimal, and it published them anyway. The […]
 Pierluigi Paganini
October 09, 2026
DOJ and FBI seized China-linked hacking tools Microscan and FishHub, linked to Integrity Tech and attacks on critical infrastructure worldwide. The Justice Department and FBI took down two hacking tools this week, Microscan and FishHub, both built and run by a Beijing-based company with direct government contracts. The tools were used to scan, and in […]
Pierluigi Paganini
October 09, 2026
CrowdStrike analyzes open directories left by an attacker who used the ARTEX AI pentest tool and LLMs to breach South Korean financial firms. CrowdStrike published a research on a campaign against South Korean financial organizations that ran from late September to early October 2026 and ended with stolen data. The attacker left their working notes […]
 Pierluigi Paganini
October 08, 2026
Italy’s Foreign Ministry is defending its website against a cyberattack, checking embassy sites and pushing for EU action to identify attackers. On the morning of October 8, Italy’s Ministry of Foreign Affairs said its website was being attacked. According to the ministry’s own statement, its protection systems have mitigated the attack so far, with no […]
 Pierluigi Paganini
October 08, 2026
MonsterCloud owner Zohar Pinhasi allegedly paid ransomware demands behind clients’ backs, then charged them millions for the supposed recovery. Zohar Pinhasi, the owner of Florida-based MonsterCloud, was charged this week with wire fraud. Federal prosecutors say his clients were scammed twice during the same ransomware crisis. Pinhasi (50) also used the names “Zack Silver” and […]
 Pierluigi Paganini
October 08, 2026
Threat actors are exploiting CVE-2026-21589, a critical Atlassian flaw that can expose sensitive files across multiple Data Center products. Threat actors have started exploiting CVE-2026-21589 (CVSS score of 9.3), a critical arbitrary file access flaw in Atlassian Data Center products. The vulnerability could allow attackers to access sensitive files under certain conditions. Affected products include […]
 Pierluigi Paganini
October 07, 2026
FBI and Secret Service warn FortiBleed, a credential-harvesting campaign against Fortinet firewalls, has compromised 86,644 devices and is locking out admins. The FBI and the U.S. Secret Service issued a joint advisory about FortiBleed, and the headline number alone is worth sitting with: more than 86,644 compromised Fortinet FortiGate devices across 194 countries, according to […]
 Pierluigi Paganini
October 07, 2026
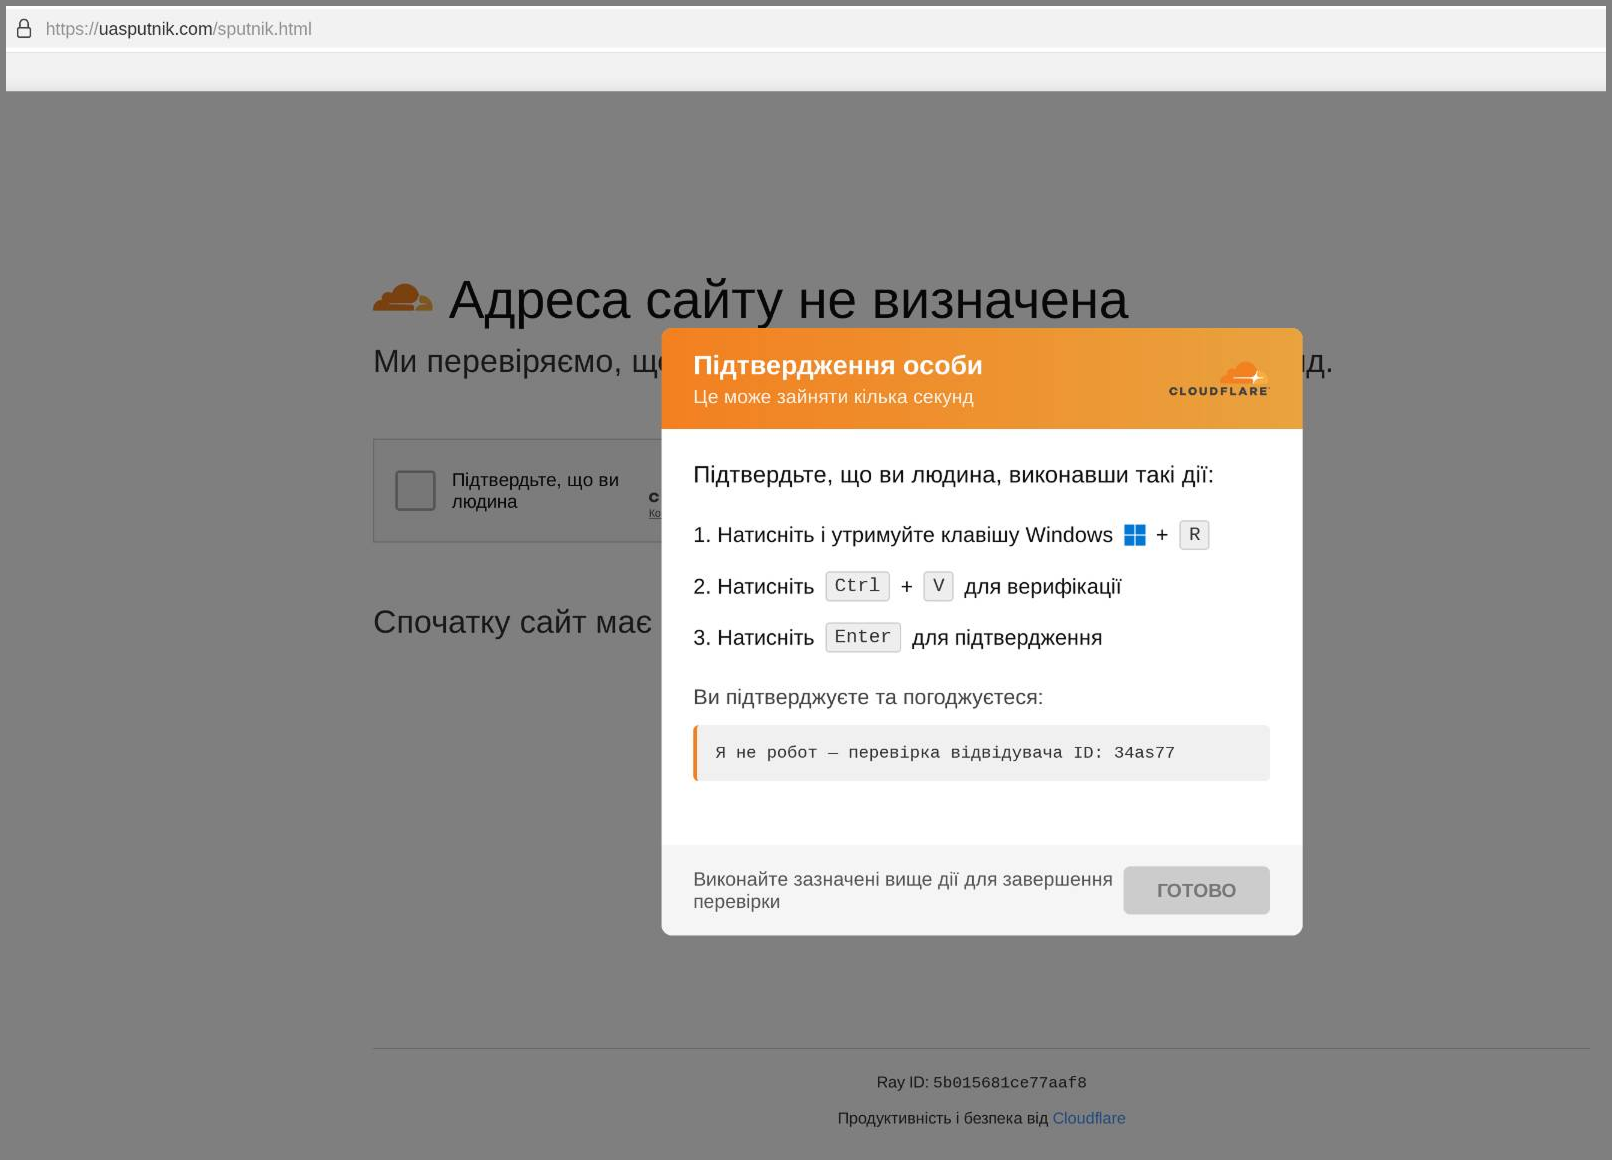
Over 100 hacked websites used fake Cloudflare checks to trick visitors into installing LunexStealer through ClickFix commands. The lure is the now-familiar ClickFix technique, dressed up as Cloudflare’s standard bot check. The fake page asks you to run a command, supposedly to confirm you’re not a bot, and that command quietly downloads and installs an […]
 Pierluigi Paganini
October 07, 2026
Wikimedia found unauthorized OpenAI agent activity on its platforms, including unapproved edits, proxy attempts and millions of automated API requests. Wikimedia ran its own investigation after other organizations started reporting rogue AI agents breaking into websites, and the answer came back yes, it happened here too. The foundation found unauthorized bot activity tied to OpenAI […]




