


 Pierluigi Paganini
 October 13, 2021
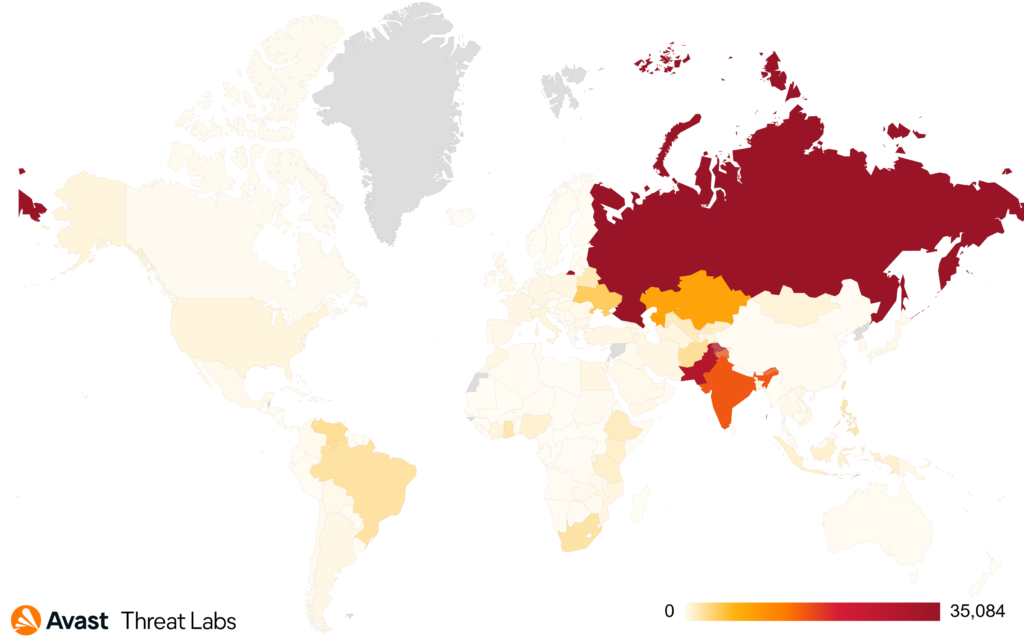
The MyKings botnet (aka Smominru or DarkCloud) is still alive and continues to spread, allowing its operators to make huge amounts of money. Avast Threat Labs researchers reported that the MyKings botnet (aka Smominru or DarkCloud) is still alive and is allowing its operators to earn huge amounts of money via cryptomining activities. Avast researchers reported […]
 Pierluigi Paganini
October 13, 2021
Dutch police warn customers of a distributed denial-of-service (DDoS) website of stopping using the service to avoid prosecution. Dutch police warn customers of a booter service, abused to carry out distributed denial-of-service (DDoS) attacks, of to stop using it to avoid prosecution. The letter sent by the Dutch Police aims to work as a deterrent […]
 Pierluigi Paganini
October 13, 2021
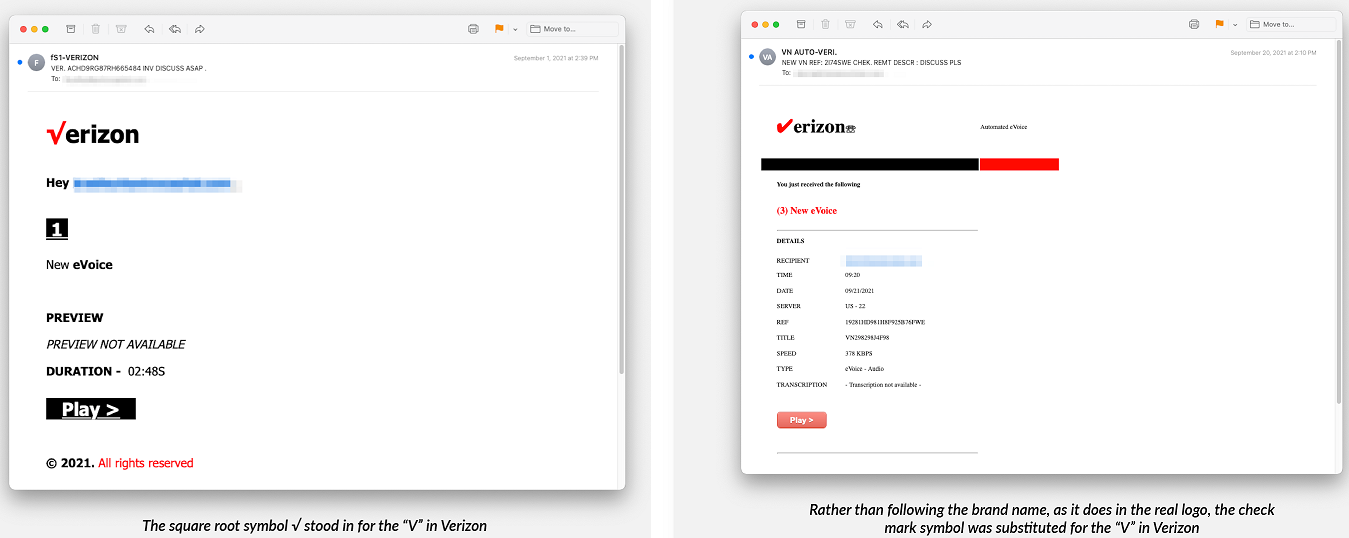
Threat actors are using mathematical symbols on impersonated company logos to evade detection in phishing campaigns. Researchers from anti-phishing cybersecurity firm INKY have detailed a new technique to evade detection in phishing attacks, it leverages using mathematical symbols on impersonated company logos. The experts analyzed the case of a campaign targeting the customers of the […]
 Pierluigi Paganini
October 13, 2021
A Chinese-speaking hacking group exploited a Windows zero-day vulnerability in a wave of attacks on defense and IT businesses. A Chinese-speaking hacking group exploited a zero-day vulnerability in the Windows Win32k kernel driver to deploy a new remote access trojan (RAT), tracked as MysterySnail. The attacks were conducted between late August and early September 2021 […]
 Pierluigi Paganini
October 12, 2021
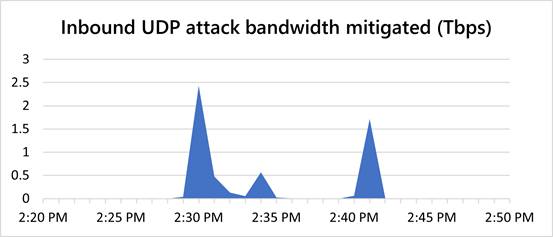
Microsoft Azure cloud service mitigated a massive DDoS attack of 2.4 terabytes per second (Tbps) at the end of August, it is the largest DDoS attack to date. Microsoft announced that its Azure cloud service mitigated a 2.4 terabytes per second (Tbps) DDoS attack at the end of August, it represents the largest DDoS attack […]
 Pierluigi Paganini
October 11, 2021
DEV-0343: Iran-linked threat actors are targeting US and Israeli defense technology companies leveraging password spraying attacks. Researchers at Microsoft Threat Intelligence Center (MSTIC) and Microsoft Digital Security Unit (DSU) uncovered a malicious activity cluster, tracked as DEV-0343, that is targeting the Office 365 tenants of US and Israeli defense technology companies. Threat actors are launching extensive […]
 Pierluigi Paganini
October 11, 2021
LibreOffice and OpenOffice released security updates to address a vulnerability that can be exploited by an attacker to spoof signed documents. LibreOffice and OpenOffice released security updates to address a moderate-severity flaw that can allow attackers to manipulate documents to appear as signed by a trusted source. “It is possible for an attacker to manipulate documents […]
 Pierluigi Paganini
October 11, 2021
Donot Team targeted a Togolese human rights advocate with a mobile spyware that has been allegedly developed by an Indian firm. Researchers from Amnesty International have uncovered a cyberespionage campaign tracked as ‘Donot Team‘ (aka APT-C-35), which was orchestrated by threat actors in India and Pakistan. Experts believe the attackers used a spyware developed by […]
 Pierluigi Paganini
October 10, 2021
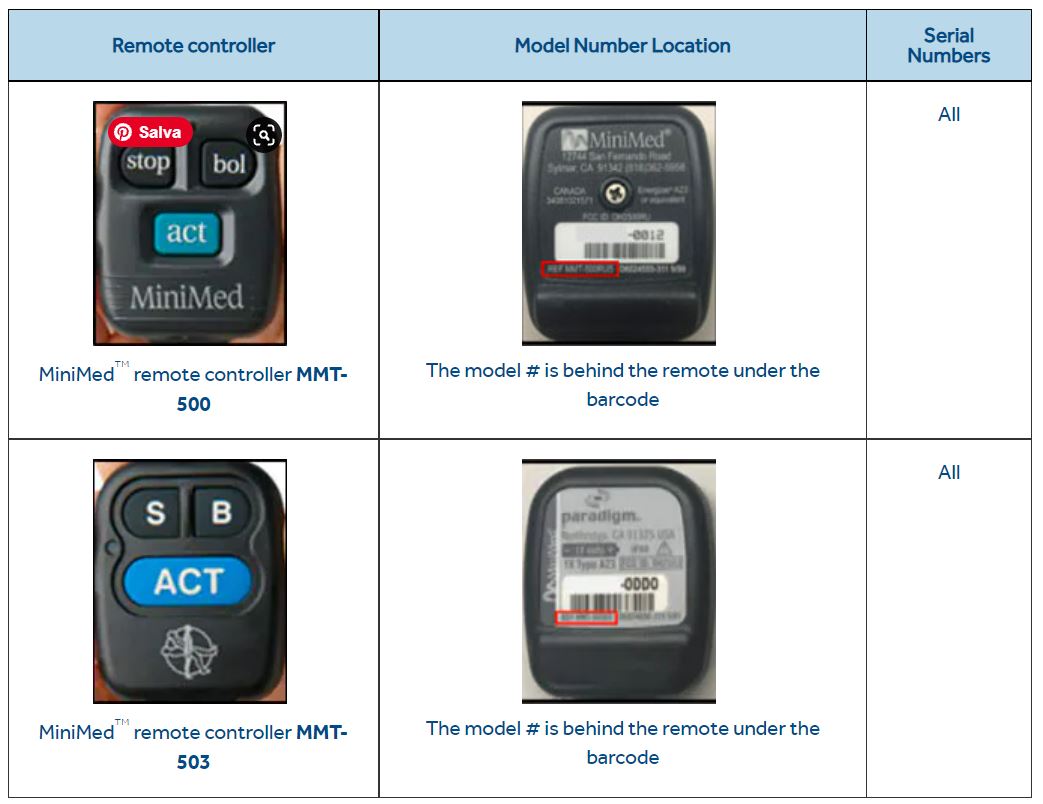
Medical device maker Medtronic recalled the remote controllers used with some of its insulin pumps because of dangerous vulnerabilities. Medical device maker Medtronic has recalled the remote controllers used with some of its insulin pumps because of they are affected by severe vulnerabilities that could lead to injury or death of the patients. An attacker can exploit the vulnerabilities […]
 Pierluigi Paganini
October 09, 2021
Security expert Dhiraj Mishra published an NMAP script for the CVE-2021-41773 Path Traversal vulnerability affecting Apache Web Server version 2.4.49. Security researcher Dhiraj Mishra released an NMAP script for the CVE-2021-41773 path traversal vulnerability affecting Apache Web Server version 2.4.49. This week Apache Software Foundation has released HTTP Web Server 2.4.51 to address an actively exploited path […]





