


 Pierluigi Paganini
 October 08, 2021
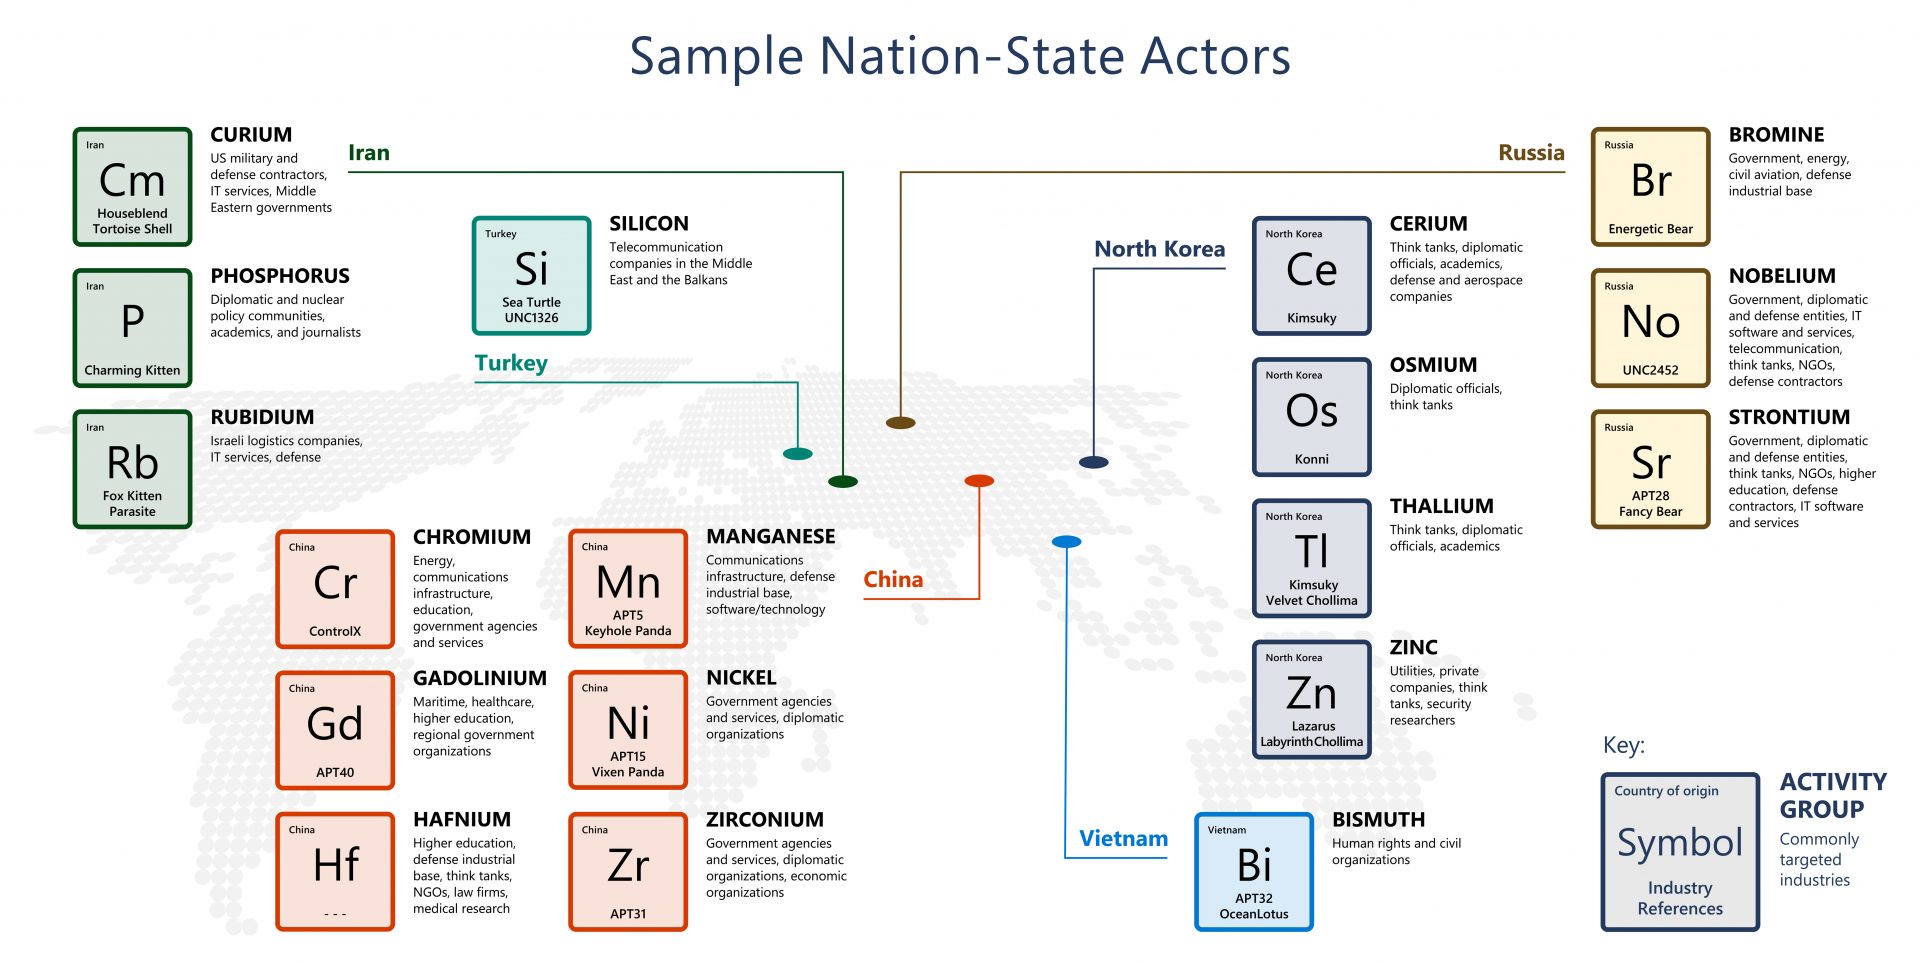
Microsoft revealed that Russia-linked cyberespionage groups are behind the majority of the nation-state cyber attacks on US government agencies. Microsoft revealed that most of the cyber attacks on US government agencies are orchestrated by Russia-linked cyberespionage groups. According to the IT giant, approximately 58% of all nation-state attacks between July 2020 and June 2021 were […]
 Pierluigi Paganini
October 08, 2021
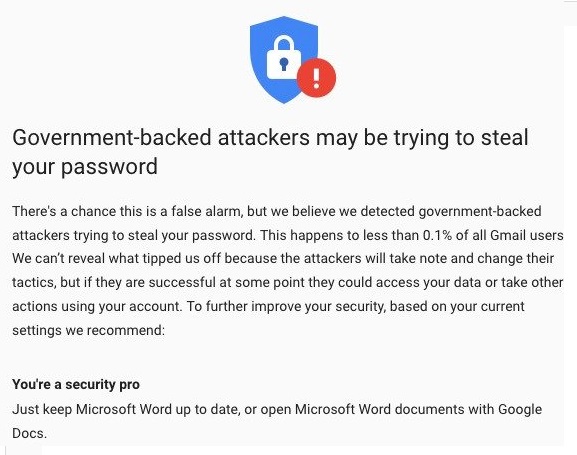
Google warned more than 14,000 Gmail users that they have been the target of nation-state spear-phishing campaigns. On Wednesday, Google announced to have warned approximately 14,000 Gmail users that they had been targeted by nation-state hackers. Shane Huntley, the head of the Threat Analysis Group (TAG), wrote on Twitter that his group had sent an above-average batch […]
 Pierluigi Paganini
October 08, 2021
Apache Software Foundation has released HTTP Web Server 2.4.51 to completely address a vulnerability that has been actively exploited in the wild. Apache Software Foundation has released HTTP Web Server 2.4.51 to address an actively exploited path traversal vulnerability (CVE-2021-41773) that was only partially addressed with a previous release. An attacker can trigger the flaw […]
 Pierluigi Paganini
October 07, 2021
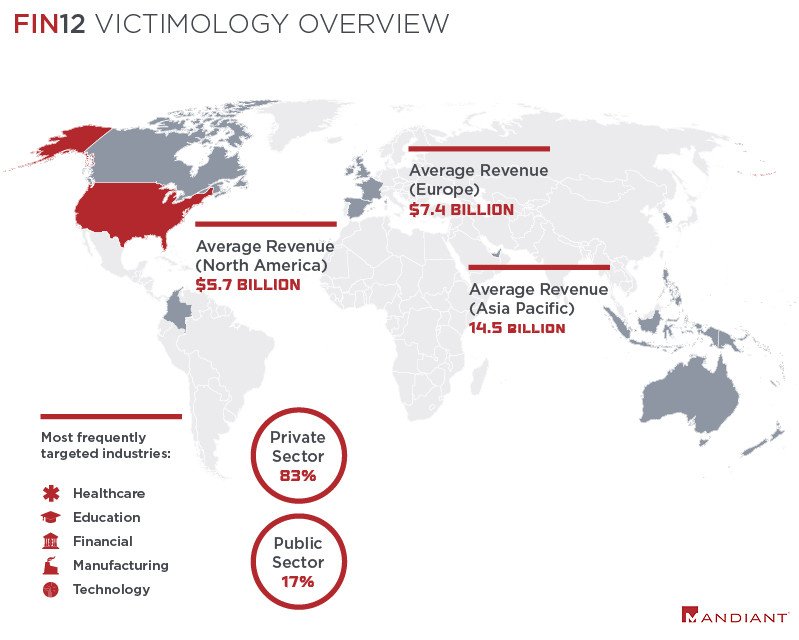
Researchers detailed the activities of the FIN12 ransomware group that earned million of dollars over the past years. Researchers from Mandiant published a detailed report on the activities of a financially motivated ransomware group tracked as FIN12 that has been active since at least October 2018. The vast majority of FIN12 victims have more than […]
 Pierluigi Paganini
October 07, 2021
A proof of concept exploit for two authentication bypass vulnerabilities in Dahua cameras is available online, users are recommended to immediately apply updates. Experts warn of the availability of proof of concept (PoC) exploit code for a couple of authentication bypass vulnerabilities in Dahua cameras, tracked as CVE-2021-33044 and CVE-2021-33045. A remote attacker can exploit both vulnerabilities […]
 Pierluigi Paganini
October 07, 2021
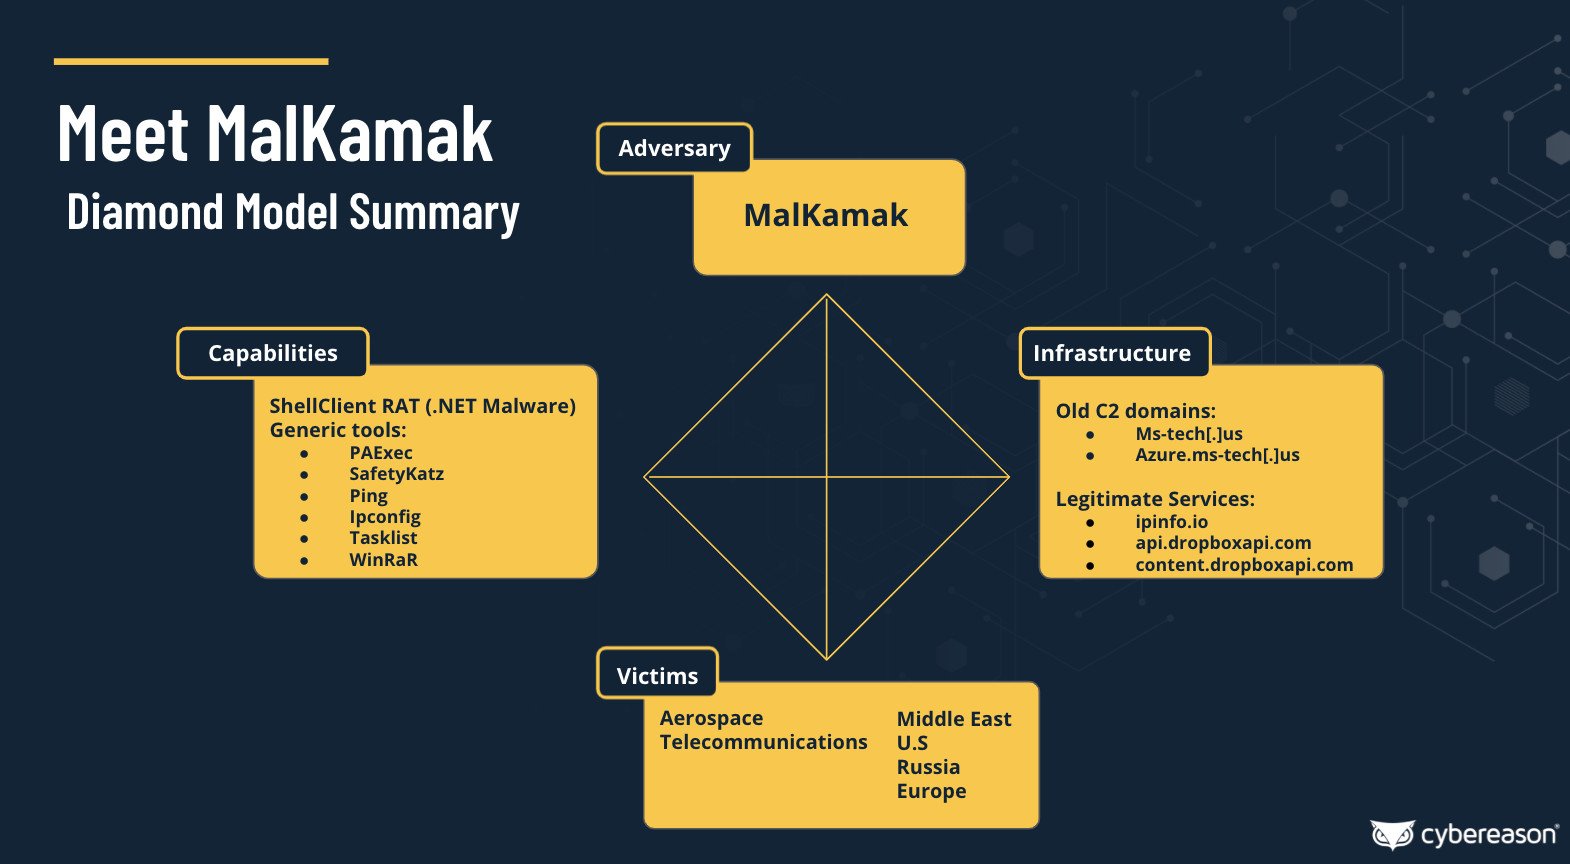
Operation GhostShell: Threat actors used ShellClient malware in cyberespionage campaigns aimed at companies in the aerospace and telecommunications sectors. Hackers use stealthy ShellClient malware on aerospace, telco firms Cybereason Nocturnus and Incident Response Teams discovered a new threat actor that is targeting organizations in the aerospace and telecommunications sectors with the ShellClient malware as part […]
 Pierluigi Paganini
October 06, 2021
Resecurity researchers dumped Gigabytes of data from Agent Tesla C2Cs, one of the most well-known cyberespionage tools suffers a data leakage. Agent Tesla, first discovered in late 2014, is an extremely popular “malware-as-a-service” Remote Access Trojan (RAT) tool used by threat actors to steal information such as credentials, keystrokes, clipboard data and other information from […]
 Pierluigi Paganini
October 06, 2021
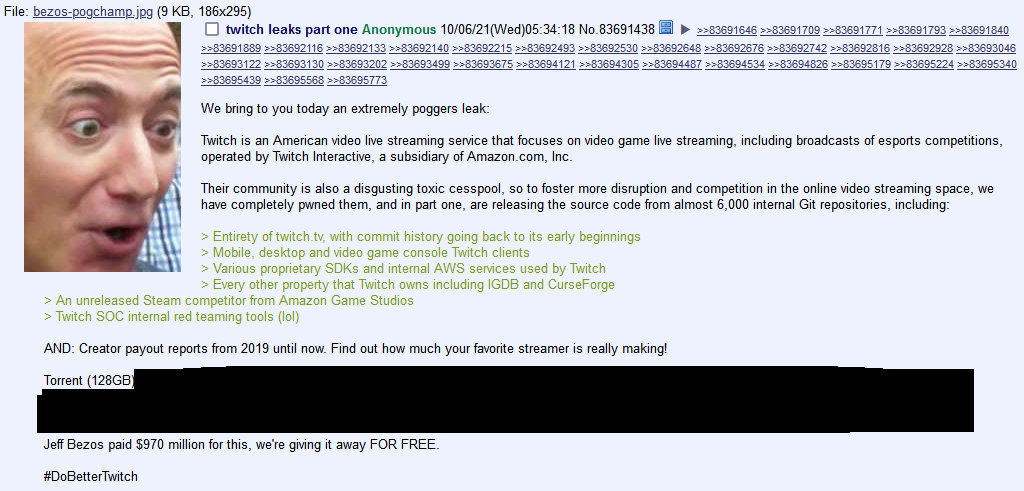
An anonymous individual has leaked the source code and data of the popular video streaming platform Twitch via a torrent file posted on 4chan. An anonymous individual has leaked online the source code and streamers and users data of the popular video streaming platform Twitch. The anonymous 4chan user has published a torrent link to […]
 Pierluigi Paganini
October 06, 2021
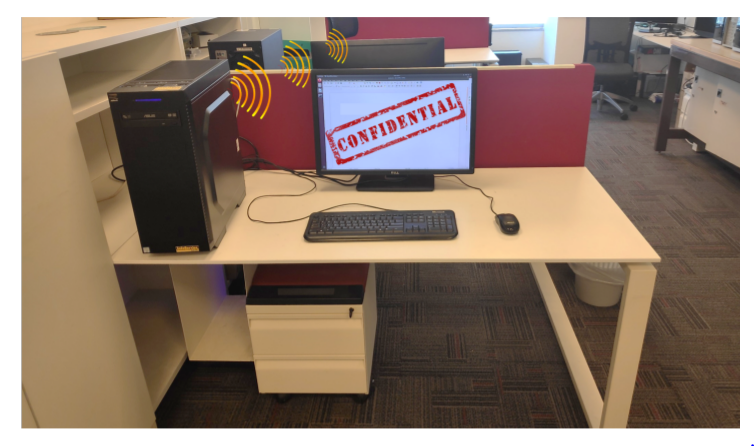
Boffins devised a new technique, dubbed LANtenna, to exfiltrate data from systems in air-gapped networks using Ethernet cables as a “transmitting antenna.” Security researchers from the Cyber Security Research Center in the Ben Gurion University of the Negev (Israel) devised a new data exfiltration mechanism, dubbed LANtenna Attack, that leverages Ethernet cables as a “transmitting […]
Pierluigi Paganini
October 05, 2021
Apache has addressed two vulnerabilities, one of which is a path traversal and file disclosure flaw in its HTTP server actively exploited in the wild. Apache has rolled out security patches to address two flaws, including a path traversal and file disclosure issue in its HTTP server that is actively exploited in the wild. The […]





