


 Pierluigi Paganini
 September 28, 2021
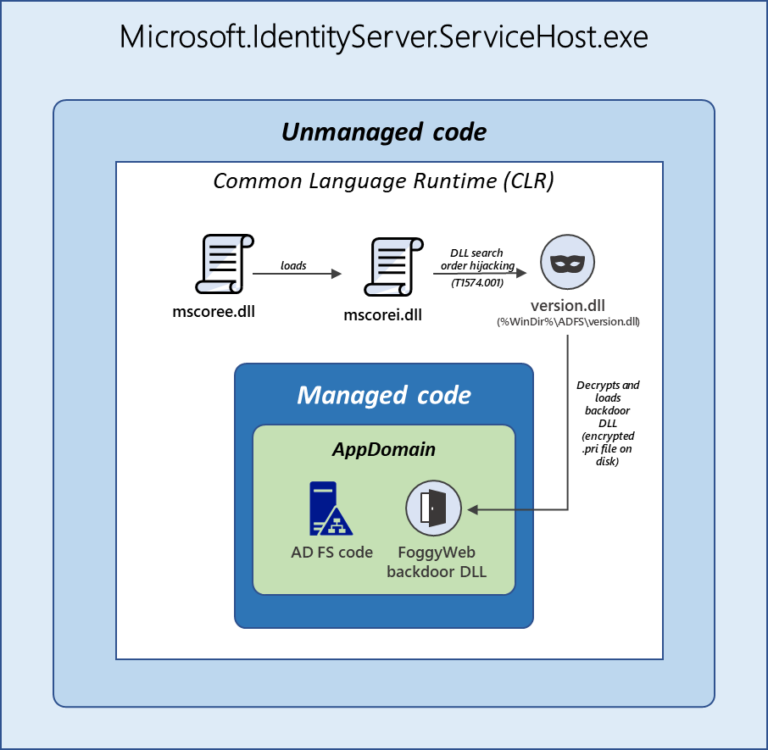
Microsoft discovered new custom malware, dubbed FoggyWeb, used by the Nobelium cyberespionage group to implant backdoor in Windows domains. Microsoft Threat Intelligence Center (MSTIC) researchers have discovered a new custom malware, dubbed FoggyWeb used by the Nobelium APT group to deploy additional payloads and steal sensitive info from Active Directory Federation Services (AD FS) servers. […]
 Pierluigi Paganini
September 27, 2021
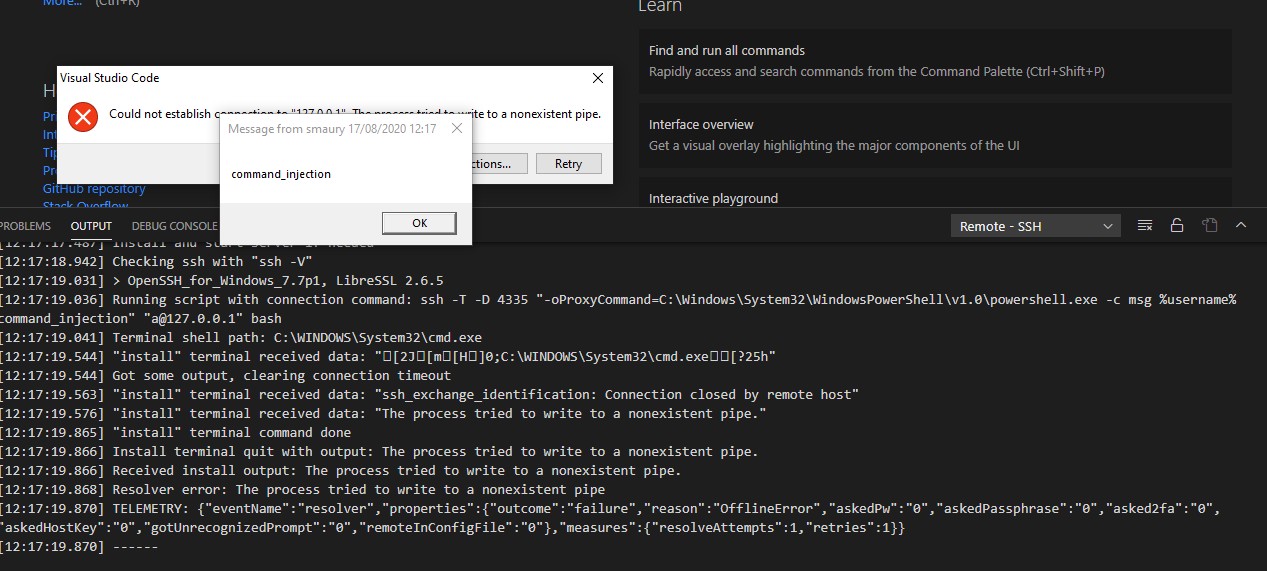
Researchers from the Italian cybersecurity firm Shielder found a remote code execution vulnerability in Visual Studio Code Remote Development Extension. Visual Studio Code Remote Development allows users to adopt a container, remote machine, or the Windows Subsystem for Linux (WSL) as a full-featured development environment. Users can: Develop on the same operating system you deploy to or use […]
 Pierluigi Paganini
September 26, 2021
Last month, the Port of Houston, one of the major US ports, was hit by a cyber attack allegedly orchestrated by a nation-state actor. One of the major US ports, the Port of Houston, revealed that it was hit by a cyber attack in August that had no impact on its systems. “The Port of […]
 Pierluigi Paganini
September 26, 2021
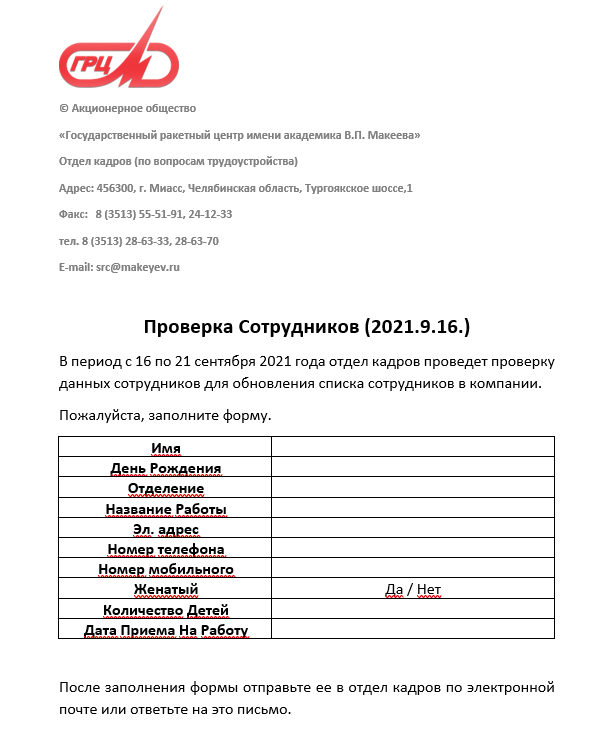
A cyberespionage campaign hit multiple Russian organizations, including JSC GREC Makeyev, a major defense contractor, exploiting a recently disclosed zero-day. Security researchers from Malwarebytes uncovered multiple attacks targeting many Russian organizations, including JSC GREC Makeyev, a company that develops liquid and solid fuel for Russia’s ballistic missiles and space rocket program. Threat actors behind the cyberespionage […]
 Pierluigi Paganini
September 26, 2021
Researchers from Google’s TAG team reported that financially motivated actors are using new code signing tricks to evade detection. Researchers from Google’s Threat Analysis Group reported that financially motivated actors are using new code signing tricks to evade detection. By code signing executables, it is possible to verify their integrity and provide information about the […]
 Pierluigi Paganini
September 25, 2021
Immediately after the public release of the exploit code for the VMware vCenter CVE-2021-22005 flaw threat actors started using it. Researchers warn that immediately after the release of the exploit code for the recently addressed CVE-2021-22005 flaw in VMware vCenter threat actors started using it. The CVE-2021-22005 issue is a critical arbitrary file upload vulnerability […]
 Pierluigi Paganini
September 25, 2021
Google released a Chrome emergency update for Windows, Mac, and Linux that addresses a high-severity zero-day flaw exploited in the wild. Google has released Chrome 94.0.4606.61 for Windows, Mac, and Linux that addresses a high-severity zero-day vulnerability (CVE-2021-37973) exploited in the wild. An attacker can exploit this flaw to execute arbitrary code on systems running vulnerable Chrome versions. This vulnerability […]
 Pierluigi Paganini
September 24, 2021
Researcher release PoC exploit code for three iOS zero-day flaws after Apple delayed addressing them and did not credit him. An unknown researcher publicly released on GitHub proof-of-concept exploit code for three iOS zero-day vulnerabilities and one flaw addressed by Apple in July. The experts discovered the four zero-day issues between March 10 and May […]
 Pierluigi Paganini
September 24, 2021
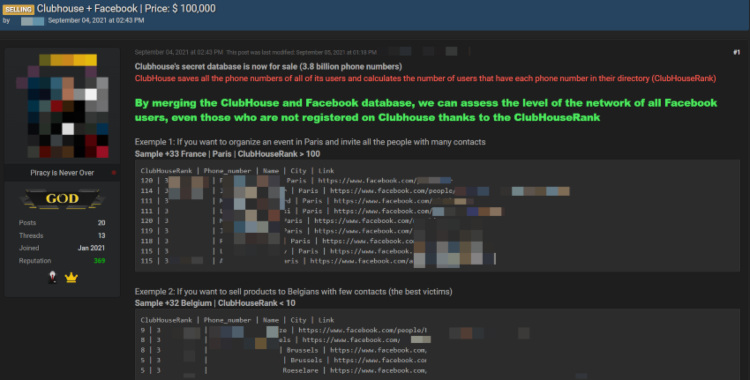
A user on a popular hacker forum is selling a database that purportedly contains 3.8 billion Clubhouse and Facebook user records. Original Post @CyberNews https://cybernews.com/security/3-8-billion-allegedly-scraped-and-merged-clubhouse-and-facebook-user-records-put-for-sale-online/ A user on a popular hacker forum is selling a database that purportedly contains 3.8 billion user records. The database was allegedly compiled by combining 3.8 billion phone numbers from […]
 Pierluigi Paganini
September 24, 2021
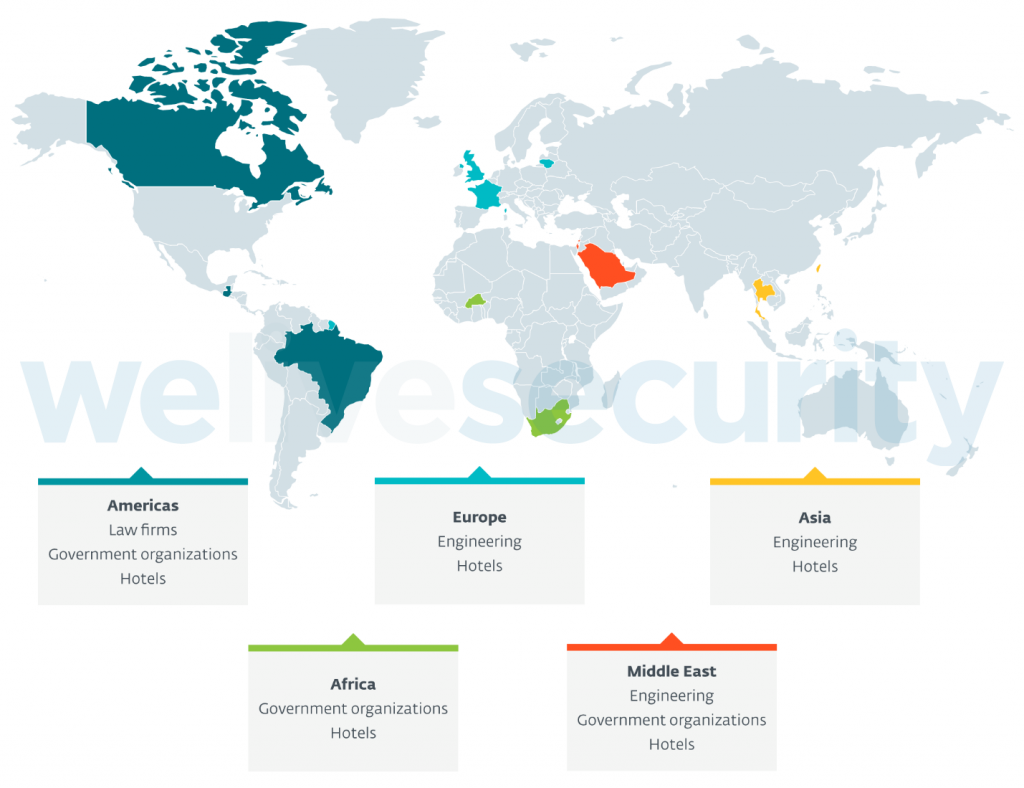
Researchers spotted a new cyberespionage group, dubbed FamousSparrow, that used ProxyLogon exploits to target hotels worldwide. Researchers from ESET discovered a new cyberespionage group, tracked as FamousSparrow, that has been targeting hotels worldwide around the world since at least 2019. The group also hit higher-profile targets such as law firms, governments, and private companies worldwide. According […]






