


 Pierluigi Paganini
 September 23, 2021
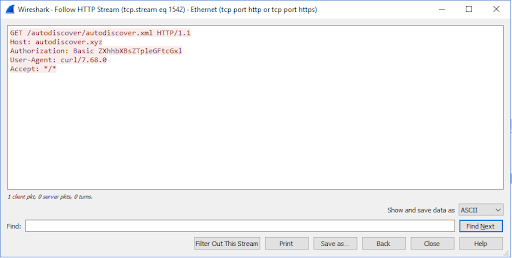
A flaw in the Microsoft Exchange Autodiscover feature can be exploited to harvest Windows domain and app credentials. Security researchers from Guardicore discovered a flaw in the Microsoft Exchange Autodiscover feature that can be exploited to harvest Windows domain and app credentials from users worldwide. The Microsoft Autodiscover protocol feature of Exchange email servers provides an […]
 Pierluigi Paganini
September 23, 2021
CVE-2021-40847 flaw in Netgear SOHO routers could be exploited by a remote attacker to execute arbitrary code as root. Security experts from consulting firm GRIMM have discovered a vulnerability in Small Offices/Home Offices (SOHO) Netgear routers that could be exploited by a remote attacker to execute arbitrary code as root The flaw, tracked as CVE-2021-40847, […]
 Pierluigi Paganini
September 22, 2021
A critical issue, tracked as CVE-2021-36260, affects more than 70 Hikvision device models and can allow attackers to take over them. A critical vulnerability, tracked as CVE-2021-36260, affects more than 70 Hikvision camera and NVR models and can allow attackers to take over the devices. The vulnerability is an unauthenticated Remote Code Execution (RCE) vulnerability […]
 Pierluigi Paganini
September 22, 2021
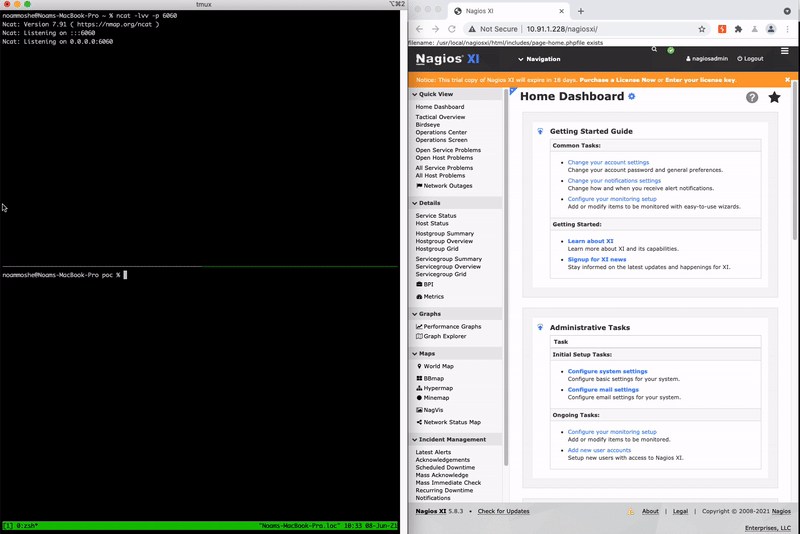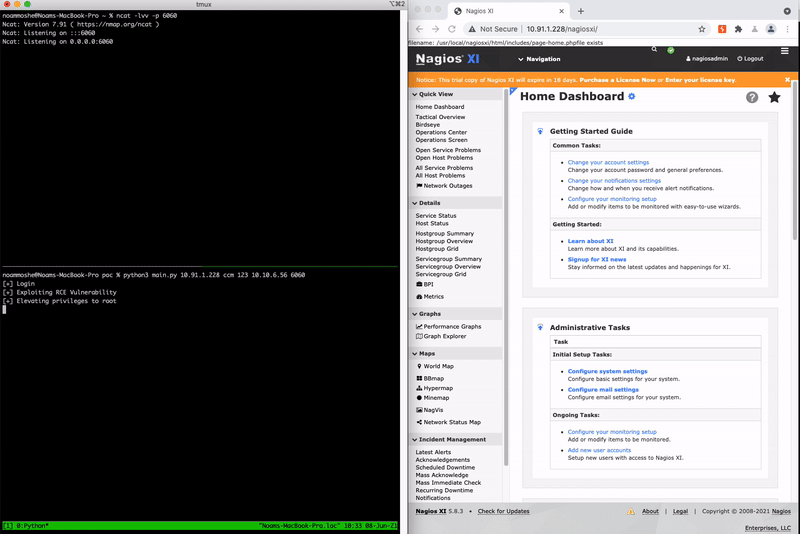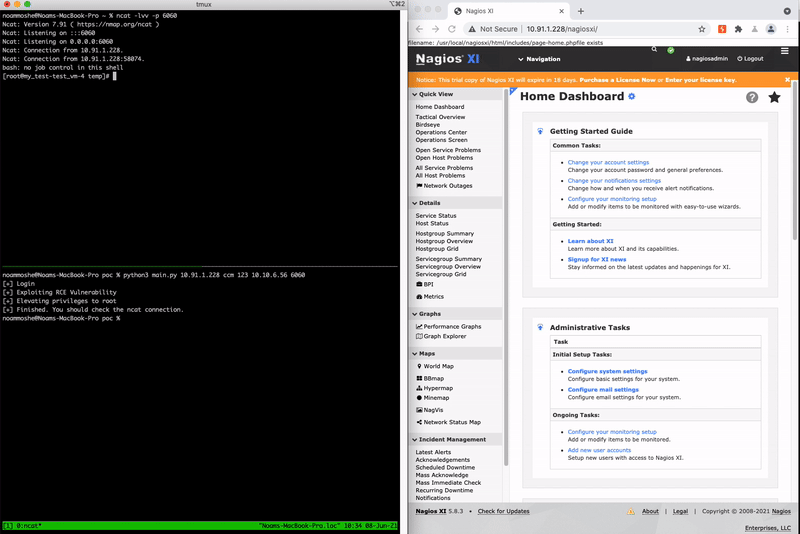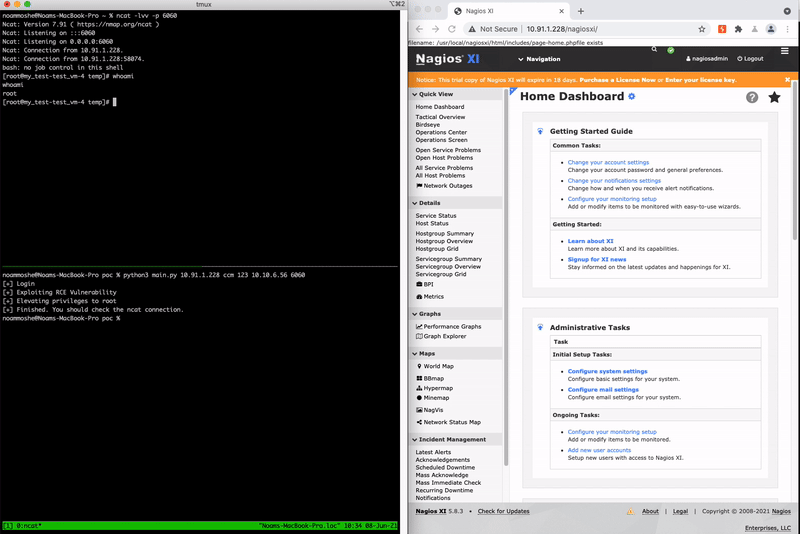
Researchers found multiple flaws in widely used network management products from Nagios that pose serious risk to organizations. Researchers from industrial cybersecurity firm Claroty have discovered eleven vulnerabilities in widely used network management products from Nagios. Nagios XI provides monitoring of all mission-critical infrastructure components including applications, services, operating systems, network protocols, systems metrics, and […]
 Pierluigi Paganini
September 21, 2021
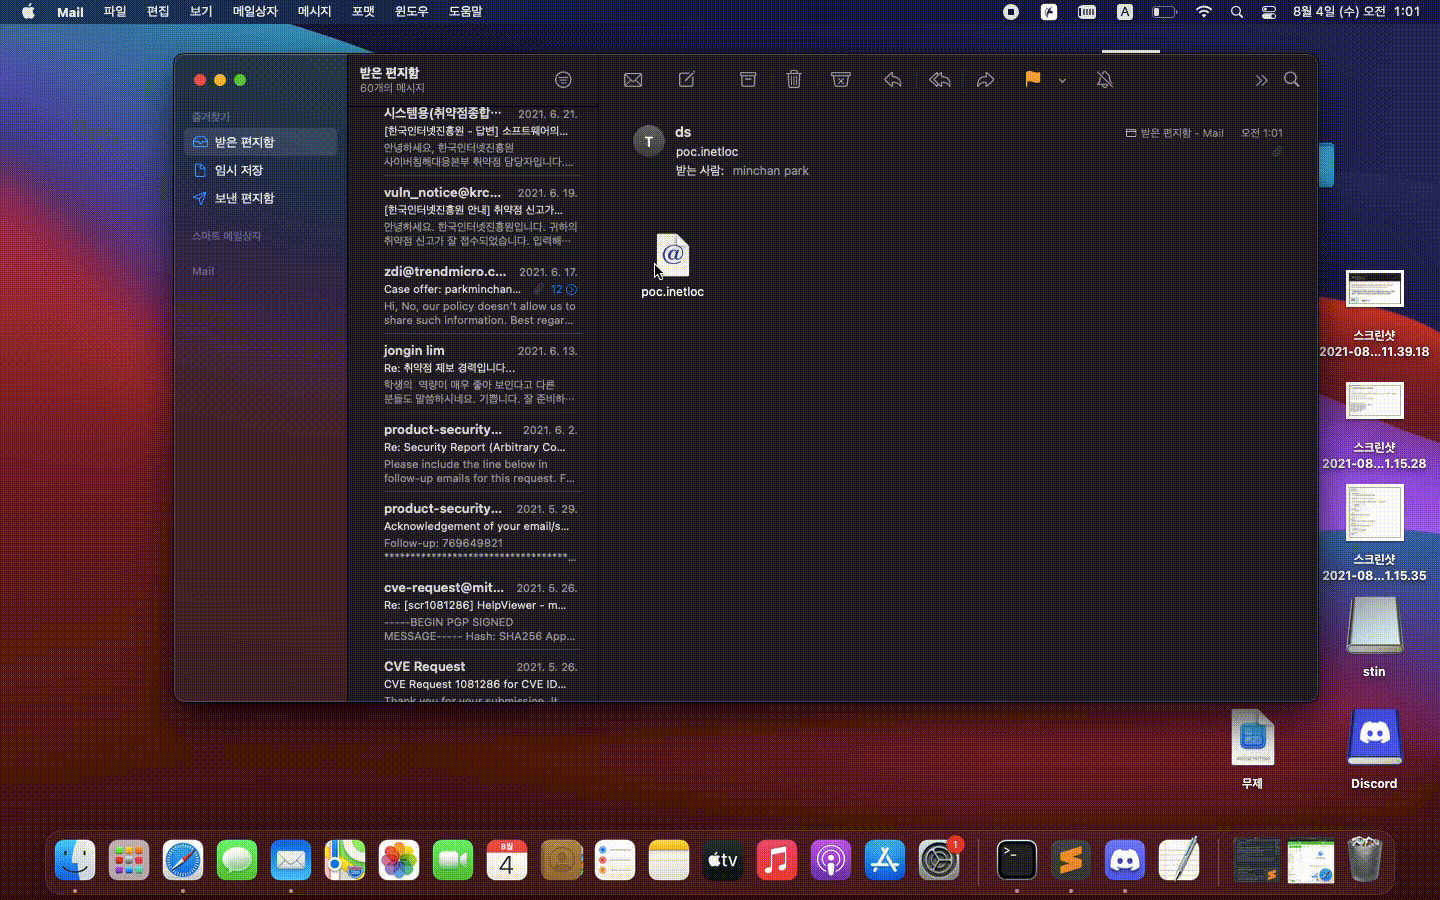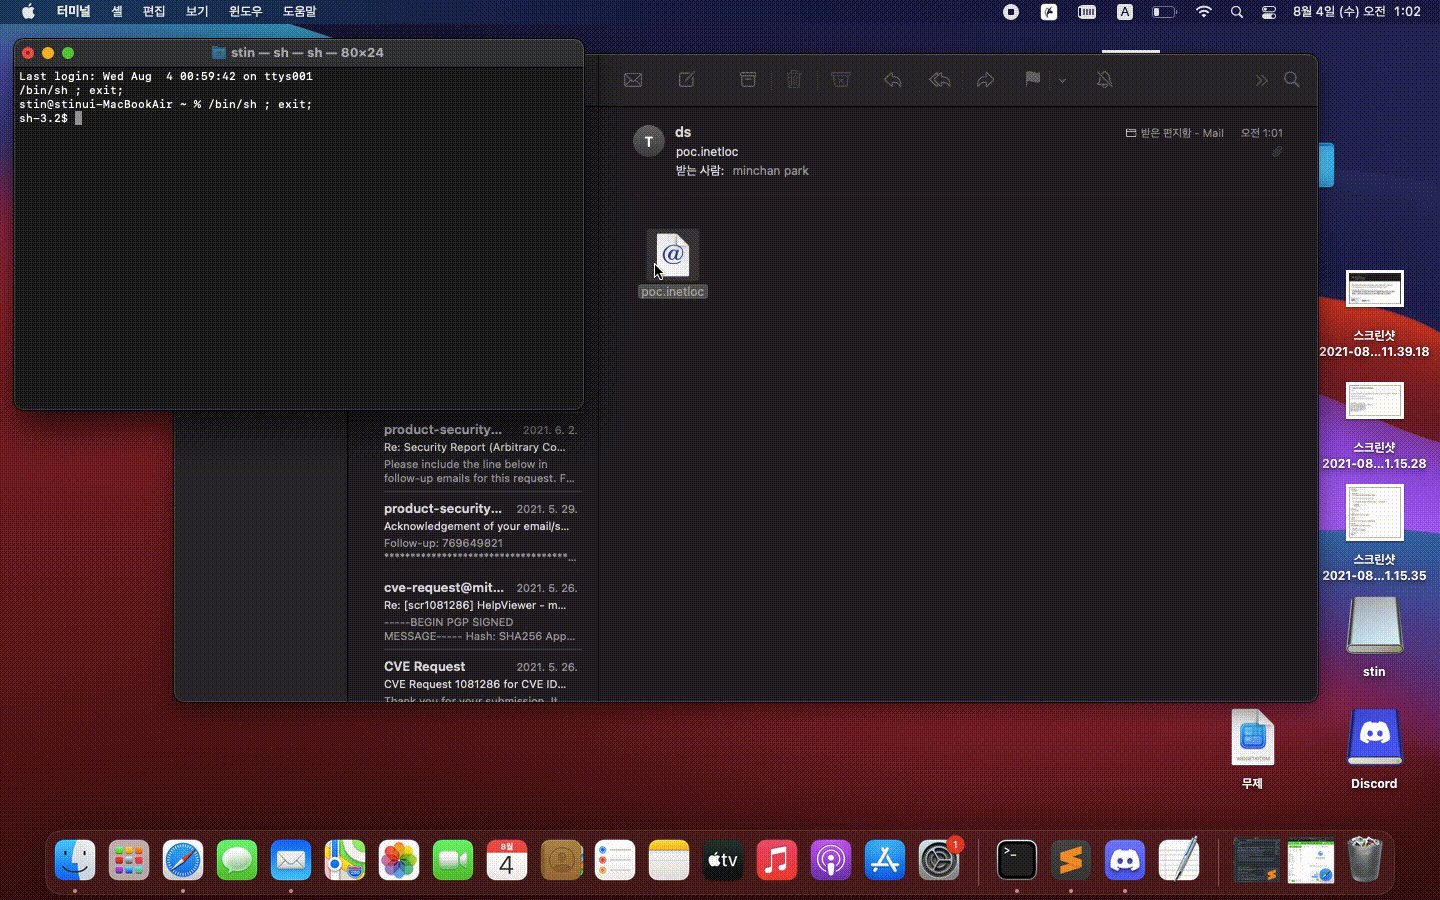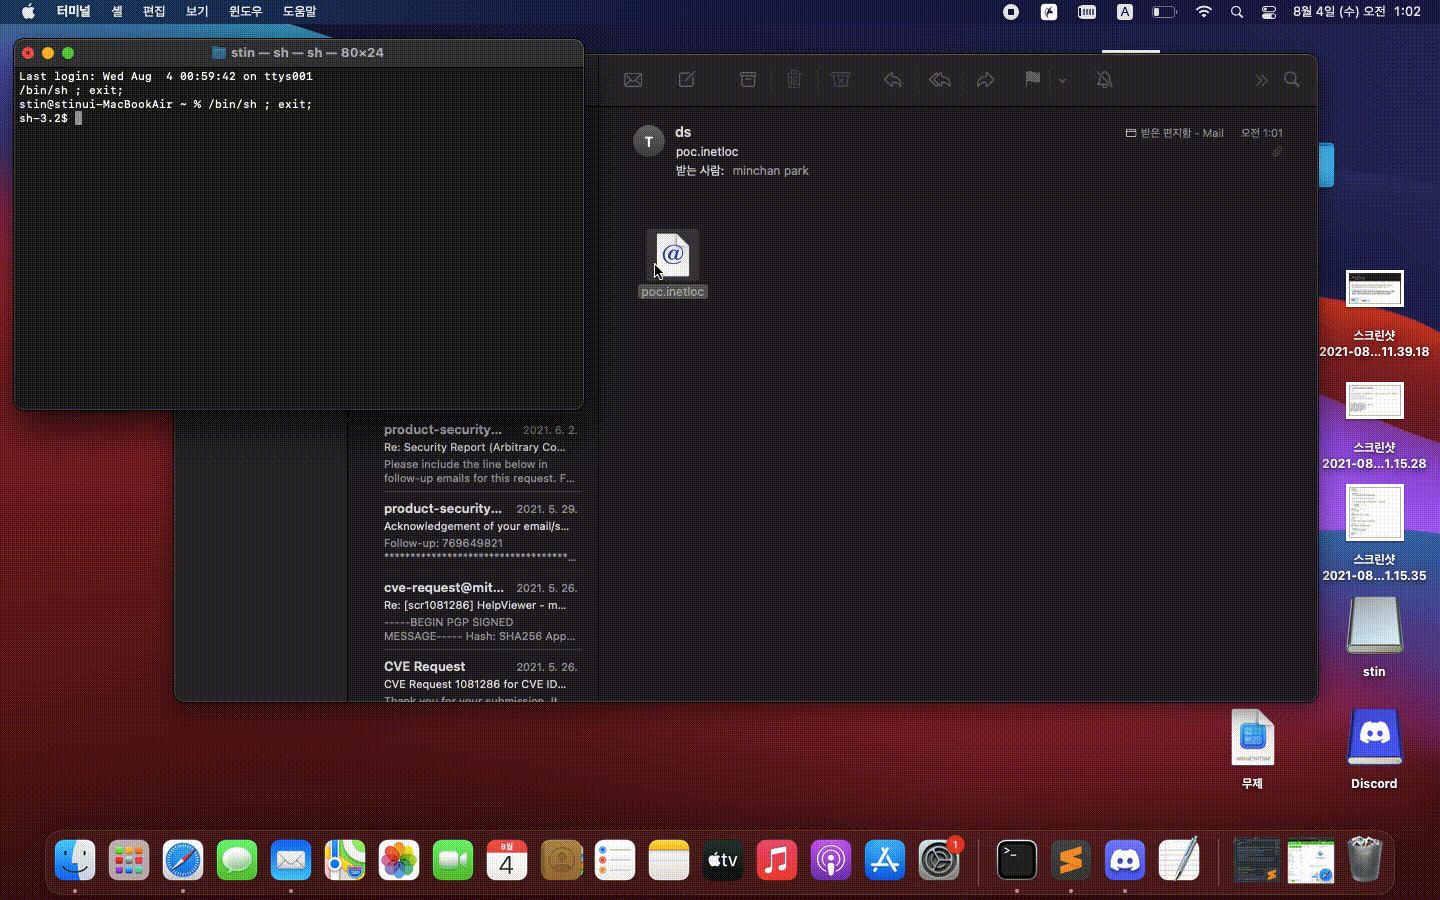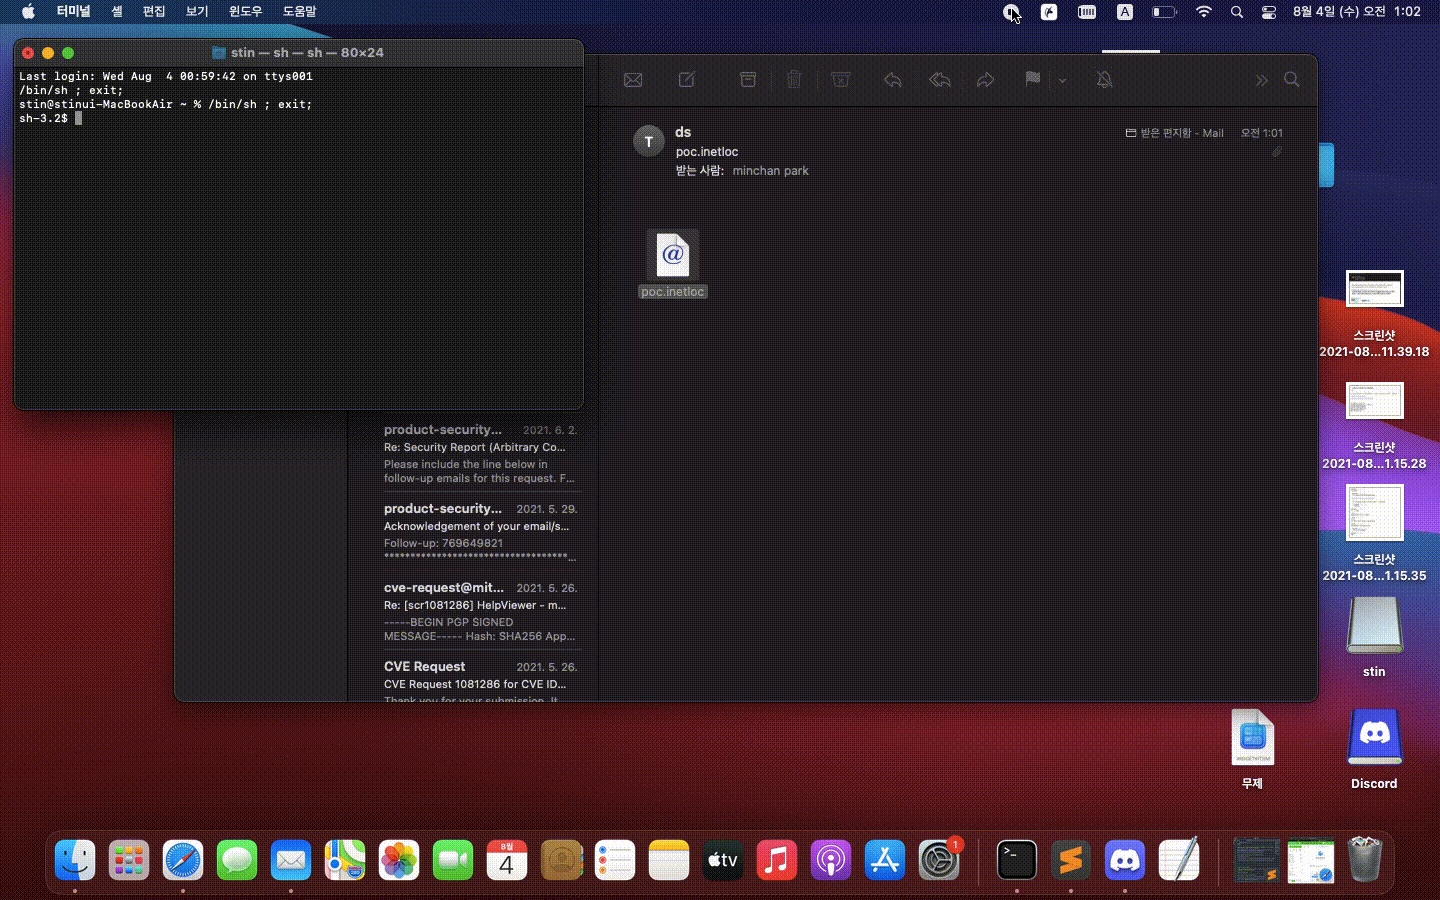
Security researchers disclosed a new zero-day flaw in Apple’s macOS Finder that can allow attackers to run arbitrary commands on Macs. Independent security researcher Park Minchan disclosed a zero-day vulnerability in Apple’s macOS Finder that can be exploited by attackers to run arbitrary commands on Mac systems running any macOS version. The flaw is due […]
 Pierluigi Paganini
September 21, 2021
Apache OpenOffice (AOO) is currently impacted by a remote code execution flaw, tracked as CVE-2021-33035, that has yet to be fixed in the official release. Security researcher Eugene Lim (@spaceraccoonsec) recently revealed technical details about a remote code execution flaw, tracked as CVE-2021-33035, (CVE-2021-33035) that impacts OpenOffice (AOO). The experts disclosed the flaw at HackerOne’s […]
 Pierluigi Paganini
September 20, 2021
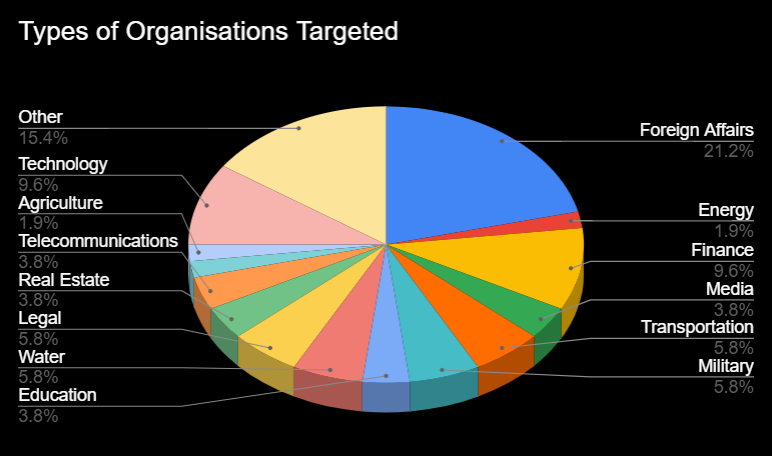
Security researchers uncovered a large phishing campaign targeting multiple government departments in APAC and EMEA countries. Researchers from cybersecurity firm Cyjax uncovered a large phishing campaign targeting multiple government departments in APAC and EMEA countries. The phishing campaign has been ongoing since spring 2020 when the domains were first transferred to their current host. At […]
 Pierluigi Paganini
September 20, 2021
A Pakistani national has been sentenced to 12 years of prison in the US for his role in a hacking scheme against the telecom giant AT&T. The Pakistani national Muhammad Fahd (35) was sentenced to 12 years of prison in the United States for his primary role in a seven-year scheme to illegally unlock nearly […]
Pierluigi Paganini
September 18, 2021
A new critical vulnerability in Netgear smart switches can be exploited by an attacker to potentially execute malicious code and take over impacted devices. Researchers provided technical details about a recently addressed critical vulnerability, dubbed Seventh Inferno, in Netgear smart switches that could be exploited by an attacker to potentially execute malicious code and take […]
 Pierluigi Paganini
September 17, 2021
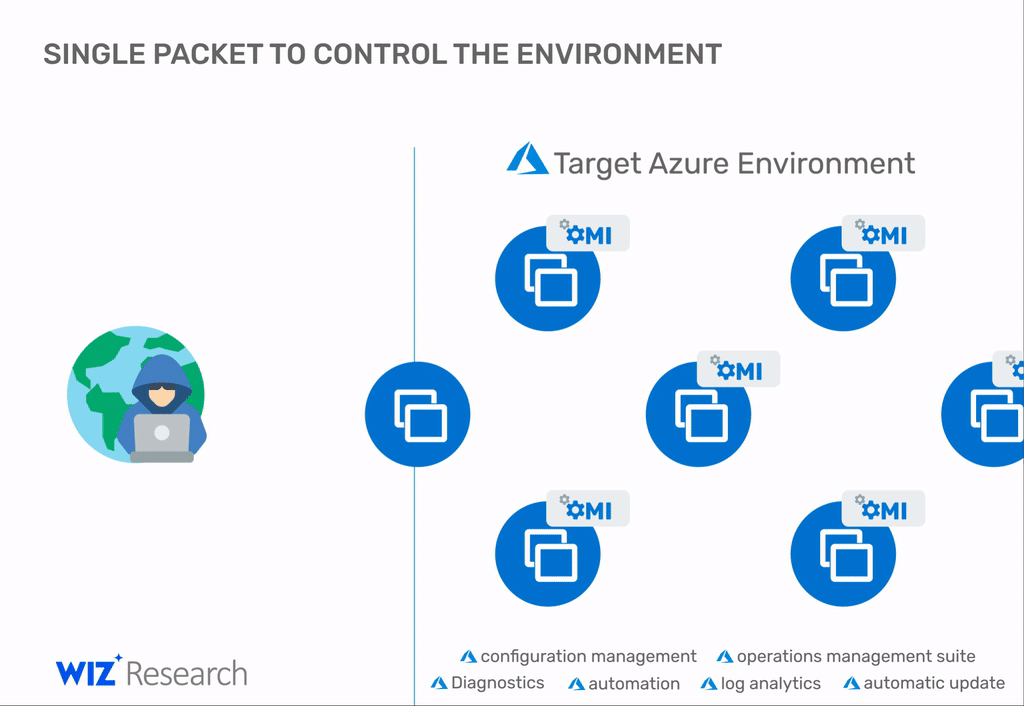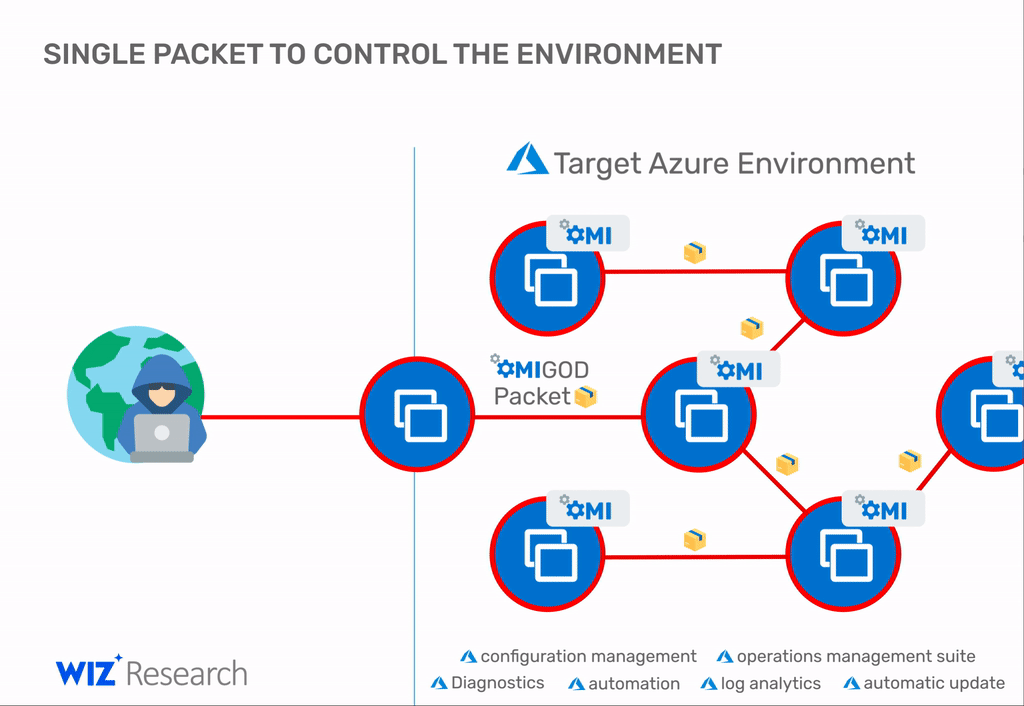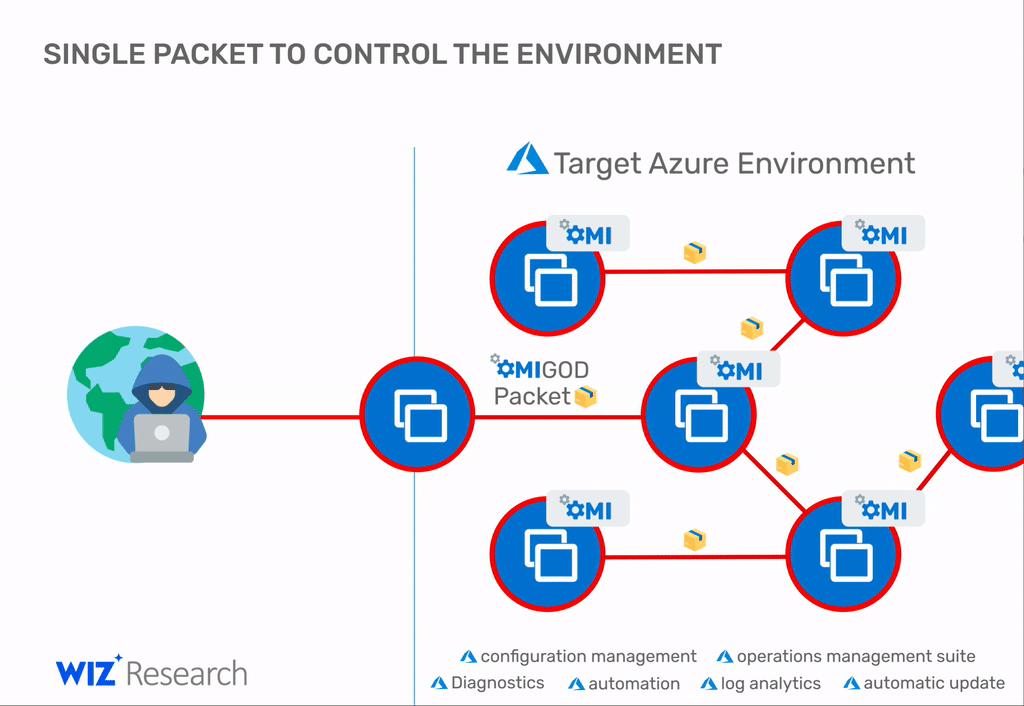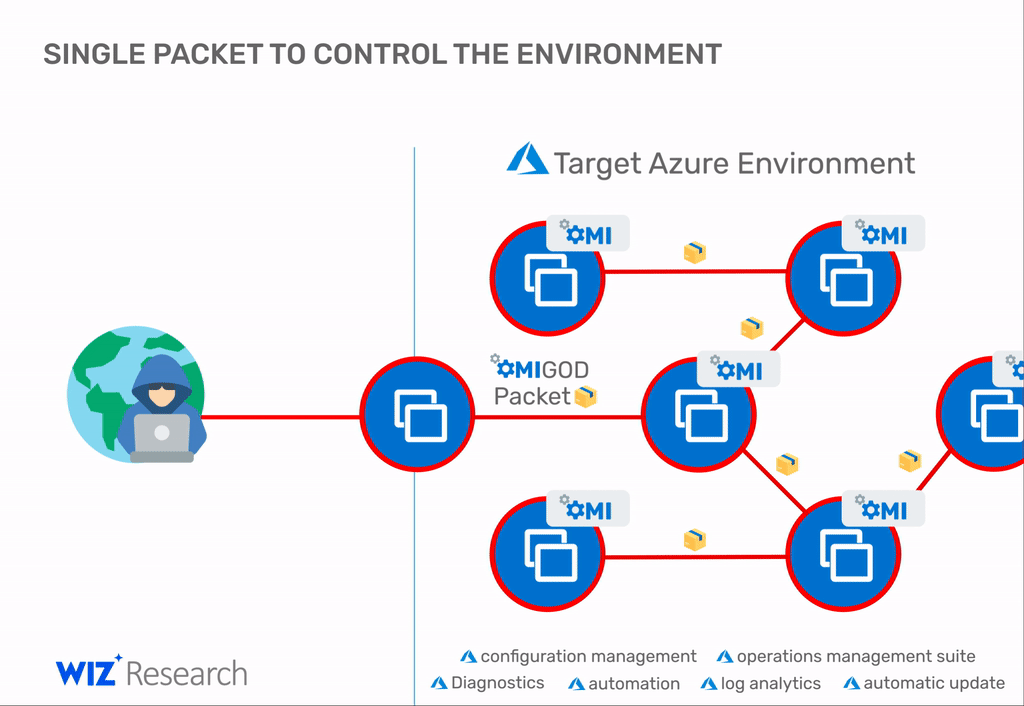
The Mirai botnet starts exploiting the recently disclosed OMIGOD vulnerability to compromise vulnerable systems exposed online. Threat actors behind a Mirai botnet starts exploiting a critical Azure OMIGOD vulnerability, tracked as CVE-2021-38647, a few days after Microsoft disclosed them. Recently released September 2021 Patch Tuesday security updates have addressed four severe vulnerabilities, collectively tracked as OMIGOD, in the Open Management […]






