


 Pierluigi Paganini
 August 27, 2021
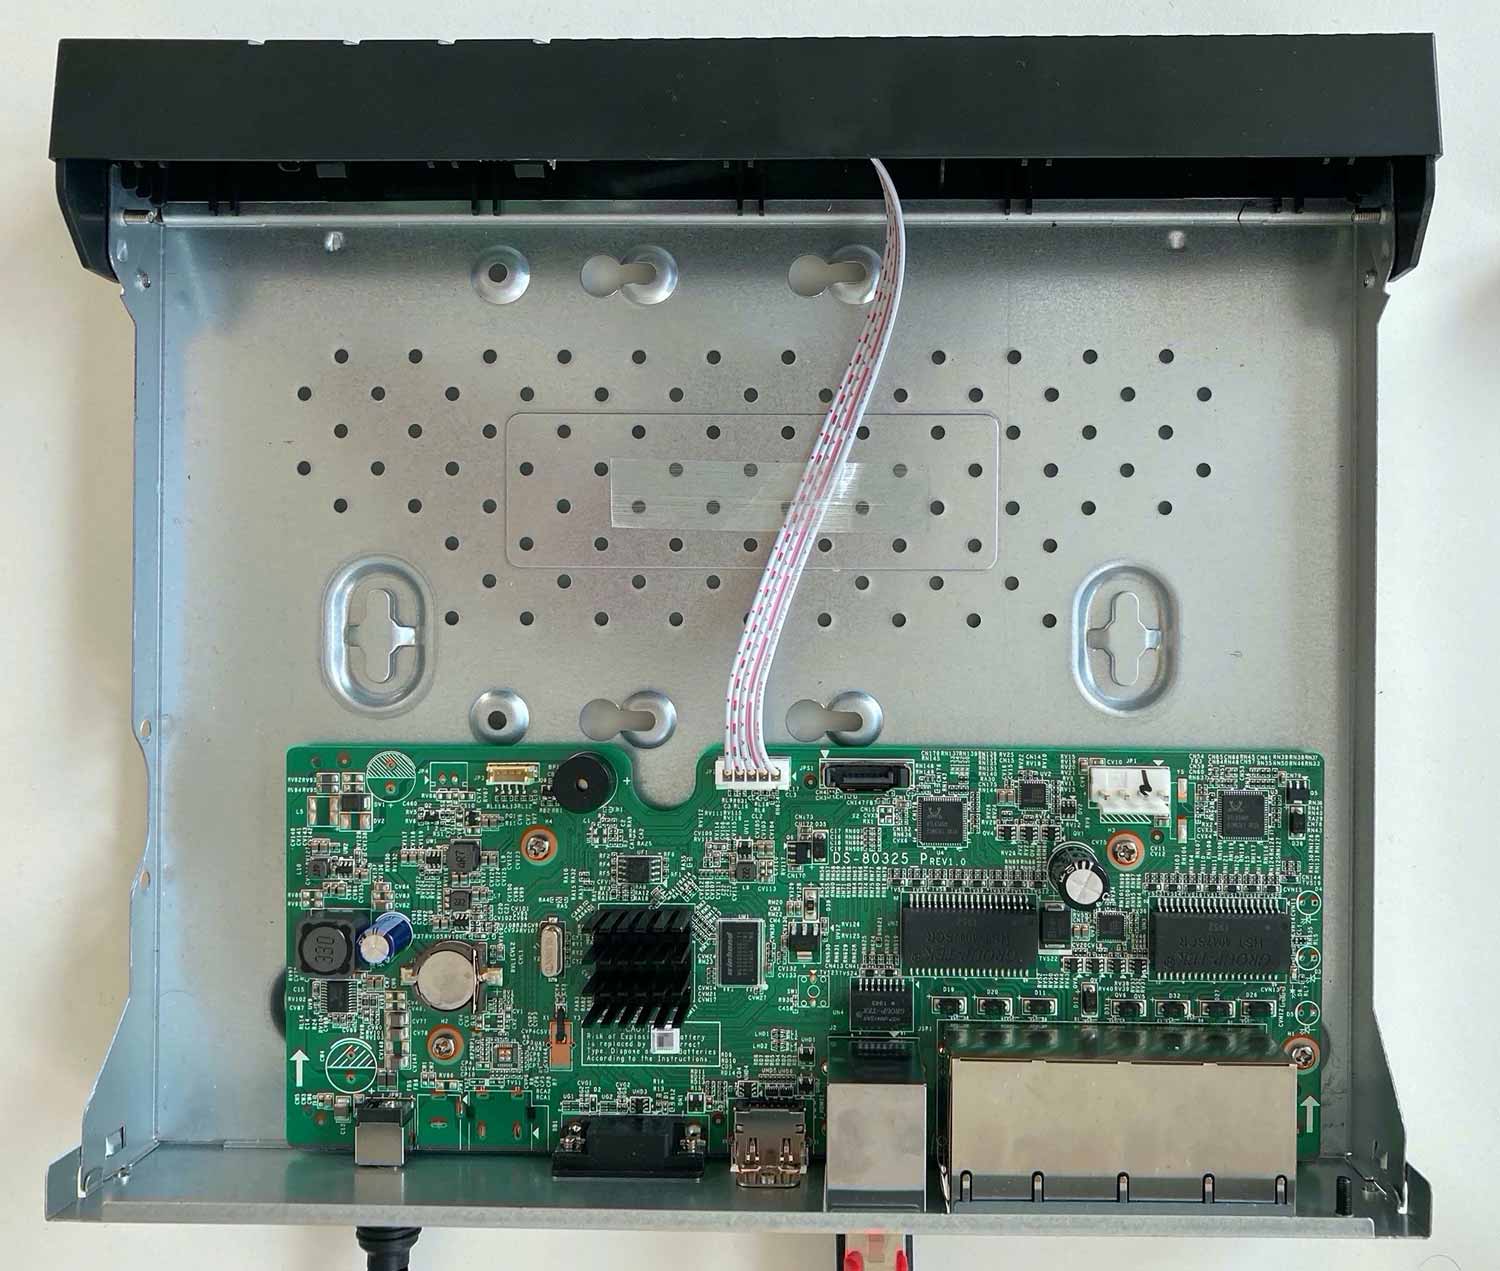
Researchers from Nozomi Networks discovered a critical vulnerability that can be exploited to hack a video surveillance product made by Annke. Researchers at industrial and IoT cybersecurity firm Nozomi Networks have discovered a critical flaw affecting a video surveillance product made by Annke, a popular manufacturer of surveillance systems and solutions. The vulnerability, tracked as […]
 Pierluigi Paganini
August 27, 2021
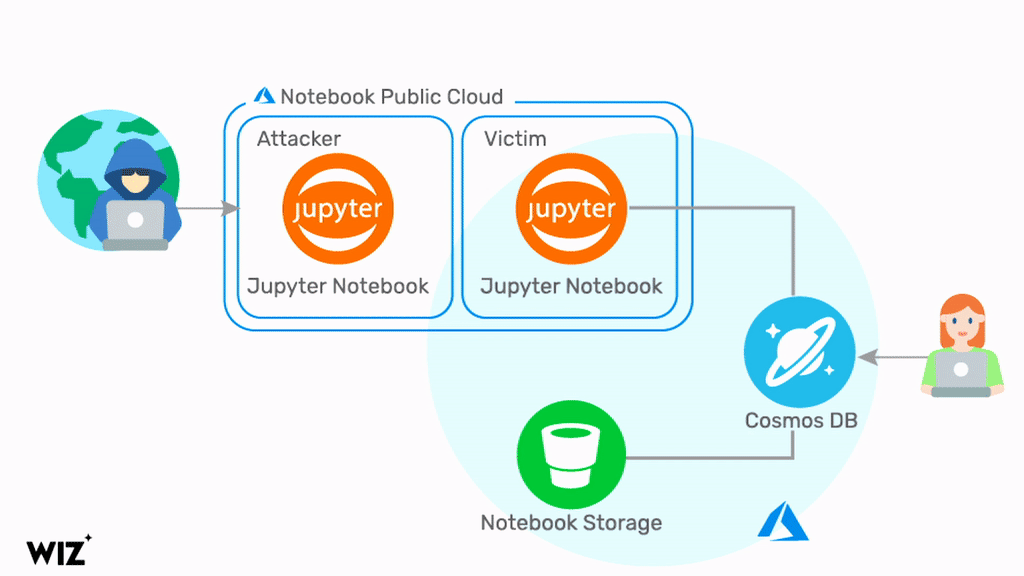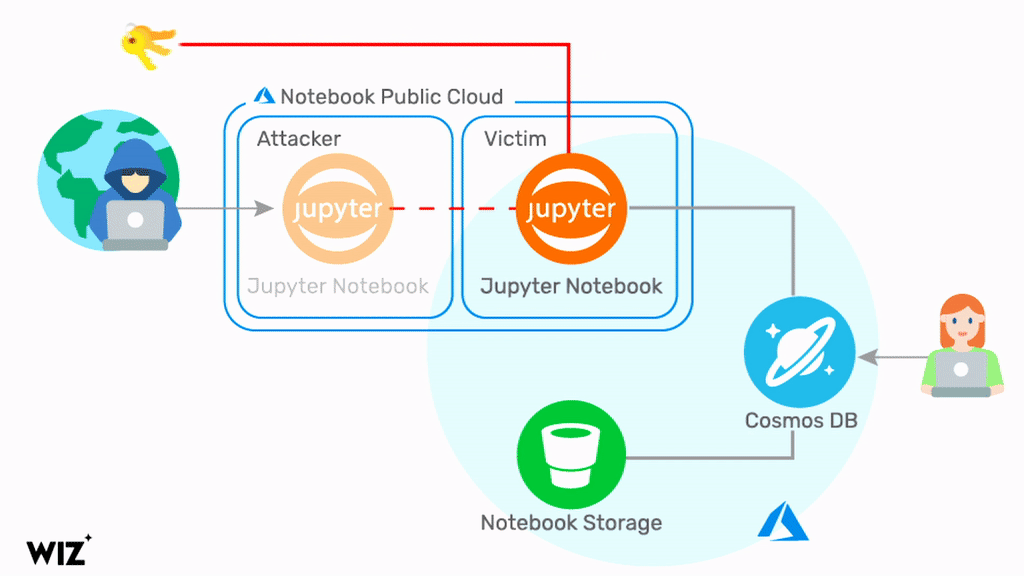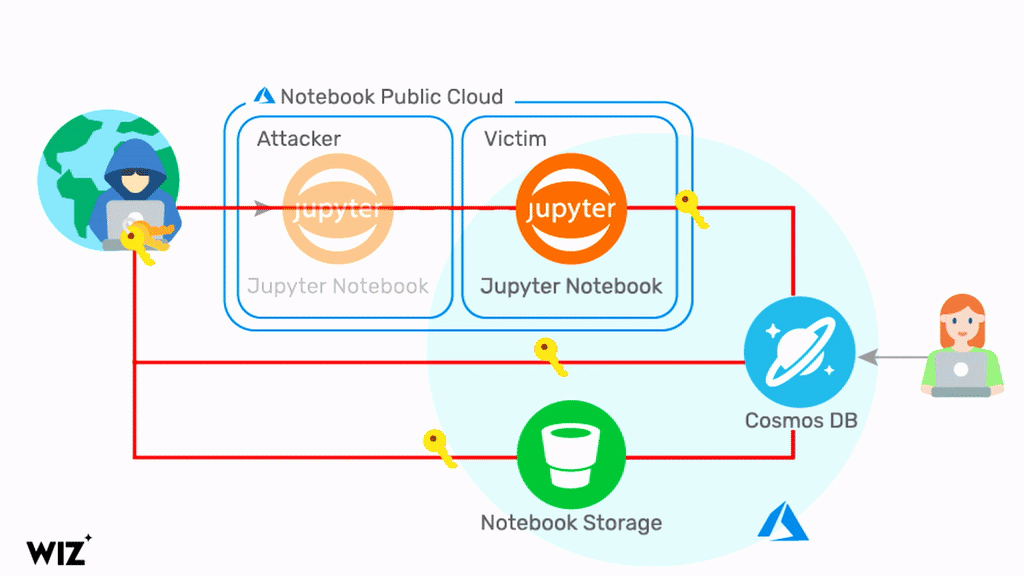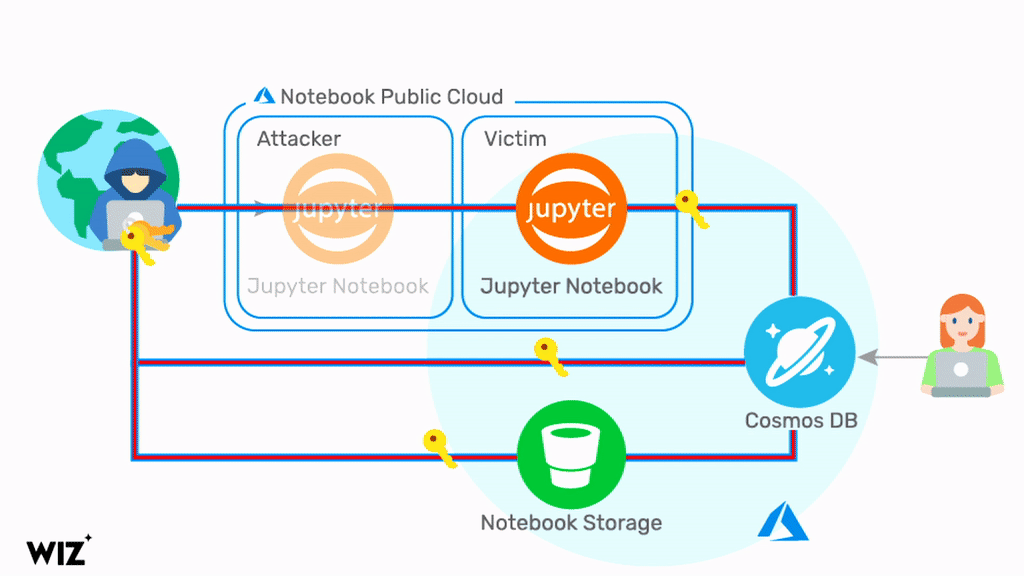
Microsoft has fixed a critical flaw in Cosmos DB that allowed any Azure user to remotely take over other users’ databases without any authorization. Researchers from Cloud security company Wiz disclosed technical details of a now-fixed Azure Cosmos database vulnerability, dubbed ChaosDB, that could have been potentially exploited by attackers to gain full admin access […]
 Pierluigi Paganini
August 27, 2021
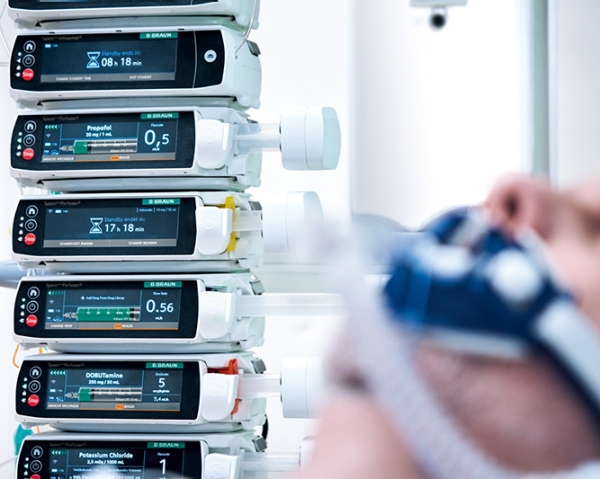
Researchers disclosed five vulnerabilities in B. Braun ‘s Infusomat Space Large Volume Pump and SpaceStation that could be remotely hacked. Cybersecurity researchers from McAfee disclosed five vulnerabilities in B. Braun’s Infusomat Space Large Volume Pump and SpaceStation that could be exploited by threat actors to alter medication doses. The flawed devices are uses in both […]
 Pierluigi Paganini
August 26, 2021
Software firm Kaseya addressed Kaseya Unitrends zero-day vulnerabilities that were reported by security researchers at the Dutch Institute for Vulnerability Disclosure (DIVD). Kaseya released security updates address server-side Kaseya Unitrends zero-day vulnerabilities that were reported by security researchers at the Dutch Institute for Vulnerability Disclosure (DIVD). Kaseya Unitrends is a cloud-based enterprise solution that provides affordable, […]
 Pierluigi Paganini
August 25, 2021
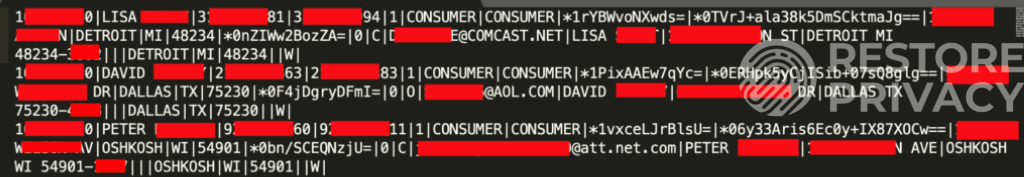
Threat actors claim to have a database containing private information on roughly 70 million AT&T customers, but the company denies any security breach. ShinyHunters group claims to have a database containing private information on roughly 70 million AT&T customers, but the company denies that they have been stolen from its systems. ShinyHunters is a popular […]
 Pierluigi Paganini
August 24, 2021
The OpenSSL Project patched a high-severity vulnerability, tracked as CVE-2021-3711, that can allow an attacker to change an application’s behavior or cause the app to crash. The OpenSSL Project released the OpenSSL 1.1.1l version that addresses a high-severity buffer overflow flaw, tracked as CVE-2021-3711, that could allow an attacker to change an application’s behavior or […]
 Pierluigi Paganini
August 24, 2021
Researchers warn that threat actors are actively exploiting Realtek SDK vulnerabilities since their technical details were publicly disclosed. Researchers from SAM Seamless Network warn that threat actors are actively exploiting Realtek SDK vulnerabilities since their technical details were publicly disclosed. Realtek published a security advisory on August 15 to warn customers about security updates to address vulnerabilities in its […]
 Pierluigi Paganini
August 23, 2021
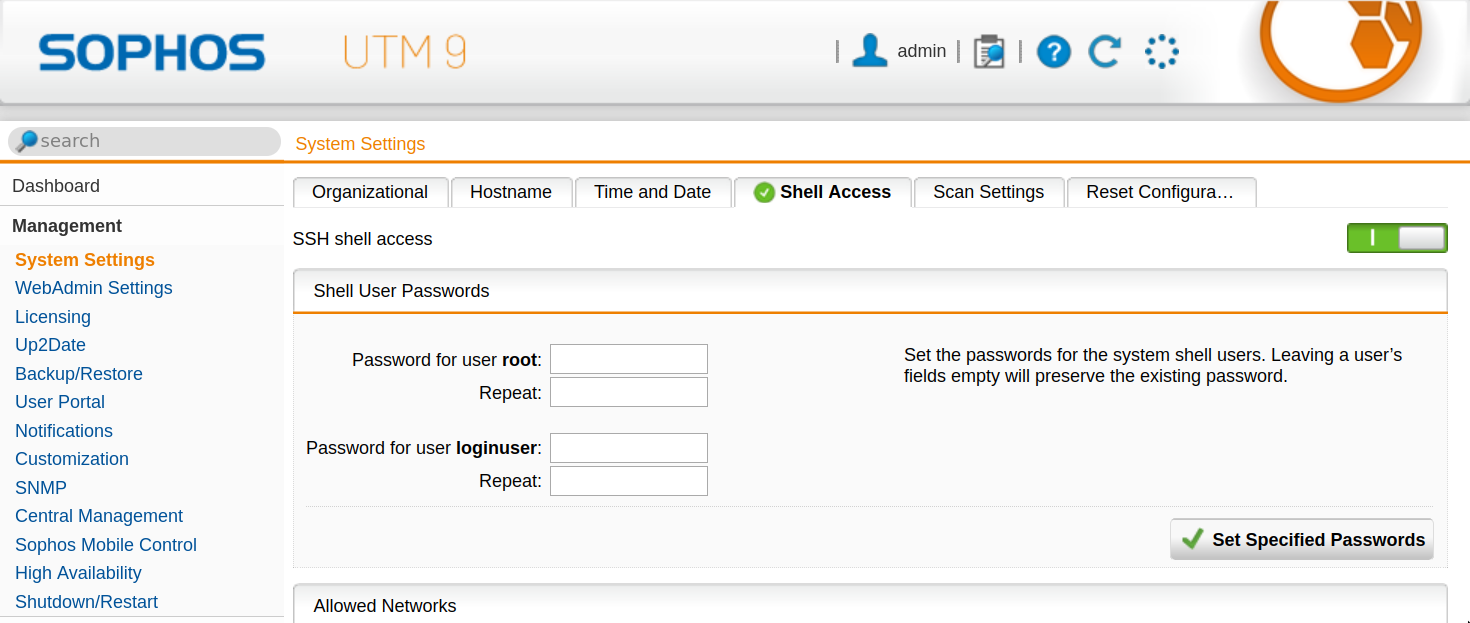
A researcher disclosed technical details of a critical remote code execution vulnerability, tracked as CVE-2020-25223, patched last year. In September, Sophos addressed a remote code execution vulnerability (CVE-2020-25223) in the WebAdmin of SG UTM that was reported via the company bug bounty program. At the time, the security vendor said that there was no evidence that […]
 Pierluigi Paganini
August 23, 2021
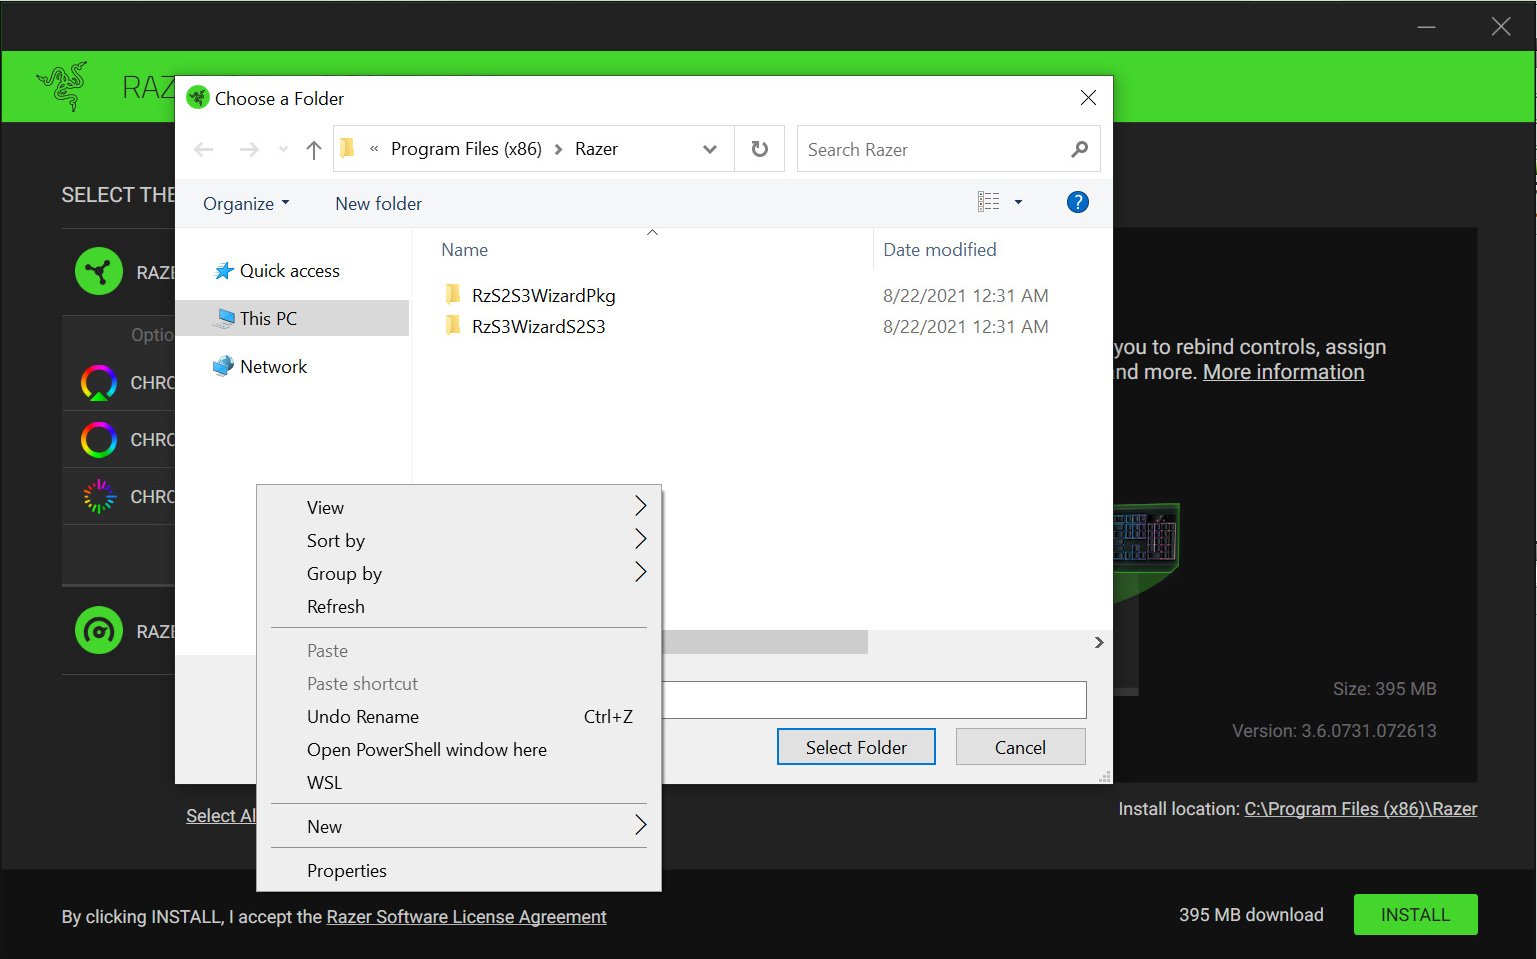
A zero-day vulnerability in Razer Synapse could allow threat actors to gain Windows admin privileges by plugging in a Razer mouse or keyboard. Razer is a popular manufacturer of computer accessories, including gaming mouses and keyboards. A local privilege escalation (LPE) zero-day flaw in Razer Synapse allows attackers to gain SYSTEM privileges on Windows systems […]
 Pierluigi Paganini
August 23, 2021
Health organization Memorial Health System was hit by a disruptive cyber attack that forced it to cancel surgeries and divert patients last week. The Memorial Health System announced that was hit by a disruptive cyber attack that forced it to suspend some of its operations. The organization operates the Marietta Memorial Hospital, the Selby General […]






