


 Pierluigi Paganini
 September 01, 2021
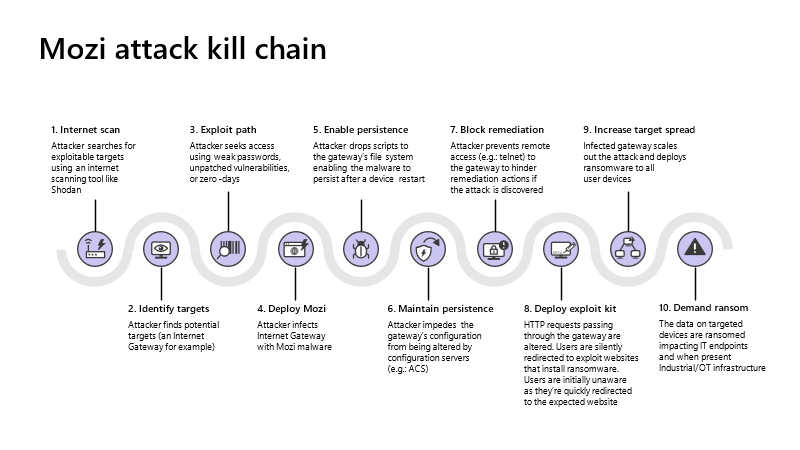
The Mozi botnet continues to spread despite the arrest of its alleged author and experts believe that it will run for many other years. Mozi is an IoT botnet that borrows the code from Mirai variants and the Gafgyt malware, it appeared on the threat landscape in late 2019. The Mozi botnet was spotted by security experts from 360 Netlab, at […]
 Pierluigi Paganini
September 01, 2021
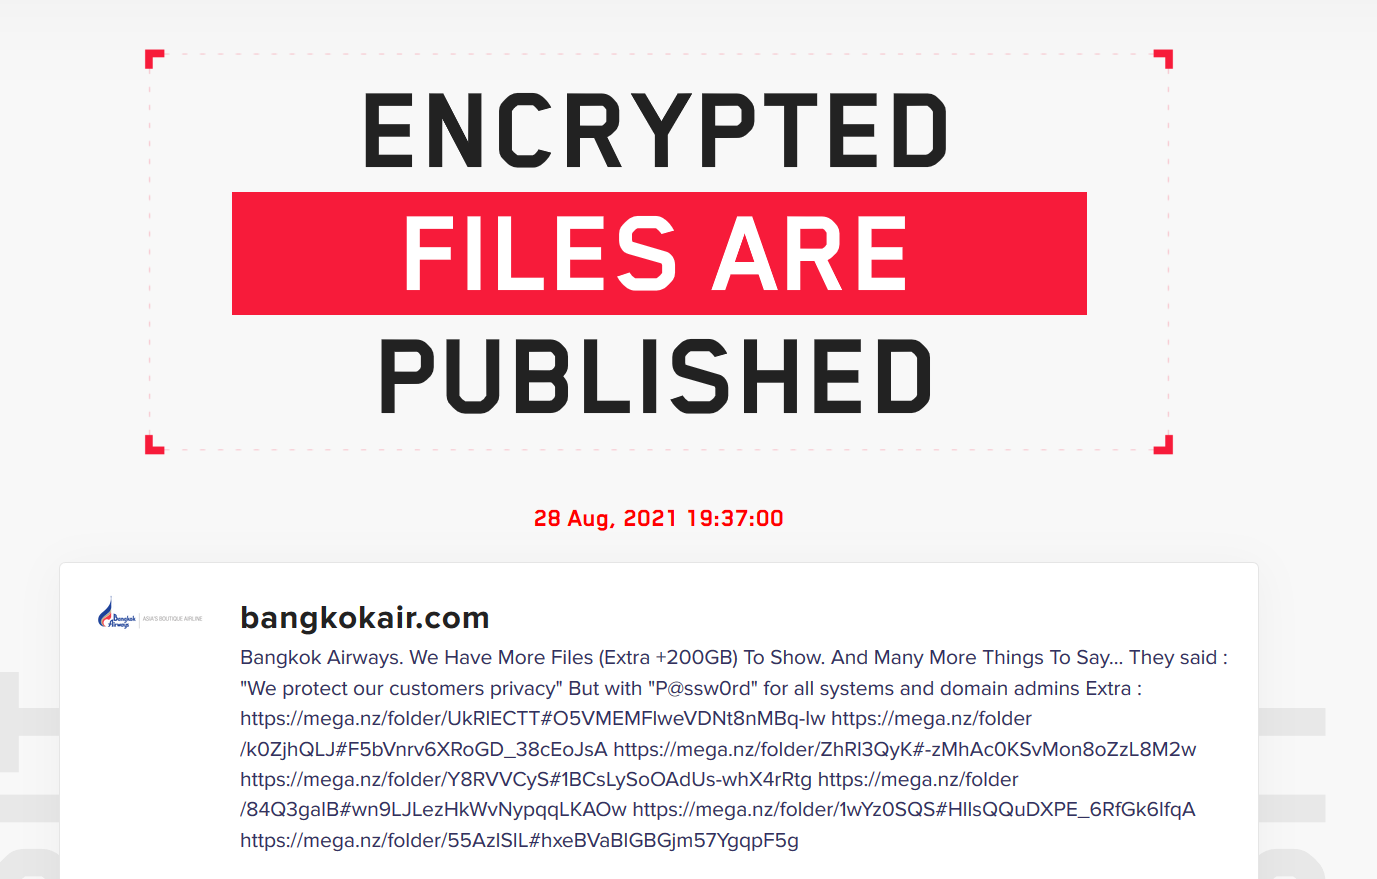
LockBit ransomware operators have breached Bangkok Airways, the airline confirmed it was the victim and discloses a data breach impacting its passengers. Bangkok Airways, a regional airline based in Bangkok, discloses a data breach as a result of a ransomware attack orchestrated by the LockBit ransomware operators. The ransomware gang had posted a message on their leak site […]
 Pierluigi Paganini
August 31, 2021
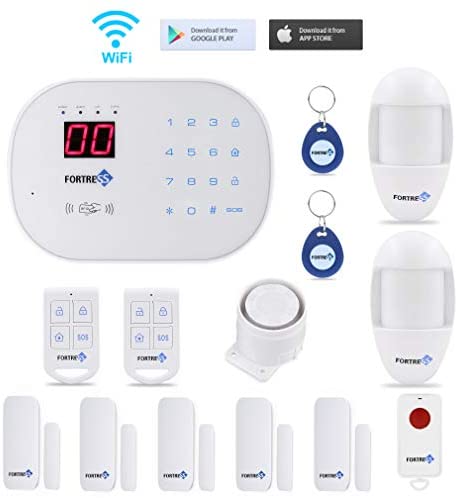
Rapid7 researchers discovered two flaws that can be exploited by attackers to remotely disable one of the home security systems offered by Fortress Security Store. Researchers at cybersecurity firm Rapid7 discovered two vulnerabilities that can be exploited by hackers to remotely disarm the Fortress S03 WiFi Security System manufactured by Fortress Security Store. The Fortress […]
 Pierluigi Paganini
August 31, 2021
Crooks have stolen more than $29 million in cryptocurrency assets from Cream Finance, a decentralized finance (DeFi) platform. Threat actors have stolen more than $29 million in cryptocurrency assets from Cream Finance, a decentralized finance (DeFi) platform. C.R.E.A.M. Finance is a decentralized lending protocol for individuals, institutions and protocols to access financial services. It promises […]
 Pierluigi Paganini
August 31, 2021
ProxyToken is a serious vulnerability in Microsoft Exchange Server that could allow unauthentication attackers to access emails from a target account. Technical details of a serious vulnerability in the Microsoft Exchange Server, dubbed ProxyToken (CVE-2021-33766), were publicly disclosed. The issue could be exploited by an unauthenticated attacker to access emails from a target account. An […]
 Pierluigi Paganini
August 30, 2021
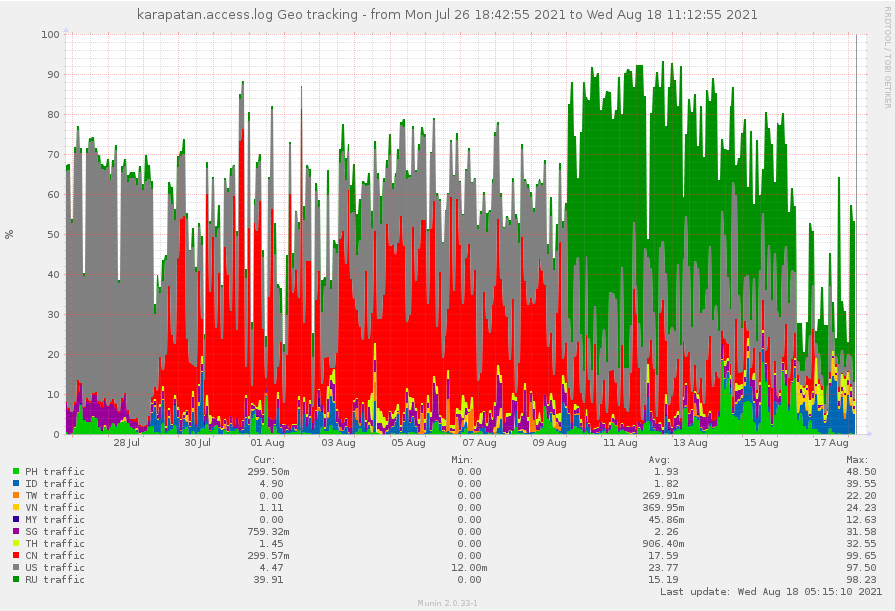
Who is behind the massive and prolonged Distributed Denial of Service (DDoS) attack that hit the Philippine human rights alliance Karapatan? The 25 days long DDoS attack against the website of Karapatan was launched by almost 30.000 IP addresses, whereas one third of the addresses originated from devices that there were not running “Open Proxies” or “Tor exits”. […]
 Pierluigi Paganini
August 30, 2021
The Boston Public Library was victim of a cyberattack that crippled its computer network, the library revealed in a statement Friday. The Boston Public Library announced on Friday that it was hit by a cyberattack that compromised its computer network. The affected systems were taken offline to prevent the threat from spreading. At the time […]
 Pierluigi Paganini
August 28, 2021
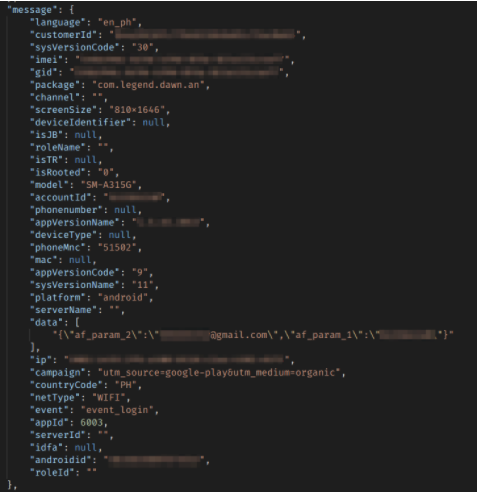
vpnMentor’s researchers reported that the Chinese mobile gaming company EskyFun suffered a data breach, over 1 million gamers impacted. vpnMentor’s researchers discovered that the Chinese mobile gaming company EskyFun suffered a data breach, information of over 1 million gamers were exposed on an unsecured server. EskyFun developed several Android games including Rainbow Story: Fantasy MMORPG, Adventure Story, […]
 Pierluigi Paganini
August 28, 2021
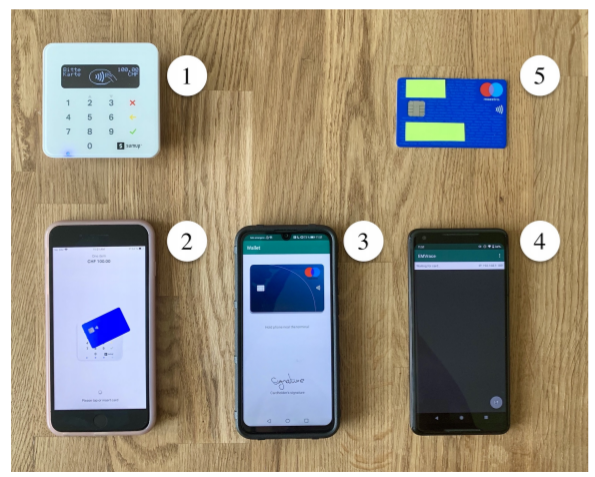
Boffins from the Swiss ETH Zurich university demonstrated PIN bypass attack on contactless cards from Mastercard and Maestro. A group of researchers from the Swiss ETH Zurich university has discovered a vulnerability that allowed them to bypass PIN codes on contactless cards from Mastercard and Maestro. Technically the researchers performed a Man-in-the-Middle (MitM) attack between […]
 Pierluigi Paganini
August 28, 2021
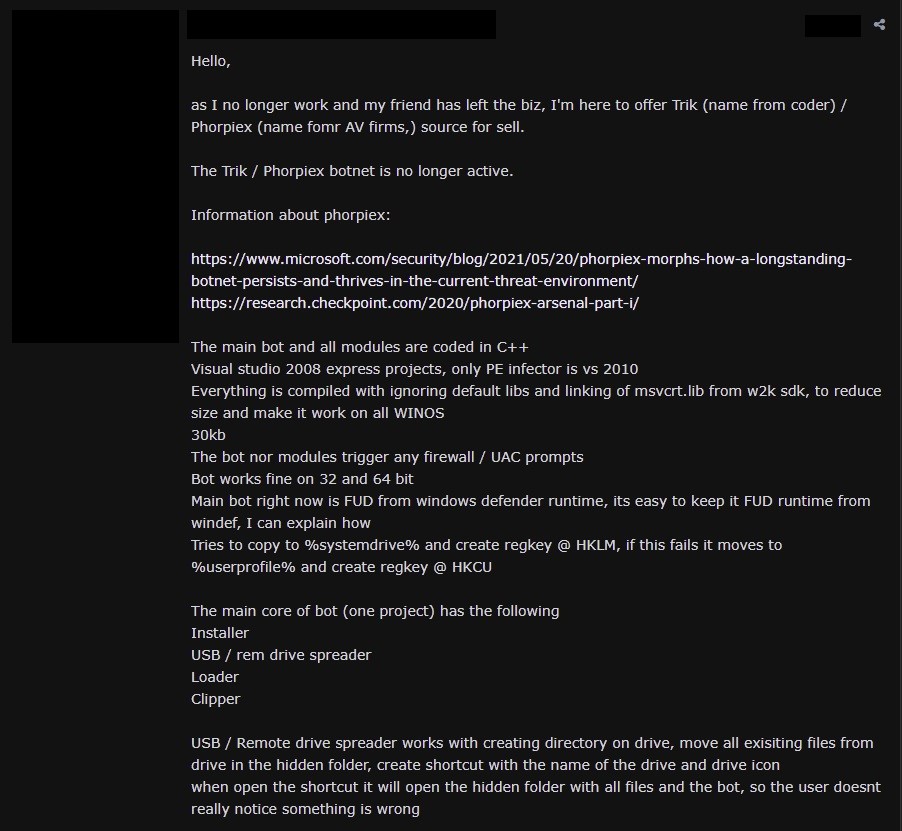
Crooks behind the Phorpiex botnet have shut down their operations and put the source code for sale on the dark web. The criminal organization behind the Phorpiex botnet have shut down their operations and put the source code of the bot for sale on a cybercrime forum in on a dark web. The news was […]






