


 Pierluigi Paganini
 August 16, 2021
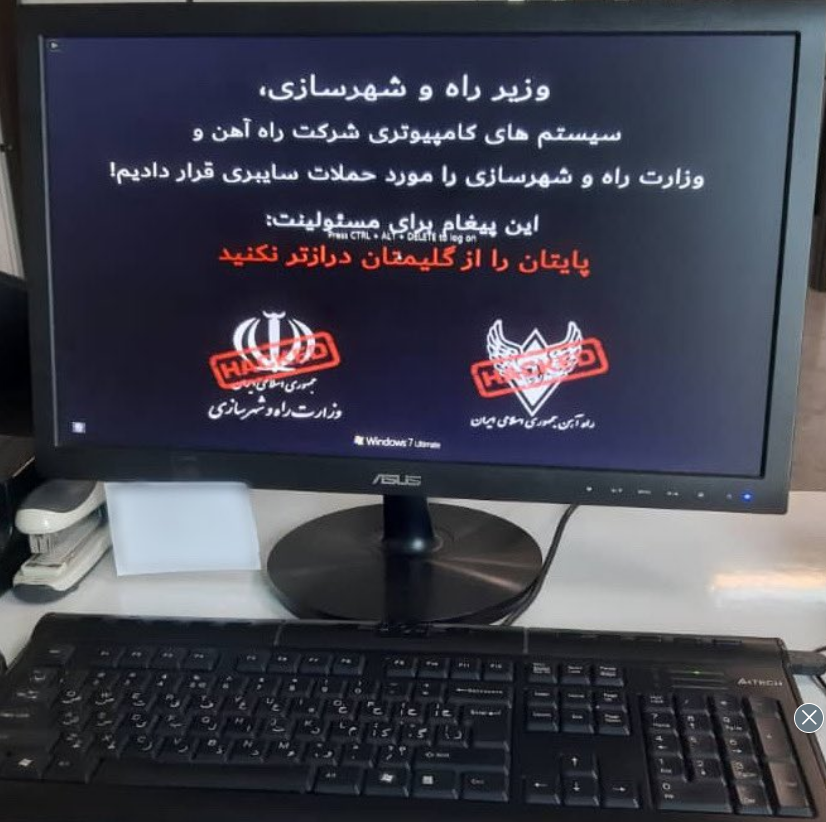
The recent attacks that targeted Iran’s transport ministry and national train system were conducted by a threat actor dubbed Indra. In July, Iran’s railroad system was hit by a cyberattack, threat actors published fake messages about delays or cancellations of the trains on display boards at stations across the country, the Fars news agency reported. The […]
 Pierluigi Paganini
August 16, 2021
The US FINRA warns US brokerage firms and brokers of an ongoing phishing campaign impersonating its representatives to steal sensitive info. The US Financial Industry Regulatory Authority (FINRA) is warning US brokerage firms and brokers of an ongoing phishing campaign. Threat actors are impersonating FINRA officials and are using the threat of penalties to trick victims recipients into providing […]
 Pierluigi Paganini
August 16, 2021
T-Mobile is investigating a possible data breach after a threat actor published a post on a forum claiming to be selling the personal data of its customers. New problems for T-Mobile, the company is investigating a possible data breach after that a threat actor has published a post on a hacking forum claiming to be […]
Pierluigi Paganini
August 15, 2021
The Glowworm attack leverages optical emanations from a device’s power indicator LED to recover sounds from connected peripherals and spy on electronic conversations. Boffins from the Ben-Gurion University of the Negev devised a new attack technique, dubbed the “Glowworm attack,” that leverages optical emanations from a device’s power indicator LED to recover sounds from connected […]
 Pierluigi Paganini
August 14, 2021
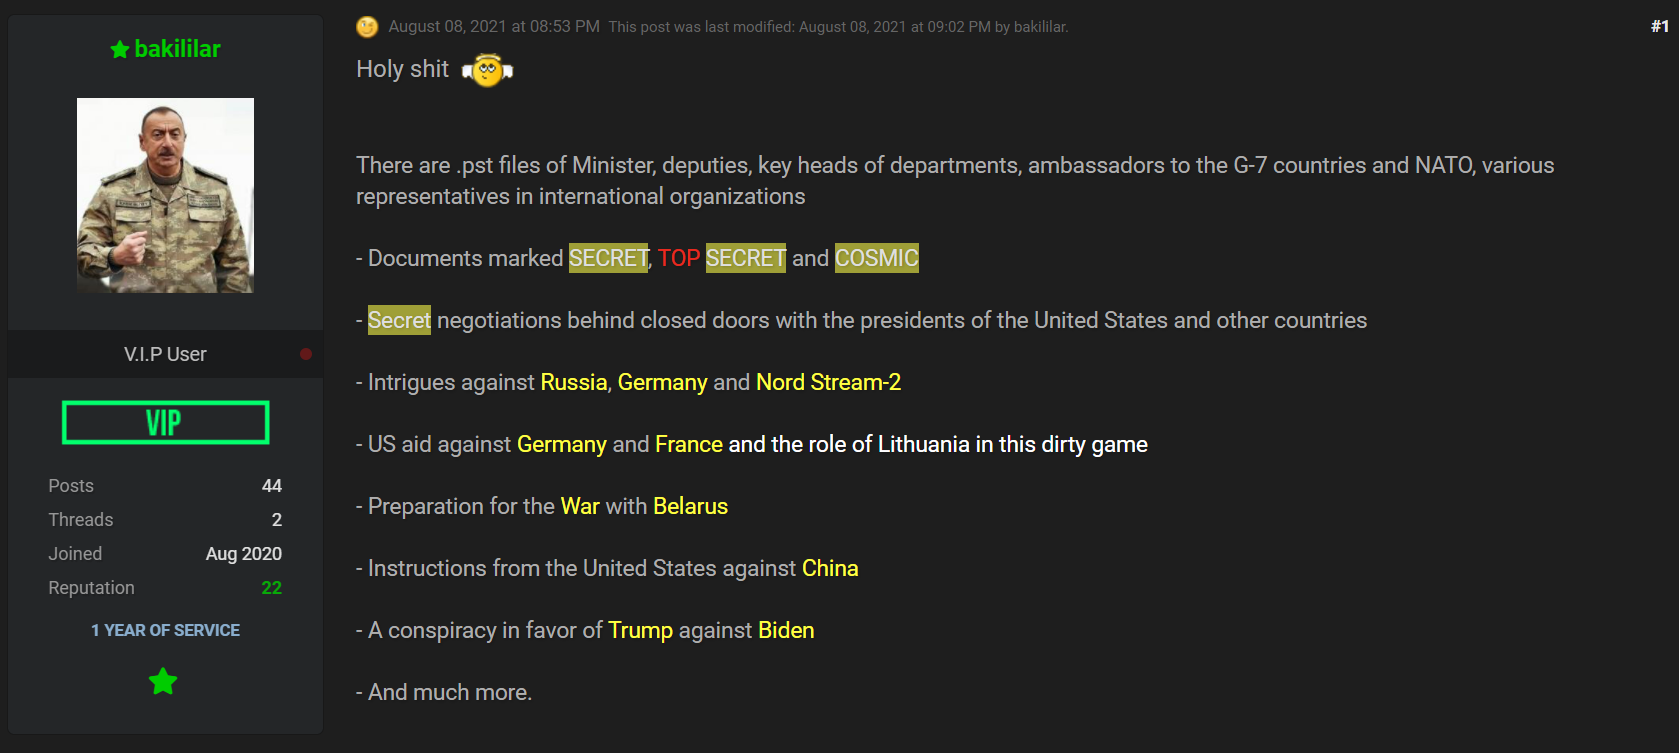
Emails allegedly stolen from the Lithuanian Ministry of Foreign Affairs are available for sale in a cybercrime forum, some emails include high-sensitive info. An archive containing 1.6 million emails containing highly sensitive messages allegedly stolen from the Lithuanian Ministry of Foreign Affairs is available for sale on the RaidForums hacking forum. The ad doesn’t include […]
 Pierluigi Paganini
August 14, 2021
A security expert devised a method to retrieve a user’s Microsoft Azure credentials in plaintext from Microsoft’s new Windows 365 Cloud PC service using Mimikatz. Benjamin Delpy, the popular security researcher and author of the Mimikatz tool, has devised a method to retrieve a user’s Microsoft Azure credentials in plaintext from Microsoft’s new Windows 365 […]
 Pierluigi Paganini
August 13, 2021
Another ransomware gang, the Vice Society ransomware operators, is using Windows print spooler PrintNightmare exploits in its attacks. The Vice Society ransomware operators are actively exploiting Windows print spooler PrintNightmare vulnerability in their attacks against Windows servers. The PrintNightmare flaws (tracked as (CVE-2021-1675, CVE-2021-34527, and CVE-2021-36958) reside in the Windows Print Spooler service, print drivers, and the Windows Point and […]
 Pierluigi Paganini
August 13, 2021
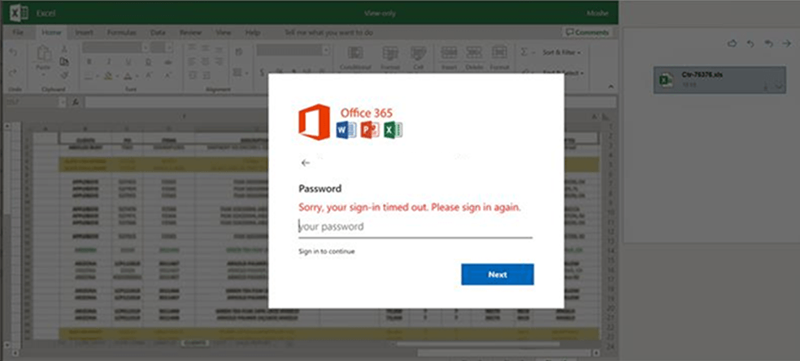
Microsoft warns of a long-running spear-phishing campaign that has targeted Office 365 customers in multiple attacks since July 2020. Microsoft revealed that a year-long spear-phishing campaign has targeted Office 365 customers in multiple attacks starting with July 2020. The attackers used invoice-themed XLS.HTML attachments, Microsoft reported that they changed obfuscation and encryption mechanisms every 37 […]
 Pierluigi Paganini
August 12, 2021
Security firms Trend Micro is warning its customers of attacks exploiting zero-day vulnerabilities in its Apex One and Apex One as a Service products. On July 28, Trend Micro released security patches for multiple incorrect permission assignment privilege escalation, incorrect permission preservation authentication bypass, arbitrary file upload, and local privilege escalation vulnerabilities in Apex One […]
 Pierluigi Paganini
August 12, 2021
Microsoft is warning of another zero-day Windows print spooler vulnerability, tracked as CVE-2021-36958, that could allow local attackers to gain SYSTEM privileges. Microsoft published a security advisory to warn its customers of another remote code execution zero-vulnerability, tracked as CVE-2021-36958, that resides in the Windows Print Spooler component. A local attacker could exploit the vulnerability […]






