 Pierluigi Paganini
 April 13, 2018
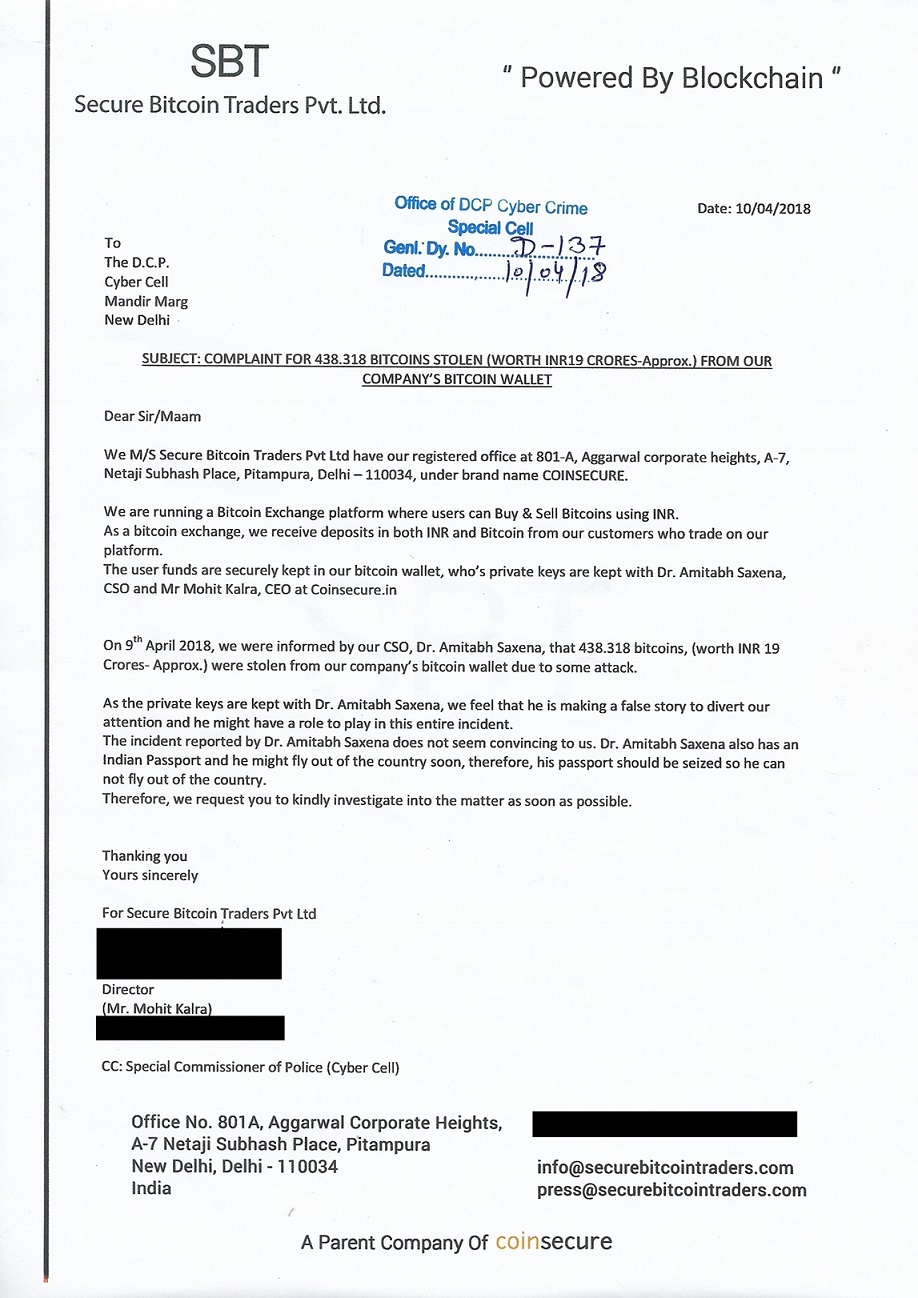
Cryptocurrency exchange Coinsecure, India’s second exchange, announced that it has suffered a severe issue, 438 bitcoin, $3,3 million worth of bitcoin Cryptocurrency exchange Coinsecure, India’s second exchange, announced that it has suffered a severe issue, 438 bitcoin, $3,3 million worth of bitcoin, have been transferred from the main wallet to an account that is not under their control. CEO […]
 Pierluigi Paganini
April 12, 2018
The Iran-linked APT33 group continues to be very active, security researchers at Cyberbit have discovered an Early Bird code injection technique used by the group. The Early Bird method was used to inject the TurnedUp malware into the infected systems evading security solutions. The technique allows injecting a malicious code into a legitimate process, it allows execution […]
 Pierluigi Paganini
April 12, 2018
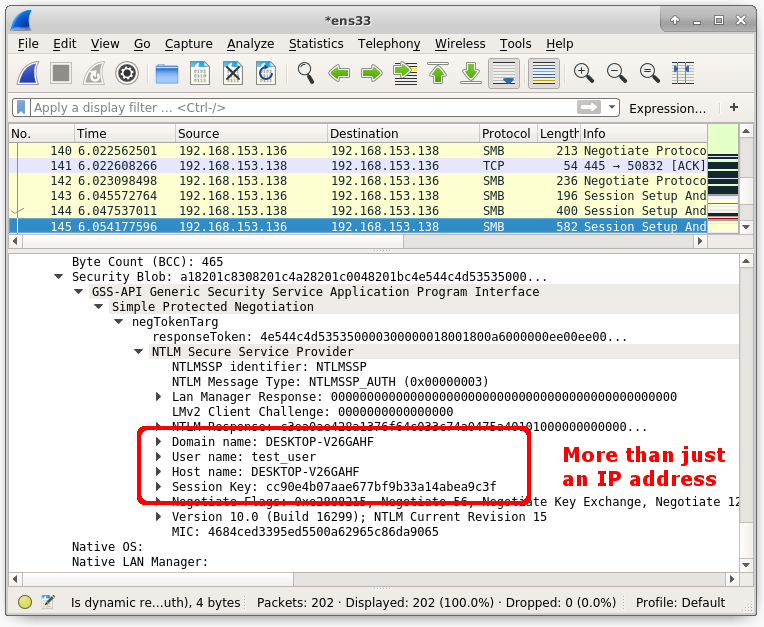
An 18-month-old CVE-2018-0950 vulnerability in Microsoft Outlook could be exploited by hackers to steal the Windows Password. Almost 18 months ago, the security researcher Will Dormann of the CERT Coordination Center (CERT/CC) has found a severe vulnerability in Microsoft Outlook (CVE-2018-0950), time is passed but Microsoft partially addressed it with the last Patch Tuesday updates. […]
 Pierluigi Paganini
April 12, 2018
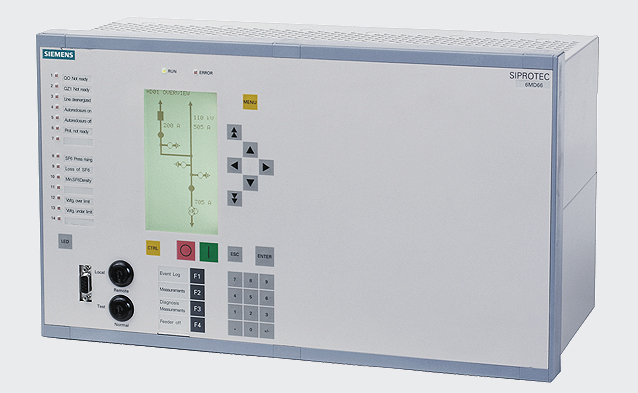
The ICS-CERT and Siemens published are warning organizations of security flaws in Siemens devices (SIPROTEC 4, SIPROTEC Compact, and Reyrolle devices) that could be exploited by hackers to target electrical substations. “Successful exploitation of these vulnerabilities could allow an attacker to upload a modified device configuration that could overwrite access authorization passwords, or allow an […]
 Pierluigi Paganini
April 11, 2018
Microsoft has released April Patch Tuesday security updates that address 66 vulnerabilities, five of them could be exploited by an attacker to compromise a PC by just tricking the victims into visiting a website or opening a specifically crafted file. Hackers can compromise your computer just visiting a malicious website or clicking a malicious link. […]
 Pierluigi Paganini
April 10, 2018
Some of the most popular music VEVO videos on YouTube, including the world’s most popular video ‘Despacito’ has been hacked by a duo calling themselves Prosox and Kuroi’SH. Some of the most popular music videos on YouTube, including the world’s most popular YouTube video ‘Despacito’ has been hacked. Popular videos of pop stars like Shakira, Drake, Selena Gomez, […]
 Pierluigi Paganini
April 10, 2018
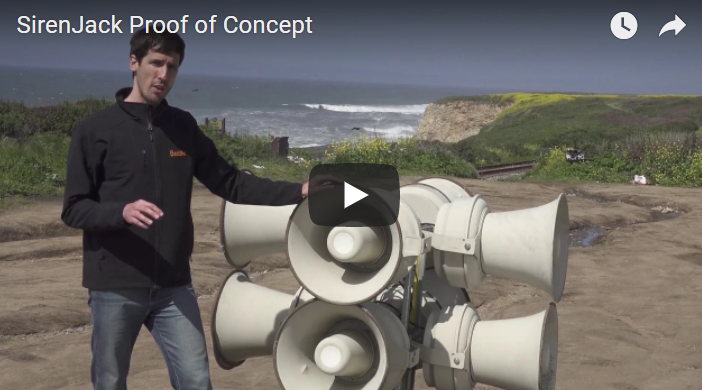
“SirenJack is a vulnerability found in ATI Systems’ emergency alert systems that can be exploited via radio frequencies (RF) to activate sirens and trigger false alarms.” Security experts at Bastille have devised a new technique, dubbed SirenJack to remotely hack emergency warning systems. Emergency warning systems are used worldwide to alert the public of emergency situations […]
 Pierluigi Paganini
April 10, 2018
A cyber attack shut down the entire government infrastructure of the Caribbean island Sint Maarten. public services were interrupted. A massive cyber attack took offline the entire government infrastructure of the Caribbean island Sint Maarten. it is a constituent country of the Kingdom of the Netherlands. Government building remained closed after the attack. “The Ministry of General Affairs hereby informs […]
 Pierluigi Paganini
April 10, 2018
Microsoft Office documents created with the exploit builder kit dubbed ThreadKit now include the code for CVE-2018-4878 flaw exploitation. At the end of March, security experts at Proofpoint discovered a Microsoft Office document exploit builder kit dubbed ThreadKit that has been used to spread a variety of malware, including banking Trojans and RATs (i.e. Trickbot, Chthonic, FormBook and Loki Bot). […]
 Pierluigi Paganini
April 10, 2018
Researchers have discovered several vulnerabilities in the Linux command line tool Beep, some experts suggest to remove the utility from distros. An unnamed security researcher has found several vulnerabilities in the Linux command line tool Beep, including a severe flaw introduced by a patch for a privilege escalation vulnerability. Beep is a small open source utility […]
Security / October 08, 2026