 Pierluigi Paganini
 May 10, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter CloudZ RAT potentially steals OTP messages using Pheno plugin Backdoored PyTorch Lightning package drops credential stealer A rigged game: ScarCruft compromises gaming platform in a supply-chain attack Muddying the Tracks: The State-Sponsored Shadow Behind […]
 Pierluigi Paganini
May 09, 2026
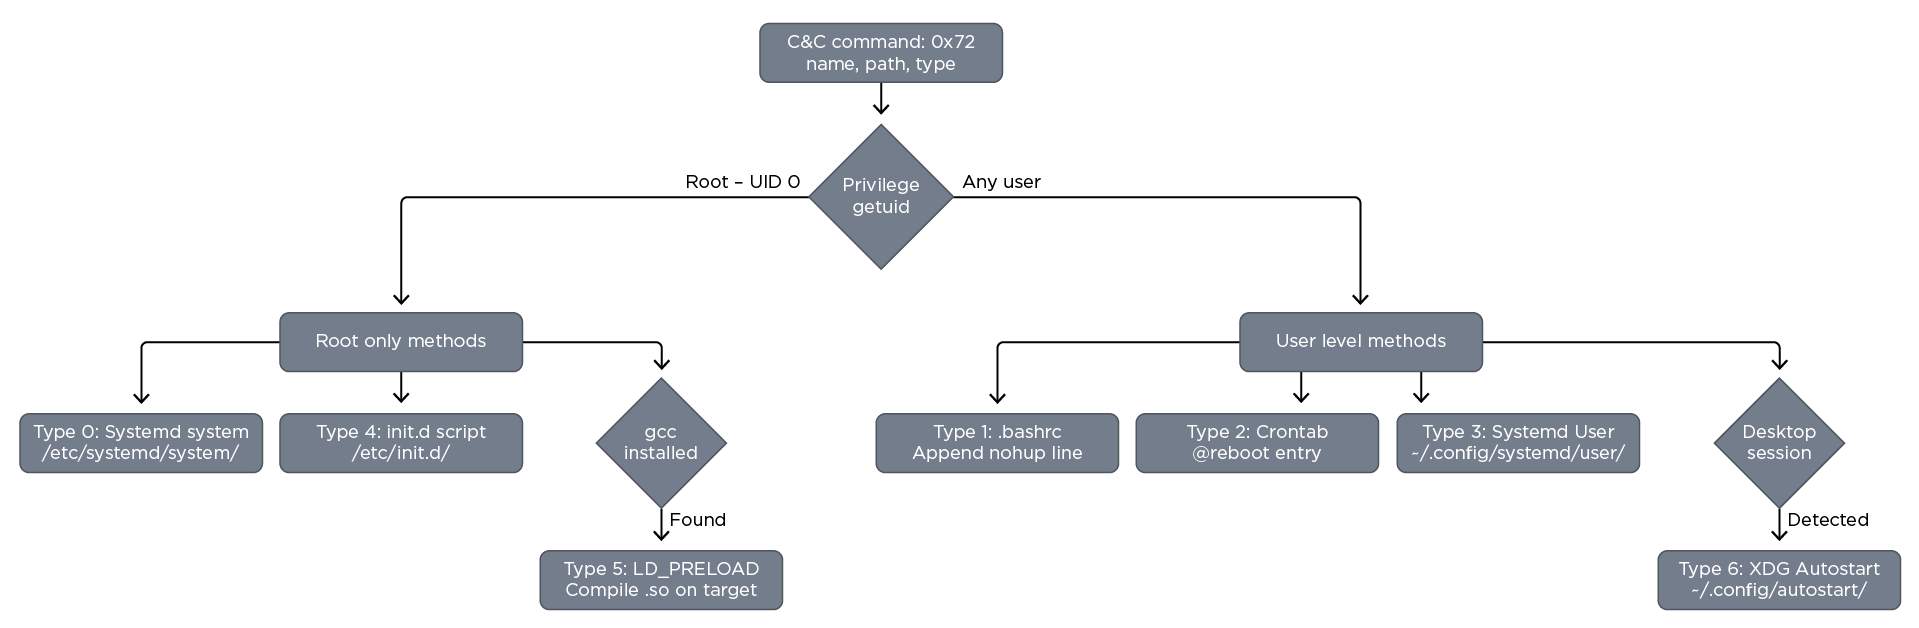
Researchers uncovered QLNX, a Linux RAT targeting developers to steal credentials, log keystrokes, monitor systems, and enable remote access. Security researchers discovered a previously undocumented Linux malware called Quasar Linux RAT (QLNX) that targets developers and DevOps environments. The malicious code can steal credentials, log keystrokes, manipulate files, monitor clipboard activity, and create network tunnels […]
 Pierluigi Paganini
May 08, 2026
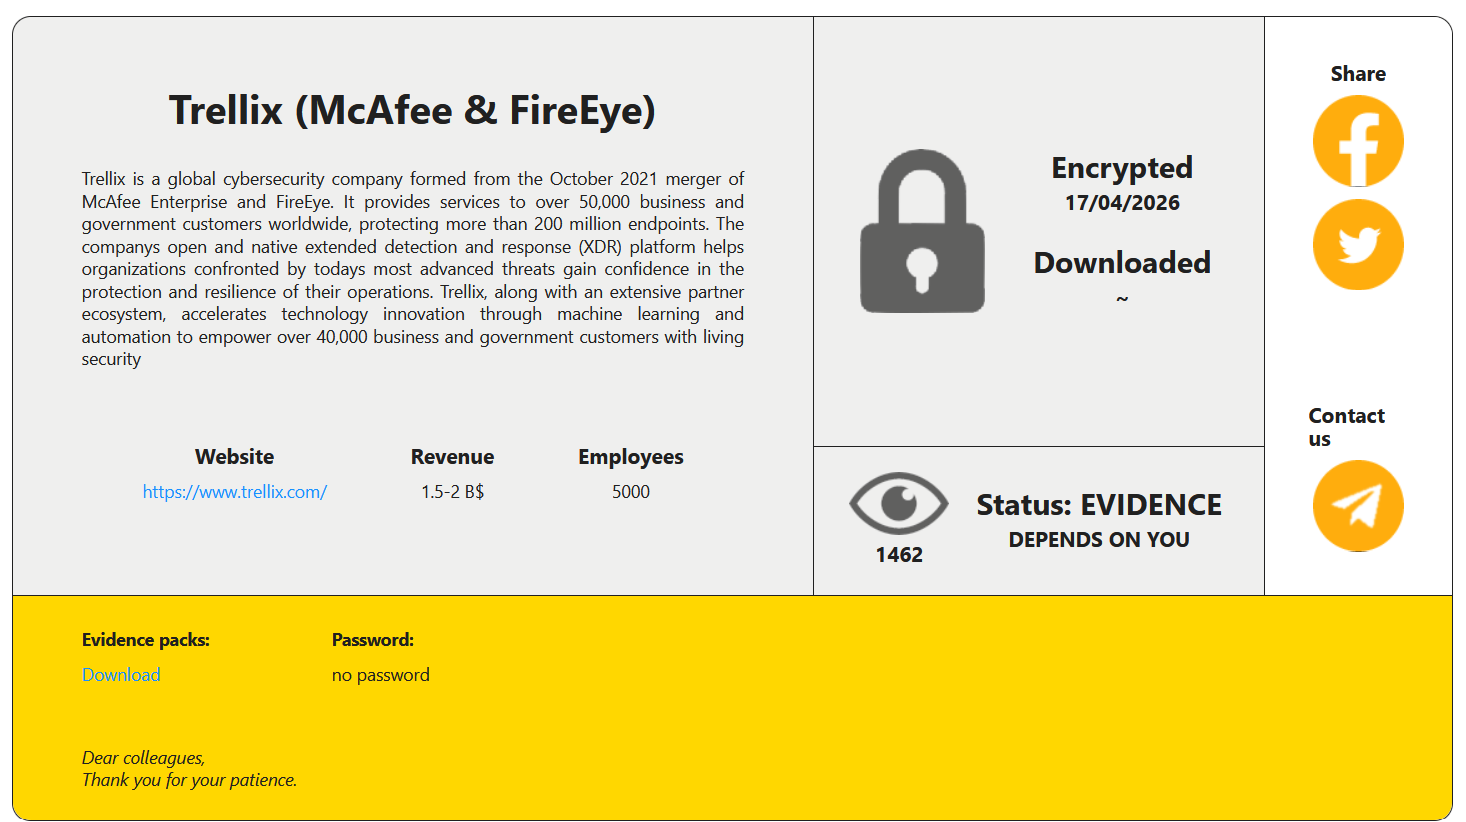
RansomHouse claimed responsibility for the Trellix breach, adding the security firm to its Tor data leak site and sharing screenshots of internal systems. The RansomHouse ransomware group has claimed responsibility for the recent cyberattack on cybersecurity firm Trellix. To support its claims, the gang published screenshots allegedly showing access to internal Trellix services. In early […]
 Pierluigi Paganini
May 07, 2026
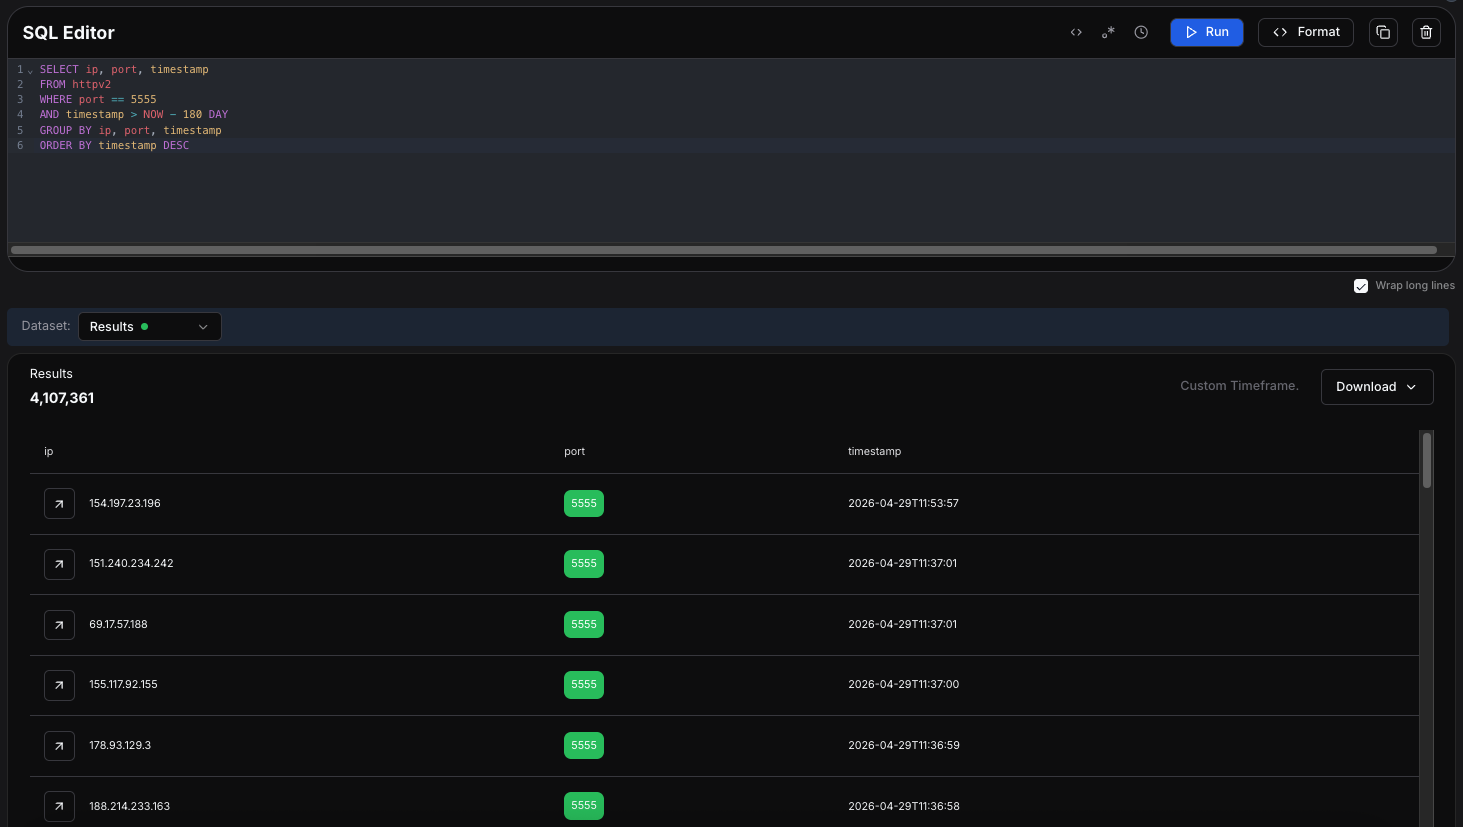
A new Mirai‑based botnet, xlabs_v1, hijacks ADB‑exposed IoT devices for powerful DDoS attacks, with 21 flooding methods and DDoS‑for‑hire use. A new Mirai‑derived botnet called xlabs_v1 is hijacking internet‑exposed devices running Android Debug Bridge (ADB) and using them for large‑scale DDoS attacks. Hunt.io discovered the bot on an unsecured server, it includes 21 flood techniques […]
 Pierluigi Paganini
May 06, 2026
Iran-linked APT MuddyWater used ransomware-style tactics to mask espionage, combining phishing, credential theft, data exfiltration, and extortion without encryption. A newly discovered cyber intrusion attributed to the Iran-linked APT MuddyWater (aka SeedWorm, TEMP.Zagros, Mango Sandstorm, TA450, and Static Kitten) reveals how state-sponsored attackers are increasingly leveraging ransomware tactics to disguise espionage operations. The campaign, uncovered by security researchers at Rapid7, blended […]
 Pierluigi Paganini
May 06, 2026
A malicious PyTorch Lightning update (v2.6.3) on PyPI spread briefly, stealing credentials and raising major concerns about AI supply chain security. A malicious update of the PyTorch Lightning library exposed developers to credential theft and remote compromise. Attackers uploaded version 2.6.3 to the Python Package Index (PyPI), where it spread among developers before maintainers removed […]
 Pierluigi Paganini
May 05, 2026
Deniss Zolotarjovs was sentenced to 8.5 years in the U.S. after pleading guilty to money laundering and fraud tied to ransomware. Deniss Zolotarjovs, a Latvian national linked to the Karakurt ransomware gang, has been sentenced to 8.5 years in U.S. prison, marking a significant step in efforts to combat global ransomware operations. “A Latvian national […]
Pierluigi Paganini
May 03, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter fast16 | Mystery ShadowBrokers Reference Reveals High-Precision Software Sabotage 5 Years Before Stuxnet 73 Open VSX Sleeper Extensions Linked to GlassWorm Show New Malware Activations An alarm clock you can’t ignore: How CapFix attacks […]
 Pierluigi Paganini
May 02, 2026
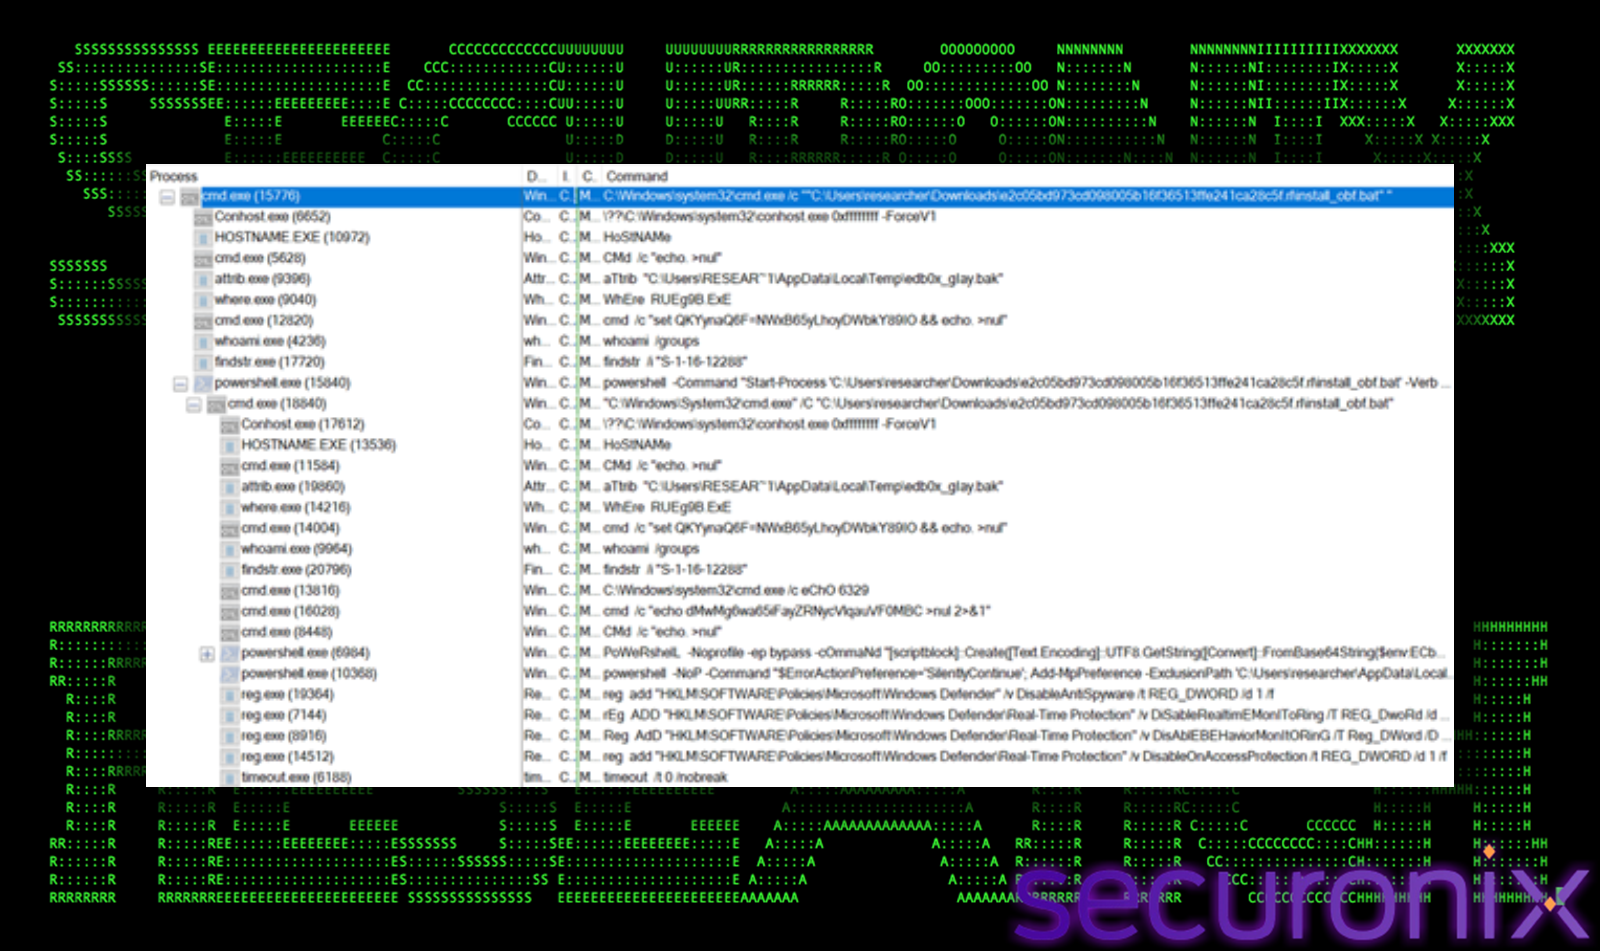
Deep#Door hides a Python RAT inside a batch file, kills Windows defenses, survives via multiple persistence methods, and exfiltrates data through a public TCP tunnel. Security researchers at Securonix uncovered a sophisticated malware campaign called Deep#Door. Threat actors employed a stealthy Python-based backdoor that uses a surprisingly simple delivery method to achieve deep, persistent access […]
 Pierluigi Paganini
April 28, 2026
Osservatorio Nessuno uncovered Morpheus spyware spreading via fake Android apps to steal data, highlighting rising covert surveillance tools. The non-partisan, non-religious, nonprofit organization Osservatorio Nessuno exposed a new spyware called Morpheus, distributed through fake Android apps posing as updates. Once installed, it can steal extensive data from the infected devices. The report shows strong demand […]

Security / September 20, 2026