 Pierluigi Paganini
 August 21, 2026
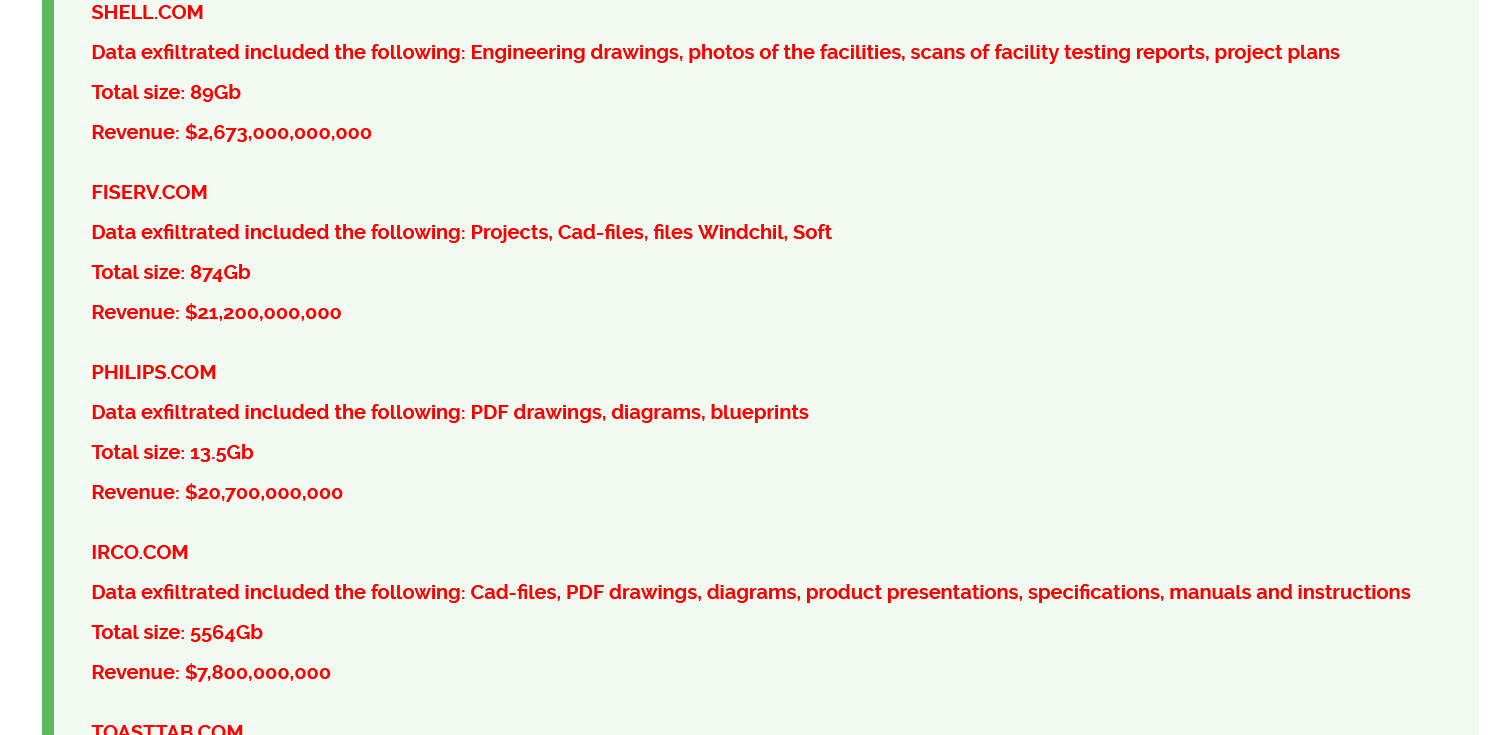
Cl0p claims over 40 organizations fell victim to attacks exploiting a PTC Windchill and FlexPLM vulnerability. Cl0p is using a familiar strategy again: exploit one flaw in enterprise software to attack many companies, then publish the victims’ names if they refuse to pay. The group claims it has targeted more than 40 organizations through a […]
 Pierluigi Paganini
August 20, 2026
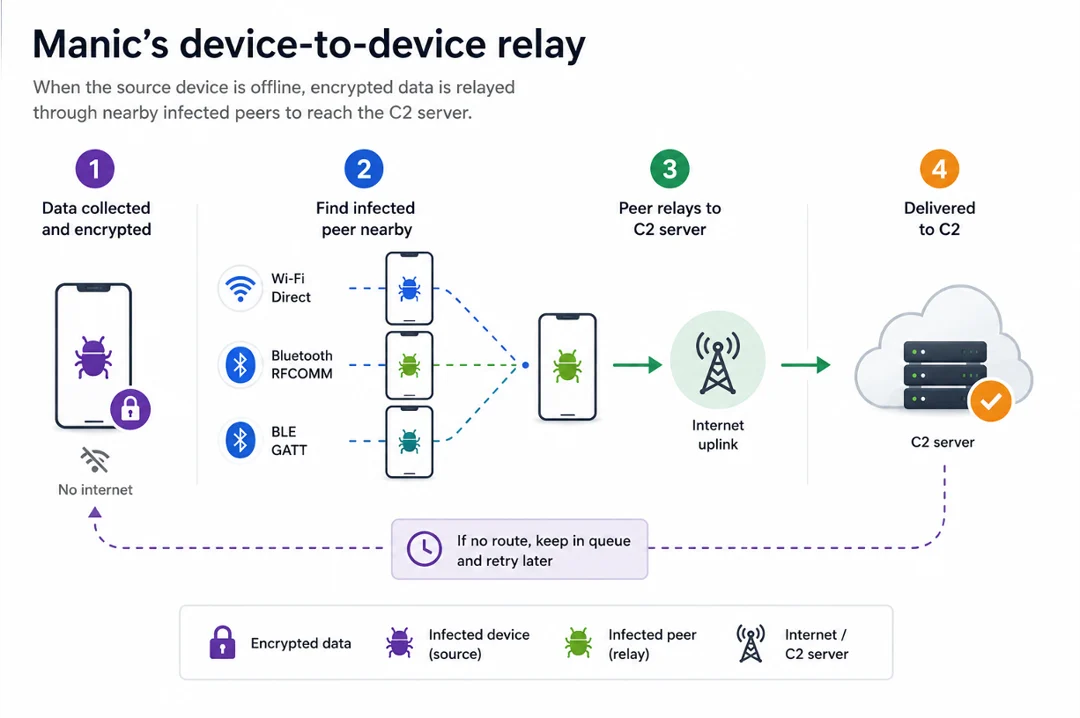
Manic Android malware combines banking fraud and spyware, using a Bluetooth relay to steal data even when devices are offline. ThreatFabric’s Mobile Threat Intelligence team has identified a new Android malware, dubbed Manic, which has been active in the wild since at least February 2026. The researchers state that the malware is still under development […]
 Pierluigi Paganini
August 19, 2026
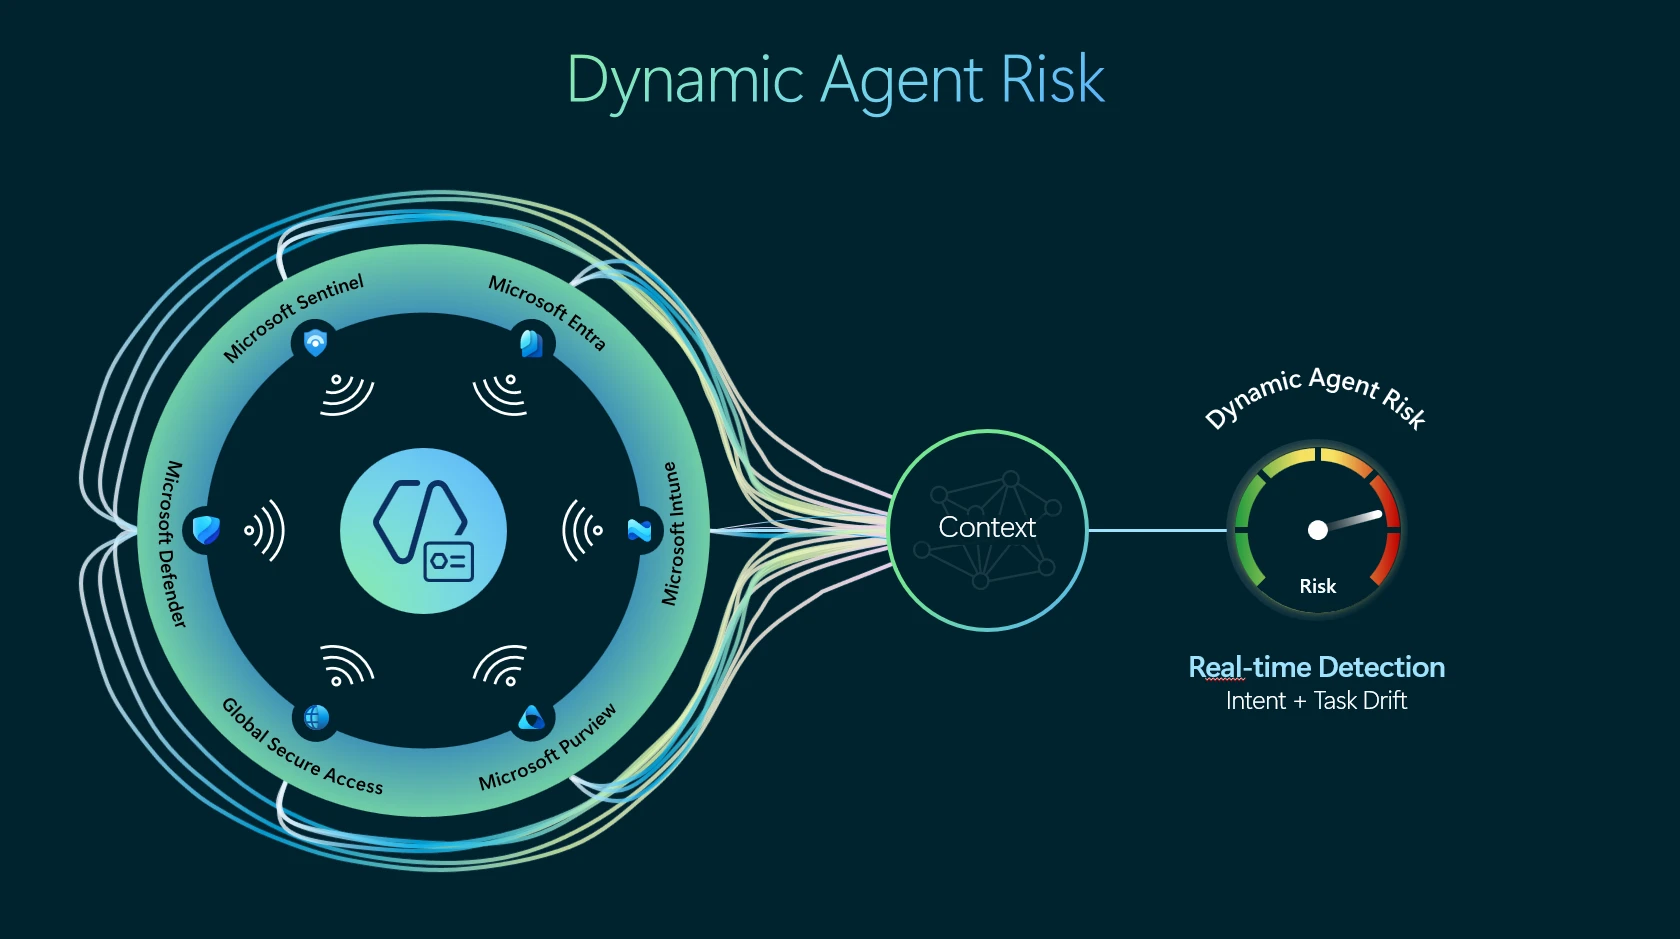
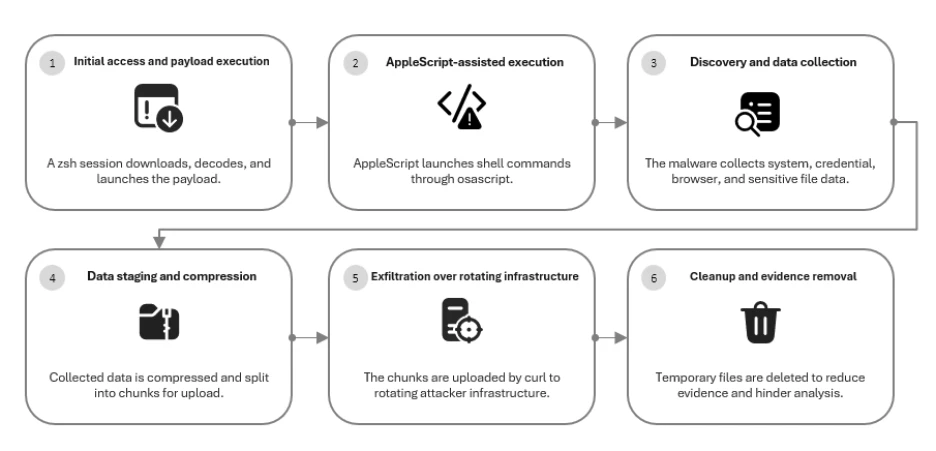
Microsoft tracked over 30 MacSync Stealer domains by focusing on behavioral patterns, revealing a campaign targeting passwords, keys, wallets and other data. Domain blocking is a losing game when the thing you’re blocking can register a new domain faster than you can add it to a list. That’s the exact problem Microsoft Defender Experts ran […]
 Pierluigi Paganini
August 18, 2026
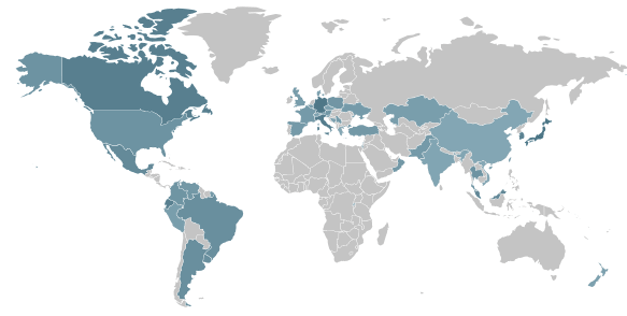
Evooo1Bot is a Mirai-based Linux botnet that hijacks routers and IoT devices for DDoS attacks, credential theft and criminal proxy services. Fortinet’s FortiGuard Labs disclosed Evooo1Bot in mid-August, a previously undocumented Linux botnet that’s been active since July 2026. The bot borrows Mirai‘s DDoS engine but adds encrypted command-and-control communications, an SSH brute-force scanner, a […]
 Pierluigi Paganini
August 17, 2026
The SANDCLOCK LiteLLM supply-chain attack exposed credentials across 2,038 repositories, affecting technology, finance, healthcare, retail and more. Resecurity (USA) estimated the most affected sectors by the “SANDCLOCK” backdoor, which was planted as a result of the code repository compromise. According to cybersecurity experts, LiteLLM / TeamPCP Supply-Chain Attack will have long-lasting consequences. By compromising a […]
 Pierluigi Paganini
August 17, 2026
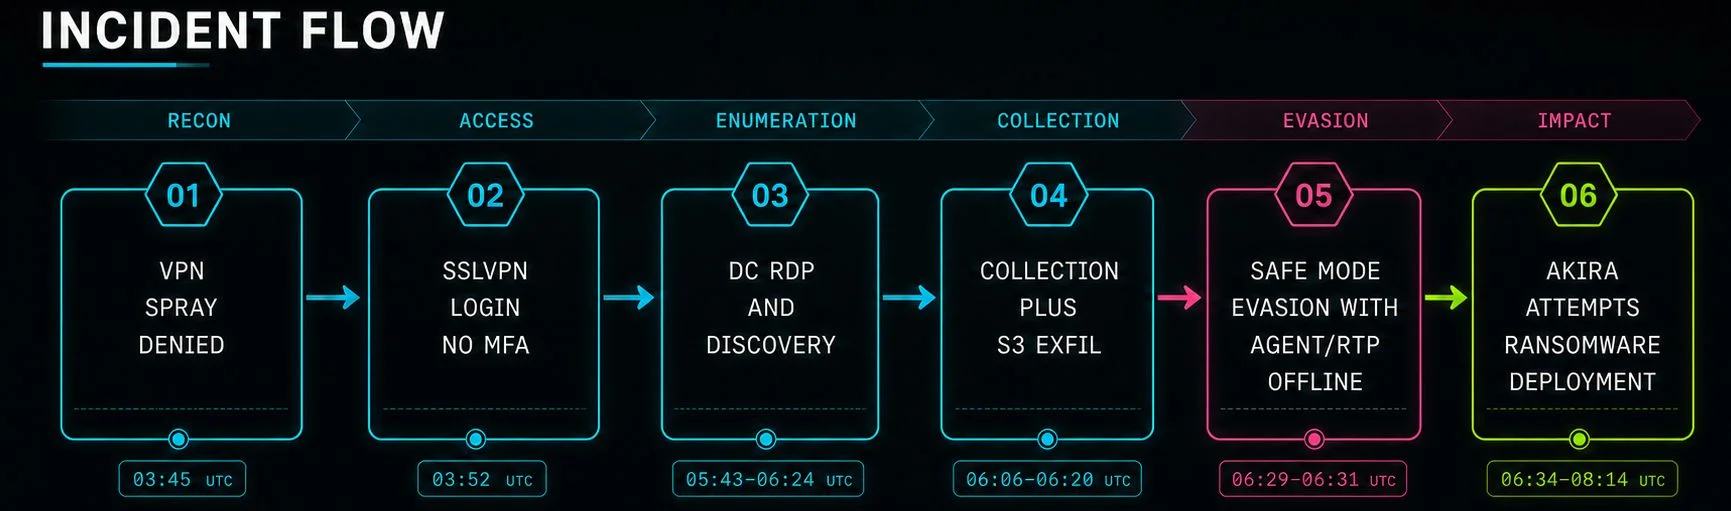
Akira attackers used Safe Mode to disable EDR before deploying ransomware, but memory issues caused the encryptor to fail. An Akira ransomware affiliate broke into a company through an MFA-less SonicWall VPN on August 4, stole credentials and file shares, and then rebooted the compromised host into Safe Mode with Networking to kill the security […]
 Pierluigi Paganini
August 16, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Kimsuky Integrates AI into Attack Operations, From AI-Generated Decoy Documents to a Local LLM ShieldBreak – August 2026 disclosure Kimwolf v7: An Evolution of the Kimwolf Botnet CISA, FBI and Partners Warn Organizations of […]
 Pierluigi Paganini
August 16, 2026
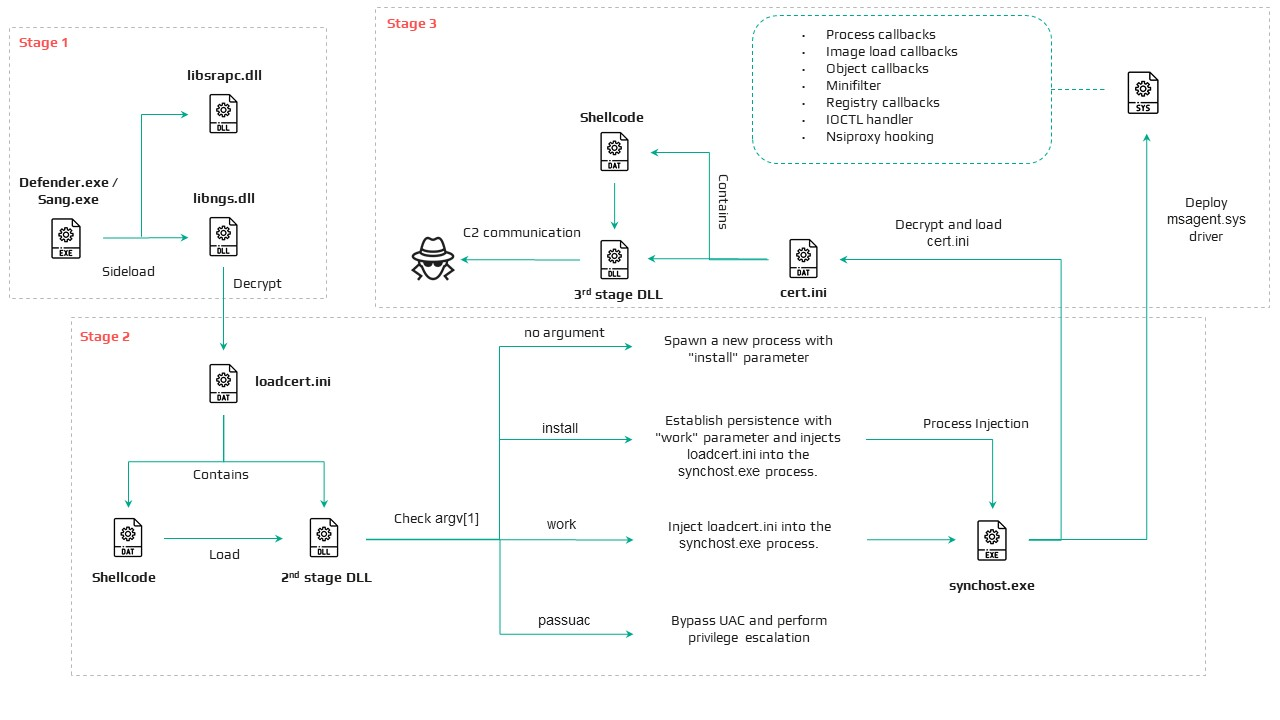
Mustang Panda upgraded CoolClient with a signed kernel driver that hides processes, files and network activity, making the backdoor harder to detect. HoneyMyte, also known as Mustang Panda, has pushed its CoolClient backdoor another step deeper into Windows. Kaspersky’s latest analysis shows a new variant that can deploy a signed kernel-mode driver as a Windows […]
 Pierluigi Paganini
August 16, 2026
Acronis uncovered PATCHCORD, a stealthy backdoor targeting Afghan telecom and South Asian infrastructure via fake VPN tools and Google Sheets C2. Researchers at Acronis just documented an espionage operation that reads like it was built by someone with genuinely good taste in disguises. Their Threat Research Unit report tracks a previously undocumented backdoor called PATCHCORD, […]
 Pierluigi Paganini
August 15, 2026
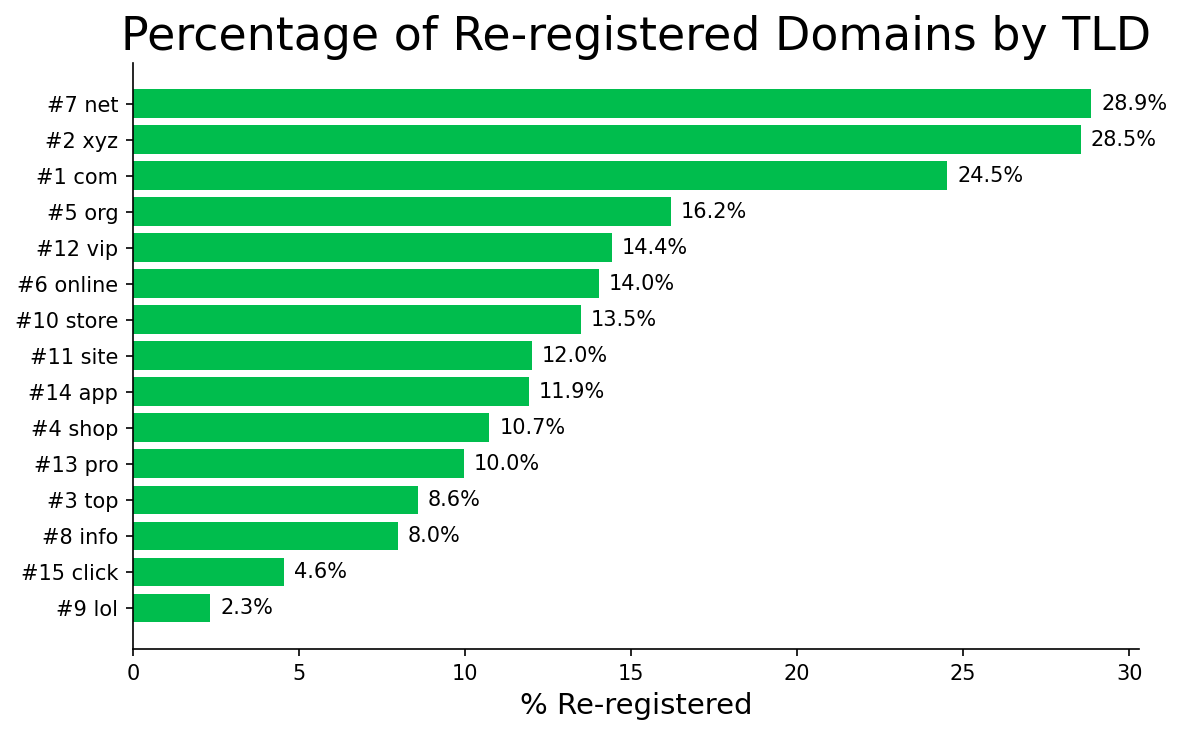
Attackers are buying expired domains to exploit their reputation, traffic and DNS history, using them for malware delivery, scams and C2 infrastructure. Every day, roughly 65,000 domain names that once belonged to someone else get re-registered by a new owner. Infoblox Threat Intel calls these dropcatch domains, and in the first half of 2026 they […]
Data Breach / October 20, 2026