



 Pierluigi Paganini
 September 13, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter REVSTEALER ramps up Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode GuardBreaker: Derailing AI-assisted malware analysis with a code comment DPRK APTs: Ted backdoor and curlRAT target South Korean media and automotive […]
 Pierluigi Paganini
September 11, 2026
Three threat groups are exploiting two Cisco FMC flaws to steal credentials, gain root access and deploy Qilin ransomware. Cisco Talos says three separate threat groups are exploiting two recently patched Secure Firewall Management Center (FMC) flaws. The main target is CVE-2026-20079, a critical authentication bypass that lets unauthenticated attackers remotely bypass security controls, run […]
 Pierluigi Paganini
September 09, 2026
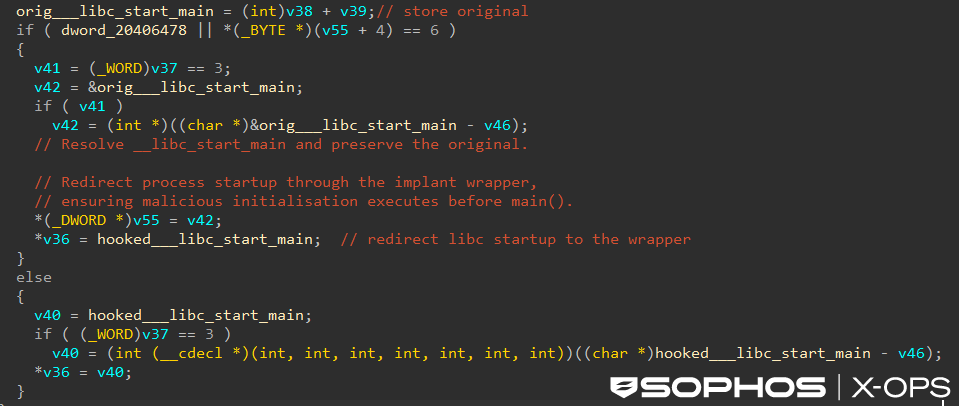
PoisonedRefresh rootkit injects PHP web shells into F5 BIG-IP APM Apache memory, leaving no disk artifacts. SophosLabs published a detailed technical analysis on September 8, 2026, of a Linux implant, dubbed PoisonedRefresh by ESET, they found in compromised F5 BIG-IP Access Policy Manager environments. Sophos tracks it as Linux/Agnt-IC. F5 has confirmed exploitation of the […]
 Pierluigi Paganini
September 08, 2026
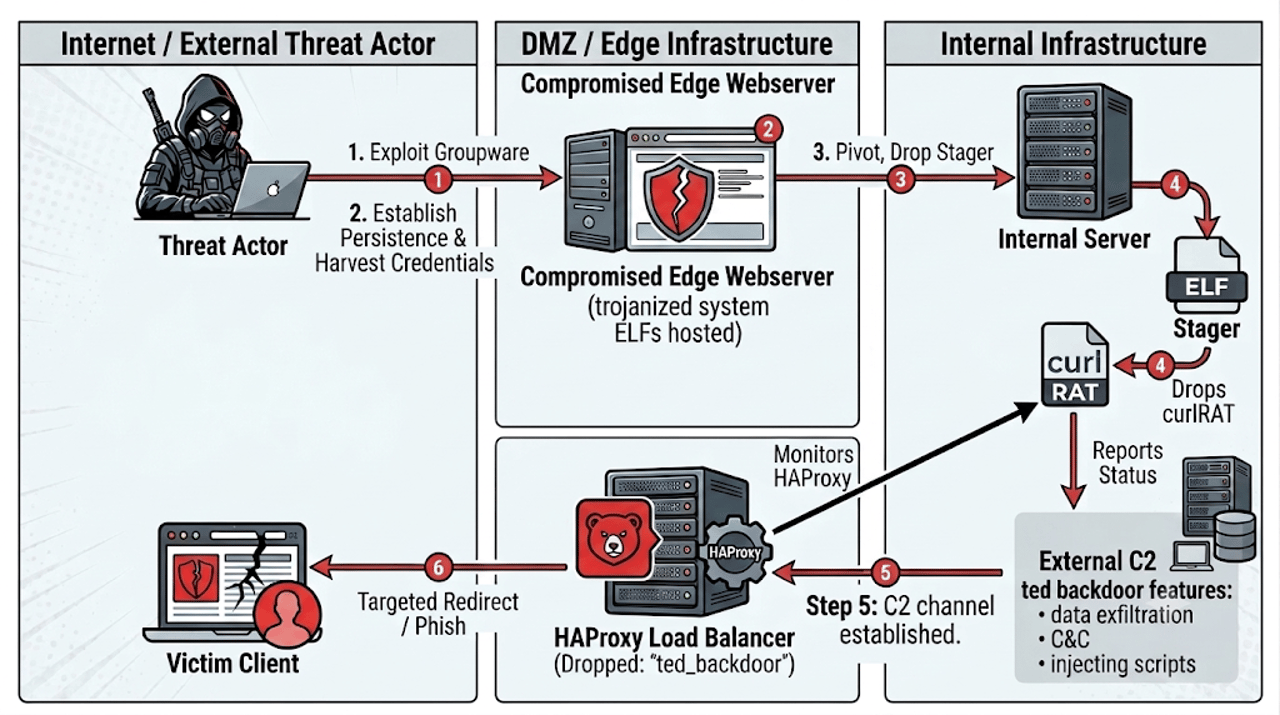
North Korea-linked hackers hid a backdoor inside HAProxy, masking C2 traffic and stealing data while keeping the load balancer working normally. North Korean-linked hackers found a genuinely clever hiding spot for their malware: inside the actual source code of HAProxy, the load balancing software running at the edge of two South Korean companies’ networks. Rapid7’s […]
 Pierluigi Paganini
September 07, 2026
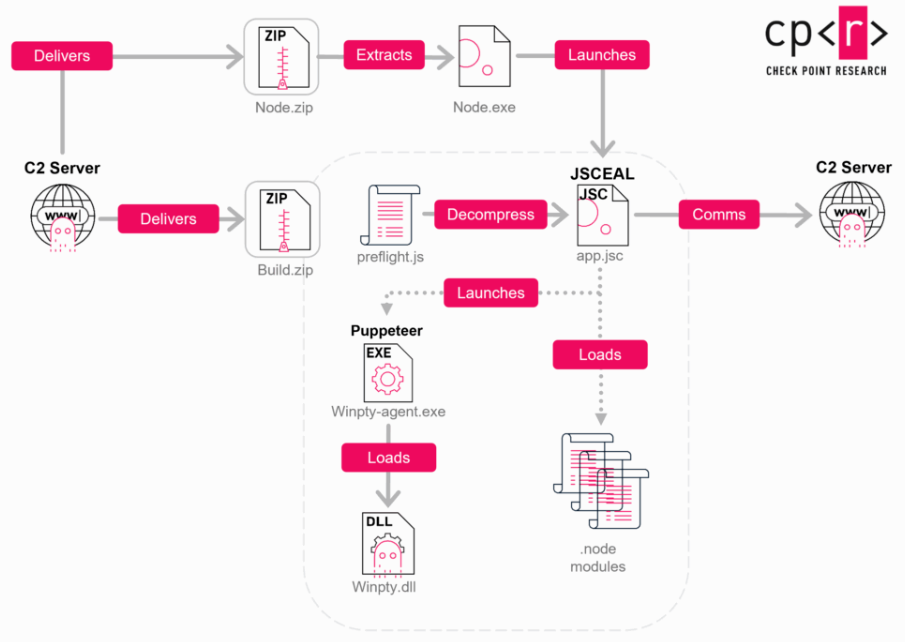
JSCeal hides crypto-stealing malware in V8 bytecode, but researchers built a tool to decompile it and expose its advanced theft capabilities. JSCeal is a cryptocurrency stealer that Check Point Research has tracked since early 2025. Unlike most malware, it hides its code in a format that makes analysis much harder. Check Point presented its latest […]
 Pierluigi Paganini
September 03, 2026
Serbian activists were targeted with zero-click Pegasus and NoviSpy spyware, exposing a major surveillance campaign ahead of elections. A member of Serbia’s student protest movement had their iPhone infected with NSO Group‘s Pegasus spyware without ever clicking a link or opening a file. The Citizen Lab confirmed the infection in collaboration with the SHARE Foundation, […]
 Pierluigi Paganini
September 02, 2026
Experts got Claude to port a PLC exploit, but it cost $536 and 8 hours, and a later AI-generated payload accidentally destroyed the hardware. Forescout researchers just answered a question that’s been hanging over industrial security for a while: can AI actually port a working exploit from one PLC to a different model with no […]
 Pierluigi Paganini
September 01, 2026
Five Venezuelan nationals pleaded guilty after failed ATM jackpotting attempts in Kansas. The FBI recorded 700+ cases in 2025, causing $20M in losses. Five Venezuelan nationals have pleaded guilty after trying to steal cash from ATMs in Kansas using the popular ATM jackpotting technique. The U.S. Department of Justice announced the case on August 31, […]
 Pierluigi Paganini
August 31, 2026
ValleyRAT hides behind legitimate adware, using DLL sideloading to evade detection, steal data and give Silver Fox control of infected systems. ValleyRAT doesn’t always need to disguise itself as a cracked game or a fake browser update. It can also hide behind something much more ordinary: an application that looks like adware and appears to […]
 Pierluigi Paganini
August 31, 2026
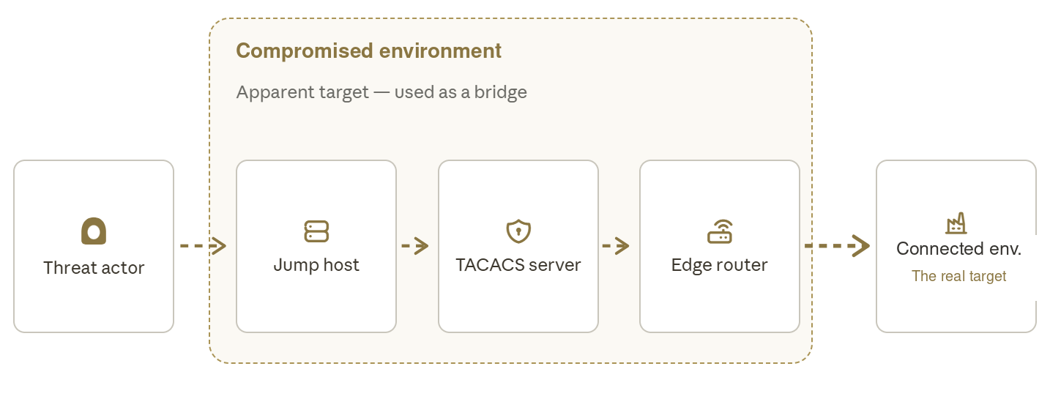
Fire Ant hijacked Cisco routers, stole credentials and altered logs to hide its tracks, using trusted infrastructure to reach high-value networks. Chinese-linked cyber espionage group Fire Ant has spent the past year quietly graduating from hacking individual computers to hacking the infrastructure that connects them. Sygnia’s new report traces how the group expanded from compromising […]





