


 Pierluigi Paganini
 August 30, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Operation QUICSILVER: China-Nexus Actor Targets Myanmar Diplomats via VHD-Delivered Go Backdoor FTP Banners: The New Dead Drop Resolver Delivering Novel RATs The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic […]
 Pierluigi Paganini
August 29, 2026
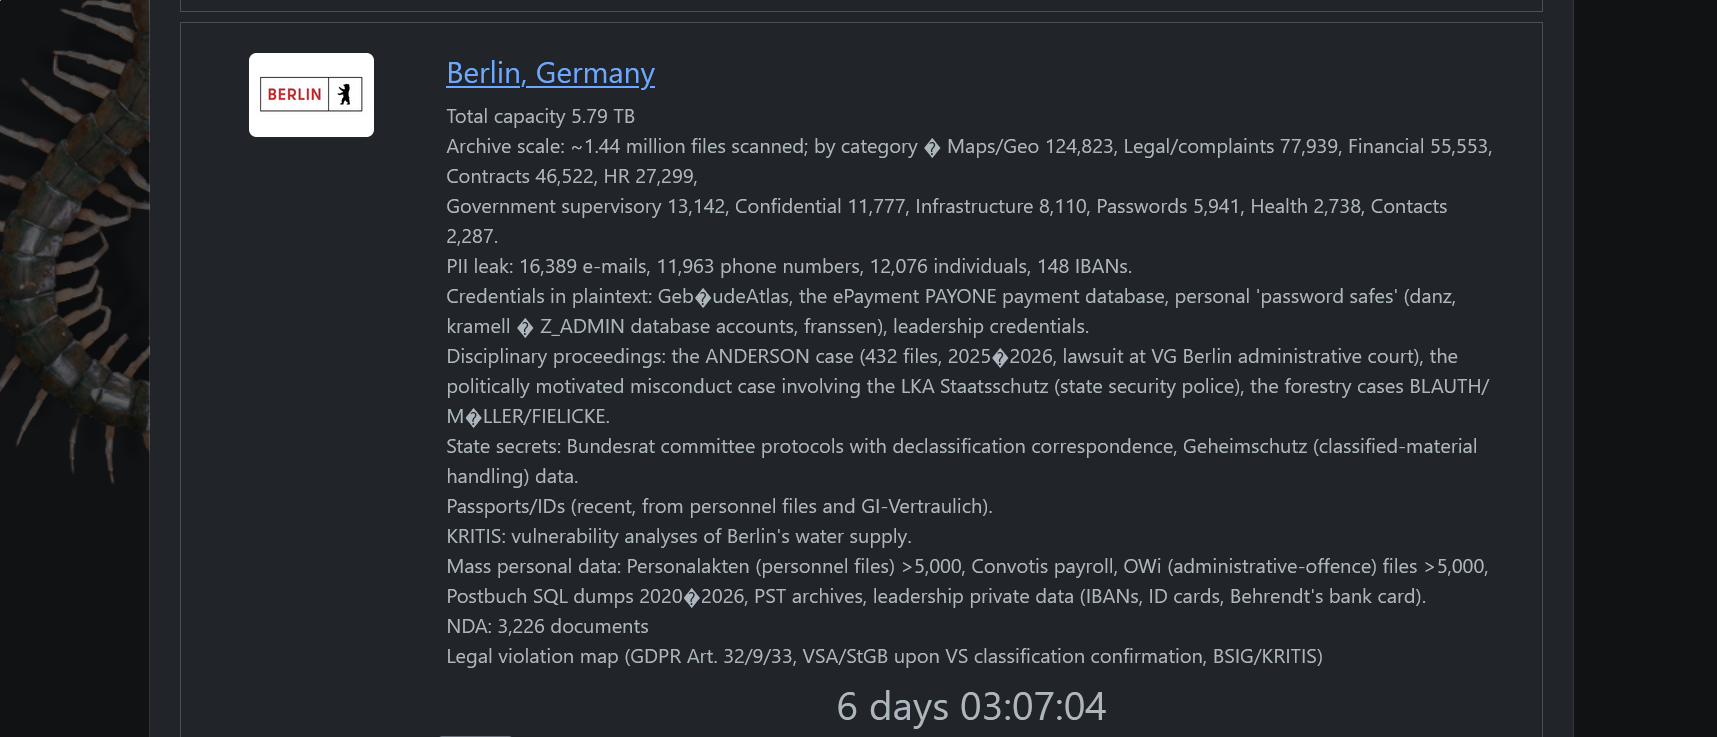
Berlin ‘s government faces a Rhysida ransomware attack weeks before elections, with officials refusing to pay despite a claimed 5.79 TB data theft. Berlin’s state government confirmed this week it’s dealing with an extortion attempt following an August cyberattack on the city-state’s administrative network, and officials have already refused the requested ransom. The ransomware group […]
 Pierluigi Paganini
August 28, 2026
BlueDelta (APT28) uses webhook.site and Microsoft Edge to hide HOOKEDGE espionage traffic targeting European governments. Recorded Future’s Insikt Group documented a campaign by BlueDelta, the Russian GRU-linked group that overlaps with the group APT28, running an entire espionage operation against European government targets using webhook.site, a service built for developers to test HTTP requests, as […]
 Pierluigi Paganini
August 27, 2026
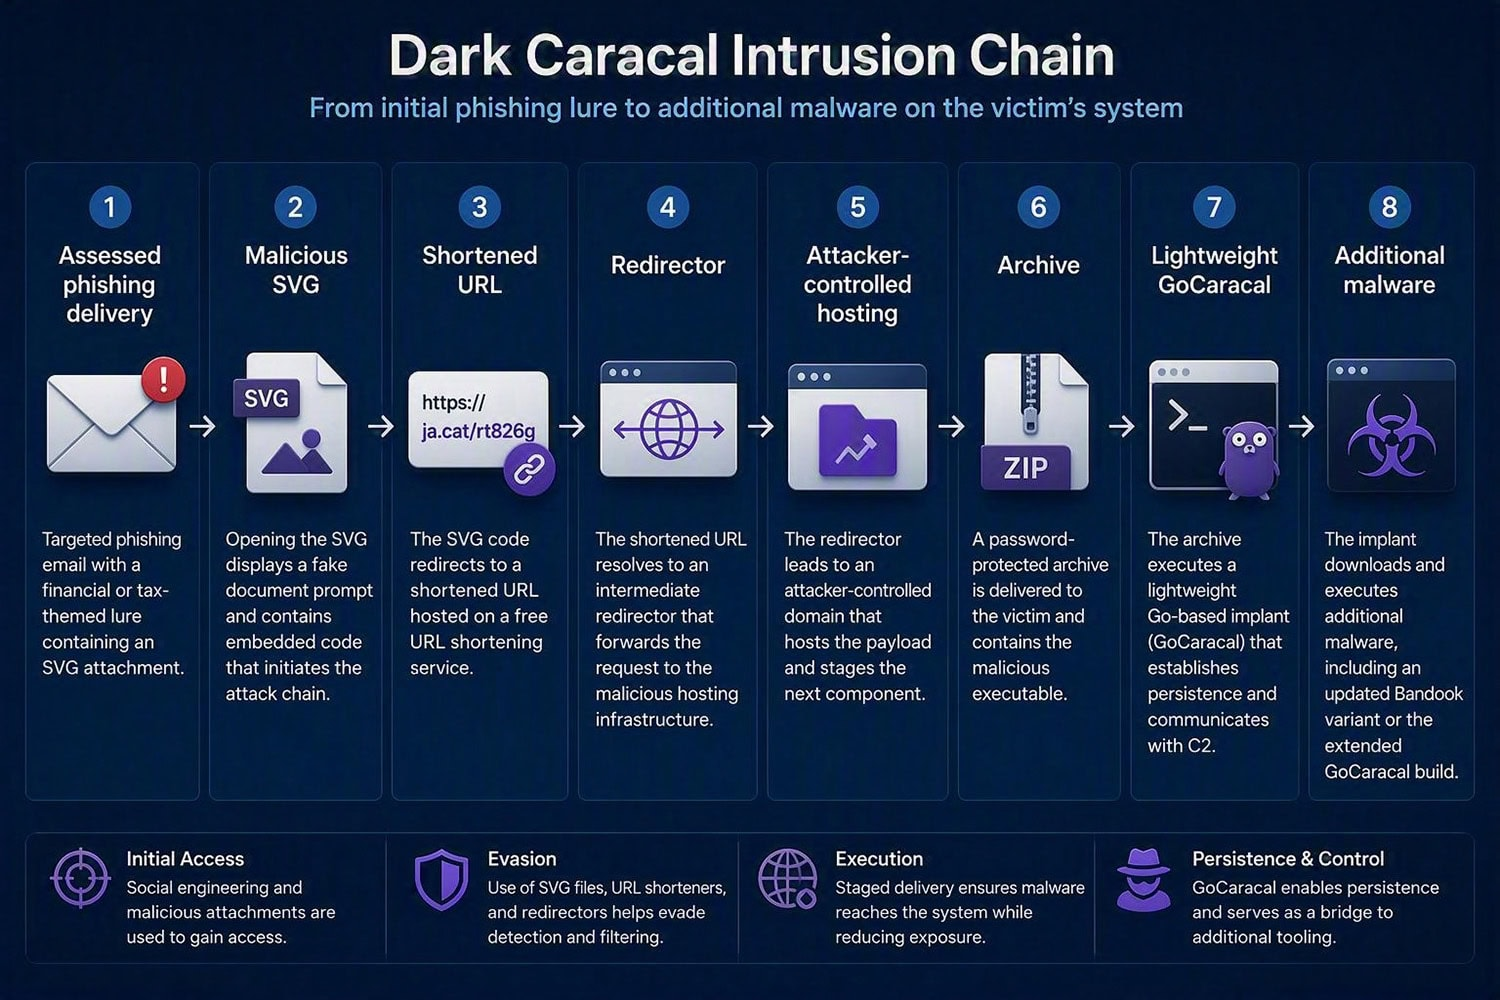
Dark Caracal targets Venezuela with GoCaracal, an upgraded Bandook toolkit and an Ethereum fallback for resilient C2 communications. Dark Caracal is back with new malware and the same hunting grounds. Arctic Wolf Labs researchers link a June 2026 intrusion against a communications organisation in Venezuela to the Lebanon‑linked espionage group, and says it deployed a […]
 Pierluigi Paganini
August 25, 2026
WeedHack Minecraft Malware Survives C2 Takedown: Fake Client Sites Still Active, SEO Poisoning Puts Malicious Downloads at the Top of Google McAfee Labs published a follow-up report on the WeedHack Malware-as-a-Service campaign this week, documenting ten active malicious sites and multiple file-hosting accounts that are still spreading the infostealer despite a disruption to its command-and-control […]
 Pierluigi Paganini
August 24, 2026
A fake 113GB GTA VI build is packed with malware, using massive empty files to hide a tiny malicious payload. GTA VI hype has reached the point where people are volunteering to infect their own computers just to check if a leak is real. Someone on X asked their followers to “take one for the […]
Pierluigi Paganini
August 23, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Akira Hits Safe Mode: Ransomware Rebooting Around EDR Multi-Functional Linux Botnet “Evooo1Bot” StubMaker RubyGems Campaign Delivers a Windows Infostealer Hunting MacSync Stealer infrastructure through behavioral pivots Manic: Blend between Banking Malware & Spyware […]
 Pierluigi Paganini
August 22, 2026
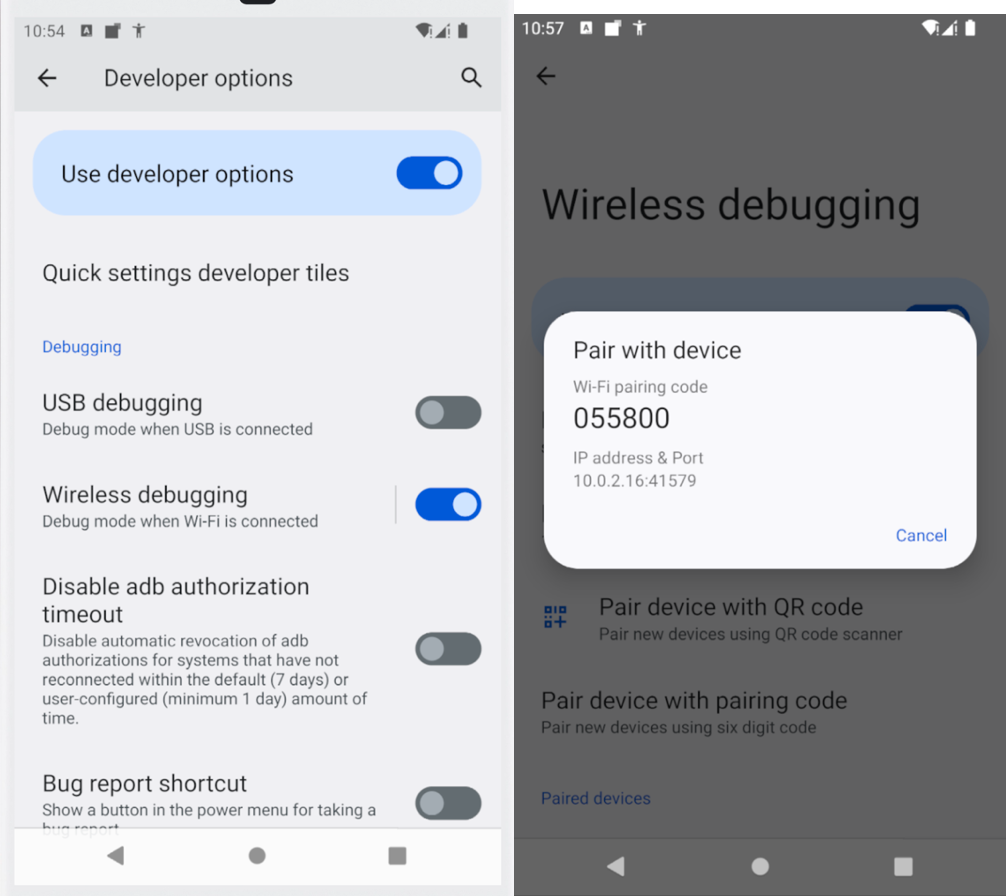
ToxicPanda 2.0 targets 349 financial apps and abuses Android Wireless Debugging to gain deeper device access and steal banking credentials. ToxicPanda used to be a Europe-focused nuisance targeting a manageable list of banks. That version is gone. Zimperium’s zLabs team just documented ToxicPanda 2.0, and the numbers alone tell the story: 349 targeted financial institutions […]
 Pierluigi Paganini
August 21, 2026
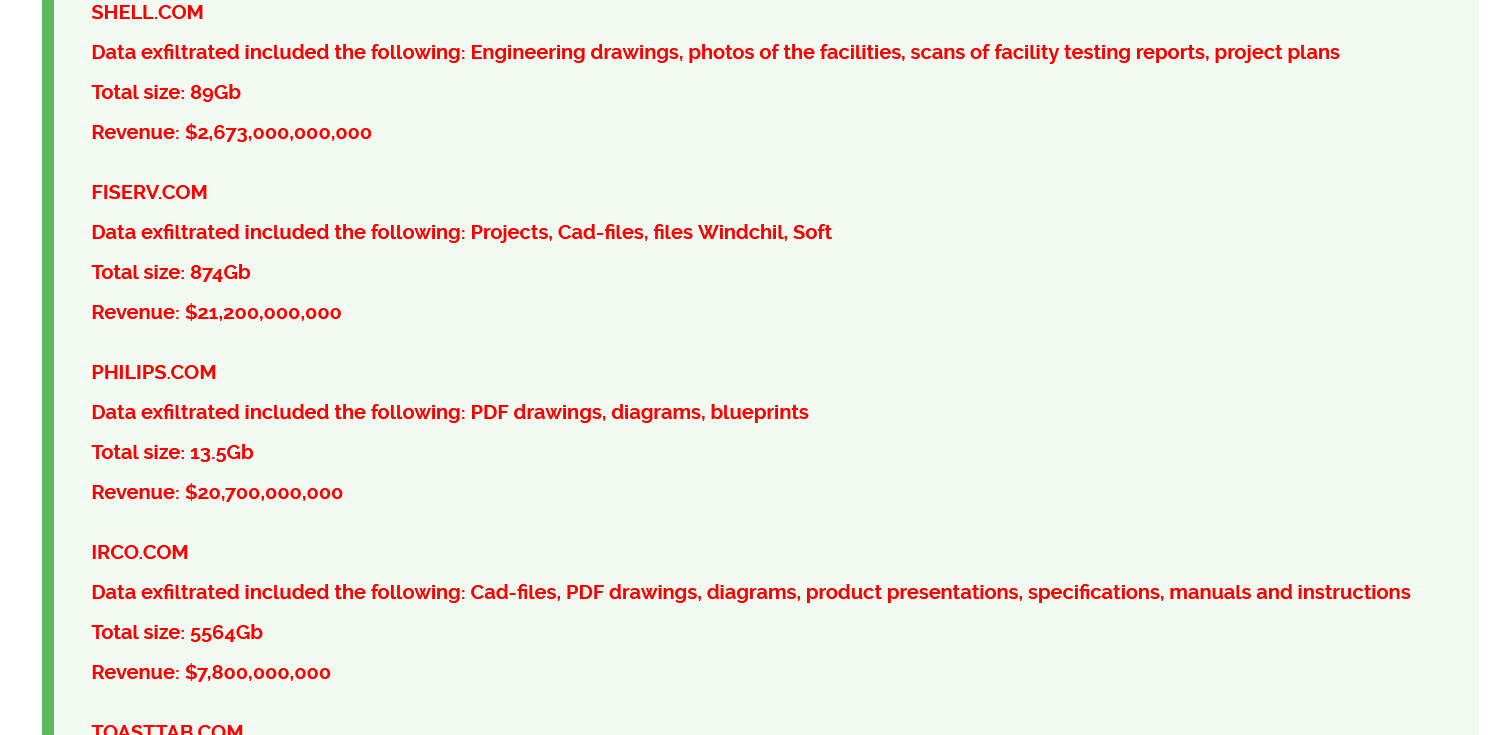
Cl0p claims over 40 organizations fell victim to attacks exploiting a PTC Windchill and FlexPLM vulnerability. Cl0p is using a familiar strategy again: exploit one flaw in enterprise software to attack many companies, then publish the victims’ names if they refuse to pay. The group claims it has targeted more than 40 organizations through a […]
 Pierluigi Paganini
August 20, 2026
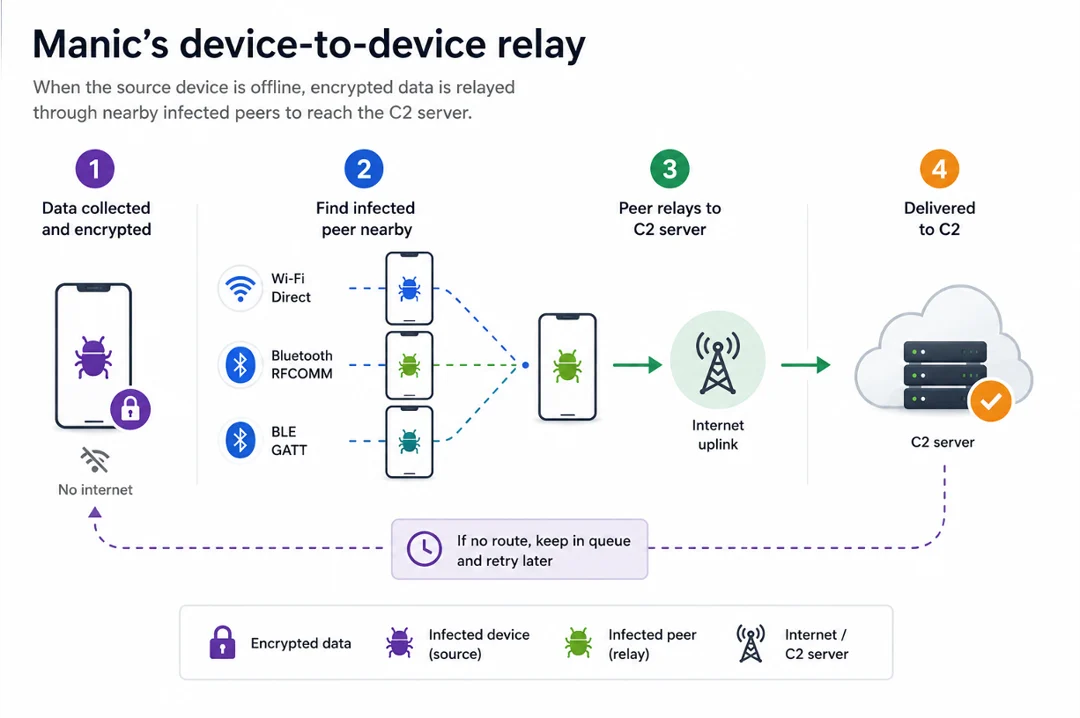
Manic Android malware combines banking fraud and spyware, using a Bluetooth relay to steal data even when devices are offline. ThreatFabric’s Mobile Threat Intelligence team has identified a new Android malware, dubbed Manic, which has been active in the wild since at least February 2026. The researchers state that the malware is still under development […]






