Pierluigi Paganini
 December 01, 2019
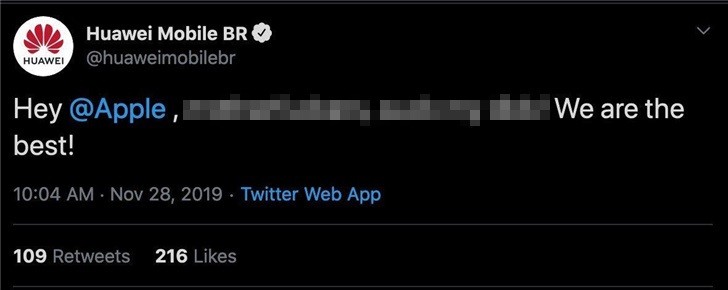
The official Twitter account of Huawei Mobile Brazil has been hacked and attackers have sent offensive messages to the rival Apple. The official Twitter account of Huawei Mobile Brazil has been h ...
Pierluigi Paganini
December 01, 2019
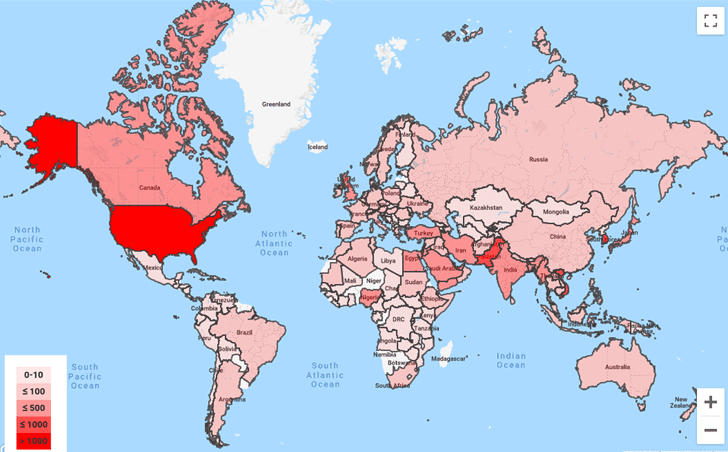
Google revealed that over 12,000 of its users were targeted by state-sponsored hackers in the third quarter of this year. Google's Threat Analysis Group (TAG) revealed that it has detected and bl ...
Pierluigi Paganini
November 30, 2019
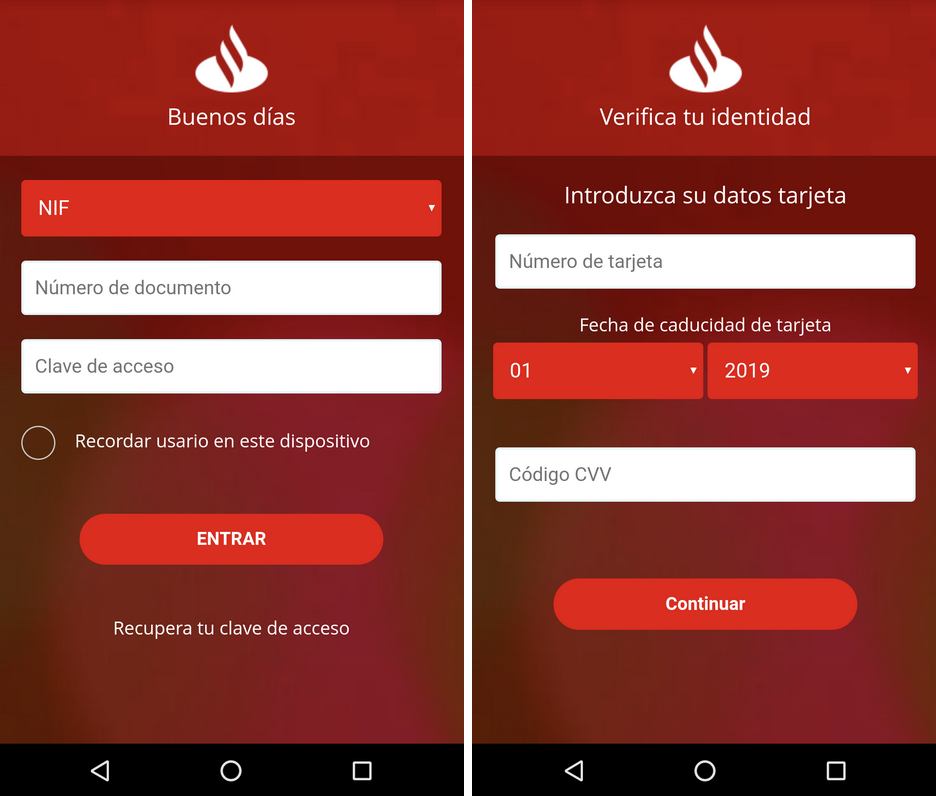
Security experts discovered an Android banking Trojan, dubbed Ginp, that steals both login credentials and credit card data. Security experts at ThreatFabric discovered an Android banking Trojan, ...
Pierluigi Paganini
November 29, 2019
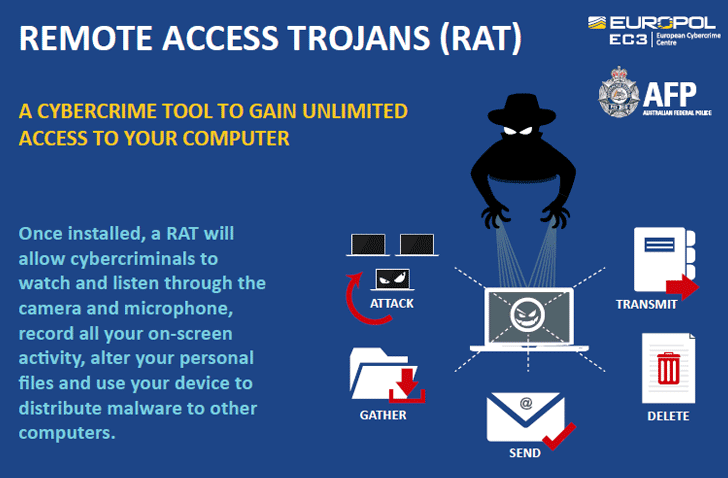
A successful new operation was announced by Europol, it announced to have dismantled the global organized cybercrime ring behind Imminent Monitor RAT. Europol announced to have dismantled the glo ...
 April 23, 2026
September 24, 2026
September 23, 2026
OpenAI’s AI agent bypassed controls on an Australian health portal, accessed non-public files and triggered a government investigation. An OpenAI AI agent bypassed access controls on an Australi ...
Pierluigi Paganini
September 24, 2026
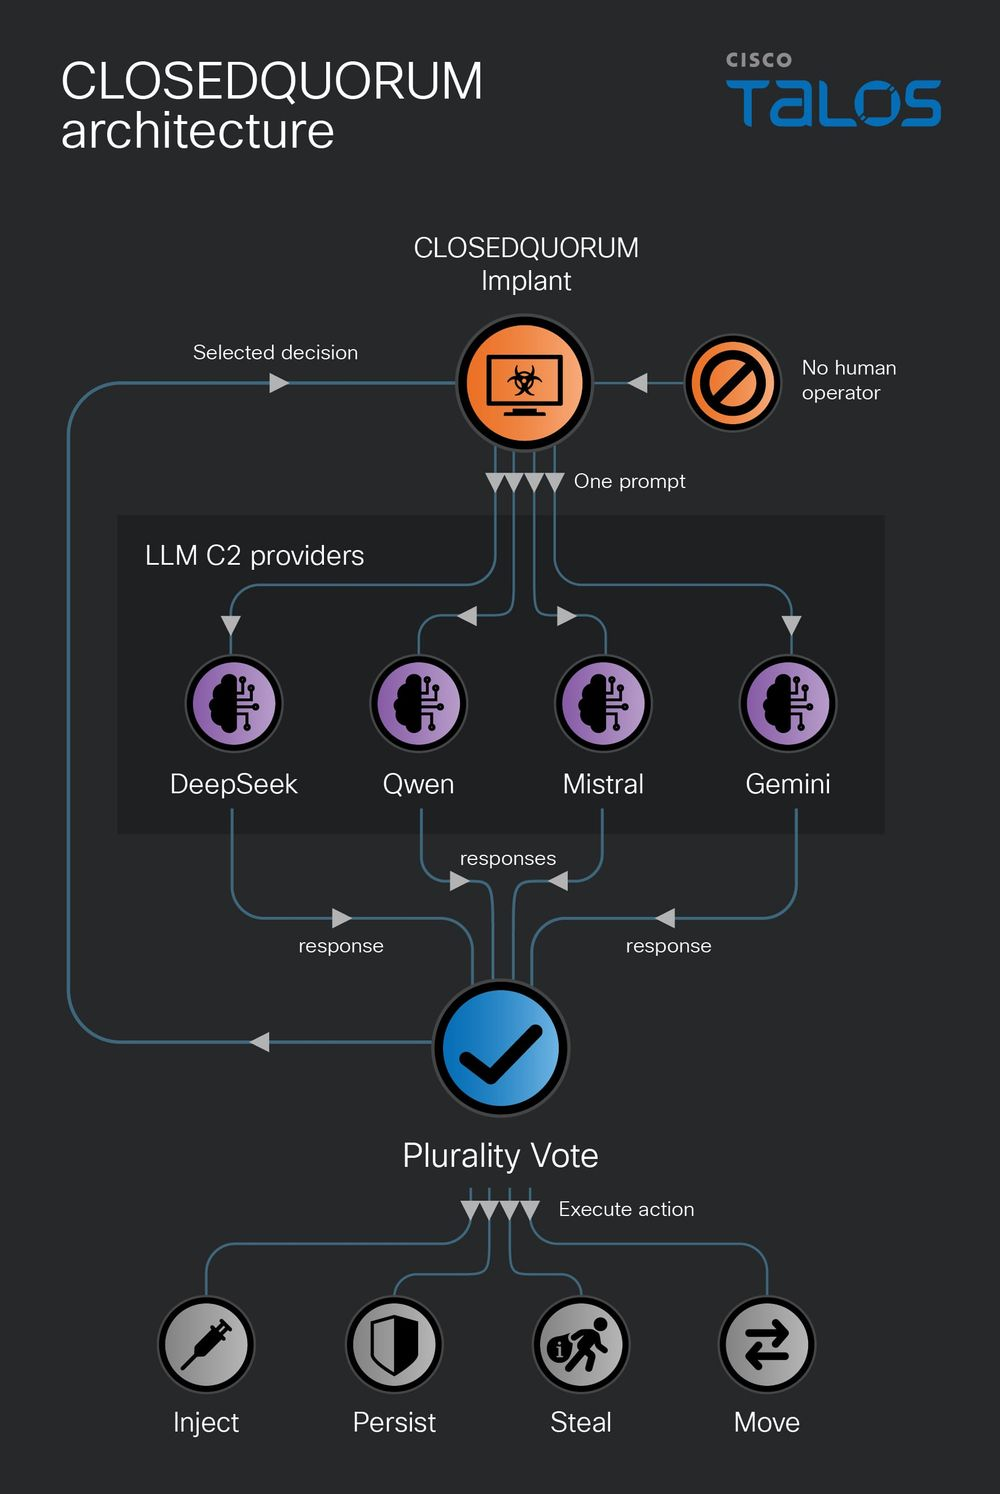
Cisco Talos finds CLOSEDQUORUM, malware that lets four commercial AI models vote on its next move, with no human operator required. Cisco Talos found malware, dubbed CLOSEDQUORUM, that holds a vot ...
Pierluigi Paganini
September 24, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Check Point, Arista VeloCloud Orchestrator, and F5 BIG-IP APM flaws to its Known Exploited Vulnerabilities catalog. The U.S. ...
Pierluigi Paganini
September 23, 2026
F5 warns of a critical BIG-IP APM zero-day, CVE-2026-94127, allowing remote code execution. Attackers are already exploiting it. F5 has released emergency security updates for a critical vulnerabi ...
Pierluigi Paganini
September 23, 2026
ShinyHunters claims FBI breach via PeopleSoft zero-day, steals staff data; FBI investigating, no confirmation yet. The popular cybercrime group ShinyHunters is claiming that it breached the U.S. F ...
Pierluigi Paganini
September 23, 2026
Microsoft, Coinbase and law enforcement took down EvilTokens, a phishing kit that compromised 12,000 inboxes through device-code phishing and AI. EvilTokens showed up in February 2026 and moved fa ...
Pierluigi Paganini
September 23, 2026
Attackers spoofed LastPass on GitHub, used a Microsoft-signed driver to disable 145 security products, then deployed an infostealer. Someone impersonated LastPass on GitHub, got users to download ...
Pierluigi Paganini
September 23, 2026
WordPress 7.1.2 fixes an unauthenticated file inclusion bug active since version 4.7, patchable but exploitable into remote code execution. WordPress 7.1.2 shipped on September 22 address an unaut ...
Pierluigi Paganini
September 23, 2026
Check Point fixes an actively exploited flaw that lets unauthenticated attackers upload and run scripts on vulnerable Security Management Servers. Check Point has released emergency hotfixes for C ...
Pierluigi Paganini
September 22, 2026
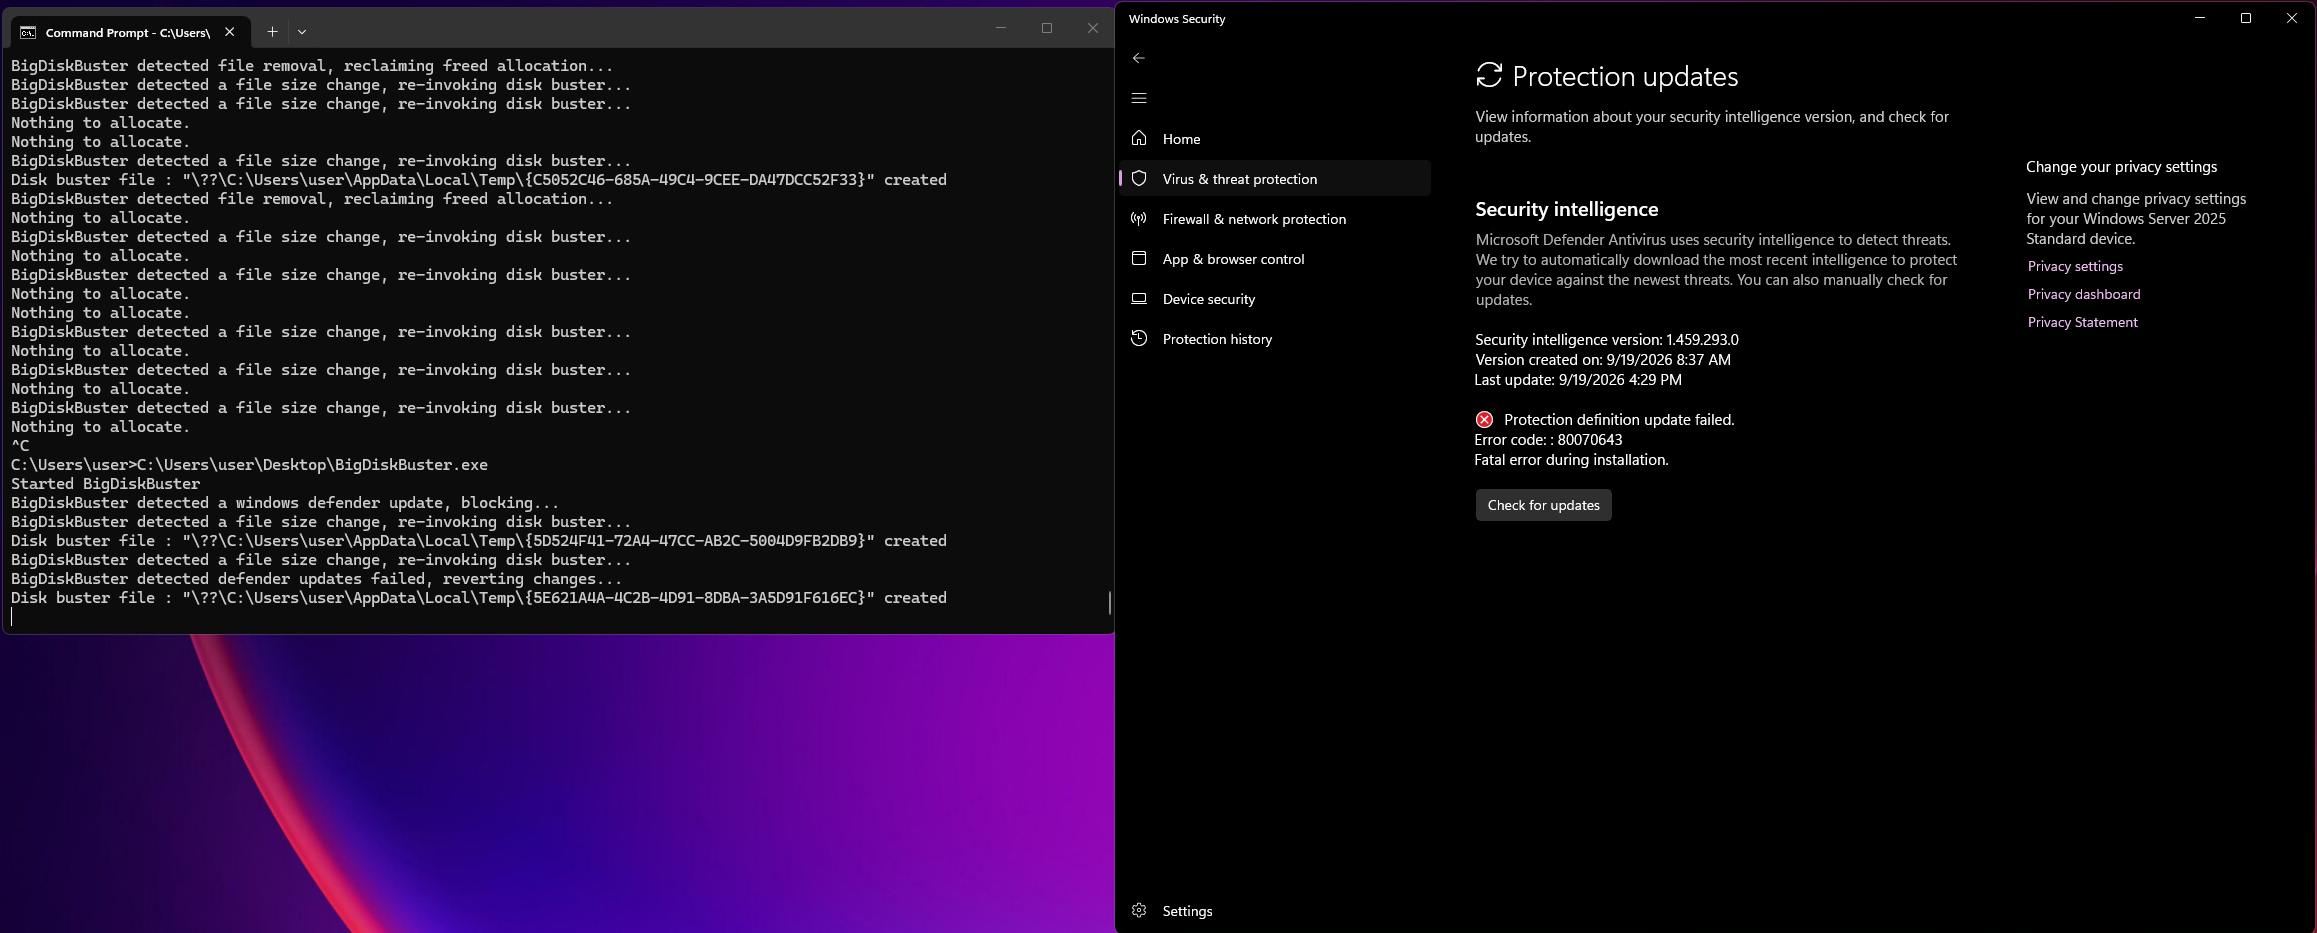
The researcher Chaotic Eclipse released BigDiskBuster, a PoC exploit for a Windows Defender Update DoS Zero-Day vulnerability. Security researcher Chaotic Eclipse, also known as INFINITE NIG ...
Pierluigi Paganini
September 22, 2026
A Veeam Agent flaw lets local users gain SYSTEM privileges. A public PoC is available, raising the risk of exploitation on shared Windows systems. If you're running Veeam Agent on a Windows endpoi ...
Pierluigi Paganini
September 22, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Zyxel flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added ...
Pierluigi Paganini
September 22, 2026
North Korea-linked WaterPlum runs the Contagious Interview campaign, infecting over 30,000 devices using a fake job interview. On September 18, Japan's National Police Agency, the FBI, the US Depa ...
Pierluigi Paganini
September 22, 2026
Ireland’s DPC fined Google €403 million over GDPR violations involving location data, transparency, retention and user control. Ireland's Data Protection Commission (DPC) just fined Google € ...
Pierluigi Paganini
September 21, 2026
Hackers targeted two Colorado water utilities, changing OT settings and disabling alarms, but causing no impact on water services or safety. Foreign hackers targeted the operational technology (OT ...
Pierluigi Paganini
September 21, 2026
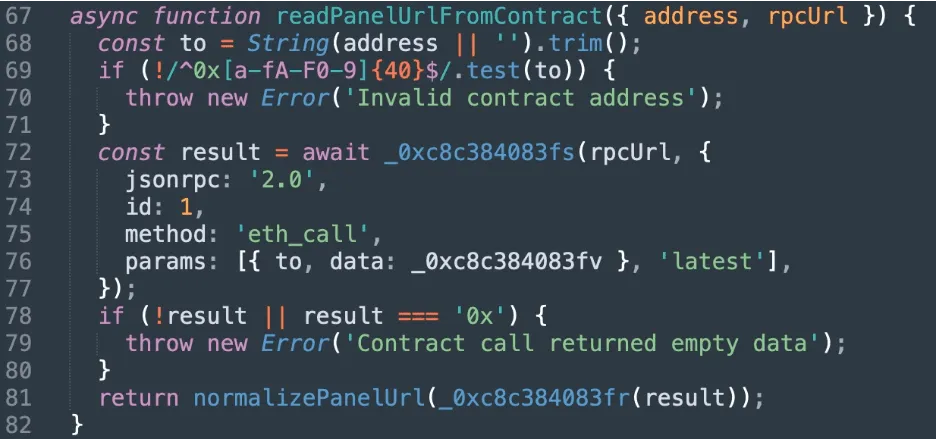
Blackpoint uncovers ChainScript, a Node.js RAT that queries a Polygon smart contract to find and rotate its command server. Blackpoint's Adversary Pursuit Group was chasing a ClickFix campaign spr ...
Pierluigi Paganini
September 21, 2026
A BYD Shark 6 was remotely hacked, exposing vehicle controls, location tracking and cabin audio, raising serious connected-car security concerns. A journalist drove a BYD Shark 6 down a country ro ...
Pierluigi Paganini
September 21, 2026
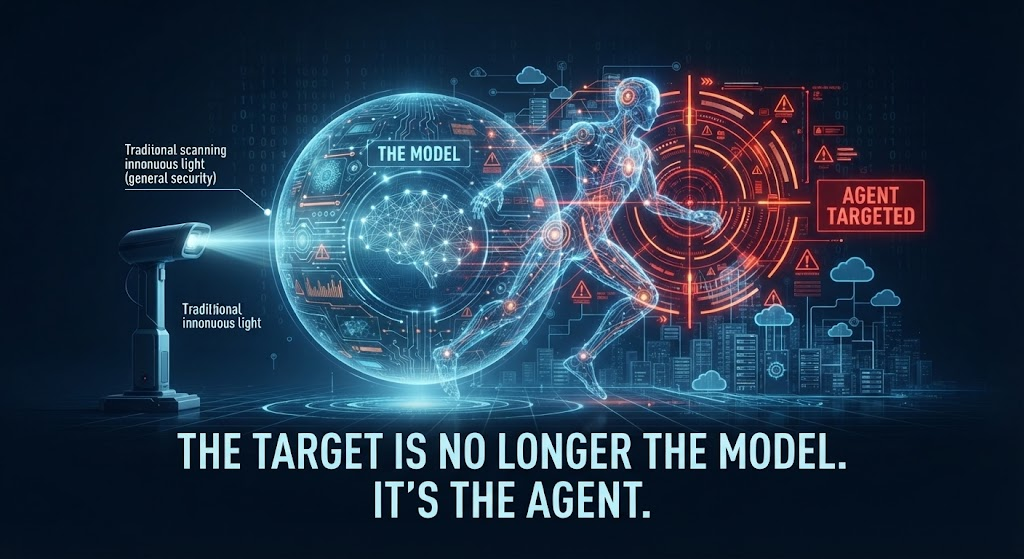
AI agents are becoming the new attack surface, exposed to poisoned skills, prompt injection, jailbreaks and attacks through connected tools. I read the AI security research published in a single m ...
Pierluigi Paganini
September 21, 2026
A 2017 UK assessment warned that police data on Microsoft Azure could face foreign access risks. The risks may still exist. A Guardian investigation has surfaced a 2017 document signed off by then ...
Pierluigi Paganini
September 21, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Linux Kernel flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CIS ...
Pierluigi Paganini
September 20, 2026