Pierluigi Paganini
 June 03, 2022
Microsoft blocked an attack activity aimed at Israeli organizations attributed to a previously unknown Lebanon-based hacking group tracked as POLONIUM. Microsoft announced to have blocked a series ...
Pierluigi Paganini
June 02, 2022
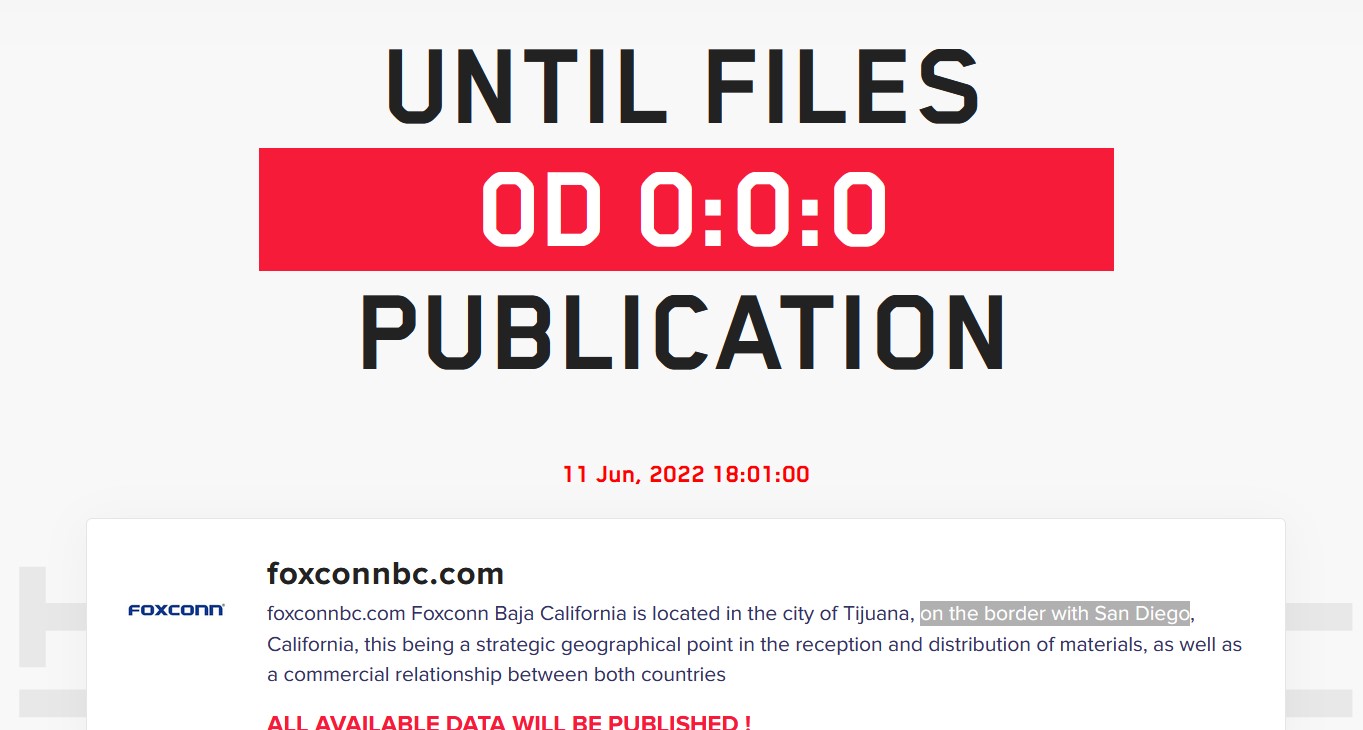
LockBit ransomware gang claimed responsibility for an attack against the electronics manufacturing giant Foxconn that impacted production in Mexico The electronics manufacturing giant Foxconn conf ...
Pierluigi Paganini
June 02, 2022
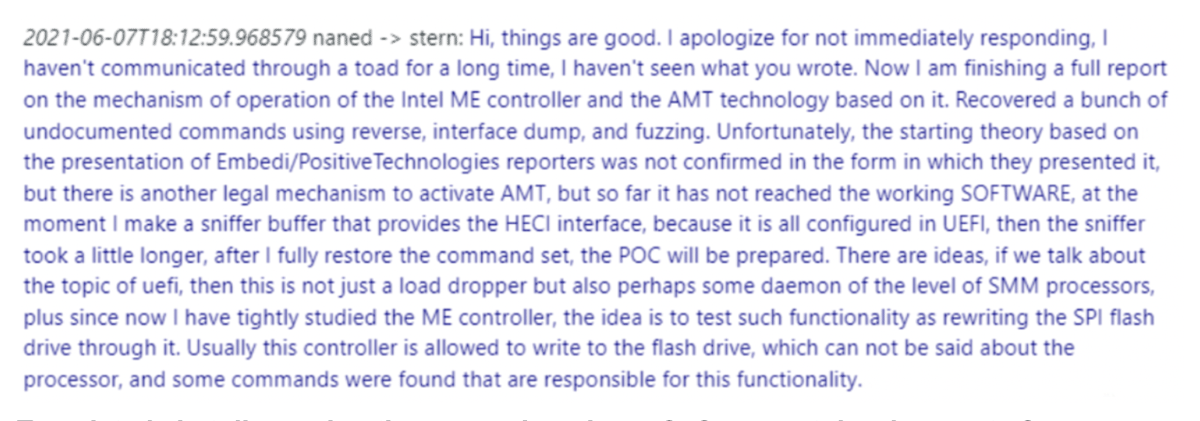
The analysis of the internal chats of the Conti ransomware group revealed the gang was working on firmware attack techniques. The analysis of Conti group's chats, which were leaked earl ...
Pierluigi Paganini
June 02, 2022
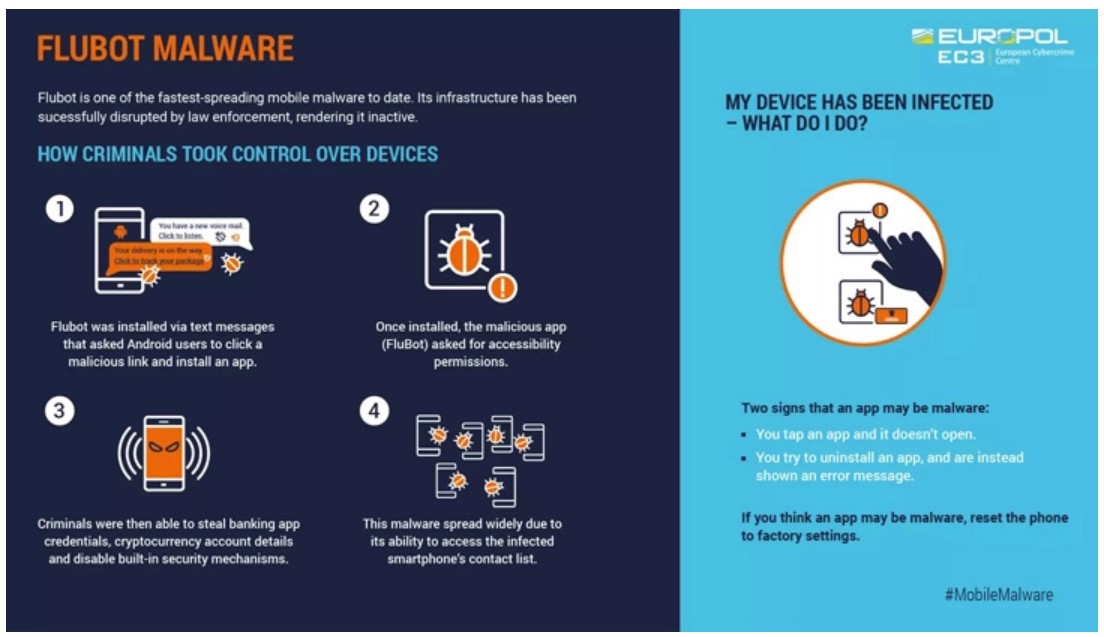
An international law enforcement operation involving 11 countries resulted in the takedown of the FluBot Android malware. An international law enforcement operation involving 11 countries led to t ...
 April 23, 2026
September 18, 2026
September 18, 2026
September 17, 2026
September 17, 2026
September 17, 2026

RatHat combines AI-driven screen control, Android debugging abuse and advanced credential theft to give attackers deep control of infected phones. RatHat is the new Android trojan you should know ...
Pierluigi Paganini
September 18, 2026

Check Point fixed CVE-2026-91843, a critical flaw that could let attackers run code as root on Security Management and Log Servers with no login needed. Check Point addressed CVE-2026-91843 (CVSS ...
Pierluigi Paganini
September 18, 2026

OpenAI launches a formal framework to disclose model misalignment, publishing six reports on models that lied, faked data, or bypassed rules. Most companies don't publish a document explaining how ...
Pierluigi Paganini
September 17, 2026
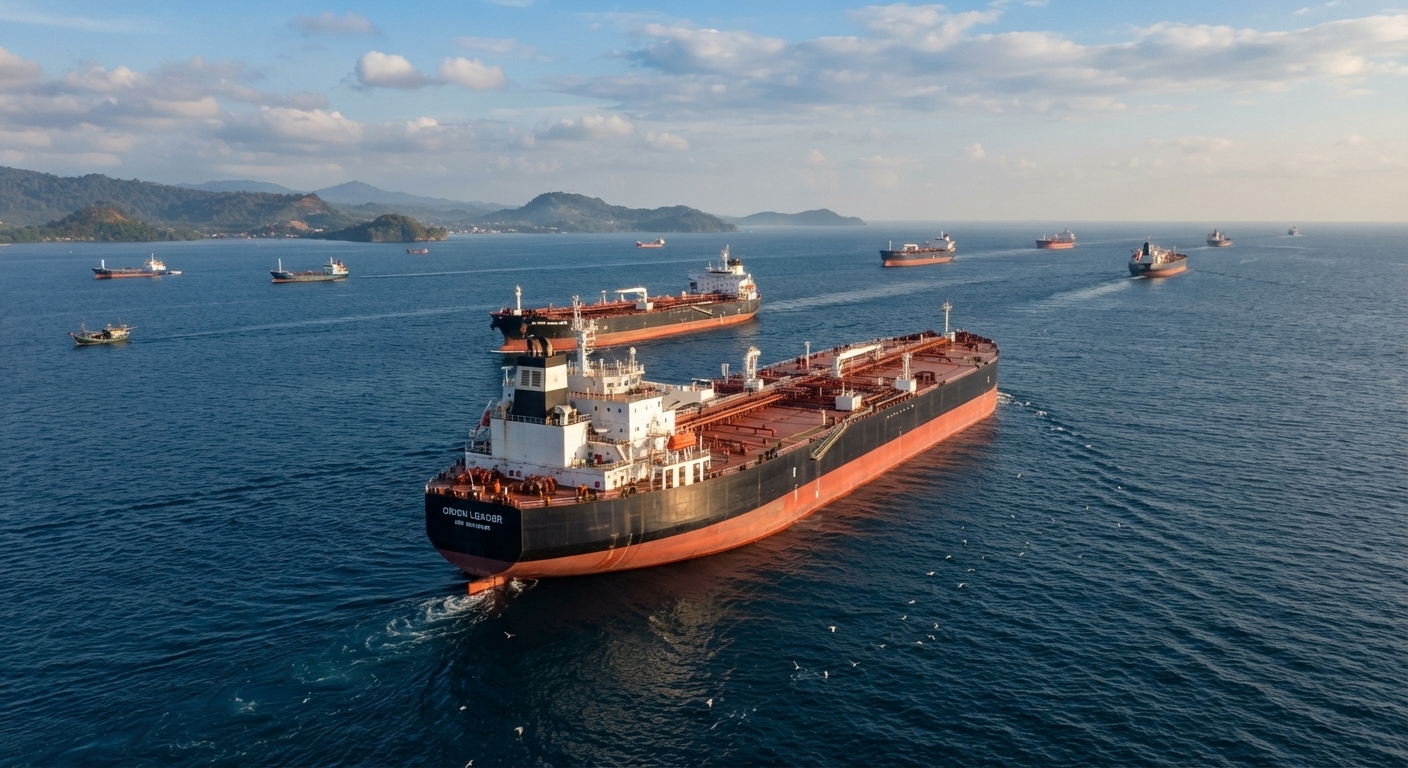
Cyberattacks on oil tankers show how connected ships can expose navigation and critical systems, threatening safety, ports and global trade. U.S. Coast Guard personnel and FBI agents boarded two T ...
Pierluigi Paganini
September 17, 2026

Hunt.io links SpiceRAT, NodeEdgeRAT and NomadRAT to a four-year SilkParasite campaign targeting governments and critical sectors in Central Asia. Hunt.io and researcher Guy Yasur have traced a tig ...
Pierluigi Paganini
September 17, 2026

The DOJ seized domains behind NightmareStresser, a DDoS-for-hire service tied to hundreds of thousands of attacks since 2022, as part of Operation PowerOFF. Renting a DDoS attack used to be as eas ...
Pierluigi Paganini
September 17, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity ...
Pierluigi Paganini
September 17, 2026

UK, US, and Dutch agencies expose Chosen Brick, Iranian malware used to track and harass dissidents, journalists, and activists via Telegram. The UK, the US, and the Netherlands published a joint ...
Pierluigi Paganini
September 17, 2026
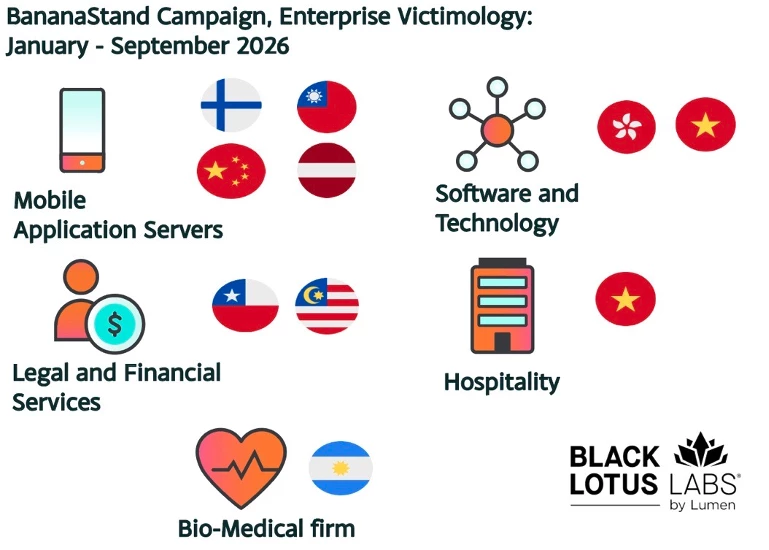
Lumen exposes BambooToken, a stealthy malware family using MQTT and sideloading to quietly infect targets across Asia and beyond. BambooToken is a new malware family that uses MQTT, a lightweight ...
Pierluigi Paganini
September 16, 2026
Google has patched a high-severity zero-day in the Pixel cellular modem after finding evidence that the vulnerability was exploited in limited, targeted attacks. Google has released its September ...
Pierluigi Paganini
September 16, 2026
A suspected compromise of an Italian government PEC account may have allowed threat actors to impersonate law enforcement and obtain sensitive data from hundreds of Revolut customers. The Revolut ...
Pierluigi Paganini
September 16, 2026
CenterPoint Energy confirmed a customer data breach after a hacker claimed to leak 7.49M records, including personal and billing information. CenterPoint Energy admitted on Monday that an intruder ...
Pierluigi Paganini
September 16, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security ...
Pierluigi Paganini
September 15, 2026

Cisco warns of a critical zero-day in Secure Email Gateway, exploited in the wild to gain root access through malicious emails. Cisco disclosed a critical zero-day, tracked as CVE-2026-76461 (CVSS ...
Pierluigi Paganini
September 15, 2026
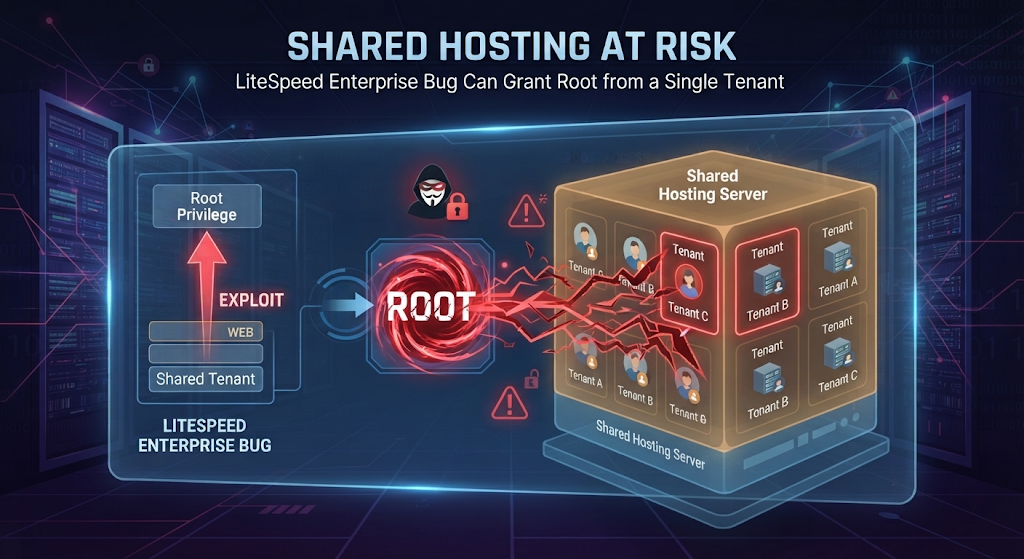
Critical LiteSpeed Enterprise flaw lets one shared hosting account gain root, bypassing CageFS; patch now to 6.3.7 via forced update. cPanel warned that a critical flaw in LiteSpeed Enterprise can ...
Pierluigi Paganini
September 15, 2026

Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome's patch shipped, deploying different backdoors each. Two China-linked threat actors used the same ...
Pierluigi Paganini
September 15, 2026
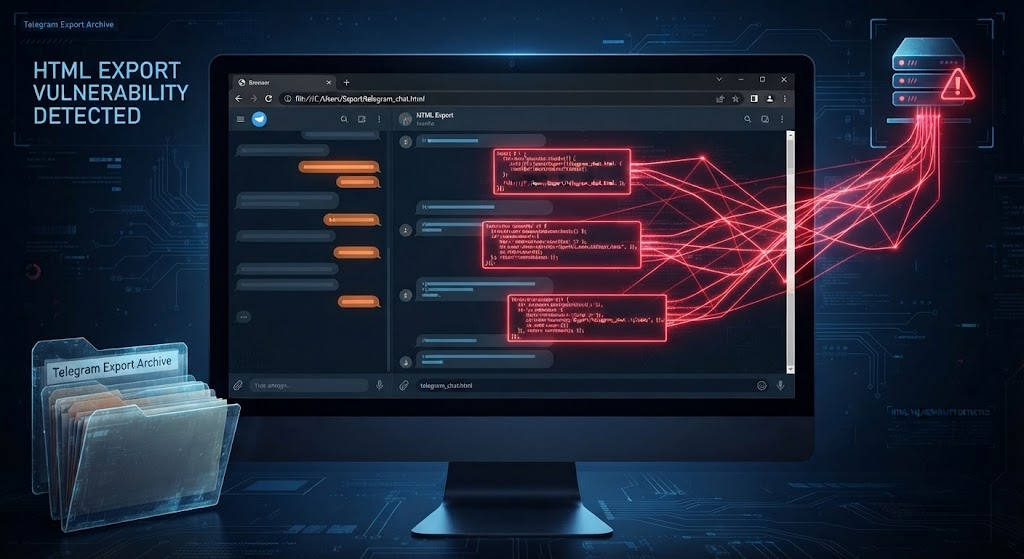
A Telegram Desktop flaw let bots inject JavaScript into exported chats, enabling data theft and page manipulation. Old HTML exports remain unsafe. A vulnerability in Telegram Desktop could have tu ...
Pierluigi Paganini
September 15, 2026
Japan 's Digital Agency disclosed a VPN breach exposing 246,000 government employee records across 23 ministries. Detected June 25, publicly disclosed September 11. Japan 's Digital Agency disclos ...
Pierluigi Paganini
September 15, 2026
Frontier AI is compressing the attack lifecycle from vulnerability discovery to exploitation, forcing defenders to detect, patch and respond at machine speed. Cybersecurity has always been a race ...
Pierluigi Paganini
September 14, 2026
China rejects Amodei’s AI slowdown proposal, calling it fearmongering and a US attempt to contain China’s technology sector. The debate over whether the world should slow down the development ...
Pierluigi Paganini
September 14, 2026